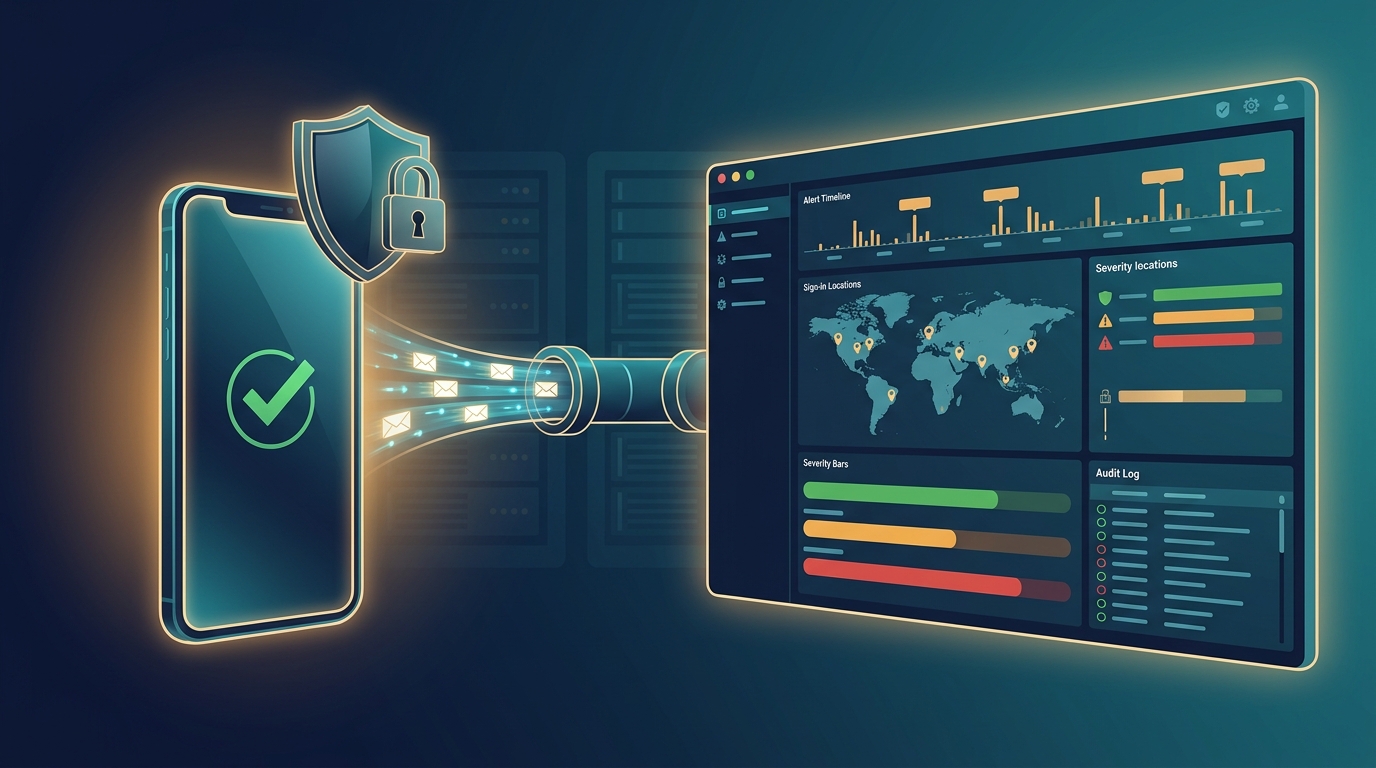
Duo authentication and admin activity logs flowing into a self-hosted Wazuh SIEM, ready for MFA monitoring and CMMC audit evidence.
As our business continues to grow our focus is on providing white labeled Tier 3 IT support services, RMM as a service, and co-managed IT services. This blog will be highlighting tips for using a Bash script to forward Cisco Duo MFA logs into a self-hosted Wazuh SIEM.
We recently connected Duo to the onsite Wazuh server of a client working toward CMMC Level 2. Logging every MFA event and every admin change is part of the evidence an assessor wants to see (NIST 800-171 controls 3.3.1 and 3.5.3). Duo ships an official tool for exactly this. Getting it to produce real Wazuh alerts took some work, so we turned everything we learned into one script that you can run by hand or from SuperOps RMM.
Research
Duo publishes DuoLogSync (github.com/duosecurity/duo_log_sync), a small Python service that pulls logs from the Duo Admin API and sends them as JSON over TCP. The plan was simple: run DuoLogSync on the Wazuh manager, send its output to a syslog listener that only accepts local connections, and let Wazuh’s built-in JSON decoder do the rest. No agent, no public port, no custom decoder.
In practice, five things got in the way. They aren’t obvious from the documentation:
Stock Wazuh rule 86600 (Suricata) matches any JSON event that has both “timestamp” and “event_type” fields. Duo auth logs have both, so every event was captured by a level 0 rule and silently thrown away. Our rules now hang under 86600 as child rules.
Wazuh loads every rule file, stock and custom together, in alphabetical order. Naming the file 9999_duo_rules.xml makes sure it loads after the stock rules it depends on.
“action” is a reserved Wazuh field name, so a field match on it stops the whole ruleset from loading. Use the <action> tag or a dotted field like action.name instead.
DuoLogSync 2.4 retired the “adminaction” endpoint. Admin events now come from the “activity” log, which has a completely different JSON layout.
DuoLogSync opens one TCP connection and never reconnects. Every Wazuh manager restart quietly lost the next batch of logs. The fix is a systemd unit tied to the manager with PartOf=wazuh-manager.service.
The payoff showed up right away. The 180-day history pull surfaced twelve failed Active Directory syncs, all caused by a Duo Authentication Proxy outage. If an AD sync fails, a user you just disabled in AD can still pass Duo, so that’s a finding worth knowing about.
Variables
DuoIntegrationKey = The integration key of a Duo Admin API application with only “Grant read log” permission – i.e. DIXXXXXXXXXXXXXXXXXX DuoSecretKey = The secret key for that application (mark this as a secure variable in SuperOps) DuoApiHost = The API hostname from the same application – i.e. api-xxxxxxxx.duosecurity.com DuoEndpoints = Optional. Which Duo logs to pull – default auth,telephony,activity DuoOffsetDays = Optional. How many days of history to pull on the first run, maximum 180 DuoAction = Optional. install, status, resend or uninstall
Script Snippet
The full script handles prerequisite checks, backups, validation, automatic rollback, and a final check with wazuh-logtest. These are the core pieces:
# DuoLogSync config - single quotes are required by DLS
cat > /opt/duologsync/config.yml <<EOF
version: '1.0.0'
dls_settings:
  log_format: 'JSON'
  api:
    offset: $DLS_OFFSET_DAYS
  checkpointing:
    enabled: True
    directory: '/opt/duologsync/checkpoints'
servers:
  - id: 'wazuh'
    hostname: '127.0.0.1'
    port: 5140
    protocol: 'TCP'
account:
  ikey: '$DUO_IKEY'
  skey: '$DUO_SKEY'
  hostname: '$DUO_API_HOST'
  endpoint_server_mappings:
    - endpoints: ['auth', 'telephony', 'activity']
      server: 'wazuh'
EOF

# Local-only listener added to ossec.conf
<remote>
  <connection>syslog</connection>
  <port>5140</port>
  <protocol>tcp</protocol>
  <local_ip>127.0.0.1</local_ip>
  <allowed-ips>127.0.0.1</allowed-ips>
</remote>

# Duo auth events are claimed by Suricata rule 86600 - attach under it
<rule id="120000" level="0">
  <if_sid>86600</if_sid>
  <field name="txid">\.+</field>
  <field name="factor">\.+</field>
  <description>Duo: authentication event</description>
</rule>

# systemd: restart with the manager, wait for the listener first
[Unit]
After=wazuh-manager.service
PartOf=wazuh-manager.service
[Service]
ExecStartPre=/bin/bash -c 'until ss -ltn | grep -q "127.0.0.1:5140 "; do sleep 2; done'
ExecStart=/opt/duologsync/venv/bin/duologsync /opt/duologsync/config.yml
Restart=always
The complete script, the SuperOps edition, and the full ruleset (with alerts for MFA fraud reports, MFA fatigue, admin panel brute force, Duo configuration changes and AD sync failures, all tagged for NIST 800-171) are free on our GitHub: https://github.com/FarmhouseNetworking/Duo-Wazuh-LogSync
If your company is a MSP or wants to become one and automation just seems out of reach, then contact us to run your RMM for you.
What the CMMC suspension teaches every small business about the danger of waiting on compliance
Building a cybersecurity policy before it’s required can save your business time, money, and trust.
On July 13, 2026, the Department of War suspended Phase II of its Cybersecurity Maturity Model Certification (CMMC) program — the rule that would have required over 100,000 defense contractors to complete third-party cybersecurity assessments starting this November. The reason wasn’t that cybersecurity stopped mattering. It’s that the compliance system itself couldn’t scale: too few certified assessors, costs approaching $600,000 per certification, and a timeline small businesses couldn’t meet.
That story has nothing to do with defense contracts if you’re not one. But it has everything to do with a mistake we see constantly: business owners treating cybersecurity policy as something to build only when a regulator forces the issue. When the deadline moves or disappears, so does the motivation — right up until a breach, an insurance audit, or a client contract makes it urgent again, usually at the worst possible time.
Why Waiting Is the Expensive Choice
Government programs get delayed, revised, or scrapped. Your actual risk — ransomware, phishing, a stolen laptop, an employee clicking the wrong link — doesn’t wait for anyone’s regulatory calendar. Businesses that build security practices proactively spend less, recover faster, and rarely scramble when a client or insurer asks for documentation they don’t have.
Action Steps for Business Owners
Write down your security policies now, even in simple form: password requirements, data handling rules, who can access what.
Inventory your systems and data — you can’t protect what you haven’t mapped.
Set a patch and update schedule instead of reacting to alerts.
Back up data regularly and actually test that restores work.
Train staff on phishing and basic security hygiene at least twice a year.
Review vendor contracts for the security commitments you’re already making to clients or partners.
Revisit your plan quarterly — don’t let it go stale.
Questions Business Owners Are Likely Asking
“If the government paused its own program, why should I move faster on mine?” Because your risk was never tied to their timeline. The suspension was about assessment logistics, not about cyber threats becoming less real.
“Isn’t this overkill for a small business?” No — attackers target small businesses precisely because they assume no one built a plan. A written policy costs far less than a breach.
“Do I need a full compliance framework?” Not necessarily. You need documented, consistently applied practices. Formal frameworks can come later if a client or contract requires them.
“What if I don’t have an in-house IT person?” That’s exactly where a managed partner earns their keep — building and maintaining the plan so you don’t have to.
How Farmhouse Networking Helps
We help small and mid-sized businesses build the security foundation regulators eventually ask for — without waiting for a mandate to force the issue. That means clear, documented policies, practical safeguards like MFA and monitored backups, and straightforward guidance you can actually act on, without the jargon.
Don’t Wait for the Next Deadline to Get Serious
Regulations pause. Real risk doesn’t. If you’ve been putting off a cybersecurity policy because “nothing’s required yet,” now is the time to close that gap — before something else forces the timeline.
Email us at support@farmhousenetworking.com for a free cybersecurity policy review. We’ll tell you plainly where you stand and what to fix first.
A Comprehensive Cost Guide for Government Contractors
CMMC certification costs by level: Budget $75K-$150K for most small DoD contractors pursuing Level 2 compliance.
CMMC Certification is a new cybersecurity standard for the Defense Industrial Base (DIB) and defense supply chain, crucial for DoD contractors to protect sensitive information and prevent security breaches. The framework’s introduction and integration into the acquisition and contracting process underscore its importance for cybersecurity maturity assessment and the safeguarding of Controlled Unclassified Information (CUI).
Changes implemented with CMMC 2.0, including the use of Plans of Actions and Milestones (POA&Ms) and limited waivers, aim to streamline the certification process while ensuring rigorous cybersecurity standards align with NIST guidelines. These adaptations demonstrate an evolving approach towards enhancing the cybersecurity infrastructure of government contractors and maintaining public trust.
Factors Influencing CMMC Compliance Costs
Understanding the multifaceted nature of CMMC certification costs is crucial for DoD contractors aiming to achieve compliance. The cost factors are primarily influenced by:
Current Security Maturity: Organizations with a higher level of NIST 800-171 compliance face lower costs in adopting CMMC. This underscores the importance of existing cybersecurity practices within the organization.
Organization Size and Complexity: Larger organizations and those with multiple locations generally incur higher compliance and maintenance costs due to the scale of operations and the complexity of securing a wider network.
Scope and Access of Controlled Unclassified Information (CUI): The extent of CUI access significantly impacts compliance costs. Organizations with broader access to CUI are required to implement more stringent security measures, thereby increasing the cost.
Additionally, the approach to system changes plays a critical role:
Full Approach vs. Enclave Approach: Opting for a full overhaul of operations to meet CMMC standards can be more costly compared to creating a secure enclave for CUI. The choice between these approaches affects the overall cost and strategy for achieving compliance.
These factors, combined with the costs associated with audits, expert consultation, and documentation, form the backbone of the financial planning required for CMMC certification. Understanding these elements is essential for DoD contractors to navigate the path to compliance efficiently and cost-effectively.
Estimated Costs by CMMC Level
Breaking down the estimated costs by CMMC level can provide a clearer picture for DoD contractors on what financial commitments might be expected. Here’s a concise breakdown:
CMMC Level 1: Basic Cybersecurity
Small Entity: Self-assessment and affirmation cost roughly $6,000.
Larger Entity: Self-assessment and affirmation cost about $4,000.
CMMC Level 2: Intermediate Cybersecurity
Small Entity: Self-assessment and related affirmations over $37,000; Certification by C3PAO nearly $105,000 [5].
Larger Entity: Self-assessment and related affirmations nearly $49,000; Certification by C3PAO approximately $118,000.
CMMC Level 3: Good Cybersecurity Practices
Small Organization: Recurring engineering costs $490,000; Nonrecurring costs $2.7 million; Certification assessment over $10,000.
Larger Organization: Recurring engineering costs $4.1 million; Nonrecurring costs $21.1 million; Certification assessment more than $41,000.
This tiered structure illustrates the significant investment in cybersecurity infrastructure required at each level, highlighting the importance of accurate budgeting and financial planning for compliance.
Strategies for Minimizing Compliance Costs
To minimize CMMC certification costs effectively, consider the following strategies:
Streamline Your Compliance Efforts:
Leverage the streamlined requirements of CMMC 2.0, including self-assessments for certain levels, which are expected to lower assessment costs compared to CMMC 1.0.
Familiarize yourself with the revised CMMC 2.0 framework to understand how it aims to reduce costs and increase trust in the assessment ecosystem.
Conduct a comprehensive self-assessment using NIST’s guide for NIST SP 800-171, focusing on foundational security measures and managing consulting fees.
Optimize Your CMMC Project Scope:
Determine the exact scope of your CMMC project. Consider storing CUI in a separate, secure enclave and using expert consultants to save money.
If only a portion of your organization handles CUI, create a separate enclave for a simpler assessment process, thereby reducing your compliance boundary.
Choose technologies and platforms that are easy to deploy and use, which support the NIST SP 800-171 security controls, and offers a compliance documentation package.
Invest Wisely in Technology and Expertise:
Utilize automated platforms to centralize various types of GRC programs, reducing siloed tasks and leveraging technology to cut costs.
Consider outsourcing for SIEM, vulnerability scanning, and hardware/software monitoring to manage costs effectively:
Engage consultants who are familiar with your technology, helping to ensure a smooth and cost-effective compliance process.
Contact us today to explore how to best align your cybersecurity efforts with the demands of CMMC Certification, ensuring protection and compliance in an ever-evolving cybersecurity landscape.
And God will generously provide all you need. Then you will always have everything you need and plenty left over to share with others. As the Scriptures say, “They share freely and give generously to the poor. Their good deeds will be remembered forever.” For God is the one who provides seed for the farmer and then bread to eat. In the same way, he will provide and increase your resources and then produce a great harvest of generosity in you. - 2 Corinthians 9:8-10
We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.