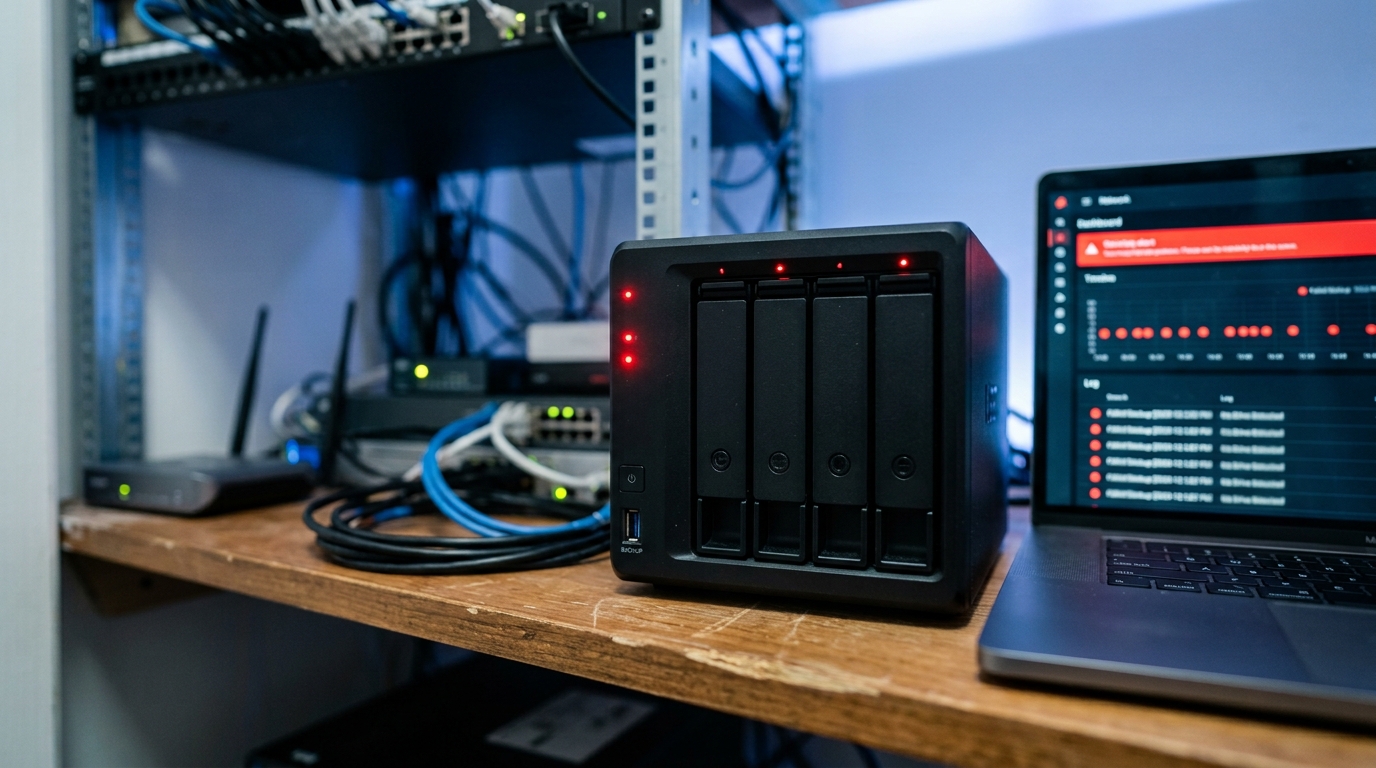
A NAS can record backup failures every night for weeks. Without centralized log monitoring, nobody sees them.
As an MSP, our focus is providing white labeled Tier 3 IT support services, RMM as a service, and co-managed IT for other IT providers and businesses. This blog will share tips on forwarding Synology NAS logs into a self-hosted Wazuh SIEM using a Bash script.
We recently connected a client’s Synology NAS to their onsite Wazuh server while they worked toward CMMC Level 2. Sending NAS sign-ins, configuration changes, file activity and backup results to a central SIEM supports NIST 800-171 controls 3.3.1 (create and retain audit records) and 3.3.2 (trace actions to individual users). It also gave the client a backup-failure alert they did not have before. We packaged the work into one script that can be run by hand on the Wazuh manager or through SuperOps RMM.
Research
Wazuh does not ship Synology decoders, so the NAS’s syslog arrives and is silently dropped as “no decoder matched.” Getting it right took longer than expected, because almost every mistake fails without an error:
The protocol has to match. DSM’s Log Center was set to UDP while our Wazuh syslog listener was TCP. A Wazuh <remote> syslog block accepts exactly one protocol. tcpdump on the manager still shows the packets, because it sees them before any program does.
DSM only sends the priorities you select. With Info and Notice unticked in Log Filters, failed sign-ins arrived and nothing else did.
Active Backup for Business has its own syslog setting. It does not go through Log Center at all, and its transfer protocol also has to be TCP.
DSM uses several line formats, and Wazuh treats them differently. Lines with a program name (“Connection:”, “ActiveBackup[pid]:”, “Hyper_Backup:”) are only checked against decoders that declare a <program_name>. Lines without one (“System user:”, “FileStation Event:”) are only checked against decoders that don’t. A decoder on the wrong list loads cleanly and never runs. We confirmed this in Wazuh’s source (decoders_list.c and cleanevent.c).
Child rule order is by level, not by file order. Wazuh tries a parent’s children highest level first. A specific rule meant to beat a general one must be at a higher level, or at the same level and earlier in the file.
Not every DSM change writes a log entry. Toggling Log Center’s own archive settings writes nothing. Creating and deleting a scheduled task always does, so that became our end-to-end test.
The results were worth it. The client’s Hyper Backup history showed one stretch of 40 days in a row with no successful backup, because no USB drive was attached. The NAS’s own notification emails had been failing too, so nobody was told. That failure now raises an alert. A scheduled report also flags any 26-hour window without a successful backup, since no rule can fire on a message that is never sent.
Variables
SynologyNasIp = NAS address, or several separated by commas (required for install)
SynologyAction = install, status or uninstall (optional, default install)
SynologyWatchUsers = break-glass account name(s); every sign-in raises a level 10 alert (optional)
SynologyAddListener = yes or no; use no if the NAS is already allowed in an existing syslog block (optional, default yes)
SynologyPort = listener port (optional, default 514)
SynologyProtocol = tcp or udp (optional, default tcp)
SynologyRuleBase = first rule ID (optional, default 127500)
SynologyOpenFirewall = yes or no; opens ufw or firewalld for the NAS address only (optional, default yes)
SynologyRestart = yes or no (optional, default yes)
Script Snippet
Before the manager restarts, the full script:
checks for rule ID collisions and listener conflicts
backs up ossec.conf
compares wazuh-analysisd -t output before and after
feeds 23 real DSM log lines through wazuh-logtest
It rolls back automatically if any of those fail. Here are the key pieces:
# Syslog listener restricted to the NAS, wrapped in markers so re-runs and uninstall can find it
<!-- BEGIN synology-wazuh-install listener -->
<remote>
  <connection>syslog</connection>
  <port>514</port>
  <protocol>tcp</protocol>
  <allowed-ips>192.0.2.10</allowed-ips>
</remote>
<!-- END synology-wazuh-install listener -->

# "Connection:" lines have a program name, so this decoder must declare one
<decoder name="synology-conn">
  <program_name>^Connection$</program_name>
  <prematch type="pcre2">User \[[^\]]*\] from \[[^\]]+\]|Host \[[^\]]+\] (?:was blocked|failed to connect)</prematch>
</decoder>

# "System user:<TAB>message" lines have no program name, so this one must not
<decoder name="synology-system">
  <prematch type="pcre2">^System \S+:\s</prematch>
</decoder>

# Hyper Backup: a rotated-out USB drive is expected (level 5); anything else is a real failure (level 10)
<rule id="127564" level="10">
  <if_sid>127560</if_sid>
  <match type="pcre2">Failed to access the backup destination|Exception occurred while backing up data|Backup task was cancell?ed|Failed to start backup task(?!\. \(The backup destination does not exist)</match>
  <description>Hyper Backup: task $(syno_task) failed - $(syno_event)</description>
  <group>backup,backup_failure,</group>
</rule>
<rule id="127563" level="5">
  <if_sid>127560</if_sid>
  <match type="pcre2">Failed to (?:run|start) backup task</match>
  <description>Hyper Backup: task $(syno_task) did not run - $(syno_event)</description>
</rule>

# Self-test: every sample line must land on its expected rule, or the install rolls back
while IFS='|' read -r off line; do
  want="$(rule_id "$off")"
  out="$(printf '%s\n' "$line" | "$OSSEC_DIR/bin/wazuh-logtest" 2>&1)"
  got="$(printf '%s\n' "$out" | sed -n "s/^[[:space:]]*id: '\([0-9]*\)'.*/\1/p" | tail -n 1)"
  [ "$got" = "$want" ] || fails=$((fails + 1))
done < <(self_test_samples)
The full script, the SuperOps edition, the decoders and the complete ruleset are free on our GitHub. There are 65 rule IDs, covering:
sign-ins and brute force
file activity and mass deletion
account and privilege changes
audit logging being turned down
storage pool and iSCSI LUN failures
power and UPS events
Active Backup for Business and Hyper Backup results
AI-Powered Microsoft 365 & Google Workspace Log Monitoring Now Included Free
Farmhouse Networking’s managed IT service now includes AI-driven log analysis for SMBs — ensuring proactive cloud security without added cost.
Small and mid-sized businesses today face the same cybersecurity threats as large enterprises — but without the same budget or in-house expertise. That’s why Farmhouse Networking is proud to announce a major upgrade to our managed IT services: AI-driven log triage and alerting for Microsoft 365 and Google Workspace. This enhanced monitoring service is automatically included in every monthly IT services contract — at no additional cost — helping business owners protect their operations, data, and reputation with enterprise-grade intelligence.
Why This Matters for Your Business
Your Microsoft 365 and Google Workspace platforms store your most vital data: emails, documents, and shared communications. Each login, file access, or configuration change generates valuable log data — but few SMBs have time or staff to analyze it.
With AI analysis, Farmhouse Networking automatically scans and prioritizes potential threats like:
Unusual logins or failed login attempts.
Unauthorized access to sensitive files.
Compromised accounts or third-party app activity.
Suspicious data downloads or sharing patterns.
Our system flags concerns in real time and alerts our team so potential incidents are triaged before they escalate into security breaches or downtime.
How AI-Enhanced Log Monitoring Works
Data ingestion: Logs from Microsoft 365 and Google Workspace are securely collected.
AI triage: Advanced machine learning detects patterns of unusual behavior.
Actionable alerts: Our technicians receive intelligent alerts prioritized by severity.
Resolution: We investigate, verify, and act before small issues become big problems.
What sets Farmhouse Networking apart is that this enterprise-grade capability is built into your existing service plan — not an add-on.
Common Questions from Business Owners
Q1: Why should my SMB care about log monitoring? A: Cloud environments record every login and activity. Monitoring those logs can detect attacks, data leaks, or insider misuse early — saving your business from costly security or compliance violations.
Q2: Does this mean I’ll get constant alerts? A: No — our AI filters the noise, so only meaningful alerts reach our support team. You see outcomes, not overwhelm.
Q3: Is my data secure when analyzed? A: Absolutely. We follow strict data handling and encryption standards to ensure privacy at every stage.
Q4: How does this benefit our productivity? A: By catching risks early, we prevent downtime, data loss, and productivity disruption — letting you focus on running your business.
How Farmhouse Networking Helps You Stay Ahead
Your business deserves the same security tools as major corporations — but without excessive cost or complexity. Our AI-assisted log triage gives you proactive protection, increased visibility, and peace of mind.
We handle the technical heavy lifting so you can keep growing.
Email support@farmhousenetworking.com today to learn how we can enhance your IT security strategy and streamline your operations.
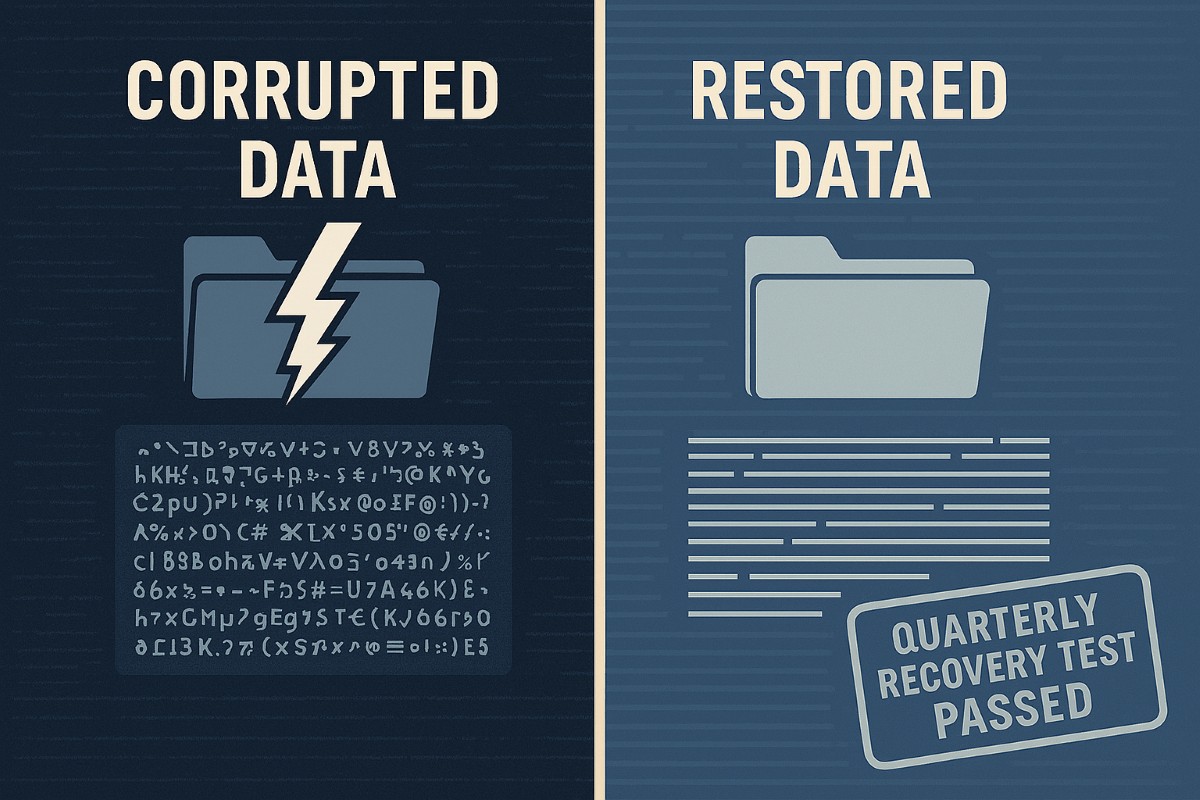
A strong data recovery plan protects businesses from data loss, downtime, and cyberattacks.
Every small and medium-sized business faces the risk of data loss—from ransomware, accidental deletions, or system failures. According to CIS Critical Security Control 11, a strong data recovery plan is essential for staying operational and protecting your reputation.
Key Action Steps for SMBs
Implement regular automated backups: Set daily schedules with both onsite and cloud solutions.
Review and test recovery plans: Don’t wait for a crisis—run annual recovery drills.
Update recovery policies as the business grows: Ensure new systems are included.
Common Client Questions
Aren’t backups enough? Not quite. You need tested recovery processes to guarantee downtime is minimal.
What if we don’t have IT staff? Partnering with an expert provider like Farmhouse Networking keeps your systems protected without you needing in-house IT.
How Farmhouse Networking Helps
We deliver reliable and cost-effective recovery strategies, handling everything from setup to ongoing monitoring, so you can focus on growth while we protect your data.
Build your incident response plan: Be ready not sorry with structured IT disaster preparedness for business continuity
A single cyber incident can halt operations, lose you money, and damage your reputation. Every small business owner should have a tested, up-to-date incident response plan for business continuity in today’s digital landscape.
Action Steps
Identify Key Systems & Vulnerabilities: Map critical assets and conduct risk assessments.
Form a Cross-functional Team: Clarify roles across IT, management, and other departments.
Draft & Document the Plan: Prepare step-by-step procedures for detection, containment, eradication, recovery, and lessons learned.
Schedule Regular Drills: Simulate breaches and review performance; adjust where needed.
Keep Everything Updated: Revise often to reflect new threats and internal changes.
Q&A
Q: What is the biggest challenge? A: Ensuring clear communication and rapid response across departments.
Q: What if something changes in our business? A: Update the plan and retrain your team right away.
How Farmhouse Networking Helps
Farmhouse Networking streamlines every step—custom planning, team training, tabletop exercises, and ongoing consults to keep your business secure.
Relieve IT staff burnout with co-managed services, ensuring vacations don’t disrupt business operations
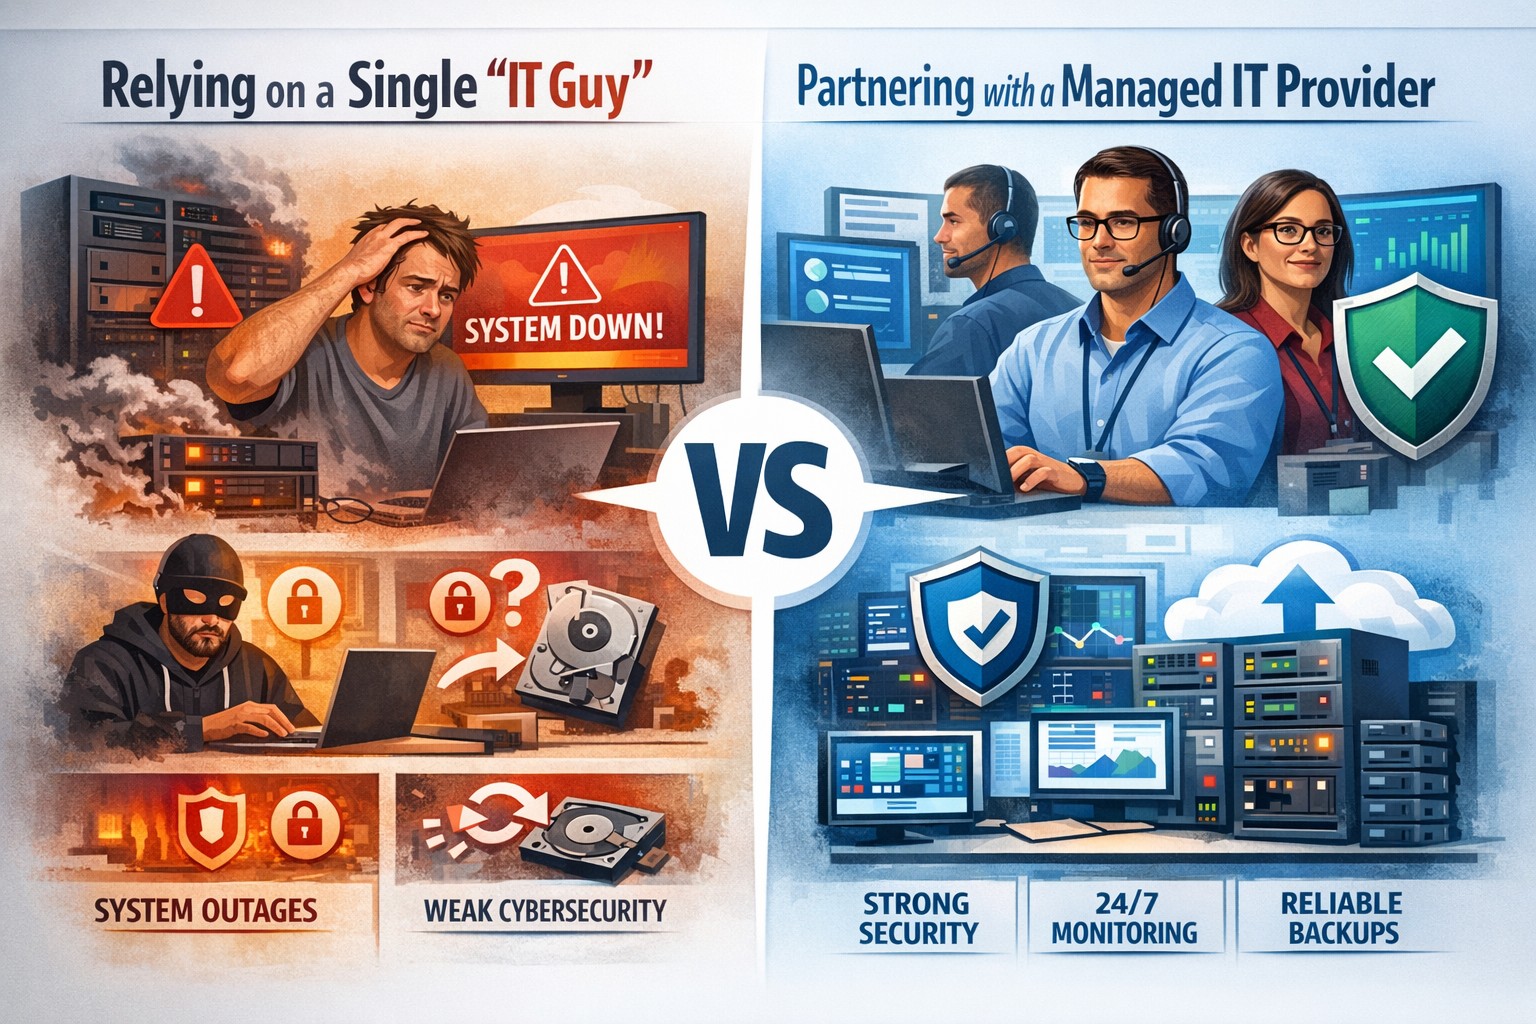
Imagine this: Your trusted IT staff member, the backbone of your business’s technology, needs a well-deserved vacation or calls in sick. Suddenly, your entire operation is at risk—projects stall, security gaps widen, and stress levels spike. For many business owners, this scenario is all too familiar. Relying on a single person for all IT needs can lead to burnout, costly downtime, and vulnerabilities that threaten your success.
Why Co-Managed IT Is the Smart Solution
Co-managed IT is a partnership that blends your in-house IT expertise with the resources and experience of a dedicated IT provider. This approach ensures there’s always IT support, so your business never misses a beat. Here’s why it matters:
Avoid the costs and risks of being understaffed or overburdened.
Gain a trusted team monitoring and managing your systems.
Your IT staff focuses on day-to-day operations and business-specific needs.
The co-managed provider handles monitoring, backups, cybersecurity, and complex projects.
Both teams communicate and collaborate, ensuring seamless coverage and peace of mind.
Practical Steps to Get Started with Co-Managed IT
If you’re ready to future-proof your business, here’s how you and your IT department can take action:
Assess Your Current IT Workload: Identify areas where your IT staff feels stretched thin or lacks specialized expertise.
Pinpoint Critical Systems: List essential operations and data that must remain secure and accessible at all times.
Open the Conversation: Discuss with your IT staff how external support could relieve pressure and enhance performance.
Research Co-Managed IT Providers: Look for partners with a proven track record, strong communication, and a collaborative approach.
Develop a Transition Plan: Work with your chosen provider to outline roles, responsibilities, and communication channels.
How Farmhouse Networking Can Help
Farmhouse Networking specializes in co-managed IT solutions tailored for businesses like yours. We work alongside, not replace, your internal IT team by offering:
24/7 monitoring and rapid response to keep your systems running smoothly.
Advanced cybersecurity to protect your data from evolving threats.
Expert support for complex projects and technology upgrades.
Seamless collaboration that empowers your staff and maximizes efficiency.
Our approach ensures your business is never vulnerable—whether your IT staff is on vacation, out sick, or simply needs an extra set of hands.
Ready to Safeguard Your Business?
Don’t let a single absence put your business at risk. Email us today to discover how Farmhouse Networking can help you achieve uninterrupted operations, reduce IT stress, and drive your business forward with confidence.
Why Every Minute Matters and How Farmhouse Networking Delivers
Every minute of system downtime costs your small business money—proactive monitoring and managed IT services dramatically reduce outages and protect your revenue.
Imagine your business suddenly grinds to a halt—orders can’t be processed, patient records are inaccessible, and your team is scrambling to keep up. Technical issues or downtime can stop operations in their tracks, leading to lost revenue, frustrated customers, and even dissatisfied patients in healthcare settings. Today every second of downtime can cost thousands of dollars and erode the trust your clients and patients place in your organization.
Why Farmhouse Networking Stands Out Among MSPs
Farmhouse Networking isn’t just another managed service provider (MSP)—we’re your proactive partner in preventing costly system interruptions. While many MSPs offer basic monitoring and support, Farmhouse Networking delivers a competitive advantage through a blend of advanced technology, rapid response protocols, and a deep understanding of the unique challenges faced by healthcare, manufacturing, and charity sectors.
Our approach is built on proactive monitoring, which means we detect potential issues—such as failing hardware, network bottlenecks, or cyber threats—before they impact your operations. With 24/7 monitoring and clearly defined Service Level Agreements (SLAs), we guarantee swift issue resolution, minimizing downtime and keeping your business running smoothly. Unlike in-house IT teams limited to business hours, our team is always on standby, ready to tackle urgent problems the moment they arise.
Key Features and Benefits: What Farmhouse Networking Offers
Proactive Network Monitoring: Continuous oversight of your IT infrastructure to catch and resolve issues before they escalate.
Rapid Issue Resolution: Fast response times with clear SLAs, ensuring minimal disruption to your business operations.
Disaster Recovery Planning: Comprehensive plans tailored to your organization, including risk assessment, backup strategies, and clear communication protocols to restore services quickly in case of a disaster.
Customized Support: Solutions designed specifically for healthcare, manufacturing, and nonprofit sectors, addressing industry-specific compliance and security needs.
Employee and Patient Satisfaction: By keeping systems online and data secure, we help you maintain trust with both your team and your clients or patients.
A Real-World Example: The Value of Proactive MSP Support
Consider a healthcare provider facing a network outage. Without proactive monitoring and rapid response, clinicians may be unable to access electronic health records, leading to delayed diagnoses, treatment errors, and frustrated patients. Farmhouse Networking’s proactive approach ensures these scenarios are prevented or swiftly resolved, safeguarding both patient safety and your organization’s reputation.
Secure Your Business Continuity
Don’t let system downtime disrupt your business or compromise your clients’ trust. Farmhouse Networking is ready to help you minimize downtime, maximize productivity, and keep your operations running smoothly—no matter what challenges arise.
Email us today to learn more about how Farmhouse Networking can improve your business continuity and end system downtime for good. Let’s build a more resilient future together.
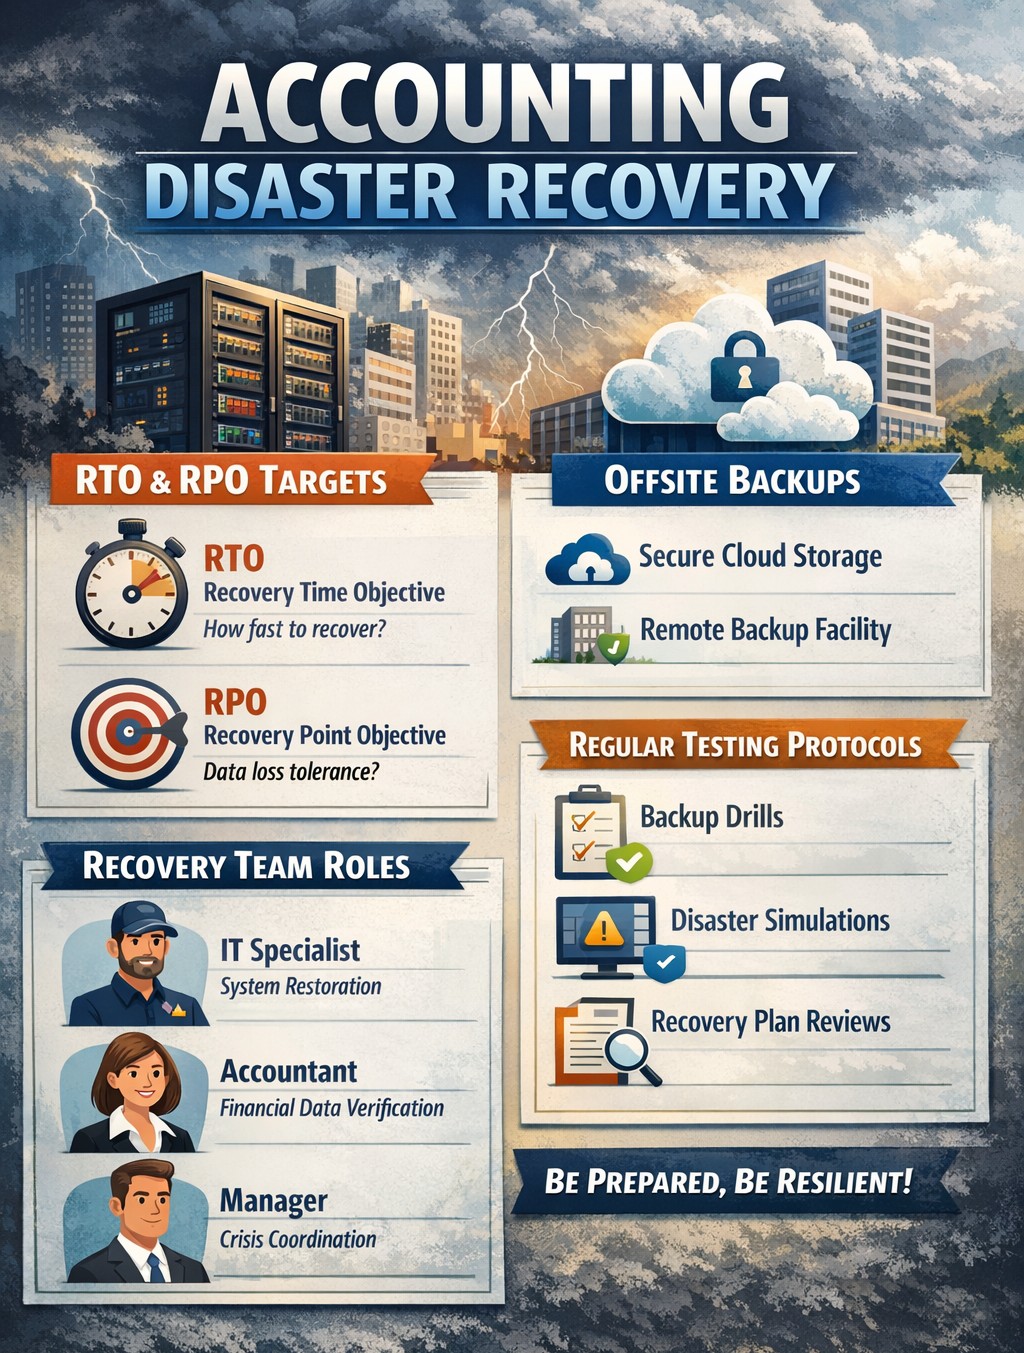
Layered backup solutions preventing data loss disasters for accounting practices
As the owner of an accounting practice, your clients trust you with their most sensitive financial data. But with great responsibility comes significant risk – data loss can devastate your operations, damage your reputation, and even threaten your firm’s survival. Understanding the causes of data loss and how to mitigate those risks is key to keeping your business secure and resilient.
The Leading Causes of Data Loss in Accounting Firms
Accounting practices face unique data risks due to the volume and sensitivity of the information they handle. The most common causes include:
Human Error: Mistakes like accidental file deletion, overwriting data, or sending sensitive information to the wrong recipient are the top cause of data loss, accounting for up to 88% of incidents. Even well-trained staff can make errors, especially under tight deadlines or with manual data entry.
Cybersecurity Breaches: Accounting firms are prime targets for hackers due to the financial data they store. Cyberattacks can lead to data theft, ransomware lockouts, and costly breaches that expose client information and trigger compliance headaches.
Hardware or Software Failure: Servers, hard drives, and other devices can fail unexpectedly, causing sudden data loss if backups aren’t in place.
Natural Disasters: Fires, floods, or power outages can physically destroy data storage systems, leading to permanent loss unless offsite or cloud backups exist.
Poor Data Management: Outdated or poorly designed systems increase the risk of accidental loss, corruption, or unauthorized access.
The consequences of data loss extend beyond immediate disruption. Accounting firms may face regulatory fines, expensive lawsuits, and – perhaps most damaging – loss of client trust and reputation.
How to Mitigate Data Loss Risks
Partnering with a trusted MSP like Farmhouse Networking provides a multi-layered approach to data protection, tailored to the unique needs of accounting practices:
Comprehensive Backups and Recovery: Farmhouse Networking implements robust, automated backup systems – storing data both onsite and in the cloud – ensuring your data is recoverable even if disaster strikes. Backups are regularly tested and monitored for reliability, so you can restore critical information quickly and minimize downtime.
Advanced Security and Encryption: Sensitive client data is protected with industry-standard encryption, both at rest and in transit. Farmhouse Networking also deploys SPAM filtering and anti-phishing tools to block malicious emails, a common entry point for cyberattacks.
Disaster Recovery and Business Continuity Planning: Farmhouse Networking works with your firm to develop and test disaster recovery plans, ensuring your operations can continue with minimal interruption after an incident.
Employee Training and Access Controls: Since human error is a leading cause of data loss, Farmhouse Networking provides security awareness training for your staff and enforces strict access controls, so only authorized personnel can access sensitive information.
Compliance and Audit Support: MSPs like Farmhouse Networking help ensure your IT systems are compliant with industry regulations, reducing the risk of fines and supporting audit readiness.
Ongoing Monitoring and Support: With 24/7 monitoring and proactive maintenance, Farmhouse Networking detects and resolves issues before they escalate, keeping your systems secure and your team focused on serving clients.
Don’t Leave Your Data and Your Reputation at Risk
Data loss is not a matter of if, but when. The right MSP partner can mean the difference between a minor hiccup and a catastrophic event. Farmhouse Networking specializes in protecting accounting firms like yours with proven solutions for backup, security, compliance, and business continuity.
Ready to safeguard your practice?
Contact Farmhouse Networking today for a free consultation and discover how we can keep your data and your business secure, resilient, and ready for whatever comes next.
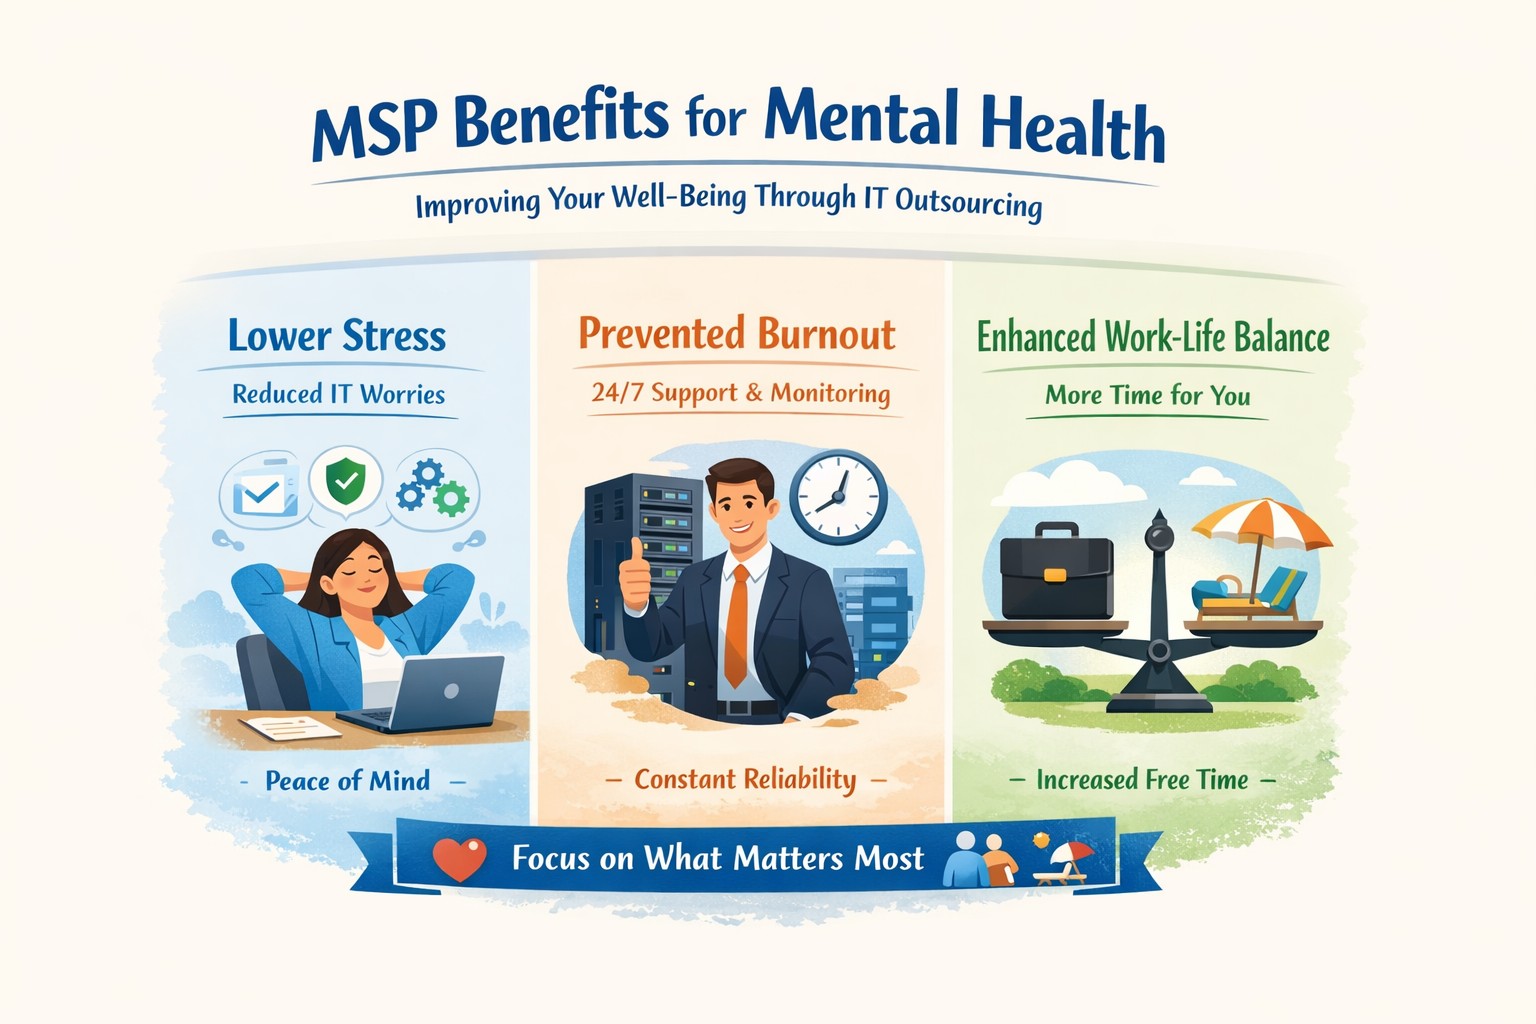
Co-managed IT MSP improving mental health through proactive support and reduced technical worries
The mental health of employees is more crucial than ever. As companies navigate the complexities of technology and cybersecurity, many are turning to Managed Service Providers (MSPs) to alleviate IT burdens. This partnership not only enhances operational efficiency but also significantly contributes to the mental well-being of employees. Here’s how having an MSP handle your company’s IT can lead to a healthier workplace.
Reducing Stress and Anxiety
IT-related issues can be a significant source of stress for employees. Frequent disruptions, outdated technology, and cybersecurity threats create an environment of constant anxiety. By outsourcing these responsibilities to an MSP, businesses can minimize these stressors. MSPs proactively manage IT systems, ensuring that potential problems are addressed before they escalate, which leads to a more stable work environment.
Promoting Work-Life Balance
One of the most profound benefits of partnering with an MSP is the ability to foster a healthier work-life balance. With an MSP managing routine IT tasks, employees can focus on their core responsibilities without the distraction of technical issues. This shift allows for better time management and reduces the likelihood of burnout, as employees can dedicate their energy to meaningful work rather than troubleshooting IT problems.
Enhancing Productivity
When employees are relieved from the constant pressure of managing IT issues, their productivity naturally increases. Studies show that mental health issues can severely impact productivity; by ensuring that technology runs smoothly and efficiently, MSPs contribute to a more engaged and productive workforce. Employees who feel supported in their roles are more likely to be motivated and perform at their best.
Investing in an MSP is not just about improving your IT infrastructure; it’s about enhancing your workplace culture and supporting your team’s mental health. By alleviating stressors associated with technology management, you empower your employees to thrive both personally and professionally.
Ready to transform your business operations while prioritizing mental well-being? Contact Farmhouse Networking today for a free consultation! Let us help you take the first step towards a healthier workplace where your team can excel without the burden of IT challenges.
Resolve to strengthen cyber defenses in 2025 with zero trust and employee training.
Stepping into 2025, SMBs face an scary and complex cybersecurity field of battle. With hackers evolving cyber threats at a rapid pace, it’s crucial to make strengthening your digital defenses a top priority. Let’s explore some essential tips to boost your cybersecurity posture in the coming year.
Embrace a Zero Trust Mindset
Start the new year by adopting a Zero Trust approach to cybersecurity. This means verifying every user, device, and application attempting to access your network, regardless of their location. Implement Zero Trust Network Access protocols and use Application Allow/Deny lists to control which software can run on your systems.
Strengthen Your Network Defenses
Secure Your Wi-Fi: Ensure your Wi-Fi network is encrypted and properly configured. Use strong passwords and consider implementing network segmentation to isolate guest networks from your internal systems.
Implement Firewalls and Intrusion Prevention Systems: Deploy robust firewalls to filter incoming and outgoing traffic. Couple this with intrusion prevention systems that actively seek out and block known threats.
Protect Your Data
Encrypt Sensitive Information: Apply encryption to both data at rest and in transit. This includes emails, file transfers, and stored documents.
Implement Data Loss Prevention (DLP) Tools: Use DLP tools to track critical data and prevent unauthorized exfiltration attempts.
Enhance Authentication Measures
Multi-Factor Authentication (MFA): Implement MFA across all your systems, applications, and websites. This additional layer of security significantly reduces the risk of unauthorized access.
Use Password Managers: Encourage the use of password managers to generate and store complex, unique passwords for each account.
Educate Your Employees
Regular Security Awareness Training: Conduct ongoing cybersecurity training for all employees. Focus on recognizing phishing attempts, proper handling of sensitive data, and best practices for remote work.
Prepare for the Worst
Develop an Incident Response Plan: Create a comprehensive plan that outlines procedures for responding to various cybersecurity incidents. Regularly test and update this plan.
Implement Robust Backup Solutions: Establish a regular backup schedule for all critical data and systems. Store backups securely, preferably in multiple locations, including off-site.
Stay Updated and Vigilant
Keep Software and Systems Current: Regularly update all software, applications, and operating systems. Automate updates where possible and conduct periodic audits to ensure nothing is missed.
Implement Real-Time Monitoring: Deploy solutions that provide continuous, real-time monitoring of your network and systems. This allows for immediate detection and response to potential threats.
Secure Your Remote Workforce
With hybrid work models likely to persist, ensure your remote workers are equipped with secure tools:
– Provide Zero Trust VPN access for secure connections – Implement endpoint security measures even on employee’s own laptops – Educate on the risks of using public Wi-Fi
Address IoT Security
As the Internet of Things (IoT) expands, so do the associated risks. Inventory your IoT devices, regularly update their firmware, and implement network segmentation to isolate these devices.
Ready to make cybersecurity your New Year’s resolution? Contact Farmhouse Networking today. Our team of experts is ready to guide you through every step of enhancing your cybersecurity posture, ensuring that your business stays protected throughout 2025 and beyond. Let’s work together to create a robust, tailored cybersecurity strategy that meets your unique needs and keeps your business safe in the digital age.
For those that missed us this week, our CEO Scott Carr was one of the guest speaking panel and the event pictured above. During our discussion, the question was asked – “What is the one thing business owners can do to protect themselves from ransomware?” Scott’s answer was – “If you do nothing else, at the very least have a backup of your data. If anything goes wrong you will be able to go back to your previous data and skip paying the ransom.”
Why Backup?
Ransomware attacks have become an increasingly prevalent threat to businesses of all sizes. As cybercriminals continue to evolve their tactics, it’s crucial for organizations to implement robust defense strategies. One of the most effective ways to protect your business from the devastating effects of ransomware is through a comprehensive backup strategy.
The Rising Threat of Ransomware
Ransomware attacks have surged dramatically in recent years, with 2024 seeing unprecedented levels of both frequency and sophistication. In the first half of 2024 alone, the average extortion demand per ransomware attack exceeded $5.2 million, with a record-breaking payment of $75 million in March. These staggering figures underscore the critical need for businesses to fortify their defenses against such attacks.
The Role of Backups in Ransomware Protection
Data backups serve as a crucial line of defense against ransomware threats. They provide a safety net that can help your company prevent irreparable damage in the event of an attack. Here’s why backups are so important:
Added Data Security: By maintaining backups of your critical data, you remove one of the primary vectors for ransomware attacks. If you can still access your data from a backup, hackers lose their leverage in demanding a ransom
Recovery Options: Reliable and well-tested backups give ransomware victims more options. Without backups, organizations have limited choices for recovery. However, with confidence in their ability to restore from backups, businesses can make more nuanced decisions during ransomware recovery and negotiations.
Best Practices for Ransomware-Resilient Backups
To ensure your backups provide effective protection against ransomware, consider implementing these best practices:
Implement the 3-2-1 Backup Strategy: This strategy involves maintaining at least three copies of your data on two different storage types, with one copy kept offsite. This approach significantly reduces the risk of losing all your data in a single attack
Use Immutable Storage: Immutable backups cannot be modified, altered, or deleted for a specified period. This ensures that your backup data remains intact and tamper-proof, protecting against both accidental and malicious changes
Maintain Offline Backups: Keep a secondary offline backup copy that ransomware cannot reach. Network attached storage devices can be an effective method for this purpose.
Increase Backup Frequency: Consider backing up mission-critical data at least once per hour. This reduces the amount of data that could potentially be lost in a ransomware attack.
Employ Endpoint Protection: Use modern endpoint protection platforms that can detect ransomware processes as they begin, even if the type of ransomware is new and unknown.
The Business Impact of Ransomware
The consequences of a ransomware attack extend far beyond the immediate financial loss. Businesses may experience:
Extensive downtime, leading to significant revenue loss
Damaged reputation among customers and partners
Delayed project timelines
Potential loss of sensitive customer data
These impacts underscore the importance of a robust backup strategy as part of your overall cybersecurity plan.
Don’t wait until it’s too late to protect your business from the devastating effects of ransomware. Contact Farmhouse Networking today to develop a comprehensive backup and cybersecurity strategy tailored to your organization’s needs. Our expert team can help you implement robust protection measures, ensuring your business remains resilient in the face of evolving cyber threats. Secure your data, protect your reputation, and safeguard your bottom line—reach out to Farmhouse Networking now.
Zero trust enables secure, high-performance networks across distributed business sites.
Multi-location companies face unique challenges when it comes to maintaining consistent and efficient network performance across all their sites. A robust and optimized network is crucial for seamless operations, effective communication, and maintaining a competitive edge. Let’s explore how businesses can optimize their network performance across multiple locations.
The Importance of Network Optimization
For multi-location businesses, network optimization is not just about speed—it’s about creating a cohesive, secure, and efficient digital environment that supports productivity and growth. A well-optimized network ensures:
Consistent performance across all locations
Improved collaboration and communication
Enhanced security and data protection
Increased operational efficiency
Better customer experience
Key Strategies for Network Optimization
Network Monitoring and Analysis: Implementing comprehensive network monitoring tools allows businesses to gain real-time insights into their network performance across all locations. This proactive approach helps identify potential issues before they impact operations.
Traffic Prioritization: Utilizing Quality of Service (QoS) protocols to prioritize critical business applications ensures that essential services receive the necessary bandwidth, regardless of location.
Load Balancing: Distributing network traffic evenly across multiple servers or network links prevents any single point from becoming overwhelmed, ensuring smooth operations across all sites. This also avoids single points of failure.
Network Segmentation: Dividing the network into smaller, manageable segments can significantly reduce congestion and improve overall performance, especially for businesses with multiple locations.
Regular Hardware and Software Updates: Keeping network infrastructure up-to-date across all locations is crucial for maintaining optimal performance and security.
Secure Remote Connections: Satellite offices will need to connect back to the main office for specific resources like authentication, computer policies, and industry specific applications. Making sure these remote connections remain online and secure is essential to make sure remote offices stay productive.
Implementing Network Optimization Strategies
To effectively optimize your multi-location network:
Conduct a comprehensive network audit across all locations to identify performance bottlenecks and security vulnerabilities.
Implement unified network monitoring tools to gain visibility into performance across all sites.
Standardize network infrastructure and policies across locations to ensure consistency and ease of management.
Utilize cloud-based solutions for improved accessibility and scalability across multiple sites.
Regularly review and update your network optimization strategy to adapt to changing business needs and technological advancements.
The Role of Managed IT Services in Network Optimization
A Managed IT services provider can be instrumental in implementing and maintaining these optimization strategies:
Centralized Management: They provide a single point of contact for all network-related issues across locations.
Customized Solutions: Tailoring optimization strategies to meet the specific needs of each business location.
Continuous Improvement: Regularly assessing and upgrading network performance based on the latest technologies and best practices.
Disaster Recovery and Business Continuity: Implementing robust backup and recovery solutions to ensure business continuity across all locations.
Optimizing network performance for multi-location businesses is a complex but crucial task. By leveraging the expertise of a Managed IT services provider, businesses can ensure that their network infrastructure is not just a utility, but a strategic asset that drives growth and innovation.
Ready to take your multi-location network performance to the next level? Contact Farmhouse Networking today to get started on your network optimization journey. Our team of experts is ready to help you create a seamless, efficient, and secure network environment across all your business locations.
As our business continues to grow our focus is on providing white labeled Tier 3 IT support services, RMM as a service, and co-managed IT services. This blog will be highlighting tips for using PowerShell to deploy Synology Active Backup for Business.
Research
Found a support page from Synology that details how to edit the MSI file and deploy it via a Group Policy Object. We are using a similar method to edit the MSI package and deploy it from a local share to all computers via the RMM. You will need to configure a Synology Active Backup for Business template for PCs and download the MSI installer. We use a software called InstEd to edit the MSI installer as follows:
Click Property in the Tables list on the left. Enter the values for the following properties3:
USERNAME: Enter the username for accessing the Synology NAS.
NO_SHORTCUT: Enter “1” if you want to hide the Active Backup for Business Agent’s icon from the main menu of the end user’s device.
ADDRESS: Enter the IP address of the Synology NAS.
PASSWORD: Enter the password for accessing the Synology NAS.
ALLOW_UNTRUST: Enter “1” if you want to connect to the Synology NAS using an IP address instead of a domain or DDNS.
PROXY_ADDR, PROXY_PORT, PROXY_USERNAME, PROXY_PASSWORD: Enter these values only when users have to access your Synology NAS via proxy.
Click File > Save
Once done, upload to the local network share and take note of the share path – i.e. \\192.168.20.10\Support
Variables
$MSIArguments = This will include full file name of the Synology Active Backup for Business MSI installer – i.e. ‘Synology Active Backup for Business Agent-2.7.0-3221-x64.msi’
Script Snippet
Push-Location -Path '\\192.168.20.10\Support' -StackName 'Backup'
Set-Location -StackName 'Backup'

$MSIArguments = "/i Synology Active Backup for Business Agent-2.7.0-3221-x64.msi"

Start-Process "msiexec.exe" -ArgumentList $MSIArguments -Wait -NoNewWindow
The script will take several seconds to minutes to run based on the speed of the computer. The computers will start populating on their own into the Synology Active Backup for Business app.
If your company is a MSP or wants to become one and automation just seems out of reach, then contact usto run your RMM for you.
Cloud backups enable robust DR and BCP for seamless business operations.
Businesses face numerous threats that can disrupt operations and compromise critical data. From natural disasters to cyberattacks, the potential for catastrophic events looms large. This is where comprehensive disaster recovery and business continuity planning comes into play, offering a lifeline for organizations in times of crisis.
The Importance of Preparedness
Disaster recovery (DR) and business continuity planning (BCP) are essential components of any robust IT strategy. While often used interchangeably, these two concepts have distinct focuses:
Disaster Recovery primarily deals with restoring data access and IT infrastructure after a disaster. It’s about getting systems back online and operational as quickly as possible.
Business Continuity focuses on keeping the business operational during a disaster. It ensures that critical functions can continue even in unfavorable circumstances.
When combined, DR and BCP create a powerful shield against potential disruptions, minimizing downtime and protecting valuable data.
Benefits of a Comprehensive Plan
A well-crafted DR and BCP strategy offers numerous advantages:
Ensures Business Continuity: With a solid plan in place, businesses can quickly restart operations after a disaster, reducing costly downtime.
Enhances System Security: Integrated data protection and backup processes limit the impact of security threats like ransomware and malware.
Improves Customer Retention: A swift response to disasters instills confidence in customers, showcasing the organization’s reliability.
Reduces Recovery Costs: By enabling rapid system restoration, a robust plan helps avoid unnecessary financial losses.
Key Components of an Effective Plan
A comprehensive DR and BCP strategy should include:
Clear Communication Protocols: Ensuring all stakeholders know their roles and responsibilities during a crisis.
Regular Data Backups: Implementing backup solutions with both onsite and offsite aka cloud storage options.
Redundant Infrastructure: Establishing backup systems to maintain operations during primary system failures.
Employee Training: Conducting regular drills and awareness programs to prepare staff for potential disasters.
Regular Testing and Updates: Periodically reviewing and updating the plan to address evolving threats and business needs.
The Role of Managed IT Services
Partnering with a managed IT services provider can significantly enhance your DR and BCP efforts. These experts bring specialized knowledge and resources to:
Develop comprehensive strategies tailored to your business needs
Implement resilient backup and recovery solutions
Provide monitoring and rapid incident response
Conduct regular testing and plan updates
By leveraging managed IT services, businesses can ensure they’re prepared for any eventuality, minimizing the risk of prolonged downtime and data loss.
Don’t wait for disaster to strike before taking action. A proactive approach to DR and BCP can mean the difference between a minor setback and a major catastrophe for your business. Contact Farmhouse Networking today to start developing your comprehensive disaster recovery and business continuity plan. Our team of experts will work with you to assess your unique needs, identify potential risks, and create a tailored strategy to keep your business running smoothly, no matter what challenges arise. Don’t leave your business’s future to chance.
Protecting patient data and ensuring the security of your medical practice’s IT infrastructure is more critical than ever. With cyber threats constantly evolving, implementing strong cybersecurity measures is not just a good practice—it’s essential for maintaining patient trust, complying with regulations, and safeguarding your practice’s reputation.
The Growing Threat to Healthcare
Healthcare organizations are prime targets for cybercriminals due to the valuable nature of patient data. In recent years, the healthcare industry has experienced a surge in cyberattacks, with data breaches affecting millions of patients and costing healthcare providers billions of dollars.
Essential Cybersecurity Measures:
To protect your medical practice from these threats, consider implementing the following cybersecurity essentials:
Firewalls: A robust firewall acts as the first line of defense against unauthorized access to your network. It monitors incoming and outgoing traffic, blocking potential threats before they can infiltrate your systems.
Antivirus Software: Comprehensive antivirus solutions are crucial for detecting and preventing malware, ransomware, and other malicious software that could compromise patient data. Modern antivirus programs use advanced techniques like machine learning to identify and neutralize emerging threats in real-time.
Data Encryption: Encrypting sensitive patient information, both at rest and in transit, ensures that even if data is intercepted, it remains unreadable and unusable to unauthorized parties. This is particularly important for maintaining HIPAA compliance.
Regular Software Updates: Keeping all systems and software up-to-date with the latest security patches is vital for addressing known vulnerabilities and protecting against new threats.
Employee Training: Your staff is often the first line of defense against cyberattacks. Regular cybersecurity training can help employees recognize phishing attempts, practice good password hygiene, and follow proper data handling procedures.
The Role of Managed IT Services
While these measures are essential, implementing and maintaining a comprehensive cybersecurity strategy can be challenging for many medical practices. This is where managed IT services come into play. Managed IT service providers, like Farmhouse Networking, offer expertise and resources to ensure your practice’s cybersecurity measures are robust, up-to-date, and compliant with industry regulations. Here’s how managed IT can protect your patient data:
24/7 Monitoring and Threat Detection: Continuous surveillance of your network to identify and respond to potential threats before they cause damage.
Automated Updates and Patch Management: Ensuring all systems and software are current with the latest security updates.
Data Backup and Disaster Recovery: Implementing comprehensive backup solutions and disaster recovery plans to safeguard patient data in case of a breach or system failure.
Compliance Management: Helping your practice stay compliant with HIPAA and other relevant regulations through regular audits and updates to security protocols.
Advanced Security Solutions: Implementing enterprise-grade security measures that might be out of reach for smaller practices managing IT in-house.
In an era where cyber threats are constantly evolving, partnering with a managed IT service provider is one of the most effective ways to ensure your medical practice’s cybersecurity stays ahead of the curve. Farmhouse Networking offers comprehensive IT solutions tailored specifically for healthcare providers, combining local expertise with cutting-edge technology to keep your patient data safe and your practice secure. Don’t wait for a breach to occur before taking action. Call us at (541) 761-9549 or visit our website at www.farmhousenetworking.com to schedule a consultation.
Cloud solutions streamline charity IT for maximum impact and minimal costs.
Charities and nonprofit organizations can significantly enhance their impact and operational efficiency by optimizing their IT infrastructure. By strategically leveraging technology, these organizations can streamline workflow, improve communication, and ultimately better serve their mission and constituents.
Aligning Technology with Organizational Goals
The first step in optimizing IT infrastructure is to ensure that technology initiatives are aligned with the charity’s overall objectives. This alignment is crucial for several reasons:
– It ensures that technology investments directly contribute to the organization’s mission – It helps prioritize IT projects based on their potential impact – It allows for more effective allocation of limited resources
To achieve this alignment, charities should involve key stakeholders, including staff, volunteers, and board members, in the IT strategy development process. This collaborative approach ensures that diverse perspectives are considered and that the resulting strategy addresses the needs of all parts of the organization.
Assessing Current Infrastructure and Capabilities
Before implementing new technologies, it’s essential for charities to evaluate their existing IT infrastructure. This assessment should cover:
– Hardware and software inventory – Network capabilities – Data storage and management systems – Security measures
By understanding the current state of their IT infrastructure, charities can identify gaps, inefficiencies, and areas for improvement. This information forms the foundation for developing a comprehensive IT strategy that addresses the organization’s specific needs and challenges.
Embracing Cloud-Based Solutions
Many nonprofits are transitioning from legacy on-premise systems to cloud-based services, which offer numerous advantages:
– Scalability: Cloud services can easily grow with the organization – Cost-effectiveness: Pay-as-you-go models reduce upfront costs – Flexibility: Access to data and applications from anywhere – Automatic updates: Ensures the organization always has the latest features and security patches
For example, Microsoft Office 365 provides powerful tools for data analysis and collaboration, enabling charities to gain valuable insights from donor data and improve fundraising strategies.
Prioritizing Security and Data Protection
Given the sensitive nature of the data handled by charities, including donor information and financial records, security should be a top priority in their IT strategy. Key security measures to consider include:
– Implementing robust firewalls and next-gen antivirus software – Regularly updating and patching systems – Encrypting sensitive data – Providing staff training on cybersecurity best practices – Developing and enforcing data privacy policies
By prioritizing security, charities can protect their reputation, maintain donor trust, and avoid costly data breaches.
Implementing Effective IT Governance
To ensure the ongoing success of IT initiatives, charities should establish clear governance structures and support mechanisms. This includes:
– Defining roles and responsibilities for IT management – Creating processes for handling IT requests and incidents – Establishing an IT committee or designating a dedicated IT staff member – Developing policies for technology use and data management – Consider out-sourcing IT management to lower maintenance costs
Effective IT governance helps ensure that technology continues to serve the organization’s needs and that resources are used efficiently.
Addressing Technical Debt
Many nonprofits accumulate technical debt over time by choosing quick or cheap solutions over more sustainable options. To address this issue:
– Conduct regular audits of IT infrastructure – Identify and replace outdated or inefficient systems – Invest in modernization to reduce long-term maintenance costs and security risks
While addressing technical debt may require upfront investment, it can lead to significant cost savings and improved performance in the long run.
Navigating the complex world of IT infrastructure optimization can be challenging, especially for charities with limited resources. That’s where Farmhouse Networking comes in. Our team of experts specializes in helping nonprofit organizations leverage technology to maximize their impact and efficiency.
Ready to transform your charity’s IT infrastructure? Here’s how Farmhouse Networking can help:
Conduct a comprehensive assessment of your current IT setup
Develop a tailored strategy aligned with your organizational goals
Implement cost-effective cloud solutions to enhance flexibility and scalability
Strengthen your cybersecurity measures to protect sensitive data
Provide ongoing support and maintenance to ensure optimal performance
Don’t let outdated technology hold your charity back. Contact Farmhouse Networking today to schedule a free consultation. Together, we can harness the power of technology to amplify your mission and make a greater difference in the world. Call us at (541) 761-9549 or visit www.farmhousenetworking.com to get started on your IT optimization journey.
Let’s empower your charity with the right technology solutions. Reach out now and take the first step towards a more efficient, secure, and impactful future.
Secure your patient data with HIPAA-compliant managed IT: encryption, access controls, and continuous monitoring.
Ensuring the privacy and security of patient information is paramount. The Health Insurance Portability and Accountability Act (HIPAA) sets stringent standards for protecting sensitive patient data. For medical practices, staying compliant with HIPAA regulations can be a daunting task, especially with the increasing complexity of IT systems. This is where a Managed IT Service Provider (MSP) can play a crucial role. In this blog, we’ll explore how partnering with an MSP can help your medical practice remain compliant with HIPAA regulations for data privacy and security.
Understanding HIPAA Compliance
HIPAA compliance involves adhering to a set of rules and regulations designed to safeguard Protected Health Information (PHI). These rules are divided into several key areas:
Privacy Rule: Governs the use and disclosure of PHI.
Security Rule: Establishes standards for protecting electronic PHI (ePHI) through administrative, physical, and technical safeguards.
Breach Notification Rule: Requires covered entities to notify affected individuals, the Secretary of Health and Human Services (HHS), and, in some cases, the media, of a breach of unsecured PHI.
Enforcement Rule: Outlines the penalties for non-compliance and the procedures for investigations and hearings.
The Role of Managed IT in HIPAA Compliance
A Managed IT Service Provider can offer a range of services that help ensure your medical practice remains compliant with HIPAA regulations. Here are some key ways an MSP can assist:
Risk Assessment and Management: HIPAA requires regular risk assessments to identify potential vulnerabilities in your IT systems. An MSP can conduct comprehensive risk assessments to:
Identify and evaluate risks to ePHI.
Implement measures to mitigate identified risks.
Continuously monitor and update risk management strategies.
Data Encryption and Secure Communication: Encrypting ePHI is a critical component of HIPAA compliance. An MSP can implement robust encryption protocols to ensure that data is protected both at rest and in transit. Additionally, they can set up secure communication channels, such as encrypted email, secure messaging platforms, and encrypted file sharing, to protect sensitive information.
Access Control and Authentication: HIPAA mandates strict access controls to ensure that only authorized personnel can access ePHI. An MSP can help by:
Implementing role-based access controls (RBAC).- all users in a group and only specific groups get access to specific things
Setting up multi-factor authentication (MFA) to add an extra layer of security.
Regularly reviewing and updating access permissions.
Backup and Disaster Recovery: Data loss can have severe consequences for HIPAA compliance. An MSP can design and implement a robust backup and disaster recovery plan to ensure that ePHI is regularly backed up and can be quickly restored in the event of data loss or a cyberattack.
Security Awareness Training: Human error is a significant factor in many data breaches. An MSP can provide ongoing security awareness training for your staff to:
Educate them about HIPAA regulations and the importance of data privacy.
Teach best practices for identifying and responding to potential security threats.
Conduct regular phishing simulations to test and improve staff vigilance.
Continuous Monitoring and Incident Response: HIPAA requires continuous monitoring of IT systems to detect and respond to security incidents promptly. An MSP can offer:
24/7 monitoring of your IT infrastructure.
Advanced threat detection and response solutions.
Incident response planning and execution to minimize the impact of security breaches.
Benefits of Partnering with a Managed IT Provider
Partnering with an MSP for HIPAA compliance offers several benefits:
Expertise: MSPs have specialized knowledge and experience in healthcare IT and HIPAA regulations.
Cost-Effectiveness: Outsourcing IT management can be more cost-effective than maintaining an in-house IT team.
Focus on Core Activities: With IT management in the hands of experts, your medical practice can focus on providing quality patient care.
Scalability: MSPs can scale their services to meet the growing needs of your practice.
Ensuring HIPAA compliance is a complex but essential task for any medical practice. By partnering with a Managed IT Service Provider, you can leverage their expertise and resources to safeguard patient data, mitigate risks, and maintain compliance with HIPAA regulations. This not only protects your practice from potential penalties but also builds trust with your patients, knowing their sensitive information is in safe hands. For medical practices looking to navigate the intricacies of HIPAA compliance, a Managed IT Service Provider like Farmhouse Networking can be an invaluable ally in maintaining the highest standards of data privacy and security.
CrowdStrike Falcon update triggers massive IT outage across cloud services
The recent CrowdStrike IT outage on July 19, 2024, caused by a defective update for Windows, serves as a stark reminder of the importance of managing IT infrastructure and proactive measures to prevent system downtime. While no system is entirely immune to outages, there are several strategies businesses can implement to minimize the risk and impact of such incidents.
Key Strategies to Prevent IT Outages
Improve Continuous Integration / Continuous Deployment (CI/CD) Practices: One of the most effective ways to prevent outages caused by software updates is to enhance CI/CD practices. This approach involves:
Automating the testing and deployment process
Implementing rigorous quality assurance checks
Using staging environments to test updates before full deployment
Gradually rolling out updates to detect issues early
By improving CI/CD practices, businesses can catch potential issues before they affect the entire network, reducing the likelihood of widespread outages.
Implement Comprehensive Load / Failure Testing: Regular load testing is crucial to ensure that systems can handle typical use cases and determine their potential in high use scenarios. A game plan should also be put in place for when systems fail to map out the road to recovery. This involves:
Simulating various levels of user activity
Identifying performance bottlenecks
Optimizing system architecture and configuration
Preparing for crisis scenarios, such as partial resource failures
Practice response to system failures before they become reality
Load / failure testing helps businesses understand their system’s limitations and address potential issues before they lead to outages.
Ensure Proper Scalability: As businesses grow, their IT infrastructure must be able to scale accordingly. This includes:
Designing systems with future growth in mind
Utilizing cloud technologies for flexible resource allocation
Regularly reviewing and updating system architecture
Implementing efficient systems that can handle increased business
Proper scalability ensures that systems can continue to function effectively as demand increases, reducing the risk of outages due to overload.
Enable Automatic Updates with Caution: While automatic updates can help keep systems secure and up-to-date, they should be implemented carefully. Best practices include:
Testing updates in a controlled environment before widespread deployment
Staggering updates across different system components
Having a rollback plan in case of issues
Monitoring systems closely after updates are applied
Automatic updates can help prevent security vulnerabilities, but they must be managed carefully to avoid introducing new issues.
Implement Comprehensive Monitoring: A robust monitoring system is essential for detecting and addressing potential issues before they escalate into outages. This includes:
Using a centralized monitoring platform for all IT infrastructure
Outsourcing it management is resources are not available
Setting up alerts for unusual system behavior or performance metrics
Implementing predictive analytics to identify potential issues early
Regularly reviewing and updating monitoring parameters
Comprehensive monitoring allows businesses to take a proactive approach to system management, reducing the risk of unexpected outages.
Conduct Regular Employee Training: Human error is a common cause of IT outages. Regular employee training can help mitigate this risk. Training should cover:
Best practices for system usage
Recognizing and reporting potential security threats
Proper procedures for applying updates and patches
Emergency response protocols in case of system issues
Well-trained employees are less likely to make mistakes that could lead to outages and are better equipped to respond effectively when issues do occur.
Don’t let IT outages disrupt your business. Take action now to protect your company’s technology infrastructure. Call Farmhouse Networking today at (541) 761-9549 to schedule a comprehensive IT assessment and learn how our expert team can implement strategies to prevent costly downtime. Secure your business’s future with proactive IT management.
Safeguarding your business data is paramount. Cyber threats are ever-evolving, and data breaches can have severe consequences. To fortify your business defenses, consider implementing the following security and encryption tools:
Operating System Encryption
Encryption is the process where normal data is transformed into something unreadable without the keys unlock it. Windows has encryption built in using BitLocker software in conjunction with modern hardware to keep data safe on physical hard drives. In case a computer is stolen or lost the data is unreadable (assuming the password protecting the computer is strong).
Virtual Private Network / Zero Trust Network Access
Whenever employees are remote or working from home they need to be able to connect to company resources without endangering company data. This is best done through Zero Trust Network Access (ZTNA) which is the next-gen replacement for the older virtual private network connection ZTNA assumes that all connections are threats unless proven otherwise and those who are connecting must have their computers tested to make sure they are safe. This approach also only allows users to connect to the resources that are specifically needed to function.
Antivirus / Extended Detection and Response
One key to staying cyber secure is to recognize and repel threats before they do any damage. Utilizing AI and automation extended detection and response (XDR) is the modern replacement for antivirus. It is able to detect behavior patterns that malicious software and hackers use when attacking your systems then automatically undue any changes they have made.
Email Encryption and SPAM Filtering
When sending sensitive data via email it is now the standard to send it via encrypted channels with each message also being encrypted. Most companies that provide encryption also provide SPAM filtering which keeps phishing, spoofing, and malicious emails from targeting employees. This is often the most effective means hackers use to gain a foot hold in networks.
Backups
There will inevitably be times when hackers are able to breach even the best defenses, so the only recourse at that time is to have good backups in multiple locations to recover once the attacker is repelled. Without good backups many companies have had to pay ransoms and hope for a response or go out of business.
Remember, data security is an ongoing process. Combine these tools with user education and strong password practices,. Stay vigilant, adapt to new threats, and invest wisely in protecting your digital assets and reputation. Call Farmhouse Networking to advise you on how to best secure your business.
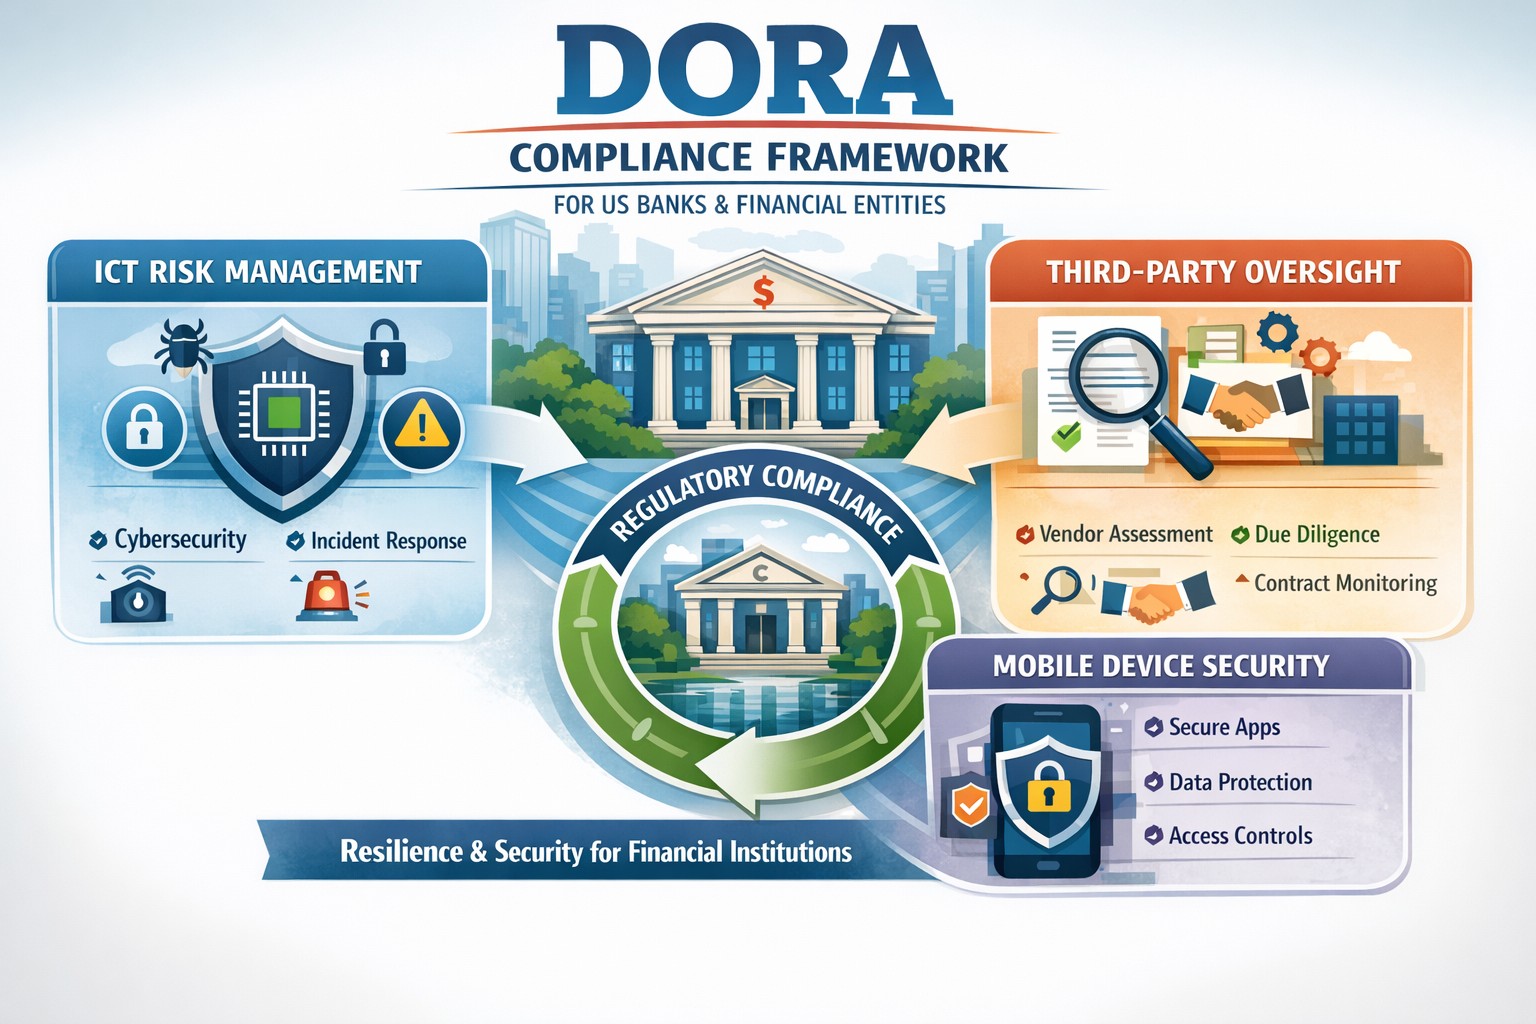
Navigating DORA changes with robust BYOD MDM for financial resilience
For US financial institutions, regulatory frameworks play a pivotal role in shaping operational protocols, enhancing security measures, and ensuring the resilience of the financial sector against a myriad of risks and vulnerabilities. Among these regulatory frameworks, the Digital Operational Resilience Act (DORA) stands out as a beacon of change, heralding a new era of compliance requirements and operational standards for financial entities.
This comprehensive guide aims to demystify the intricacies of DORA, shedding light on its key provisions, compliance requirements, and the broader implications for information and communication technology (ICT) within the financial sector. We will provide actionable insights into navigating these changes, adopting effective strategies for adaptation, overcoming potential challenges, and adhering to best practices for ensuring DORA compliance. As we delve into this exploration, the role of technology in facilitating compliance and the future landscape of US financial institutions under DORA’s influence will also be examined.
Introduction to DORA and its impact on US financial institutions
The introduction of DORA is a testament to the increasing recognition of the critical role that digital operational resilience plays in the stability and security of financial institutions. When cyber threats are looming large and the dependency on ICT infrastructures has become indispensable, DORA emerges as a regulatory response to the need for a harmonized, rigorous framework aimed at bolstering the digital defenses of financial entities. Its impact on US financial institutions is far-reaching, affecting not only the internal processes and technological deployments but also the strategic orientation towards digital operational resilience.
For US financial institutions, DORA represents both a challenge and an opportunity. The challenge lies in the comprehensive nature of the requirements, demanding a thorough reassessment of existing ICT systems, operational policies, and compliance mechanisms. On the other hand, the opportunity emerges from the potential for enhanced operational resilience, reduced vulnerability to cyber incidents, and a stronger competitive position in a digitally driven market. The anticipation of these changes has already begun to shape the strategic planning and investment priorities of financial institutions, with a clear focus on aligning with DORA’s stipulations.
The significance of DORA extends beyond mere compliance. It encapsulates a paradigm shift towards viewing digital operational resilience as a cornerstone of financial stability and consumer trust. As such, the efforts to meet DORA’s requirements are not just about adhering to a regulatory mandate but about embracing a culture of continuous improvement and risk-awareness in the digital domain. This cultural shift is fundamental to navigating the changes brought about by DORA and leveraging them to build a more resilient, trustworthy financial sector.
Understanding the key provisions of DORA
DORA is structured around several key provisions that collectively aim to enhance the digital operational resilience of financial institutions. These provisions cover a broad spectrum of requirements, from ICT risk management and incident reporting to third-party dependency management and testing of digital defenses. Understanding these key provisions is essential for financial institutions to grasp the full extent of DORA’s implications and to formulate a coherent strategy for compliance.
The first of these provisions centers on robust ICT risk management practices. Financial institutions are required to implement comprehensive risk management frameworks that can identify, assess, mitigate, and monitor ICT risks. This entails not only the deployment of advanced security measures and protocols but also the establishment of governance structures that ensure continuous oversight and accountability for ICT risk management.
Another critical provision of DORA pertains to the reporting of significant cyber incidents. Financial institutions must establish mechanisms for timely detection and reporting of such incidents to relevant regulatory authorities. This enhances the collective resilience of the financial sector by enabling a coordinated response to cyber threats and the sharing of critical information that can prevent the propagation of cyberattacks.
Lastly, DORA places a strong emphasis on the management of third-party risks. Given the interconnected nature of today’s financial ecosystem, where institutions rely heavily on external vendors for ICT services, DORA mandates stringent due diligence, monitoring, and contractual safeguards to manage the risks associated with third-party dependencies. This includes the requirement for financial institutions to ensure that their third-party providers adhere to equivalent standards of digital operational resilience.
Implications of DORA on information and communication technology (ICT)
The implications of DORA on ICT within financial institutions are profound, encompassing both the technological infrastructure and the operational processes that underpin the institution’s digital activities. At its core, DORA seeks to ensure that financial institutions have resilient, secure, and efficient ICT systems capable of withstanding a wide range of digital threats and challenges.
One of the primary implications relates to the enhancement of cybersecurity measures. DORA drives financial institutions to adopt state-of-the-art security technologies and practices, from advanced encryption methods and intrusion detection systems to comprehensive data protection protocols. This not only strengthens the institution’s defenses against cyberattacks but also fosters a culture of cybersecurity awareness and vigilance among employees and stakeholders.
Another significant implication is the focus on operational continuity and disaster recovery. DORA mandates that financial institutions develop and test robust business continuity plans (BCPs) and disaster recovery strategies (DRS) that ensure the institution can maintain or quickly resume critical operations in the event of an ICT-related disruption. This requires a careful analysis of critical business functions, the identification of potential vulnerabilities, and the implementation of measures to mitigate these risks.
Additionally, DORA underscores the importance of ICT governance and accountability. Financial institutions are expected to establish clear governance structures that define roles, responsibilities, and accountability for ICT risk management. This involves senior management taking an active role in overseeing ICT strategies, ensuring that digital operational resilience is embedded in the institution’s strategic planning and decision-making processes.
Navigating the changes brought by DORA in the financial sector
Navigating the changes brought by DORA requires a strategic, proactive approach that goes beyond mere compliance. Financial institutions must view these changes as an opportunity to enhance their operational resilience, competitive advantage, and trustworthiness in the digital age. This involves embracing a holistic view of digital operational resilience, integrating it into the institution’s overall strategic framework, and fostering a culture of continuous improvement and innovation.
The first step in this journey is to conduct a comprehensive assessment of the institution’s current ICT landscape and operational practices. This assessment should identify gaps in compliance with DORA’s provisions, areas of vulnerability to digital risks, and opportunities for enhancing digital operational resilience. Based on this assessment, financial institutions can develop a tailored action plan that addresses these gaps, leverages technological innovations, and aligns with the institution’s strategic objectives.
Engagement and collaboration across the organization are also crucial for successfully navigating the changes brought by DORA. This involves fostering an inclusive dialogue among stakeholders, including senior management, ICT professionals, risk managers, and operational staff, to ensure a shared understanding and commitment to digital operational resilience. Training and awareness programs can also play a key role in equipping employees with the knowledge and skills needed to contribute to the institution’s resilience efforts.
Furthermore, financial institutions should leverage the potential of technology to facilitate compliance and enhance operational resilience. This includes exploring advanced technologies such as artificial intelligence (AI), machine learning (ML), and blockchain, which can offer innovative solutions for risk management, incident detection, and secure transactions. Technology can also enable more efficient and effective compliance processes, from automated reporting mechanisms to real-time monitoring of third-party risks.
Strategies for adapting to DORA’s requirements
Adapting to DORA’s requirements necessitates a strategic approach that aligns with the institution’s operational realities and long-term objectives. One effective strategy is to prioritize the institution’s efforts based on the criticality of different ICT systems and processes, focusing initially on areas that present the highest risk or are most crucial for the institution’s operations. This prioritization helps to allocate resources efficiently and achieve significant enhancements in digital operational resilience.
Another key strategy involves fostering partnerships and collaboration both within the financial sector and with external technology providers. Collaborative initiatives can facilitate the sharing of best practices, insights, and experiences related to DORA compliance and digital operational resilience. Engaging with technology providers, like Farmhouse Networking, can also enable financial institutions to access innovative solutions and expertise that support compliance efforts and enhance the institution’s digital capabilities.
Continuous monitoring and evaluation are also essential for adapting to DORA’s requirements. Financial institutions should establish mechanisms for ongoing assessment of their compliance status, digital risk landscape, and the effectiveness of implemented resilience measures. This enables the institution to identify emerging risks, adapt to changes in the regulatory environment, and continuously improve its digital operational resilience.
Key challenges faced by financial institutions in implementing DORA
Implementing DORA presents a range of challenges for financial institutions, from the complexity of compliance requirements to the need for significant investments in technology and skills. One of the primary challenges is the integration of DORA’s provisions into the institution’s existing risk management and operational frameworks. This requires a comprehensive understanding of DORA’s requirements, as well as the ability to align these with the institution’s processes and objectives.
Another significant challenge is the management of third-party risks. The reliance on external providers for critical ICT services introduces a layer of complexity to compliance efforts, necessitating thorough due diligence, effective contractual arrangements, and ongoing monitoring. Ensuring that third-party providers adhere to equivalent standards of digital operational resilience can be a daunting task, requiring dedicated resources and expertise.
Additionally, the rapid pace of technological change and the evolving cyber threat landscape pose challenges for maintaining compliance and ensuring continuous digital operational resilience. Financial institutions must remain agile, constantly updating their risk assessments, cybersecurity measures, and resilience strategies to address new vulnerabilities and threats.
Best practices for ensuring DORA compliance
Ensuring DORA compliance requires a structured, diligent approach that encompasses several best practices. One of the foundational best practices is the establishment of a cross-functional team dedicated to DORA compliance. This team should include representatives from various departments, including ICT, risk management, legal, and operations, ensuring a comprehensive perspective on compliance efforts and facilitating effective coordination across the institution.
Developing a detailed compliance roadmap is another critical best practice. This roadmap should outline the key steps and milestones for achieving compliance, from initial assessments and gap analyses to the implementation of required measures and ongoing monitoring. The roadmap should also include timelines and responsibilities, providing a clear framework for the institution’s compliance efforts.
Continuous training and awareness programs are also essential for ensuring DORA compliance. Financial institutions should invest in educating their employees about the importance of digital operational resilience, the specific requirements of DORA, and their roles and responsibilities in maintaining compliance. Training programs should be regularly updated to reflect changes in the regulatory environment and emerging best practices.
Furthermore, leveraging technology can significantly enhance compliance efforts. Advanced technologies such as AI, ML, and blockchain can offer innovative solutions for risk assessment, incident detection, and secure data management. Financial institutions should explore these technologies, assessing their potential to support compliance objectives and enhance overall digital operational resilience.
The role of technology in facilitating DORA compliance
Technology plays a crucial role in facilitating DORA compliance, offering powerful tools and solutions that can enhance digital operational resilience and streamline compliance processes. One of the key areas where technology can make a significant impact is in risk assessment and management. Advanced analytics, AI, and ML can enable financial institutions to conduct more sophisticated risk assessments, identifying potential vulnerabilities and threats with greater accuracy and efficiency.
Incident detection and response is another area where technology can provide substantial benefits. Automated monitoring systems, intrusion detection technologies, and cybersecurity platforms can help financial institutions to quickly identify and respond to cyber incidents, minimizing their impact and ensuring timely reporting to regulatory authorities.
Technology can also support the management of third-party risks. Platforms and tools for vendor risk management enable financial institutions to conduct thorough due diligence, monitor third-party providers’ compliance with DORA requirements, and manage contractual arrangements more effectively. This facilitates a more robust approach to managing the risks associated with external ICT service providers.
Moreover, technology can enhance the efficiency of compliance processes, from automated reporting mechanisms to digital record-keeping systems. These technologies can reduce the administrative burden of compliance, allowing financial institutions to focus more resources on enhancing their digital operational resilience and providing value to their customers.
For financial institutions seeking to navigate the complexities of DORA compliance and enhance their digital operational resilience, partnering with expert service providers can offer valuable support. Contact Farmhouse Networking to manage your company’s ICT and protect from cyber threats, ensuring you stay ahead of the regulatory changes and build a stronger, more resilient financial institution for the future.
Relying on one IT guy can expose your small business to downtime, data loss, and security vulnerabilities—managed IT services offer stronger protection.
The role of Information Technology (IT) in business success cannot be overstated. IT systems and infrastructure form the backbone of modern businesses, facilitating communication, data management, and efficient workflow. From managing customer databases to ensuring network security, IT plays a crucial role in driving productivity and competitiveness. However, many businesses make the mistake of relying on a single IT guy to handle all their technological needs. In this article, I will discuss the risks associated with this approach and the importance of adopting a team-based approach to IT support.
The risks of relying on a single IT guy
Lack of expertise and knowledge
When you rely on a single IT guy, you are limited to their individual skills and expertise. While they may be knowledgeable in certain areas, they may not possess the breadth of knowledge required to handle all aspects of your business’s IT infrastructure. IT is a vast field that encompasses various domains such as network administration, cybersecurity, software development, and hardware maintenance. By relying on a single guy, you risk missing out on specialized expertise that could greatly benefit your business.
Limited availability and support
Another significant risk of relying on a single IT guy is limited availability and support. IT issues can arise at any time, and if your IT guy is unavailable or overwhelmed with other responsibilities, it can lead to significant downtime and disruptions in your business operations. With a single point of contact, you may have to wait for extended periods before your IT issues are resolved, resulting in decreased productivity and potential financial losses.
Single point of failure
Relying on a single IT guy also means that your business is vulnerable to a single point of failure. If your IT guy falls ill, takes a vacation, or leaves the company, you may be left without any IT support. Singular IT techs often don’t have the time or resources to properly document procedures and critical passwords, so when they go this information is lost. This can be particularly problematic during critical times when you need immediate assistance. Having a backup plan or a team of IT professionals ensures that your business operations can continue uninterrupted, even if one person is unavailable.
The impact of downtime on business operations
Downtime can have severe consequences on your business operations. Every minute your systems are down translates to lost revenue, missed opportunities, and frustrated customers. According to a study conducted by Gartner, the average cost of IT downtime is $5,600 per minute. Imagine the financial implications if your IT guy is unavailable for an extended period. With a team-based approach to IT support, you can minimize downtime and ensure swift resolution of any issues, thereby safeguarding your business’s success.
The importance of a team approach to IT support
Adopting a team approach to IT support offers numerous benefits for your business. Firstly, it provides a diverse set of skills and expertise that can be leveraged to address various IT challenges effectively. Each team member brings their unique knowledge and experience, allowing for comprehensive and well-rounded support. Additionally, with a team, you have the advantage of increased availability and faster response times. By distributing responsibilities among team members, you can ensure that someone is always available to address your IT needs promptly.
The benefits of outsourcing IT support
Outsourcing IT support is a viable solution for businesses looking to avoid the risks associated with relying on a single IT guy. Outsourcing allows you to tap into a pool of talented professionals with specialized expertise in different IT domains. Moreover, outsourcing IT support can often be more cost-effective than hiring a full-time IT staff, especially for small and medium-sized businesses. By partnering with an external IT support provider, like Farmhouse Networking, you can access a wide range of services, including network monitoring, cybersecurity, data backup, and software maintenance, all while enjoying the benefits of a dedicated team.
Finding the right IT support provider
Finding the right IT support provider is crucial to ensuring a successful and secure IT infrastructure. When evaluating potential providers, consider their experience, track record, and the range of services they offer. Look for certifications and qualifications that demonstrate their expertise and commitment to quality. It is also essential to assess their responsiveness and availability to ensure that they can meet your business’s IT needs promptly. Ask them about their record keeping habits, make sure they document everything and keep your information secure with industry standard protocols. By conducting thorough research and seeking recommendations, you can find an IT support provider that aligns with your business goals and requirements.
By adopting a team-based approach to IT support or outsourcing your IT needs, you can mitigate these risks and ensure a successful and secure IT infrastructure. Don’t get stuck when your IT guy no longer responds; contact us to experience the comfort of having a team look after your business IT. With the right IT support provider, you can focus on growing your business while leaving your technological needs in capable hands.
And God will generously provide all you need. Then you will always have everything you need and plenty left over to share with others. As the Scriptures say, “They share freely and give generously to the poor. Their good deeds will be remembered forever.” For God is the one who provides seed for the farmer and then bread to eat. In the same way, he will provide and increase your resources and then produce a great harvest of generosity in you. - 2 Corinthians 9:8-10
We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.