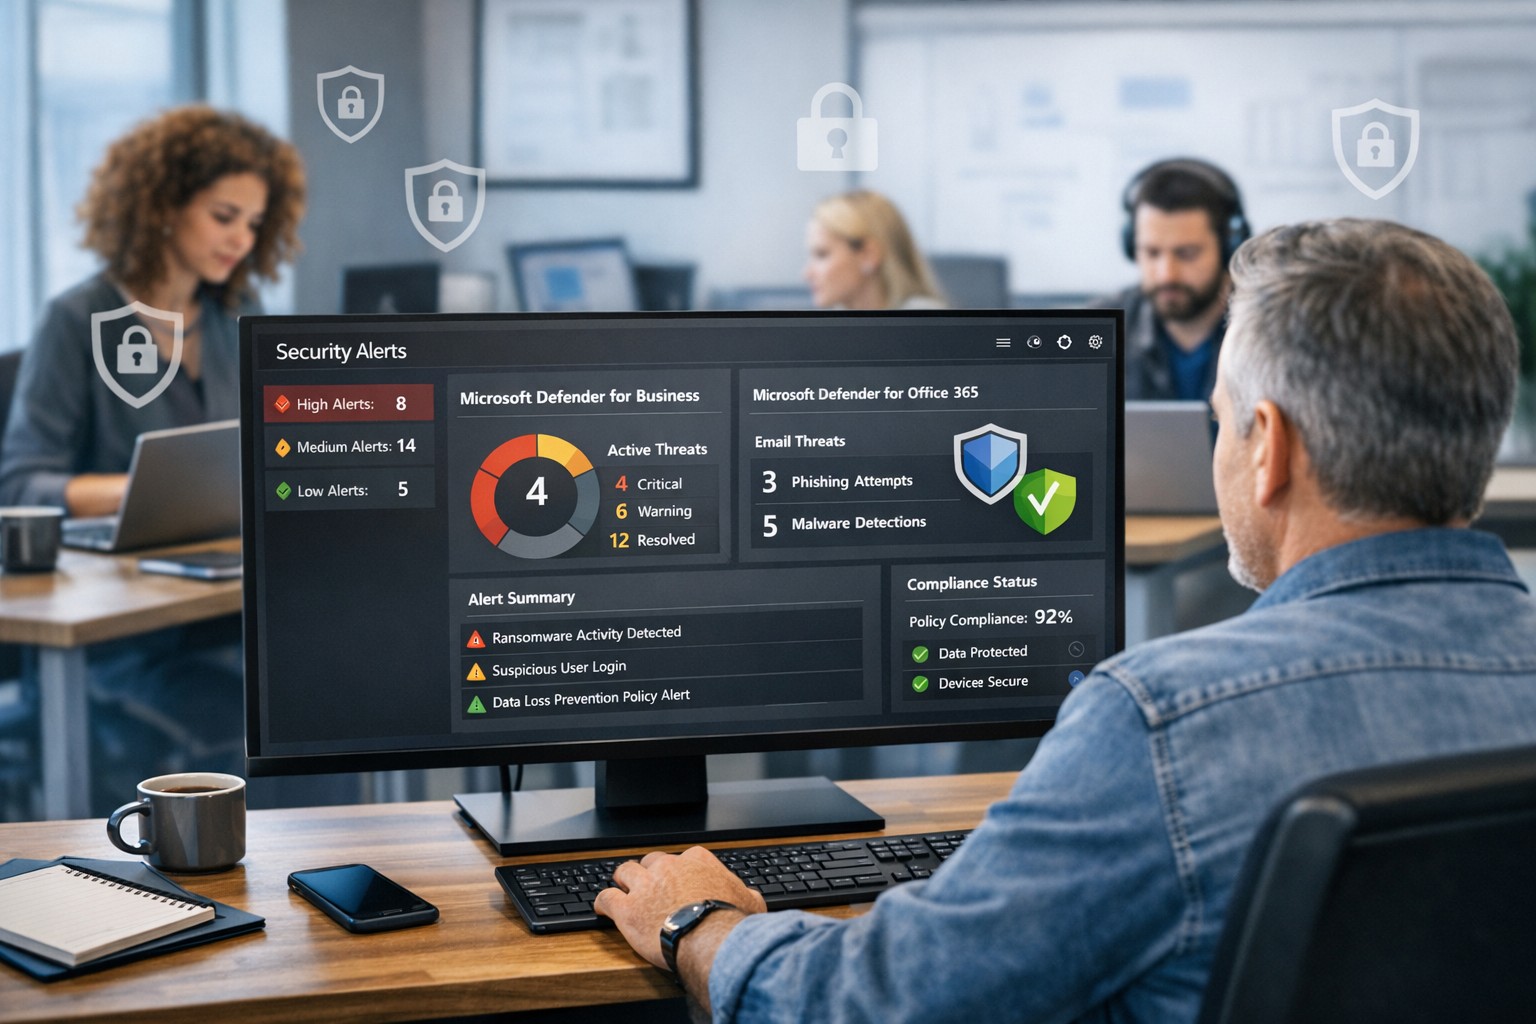
Protect your company with Microsoft security solutions: Microsoft Defender for Business and Microsoft 365 security help small and mid‑sized businesses block ransomware, phishing, and data breaches.
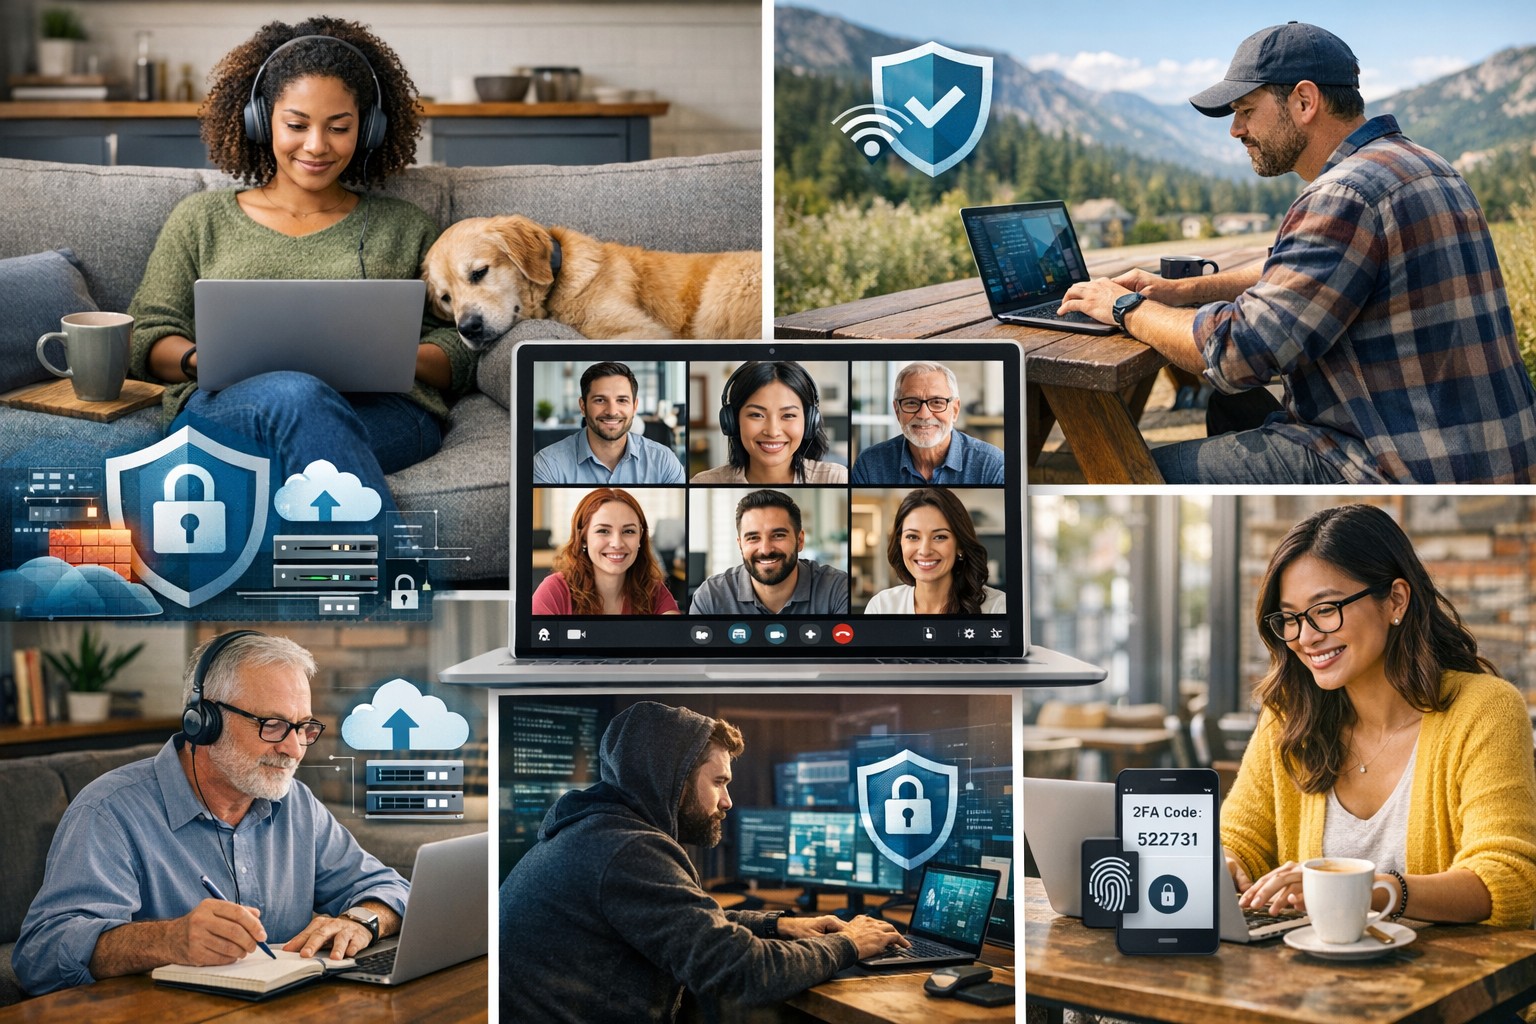
Understanding the six types of remote workers helps business owners create effective IT strategies for secure and productive remote teams.
Remote and hybrid work are here to stay. The challenge for business owners isn’t just keeping people connected — it’s understanding how different types of remote employees work best and what they need to succeed. Each worker type has unique technology, communication, and security requirements. Knowing these differences allows you to design a smart remote work strategy that boosts productivity, security, and morale.
The Six Types of Remote Workers and What They Need
1. The Independent Expert
These are the self-driven specialists who know their craft and value flexibility. They dislike micromanagement and prefer getting results on their own terms. How to support them: Ensure secure system access through a VPN and cloud-based tools. Automate routine updates to reduce interruptions, and provide strong endpoint protection to guard data while they work independently.
2. The Collaborative Communicator
This group thrives on constant interaction and quick collaboration. They drive team culture and creativity but can feel isolated when technology fails. How to support them: Use reliable communication tools like Slack, Microsoft Teams, or Zoom — and make sure your network bandwidth and security policies support uninterrupted real-time collaboration. Encourage scheduled check-ins to keep morale high and information flowing.
3. The Road Warrior
Always on the move, these employees rely on mobile devices and public networks. Field service reps, consultants, or remote managers often fall into this category. How to support them: Implement mobile device management (MDM) software, enforce two-factor authentication, and train employees on safe Wi-Fi practices. Cloud-based storage with encryption protects their data while ensuring accessibility from anywhere.
4. The Structured Performer
These workers thrive on order and clarity. They rely on defined rules, timelines, and expectations to perform well remotely. How to support them: Standardize communication and file-sharing tools, and document IT policies. Use dashboards and project management platforms like Trello or Asana to maintain structured workflows and consistent accountability.
5. The Emerging Remote Starter
New to remote work, these employees often need extra guidance, consistent access to IT resources, and reassurance that help is available when technology inevitably fails. How to support them: Provide onboarding sessions covering remote setup, company security protocols, and common troubleshooting steps. Make sure they have access to your IT helpdesk for instant support and schedule regular one-on-one check-ins as they get comfortable with their new environment.
6. The Hybrid Connector
They split time between office and home, juggling two environments with different setups. Seamless syncing is critical to maintain efficiency. How to support them: Standardize software, data access, and authentication across both locations. Unified communication systems and synchronized hardware (like docking stations and remote desktops) ensure their transition between workspaces is frictionless.
Practical Steps for Business Owners and IT Teams
Supporting these different worker types doesn’t require six distinct systems. Instead, focus on building a flexible IT framework that adapts to everyone’s needs:
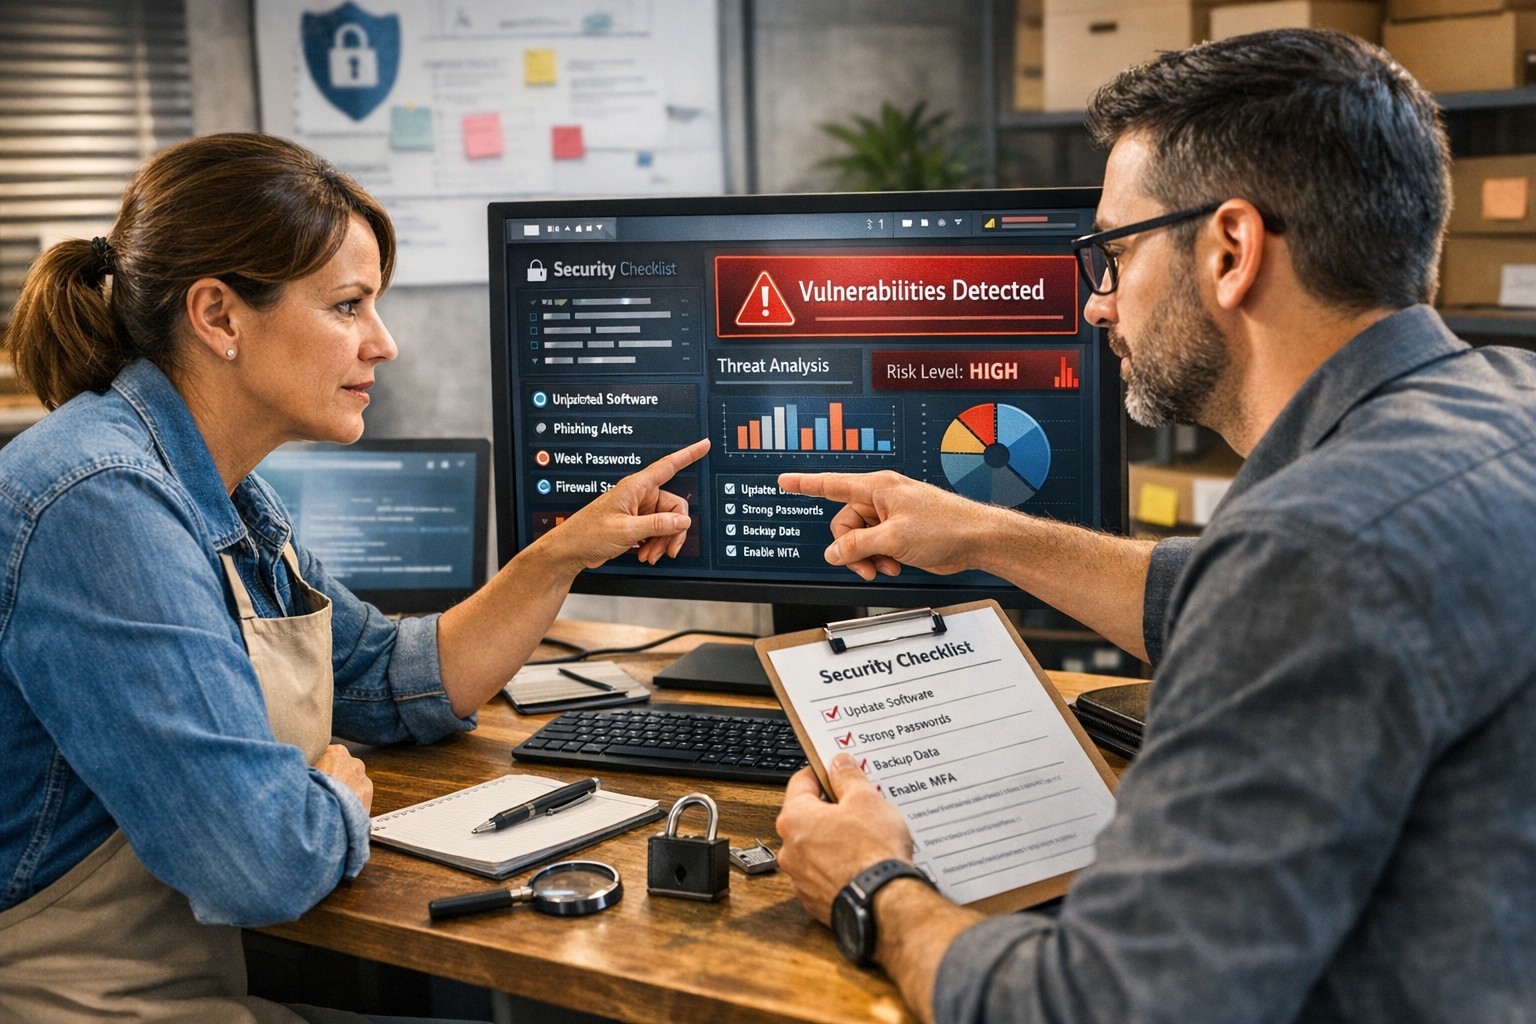
Audit your current IT environment to identify weak spots in connectivity, access, and cybersecurity.
Segment employees by work type and align their tools accordingly.
Standardize collaboration platforms to minimize confusion and ensure security consistency.
Implement cybersecurity best practices: firewalls, MFA, regular backups, and continuous network monitoring.
Train your team on safe remote practices to reduce phishing and human errors.
Create IT response and recovery plans for downtime or breaches — prevention is cheaper than disruption.
When IT is intentional and tailored, your business operates efficiently regardless of where employees log in.
Client Questions Answered
Q: How do I keep remote employees productive without micromanaging? A: Use transparent project management tools that track results, not time. Metrics-based performance systems give employees freedom while keeping you informed.
Q: Are cloud applications like Microsoft 365 and Google Workspace safe for remote work? A: They are — when configured properly. Encryption, file permissions, multi-factor authentication, and user activity logging are essential security layers.
Q: What’s the key to balancing flexibility with network security? A: Centralized IT management. By having a managed service provider monitor devices and apply consistent policies, you maintain both freedom and control.
How Farmhouse Networking Helps
Farmhouse Networking specializes in helping small businesses master remote and hybrid work environments. Whether your challenge is cybersecurity, employee onboarding, or remote infrastructure stability, our team designs tailored IT ecosystems that match how your people actually work.
We help you:
Identify which remote worker types make up your team.
Implement secure cloud access, VPNs, and remote monitoring.
Provide proactive IT support that keeps downtime minimal.
Strengthen your cybersecurity posture with continuous network protection.
Our goal is simple — to make your remote operations secure, seamless, and scalable.
Ready to build a smarter, more resilient remote workforce? Contact Farmhouse Networking at support@farmhousenetworking.com to learn how we can optimize your remote work systems and empower your team to perform at their best — wherever they are.
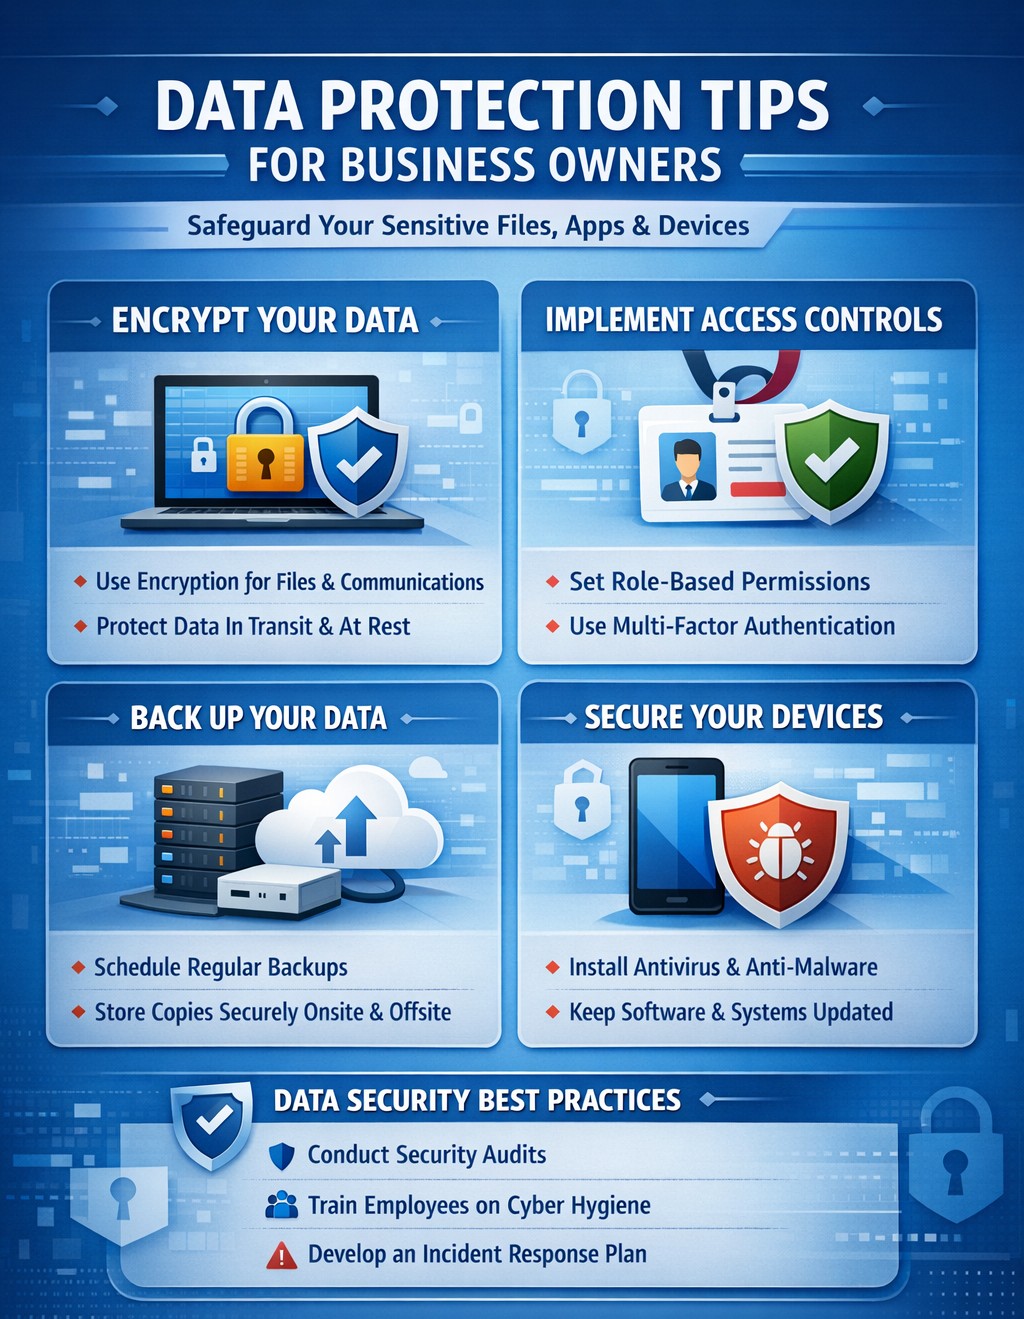
Essential data security measures: encryption, backups, and training protect small businesses from cyber threats.
Business data—customer records, financials, and intellectual property—is your lifeline. A single breach can cost thousands in downtime and lost trust, with 43% of cyberattacks targeting small firms.
Why Data Protection Matters Now
Cyber threats hit small businesses hardest due to limited resources. Ransomware, phishing, and insider errors lead to average losses of $25,000 per incident. Regulations like CCPA and GDPR mandate compliance, with fines up to 4% of revenue for violations. Protecting data safeguards profits, reputation, and legal standing.
Practical Action Steps
Implement these steps with your IT team for immediate impact.
Conduct a Data Audit: Inventory all data types (customer PII, emails, backups). Classify by sensitivity and map storage/access points. Set retention policies to delete unneeded info.
Secure Backups: Automate daily cloud backups (e.g., encrypted AWS S3). Test restores quarterly. Use 3-2-1 rule: 3 copies, 2 media types, 1 offsite.
Enable Encryption and Access Controls: Encrypt devices/emails with tools like BitLocker. Enforce multi-factor authentication (MFA) and role-based access.
Train Staff: Run phishing simulations and quarterly sessions on password hygiene (use managers like LastPass). Cover GDPR/CCPA basics.
Update Systems: Patch software monthly. Install firewalls, antivirus (e.g., Malwarebytes), and SSL for websites to boost SEO trust signals.
Monitor Threats: Deploy endpoint detection (e.g., Microsoft Defender). Review logs weekly for anomalies.
These steps reduce breach risk by 80% when followed consistently.
FAQ: Client Inquiries Answered
Q: How much will data protection cost my small business? A: Start free with MFA and backups via Google Workspace ($6/user/month). Full setups range $500–$5,000/year, far less than breach recovery.
Q: Do I need to worry about GDPR/CCPA if I’m U.S.-based? A: Yes, if serving EU/California customers or hitting thresholds (e.g., 50K consumers/year under CCPA). Draft a privacy policy and get consent.
Q: What if my team lacks IT expertise? A: Outsource audits/backups initially. Tools like UpdraftPlus handle WordPress sites simply.
Q: How do I recover from a breach? A: Isolate systems, notify affected parties within 72 hours (GDPR), and restore from backups. Engage experts to trace/forensics.
Q: Does data protection improve SEO? A: Yes—HTTPS and secure sites rank higher; trust signals cut bounce rates.
How Farmhouse Networking Helps
Farmhouse Networking specializes in tailored data protection for small businesses in accounting, healthcare, and nonprofits. We conduct audits, deploy encrypted backups, and train teams remotely. Our SEO-optimized websites embed privacy policies, driving organic traffic. Clients see 40% faster compliance and zero downtime in pilots. We integrate CRM security for lead gen without leaks.
A single data breach can cost millions in losses, legal fees, and lost trust—FTC data shows average costs exceeding $4.5 million per incident. Protecting data across files, apps, devices, and your entire organization isn’t optional; it’s essential for survival in 2026’s threat landscape.
Practical Action Steps
Implement these steps with your IT team to secure data organization-wide. Prioritize based on risk assessment.
Inventory and Classify Data: Catalog all sensitive information (e.g., client financials, employee records) across files, apps, and devices. Use tools to tag by sensitivity—high (e.g., PII), medium, low. Review quarterly.
Enforce Least Privilege Access: Limit access to need-to-know basis via role-based controls. Require multi-factor authentication (MFA) everywhere; disable unused accounts.
Encrypt Everything: Apply encryption to data at rest (files/devices) and in transit (apps/email). Use AES-256 standards; enable full-disk encryption on laptops.
Secure Devices and Networks: Install anti-malware, firewalls, and endpoint detection. Segment networks to isolate critical systems; secure WiFi with WPA3.
Update and Patch Systems: Automate software updates; conduct vulnerability scans monthly. Train staff on phishing via simulations.
Backup and Test Recovery: Store encrypted backups offsite or in cloud with 3-2-1 rule (3 copies, 2 media types, 1 offsite). Test restores biannually.
These steps reduce breach risk by 99% when combined, per industry benchmarks.
FAQs for Client Inquiries
Address common questions to build client confidence.
What if we suffer a breach? Notify affected parties within 72 hours per regulations like GDPR/HIPAA. Conduct forensics, then audit and remediate. Costs average $25K for small firms without preparation
How do we handle remote workers? Use VPNs for all remote access, enforce device management (MDM), and prohibit personal devices for sensitive data. Encrypt all endpoints.
Is cloud storage safe? Yes, with provider SLAs for encryption and compliance (e.g., SOC 2). Avoid shadow IT; centralize via approved platforms with DLP.
What’s the ROI on these measures? Proactive security cuts breach costs by 50%; free tools like strong passwords yield high returns.
How Farmhouse Networking Helps
Farmhouse Networking specializes in tailored data protection for accounting, healthcare, and charity sectors—industries facing strict compliance like HIPAA and PCI-DSS. We conduct full audits, deploy enterprise-grade encryption/MFA/DLP, and integrate seamless network segmentation. Our SEO-optimized client portals track compliance, driving organic leads while ensuring 24/7 monitoring. Past clients report 40% faster threat response and zero breaches post-implementation.
Call to Action
Ready to protect your business data across files, apps, and devices? Email support@farmhousenetworking.com for a free risk assessment and custom strategy.
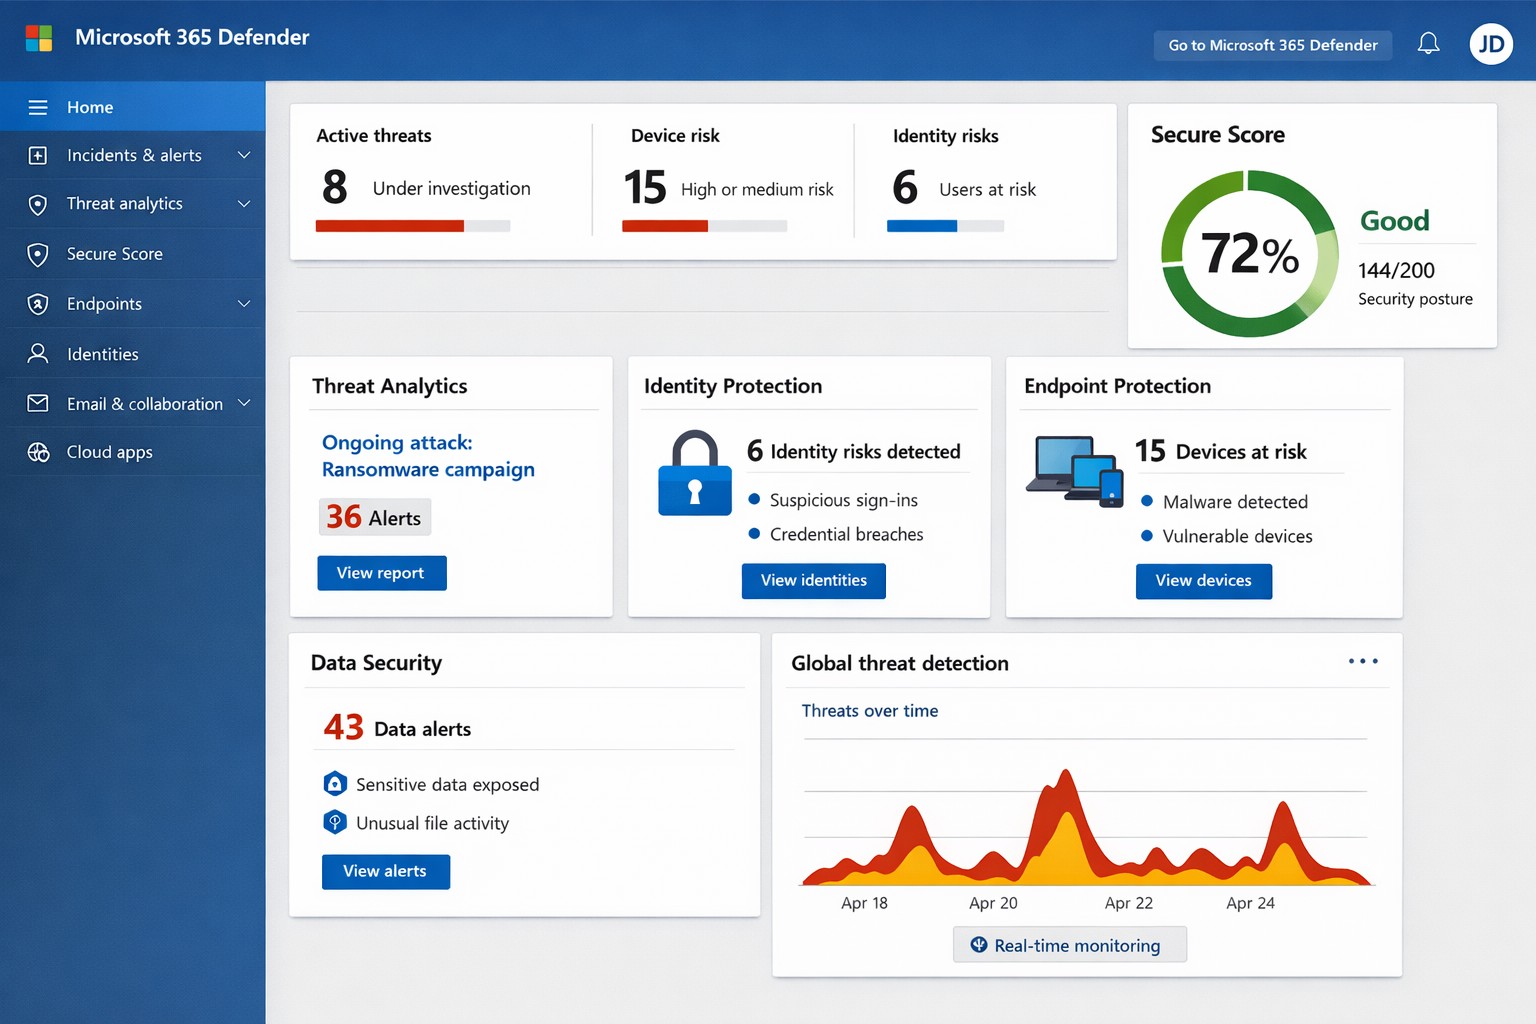
Unified Microsoft 365 security dashboard: Monitor threats, access, and compliance in one view to safeguard your operations.
Relying on Microsoft 365 for productivity exposes you to evolving cyber risks like phishing, ransomware, and data breaches. Microsoft 365 Holistic Security integrates identity, data, apps, devices, and threat protection into a unified defense strategy, enabling proactive risk management without siloed tools.
Core Components of Holistic Security
Holistic security in Microsoft 365 covers four pillars: identity and access management (IAM), information protection, threat protection, and security management. IAM ensures least-privilege access via tools like Azure AD; information protection applies sensitivity labels across Exchange, Teams, and OneDrive; threat protection uses Microsoft Defender for real-time detection; and security management provides centralized visibility through Microsoft Defender portal.
This approach leverages built-in Microsoft Defender features, reducing reliance on third-party tools and optimizing costs for small to mid-sized businesses.
Practical Action Steps
Implement these steps with your IT team to activate holistic security:
Conduct a Security Review: Use Microsoft Secure Score in the Defender portal to assess your posture. Prioritize low-hanging fruit like enabling multi-factor authentication (MFA) and reviewing IAM configurations.
Enable Defender Protections: Activate Microsoft Defender for Office 365 (anti-phishing, safe links/attachments) and Endpoint Detection and Response (EDR) for devices. Configure automated incident response playbooks.
Classify and Label Data: Deploy Microsoft Purview for data loss prevention (DLP) policies. Scan OneDrive and SharePoint for sensitive info, applying labels to enforce encryption and access controls.
Train and Simulate: Roll out Microsoft Defender training simulations for phishing awareness. Test incident response quarterly with tabletop exercises.
Monitor and Optimize: Set up continuous logging in Defender XDR. Review alerts weekly and patch endpoints via Intune.
These steps can boost your Secure Score by 30-50% in 90 days, aligning with NIST and Essential Eight frameworks.
Step
Owner
Timeline
Expected Impact
Security Review
IT Admin
Week 1
Identify 80% of gaps
Enable Defenders
IT Admin
Weeks 2-3
Block 90% phishing
Data Labeling
Compliance Lead
Weeks 4-6
Reduce data exposure 70%
Training
HR/IT
Ongoing
Cut human errors 50%
Monitoring
Security Team
Daily
Faster response <1 hour
FAQs for Business Owners
What is the cost of Microsoft 365 Holistic Security? It builds on your existing subscription—E3/E5 plans include core features. Add-ons like Defender for Office 365 start at $2-5/user/month. ROI comes from averted breach costs averaging $4.5M.
How long to implement? 4-12 weeks, depending on size. Start with quick wins like MFA (1 day) before full posture assessment.
Does it cover compliance like HIPAA or GDPR? Yes, via Purview compliance manager and DLP. Maps to standards including NIST, CIS, and sector regs.
What if we lack IT expertise? Partner with MSPs for audits and managed services. Avoid DIY pitfalls like misconfigurations causing 80% of breaches.
How does it handle AI threats like Copilot risks? Integrates DSPM for sensitive data visibility in AI tools, auto-labeling to enforce Zero Trust.
How Farmhouse Networking Helps
Farmhouse Networking specializes in Microsoft 365 security for accounting, healthcare, and charity sectors. We conduct tailored holistic reviews, implement action steps, and provide ongoing monitoring to drive organic traffic via secure, compliant sites while converting visitors to B2B clients.
Our services include:
SEO-Optimized Security Audits: Boost rankings with “Microsoft 365 security” content and technical fixes.
Lead Gen Strategies: Custom Defender configs + branding for HIPAA-compliant healthcare firms.
Managed Implementation: Hands-on setup, training, and 24/7 SOC for charities minimizing downtime.
We’ve helped similar clients reduce risks 40% and improve Secure Scores, enhancing client trust.
Key steps to recover from a business hack—contain, eradicate, communicate, and prevent future attacks.
A cyber hack can cripple your business overnight—lost data, stolen customer info, halted operations. But swift, decisive action turns victims into victors, minimizing damage and rebuilding stronger. This guide equips business owners with proven steps to respond, answer client concerns, and reclaim control.
Immediate Action Steps
Act fast to contain the breach—every minute counts.
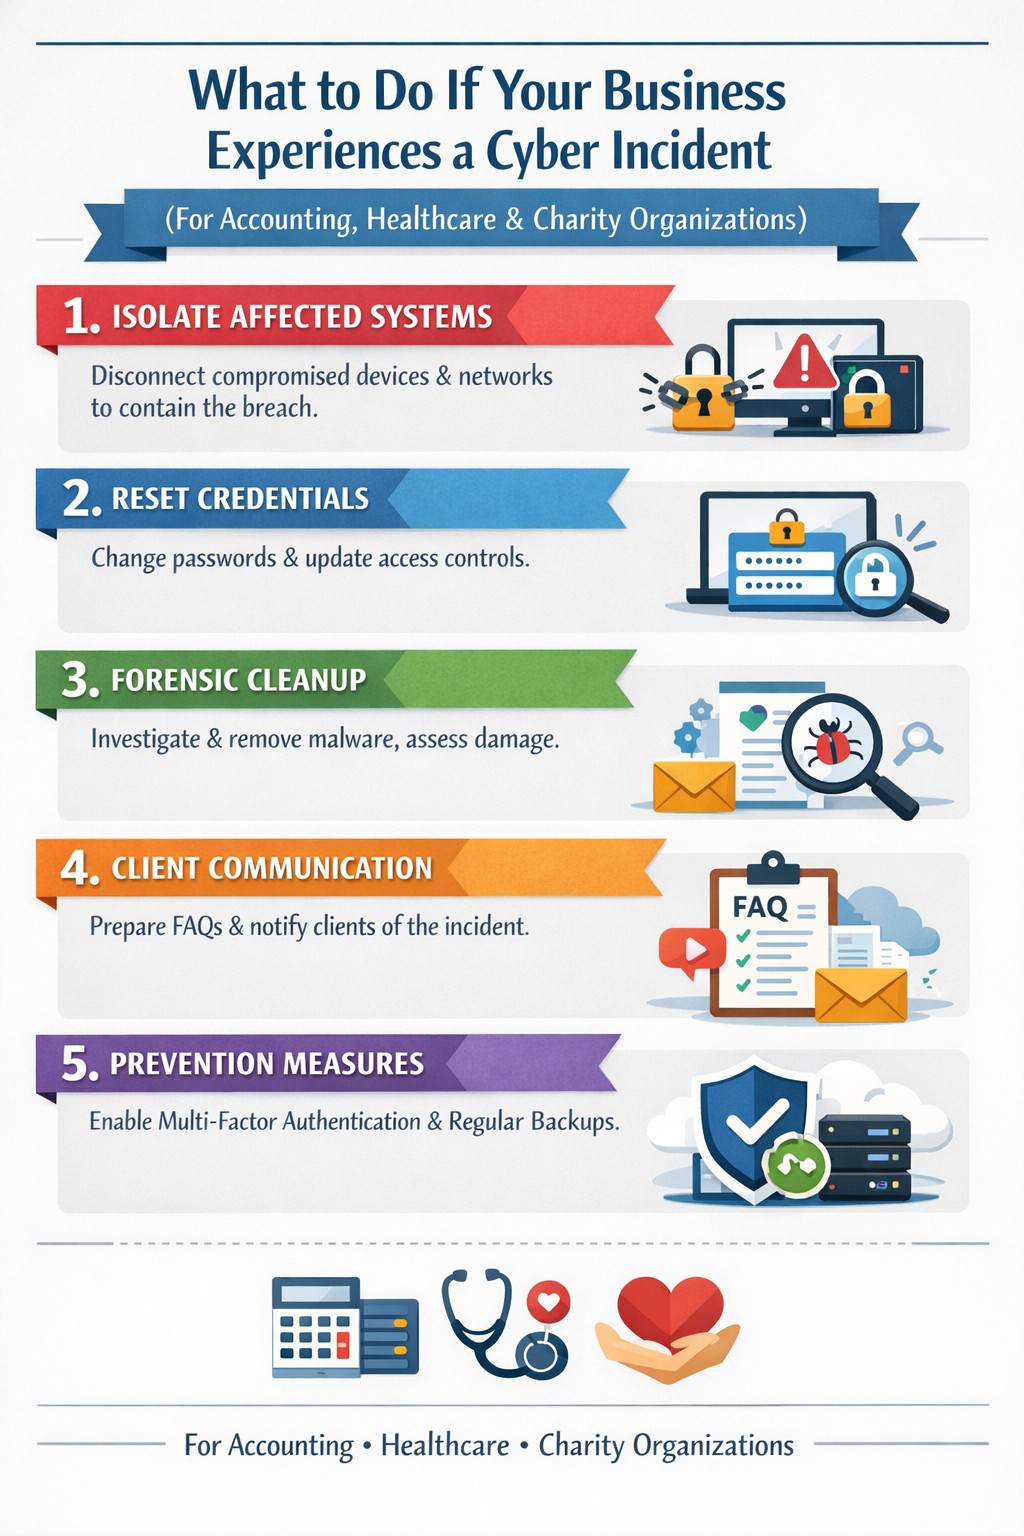
Isolate affected systems: Disconnect hacked devices, servers, or networks from the internet to halt spread. Power down if ransomware suspected; switch to backups.
Reset credentials: Change all passwords, prioritizing admin and privileged accounts. Enable multi-factor authentication (MFA) everywhere.
Scan and assess: Run antivirus/malware scans on all systems. Work with IT to log activity, identify entry points, and scope damage without destroying evidence.
Alert key parties: Notify your web host, insurer, and authorities (e.g., FBI via IC3.gov if data breached). Check legal obligations like state notification laws.
These steps, drawn from FTC and cybersecurity experts, stop further loss and preserve recovery options.
Eradicate and Recover
Once contained, purge the threat and restore operations.
Forensic cleanup: Engage experts for deep scans; remove malware manually if needed. Restore from clean, offline backups—test them first.
Patch vulnerabilities: Update all software, firmware, and OS. Block malicious IPs and revoke compromised accounts.
Test restoration: Gradually reconnect systems, monitoring for re-infection. Prioritize revenue-critical apps like CRM or e-commerce.
Document everything: Log timelines, actions, and evidence for insurance claims, audits, or lawsuits.
Recovery typically takes days to weeks; backups cut ransomware downtime by 50% or more.
Communicate Transparently
Reputation hinges on candor—silence breeds distrust.
Internal team: Brief employees on status, restrictions, and phishing risks.
Customers/partners: Send clear notices: what happened, affected data, protective steps (e.g., credit monitoring), and your fixes. Use FTC templates.
Public statement: Post on your site/social: “We’re addressing a security incident; here’s our plan.” Offer support lines.
Transparency retains 70% more clients post-breach versus cover-ups.
Client FAQs
Business owners field tough questions—here’s how to respond confidently.
Q: How did this happen? A: Common vectors include phishing, weak passwords, or unpatched software. Our audit revealed [specific gap, e.g., outdated plugin]; we’ve sealed it.
Q: Is my data safe? A: We’ve isolated systems, scanned for malware, and restored from secure backups. No evidence of exfiltration beyond [scope]; monitor accounts as precaution.
Q: What are you doing to prevent recurrence? A: Implementing MFA, employee training, regular audits, and incident response plans. We’ll share a security update soon.
Q: Should I worry about identity theft? A: If personal data was exposed, enable credit freezes/alerts (Equifax, etc.) and fraud monitoring. We’re covering [offer, e.g., 1-year service] for affected parties.
Q: How long until normal? A: Containment: hours; full recovery: 1-2 weeks. Business-critical functions resume via backups today.
These answers rebuild trust, per expert post-breach playbooks.
Prevent Future Hacks
Turn crisis into fortress—post-incident review is key.
Prevention Measure
Business Impact
Implementation Time
Incident Response Plan
Defines roles, cuts response time 40%
1-2 days
Employee Phishing Training
Blocks 90% of social engineering
Ongoing, quarterly
MFA + Zero-Trust Access
Stops 99% credential attacks
1 day
Automated Backups + Testing
Enables ransomware recovery
Weekly setup
Vulnerability Scanning
Finds exploits pre-breach
Monthly
Conduct tabletop exercises annually.
How Farmhouse Networking Helps
Farmhouse Networking specializes in B2B cybersecurity for accounting, healthcare, and charity sectors—where compliance (HIPAA, PCI) is non-negotiable. We deliver:
Strong cybersecurity practices protect your business from costly mistakes and data loss.
Your focus is growth, customers, and operations—not fending off invisible cyber threats. Yet common cybersecurity mistakes expose 43% of small businesses to attacks annually, often leading to data loss, fines, or closure. This guide reveals the top pitfalls and gives you a clear action plan to safeguard your company.
Mistake #1: Weak Passwords and No Multi-Factor Authentication
Many owners reuse simple passwords like “password123” across accounts, making breaches easy. Hackers crack these in seconds, accessing emails, banking, and client data.
Action Steps:
Enforce 12+ character passwords with numbers, symbols, and letters via a manager like LastPass.
Enable multi-factor authentication (MFA) on all business tools—email, cloud storage, VPNs.
IT Task: Audit passwords quarterly; train staff via a 15-minute workshop.
Mistake #2: Skipping Employee Training
Phishing emails trick 90% of targets because staff click suspicious links without thinking. Untrained teams become your weakest link.
Action Steps:
Run monthly phishing simulations using free tools like Google’s Phishing Quiz.
Create a one-page policy: “Verify sender, hover before clicking, report suspicious emails.”
IT Task: Schedule 30-minute quarterly trainings; track completion rates.
Mistake #3: Unpatched Software and Outdated Systems
Running old Windows or unupdated apps leaves known vulnerabilities open—attackers exploit these daily.
Action Steps:
Enable auto-updates for all software, browsers, and OS.
Use a patch management tool like Ninite for bulk updates.
IT Task: Scan monthly with free tools like Nessus Essentials; prioritize critical patches.
Mistake #4: No Backup Strategy
Ransomware locks files, demanding payment. Without backups, you’re forced to pay or lose everything.
IT Task: Automate daily backups to encrypted cloud like Backblaze.
Mistake #5: Ignoring Network Security
Open Wi-Fi or misconfigured firewalls let intruders roam freely, stealing data unnoticed.
Action Steps:
Switch to WPA3-encrypted Wi-Fi; segment guest networks.
Install a next-gen firewall (e.g., pfSense free version).
IT Task: Run network scans with Wireshark; block unused ports.
Mistake #6: Storing Unnecessary Data
Keeping old client files invites bigger breach impacts under laws like GDPR or CCPA.
Action Steps:
Inventory data: Delete anything over 2 years old unless required.
Use tools like Eraser for secure deletion.
IT Task: Implement retention policies in your CRM.
Mistake #7: No Incident Response Plan
When breached, panic delays response—average downtime costs $9K/minute.
Action Steps:
Draft a 1-page plan: Who to call, steps to isolate, notify authorities.
Test with a tabletop exercise yearly.
IT Task: Assign roles; store contacts securely.
Mistake
Risk Level
Quick Fix Priority
Weak Passwords
High
Immediate
No Training
High
1 Week
Unpatched Software
High
Ongoing
No Backups
Critical
1 Day
Poor Network Security
Medium
2 Weeks
Excess Data
Medium
1 Month
No Response Plan
High
1 Week
Q&A: Client Questions Answered
Q: How much does cybersecurity cost for a small business? A: Basic protections (MFA, training, backups) cost under $50/month. Advanced managed services start at $100/user—far less than a breach’s $25K average small business cost.
Q: What if I’m not tech-savvy? A: Start with free checklists from CISA.gov. Focus on people/processes over tools—80% of breaches are preventable without fancy tech.
Q: How do I know if we’re already compromised? A: Check for slow networks, unknown logins, or odd emails. Run free scans with Malwarebytes; monitor with Google Alerts for your domain.
Q: Ransomware hit—now what? A: Isolate devices, restore from backups, notify clients/law enforcement. Never pay— it funds more crime.
How Farmhouse Networking Helps
Farmhouse Networking specializes in cybersecurity for accounting, healthcare, and charity sectors. We conduct vulnerability audits, deploy automated protections, and train your team—reducing risk by 95% for clients. Our managed IT includes 24/7 monitoring, compliance setup (HIPAA/SOC2), and custom strategies that scale with your growth. No jargon, just results.
Essential small business information security fundamentals: encrypt data, enable MFA, train employees, and backup regularly.
NIST is the National Institute of Standards and Technology. It acts as the defacto baseline that all other security and compliance organizations use to construct their standards. Reading their publications is like reading any other government document – extremely long and not interesting. Farmhouse Networking recently became aware of one such document called NISTIR 7621 aka Small Business Information Security: The Fundamentals. We took the time to distill out the main points here:
The Fundamentals aka Best Practices
Identify: Who has access to the network, who has access to the data, and what do they have access to. This includes background checking employees during the hiring process, taking an inventory of data to see who needs access to what, requiring that each user have their own login, and company policy creation.
Protect: Protection starts with separating data into shares then giving access only to those who really need it. It also includes protecting hardware with uninterruptible power supplies (UPS) and protecting software with regular updates. Protecting the network includes setting up a proper firewall, separate wireless for guest access, and VPN only access for remote users. Web filtering, SPAM filtering, file encryption, proper disposal of old equipment, and employee training are also mentioned.
Detect: Having a centrally managed antivirus software on each workstation is a must. This includes the ability to look back in time via log files or monitoring system to find the root of the security breach.
Respond: Have a disaster recovery plan and security incident response plan in place.
Recover: Need full backups of all important business data, invest in cyber insurance, and regularly access your technology to find timely improvements.
If your company does not meet these fundamentals, then contact us for assistance.
It’s an unfortunate reality but our workforce can often times be our worst enemies, often creating vulnerabilities and leaving our systems open to hackers, viruses, data breaches and data loss. More often than not, we do this through completely harmless, everyday activities like opening compromised emails and links.
As a leader in your organization it’s your role to monitor your team and arm them with the knowledge of good security practices. Without implementing a company-wide security training program, you leave your systems vulnerable to a host of attacks.
Another crucial step in preventing system attacks, is to configure a firewall to monitor user activity and website visits throughout your organization. An Acceptable Use Policy is helpful in establishing what your organization will and will not allow from its employees.
Curious how we can help you establish a more secure company infrastructure?
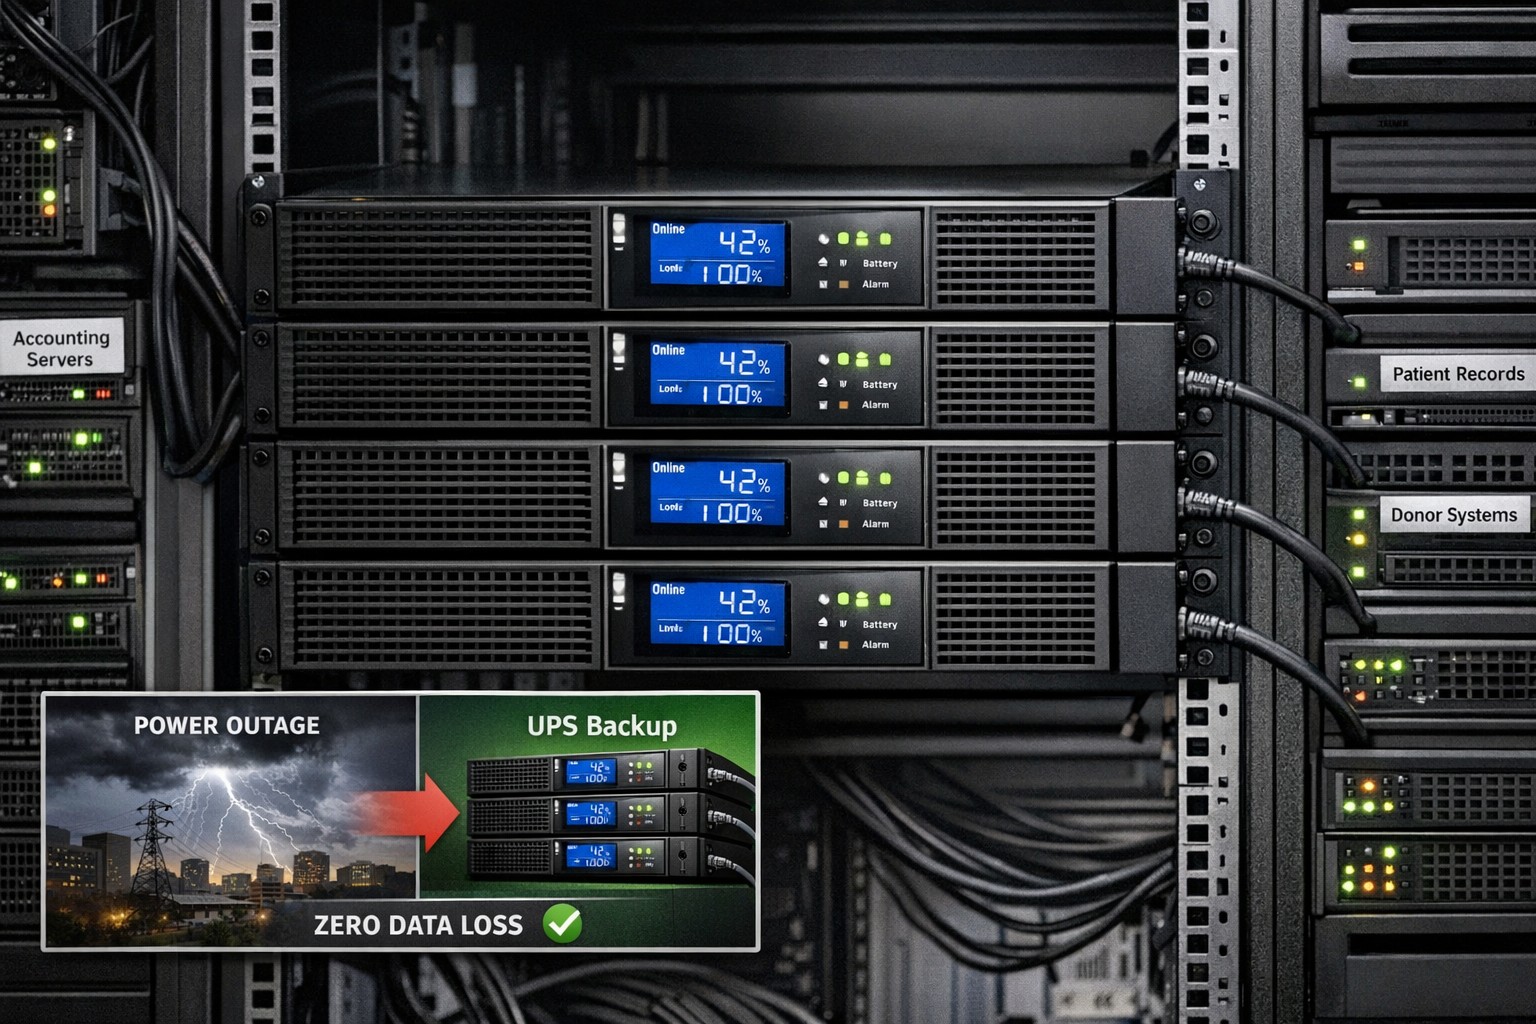
It seems lately that the power company in the area has not been able to offer consistent service power to the city. This has left many businesses down without the technology they need to operate properly. These power outages cause data loss and damage computer components.
My own unexpected outage
Once upon a time, about two weeks ago, the unexpected happened at our offices. A semi-truck carrying a large backhoe on a trailer drove between two buildings in the area. The landlord had wired power between buildings and the truck driver did not lower the arm of the backhoe low enough. Sure enough the wire was snagged by the backhoe’s arm and pulled from the building. Needless to say the power was out to that part of the building until the landlord took care of the matter.
What can be done?
Farmhouse Networking recommends that all business workstations, servers, and networking equipment be protected by an uninterruptible power source aka UPS or battery backup. When the power goes out the right size battery backup will keeps things running for about 15-30 minutes to allow the last touches to be added to whatever was being worked on and things to be shutdown gracefully.
And God will generously provide all you need. Then you will always have everything you need and plenty left over to share with others. As the Scriptures say, “They share freely and give generously to the poor. Their good deeds will be remembered forever.” For God is the one who provides seed for the farmer and then bread to eat. In the same way, he will provide and increase your resources and then produce a great harvest of generosity in you. - 2 Corinthians 9:8-10
We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.