Why Root Cause Analysis Belongs in Your Incident Response Plan
Finding the root cause of an IT incident is what stops it from happening again.
If your last IT issue got fixed but never explained, you may already be sitting on a repeat problem.
Here’s how it usually goes: an employee’s email gets compromised, your IT provider resets the password, the alerts stop, and everyone moves on. But almost nobody asks the harder question — how did the attacker actually get in, and is that same weakness still open somewhere else in your business?
That question is the entire purpose of root cause analysis (RCA). It’s the difference between putting out a fire and finding out what’s been leaking gas into the building. Skip it, and you’re not preventing the next incident — you’re just waiting for it.
What Root Cause Analysis Actually Means for Your Business
Incident response is the emergency part: contain the threat, restore access, get back to work. Root cause analysis is the follow-up step that asks why it happened in the first place — a phishing gap, a missing security policy, an unpatched system, a training blind spot. Without that step, your business ends up treating the same underlying weakness as a brand-new crisis every time it resurfaces.
Action Steps for You and Your IT Provider
Require a written root cause summary after any security incident — not just a “resolved” notification.
Ask whether your provider monitors for unusual sign-in locations and session activity, not just failed login attempts.
Confirm Conditional Access policies are enforced to block logins from unexpected countries or unmanaged devices.
Review whether staff training addresses the specific method behind the last incident, not just general reminders.
Ask your provider whether an incident was isolated or part of a broader pattern across your systems.
Build a root cause step into your written incident response plan, if you don’t already have one.
Schedule a 30-day follow-up review to confirm the fix actually held.
Questions Your Team Might Ask You
Q: We already fixed it — why dig further? A: Fixing the account doesn’t fix the door the attacker used to get in. Without knowing how it happened, you can’t be confident it won’t happen again the same way.
Q: Doesn’t this slow down how fast issues get resolved? A: No. Containment happens immediately, every time. Root cause review is a short follow-up step afterward — usually a summary or a brief call, not a delay.
Q: Is this really worth the extra step for a business our size? A: Yes — arguably more so. Smaller businesses often can’t absorb the same incident twice. Understanding the cause the first time is what keeps a bad week from becoming a bad year.
How Farmhouse Networking Helps
We recently helped a client contain an incident where an employee’s login session — not just her password — was stolen through a convincing fake sign-in page that looked identical to a real Microsoft 365 login. Containing it was step one. The real work was tracing exactly how the attacker got that session, confirming nothing else in the environment was exposed the same way, and closing the gap permanently.
That’s the process we apply to every incident we handle. Farmhouse Networking documents root cause on every security event, gives you a plain-language explanation of what actually happened and why, and makes sure the fix addresses the cause — not just the symptom.
Want to Know What’s Really Behind Your Last IT Incident?
If your business has had an IT issue that got resolved but never really explained, that’s worth a second look before it repeats itself. Email us at support@farmhousenetworking.com and we’ll walk you through what a proper root cause review looks like — plainly, and without the jargon.
A growing attack technique lets criminals steal a live login session instead of a password — and most businesses have no idea it’s happening until it’s too late.
A single stolen login session can be enough for attackers to bypass MFA and take over a business email account.
For years, business owners have been told the same thing: turn on multi-factor authentication (MFA) and you’re safe. That advice is still mostly true — but a newer style of attack is proving it isn’t the whole story. We recently helped a regional nonprofit contain an incident that shows exactly how this plays out, and it’s a pattern every small business owner should understand.
Here’s what happened, in short: an employee was directed to a fake login page that looked identical to the real Microsoft 365 sign-in screen. She entered her password and completed her MFA step normally. But the fake page was secretly relaying everything to the real Microsoft servers in real time — and it captured the “session” created after she logged in. That session is like a hall pass: once you have it, you don’t need the password or the MFA code again. The attacker used it to log in as her, days later, from the other side of the world.
From there, the attacker spent time reading email, quietly created a mail rule to auto-delete replies, and used the compromised account to send hundreds of file-sharing invitations and emails to external contacts — all appearing to come from a real, trusted employee.
Action steps for you and your IT provider:
Ask your IT provider whether your email platform is monitoring for “impossible travel” or suspicious sign-in locations, not just failed MFA attempts.
Enable and enforce Conditional Access or equivalent policies that block sign-ins from unexpected countries or devices.
Shorten session lifetimes so a stolen session expires faster.
Train staff to check the URL bar before entering credentials — even on pages that look pixel-perfect.
Make sure your provider can see and revoke active sessions instantly, not just reset passwords.
Review mail rules periodically; attackers often hide behind rules named with punctuation marks so they’re invisible in a quick glance.
Confirm your incident response plan includes session token revocation, not just password resets.
Q&A
Q: If we have MFA, aren’t we protected? A: MFA blocks most attacks, but this technique steals the session created after MFA succeeds. You need monitoring and Conditional Access policies layered on top of MFA, not instead of it.
Q: How would we even know this happened? A: Often the first sign is unusual outbound email, unexpected file-sharing invitations, or partners asking why they received a strange invoice link. Proactive monitoring catches it earlier.
Q: Is this expensive to defend against? A: Most of the defenses — Conditional Access policies, session timeout settings, monitoring — are configuration changes, not new purchases, if your provider has the expertise to set them up correctly.
How Farmhouse Networking Helps
Farmhouse Networking configures and monitors Microsoft 365 environments specifically to catch this kind of attack — unusual sign-in locations, hidden mail rules, mass outbound activity — before it turns into a full-blown incident. We also help small businesses put the right guardrails in place from the start, so a stolen password or session doesn’t become a company-wide problem.
Not sure if your email environment could catch an attack like this? Email us at support@farmhousenetworking.com to schedule an MFA and email-security review. We’ll walk through your current setup and tell you plainly where the gaps are.
How small business owners can use AI to simplify HR — hiring, onboarding, and staff support — without adding headcount or risk
Small business owners are turning to AI to simplify hiring, onboarding, and everyday HR tasks.
If you’re running a small business, HR is probably one of a dozen hats you wear, not a full-time job. AI tools built for HR — screening applicants, automating onboarding paperwork, answering common staff questions — can take real work off your plate. The opportunity is significant, but so is the need to choose and set up these tools carefully so they don’t create new security gaps.
Action Steps for Owners and IT
List the HR tasks currently taking the most time: recruiting, onboarding, PTO tracking, or answering repeat staff questions.
Evaluate AI-assisted applicant screening and interview scheduling tools that fit your team size and budget.
Set up an AI-powered internal FAQ or chatbot trained on your policies so staff get quick answers without interrupting you.
Have your IT provider review any new HR tool’s data handling and access controls before your team starts using it.
Use AI-generated summaries of employee feedback or engagement surveys to catch problems before they become turnover.
Create a simple written policy on what information staff can and can’t enter into AI tools.
Confirm data storage location and vendor security practices before rolling out any HR software company-wide.
Questions Staff Might Ask
Is the company using AI to decide who gets hired or promoted? AI speeds up early-stage screening, but hiring and promotion decisions still come from you or your managers.
Is my personal information safe with these tools? Properly vetted tools keep employee data secure and separate from other business systems — your IT provider should confirm this before adoption.
Will this replace my manager or HR contact? No — these tools reduce repetitive administrative work so the people around you have more time for you.
How Farmhouse Networking Can Help
Farmhouse Networking helps small business owners vet, integrate, and secure AI-powered HR tools — from applicant screening to internal chatbots — so you get the time savings without the security headaches. We handle the technical review and staff training so you can adopt these tools with confidence.
What the CMMC suspension teaches every small business about the danger of waiting on compliance
Building a cybersecurity policy before it’s required can save your business time, money, and trust.
On July 13, 2026, the Department of War suspended Phase II of its Cybersecurity Maturity Model Certification (CMMC) program — the rule that would have required over 100,000 defense contractors to complete third-party cybersecurity assessments starting this November. The reason wasn’t that cybersecurity stopped mattering. It’s that the compliance system itself couldn’t scale: too few certified assessors, costs approaching $600,000 per certification, and a timeline small businesses couldn’t meet.
That story has nothing to do with defense contracts if you’re not one. But it has everything to do with a mistake we see constantly: business owners treating cybersecurity policy as something to build only when a regulator forces the issue. When the deadline moves or disappears, so does the motivation — right up until a breach, an insurance audit, or a client contract makes it urgent again, usually at the worst possible time.
Why Waiting Is the Expensive Choice
Government programs get delayed, revised, or scrapped. Your actual risk — ransomware, phishing, a stolen laptop, an employee clicking the wrong link — doesn’t wait for anyone’s regulatory calendar. Businesses that build security practices proactively spend less, recover faster, and rarely scramble when a client or insurer asks for documentation they don’t have.
Action Steps for Business Owners
Write down your security policies now, even in simple form: password requirements, data handling rules, who can access what.
Inventory your systems and data — you can’t protect what you haven’t mapped.
Set a patch and update schedule instead of reacting to alerts.
Back up data regularly and actually test that restores work.
Train staff on phishing and basic security hygiene at least twice a year.
Review vendor contracts for the security commitments you’re already making to clients or partners.
Revisit your plan quarterly — don’t let it go stale.
Questions Business Owners Are Likely Asking
“If the government paused its own program, why should I move faster on mine?” Because your risk was never tied to their timeline. The suspension was about assessment logistics, not about cyber threats becoming less real.
“Isn’t this overkill for a small business?” No — attackers target small businesses precisely because they assume no one built a plan. A written policy costs far less than a breach.
“Do I need a full compliance framework?” Not necessarily. You need documented, consistently applied practices. Formal frameworks can come later if a client or contract requires them.
“What if I don’t have an in-house IT person?” That’s exactly where a managed partner earns their keep — building and maintaining the plan so you don’t have to.
How Farmhouse Networking Helps
We help small and mid-sized businesses build the security foundation regulators eventually ask for — without waiting for a mandate to force the issue. That means clear, documented policies, practical safeguards like MFA and monitored backups, and straightforward guidance you can actually act on, without the jargon.
Don’t Wait for the Next Deadline to Get Serious
Regulations pause. Real risk doesn’t. If you’ve been putting off a cybersecurity policy because “nothing’s required yet,” now is the time to close that gap — before something else forces the timeline.
Email us at support@farmhousenetworking.com for a free cybersecurity policy review. We’ll tell you plainly where you stand and what to fix first.
What this summer’s federal security campaign means for any business holding sensitive data
Taking a few hours this summer to review your security practices can prevent a costly data breach later.
What this summer’s federal security campaign means for any business holding sensitive data
This July, the IRS and its Security Summit partners launched Protect Your Clients; Protect Yourself, a five-week campaign built for tax preparers. It walks through the phishing schemes, impersonation scams, and stolen-credential attacks criminals are using against professionals who hold sensitive client data, along with the basic safeguards, written security plans, and verification tools meant to stop them.
Your business may have nothing to do with taxes. But the tactics described in this campaign — fake “new client” emails carrying malware, spoofed calls, and urgent requests designed to pressure someone into clicking or sharing information — are used against every kind of small business, not just tax firms. If your company stores customer records, payment details, or employee data, you’re a target using the same playbook. Summer is a good time to check whether your own safeguards would hold up.
Action Steps for You and Your IT Team
Write down your security practices. A simple, documented policy covering data handling, access, and response is far better than relying on informal habits.
Enable multi-factor authentication on email, financial systems, and any remote access used by your team.
Review employee access regularly, and immediately revoke access for anyone who leaves the company.
Train your team to spot phishing and impersonation attempts, especially fake vendor invoices, urgent executive requests, and unexpected attachments.
Test your backups, not just assume they’re running, to confirm you could actually recover if something went wrong.
Document an incident response plan so your team knows exactly who to call and what to do the moment something looks wrong.
Questions Your Customers or Employees Might Ask
“How do you protect the information you have on file for us?” We maintain a documented security policy, require multi-factor authentication across our systems, and regularly review who has access to sensitive data.
“What would happen if your systems were breached?” We have a tested response plan and know exactly how we’d respond and notify anyone affected.
“Why do you keep asking us to verify things that used to be simple?” Because verification steps protect both of us from scams that specifically exploit shortcuts and urgency.
How Farmhouse Networking Can Help
Farmhouse Networking helps small and mid-sized businesses turn good intentions into an actual, documented security program: written policies, MFA across your critical systems, cleaned-up user access, tested backups, and a clear incident response plan. We handle the technical details so you can run your business with confidence instead of guesswork.
Find Out Where Your Business Actually Stands
Email support@farmhousenetworking.com for a free security assessment, and close the gaps the IRS is warning everyone else about — before they cost you something worse.
Why waiting on that hardware upgrade could cost you more the longer you put it off
As computer prices continue to climb, planning your hardware refresh now can help your business avoid paying more later.
If you’ve been telling yourself “next quarter” every time a laptop upgrade comes up, it’s time to rethink that plan. Industry analysts are now projecting one of the steepest computer price increases in years, driven by a global memory chip shortage that shows no sign of easing. For business owners who’ve been putting off replacing aging machines, the math has changed. The equipment you delay buying today will likely cost meaningfully more tomorrow.
Why prices are rising now
The root cause is a supply crunch in memory chips — the RAM and storage components inside every computer. Analysts at Gartner project soaring memory costs will cut global PC shipments by over 10% in 2026, while pushing PC prices up 17% compared to 2025 levels. Combined DRAM and solid-state drive prices are expected to surge roughly 130% by the end of the year. The driver is straightforward: massive AI data center buildouts are consuming memory chip production, leaving less supply for everyday computers and laptops.
This isn’t a short-term blip. Analysts don’t expect prices to stabilize until sometime after 2027. Some manufacturers have already begun raising prices on popular devices and reducing memory in standard configurations to manage costs. Beyond pricing, availability is tightening too — component shortages are extending lead times on replacement parts and new equipment for many buyers.
For a business owner sitting on a five- or six-year-old fleet of machines, this creates a narrow window. Replacing aging hardware now, while at least some current-generation pricing is still available, is very likely cheaper than waiting another year.
Action steps to take now
Inventory your current hardware. List every workstation and laptop with its age and current performance issues.
Identify machines nearing end of useful life — slow boot times, frequent crashes, or inability to run current software are red flags.
Get a written quote for replacement now, even if you’re not ready to buy immediately, so you have a pricing baseline.
Prioritize replacements by business risk. Machines running critical software or storing sensitive data should move to the front of the line.
Build a rolling replacement budget instead of one large annual purchase, so future price swings hit smaller batches of equipment.
Ask your IT provider about bulk purchasing or reserving inventory ahead of need, which can help lock in current pricing.
Questions business owners are asking
Should we wait to see if prices come back down? Based on current forecasts, prices are expected to stay elevated well into 2027. Waiting is more likely to cost you more than save you.
Do we need to replace everything at once? No. A phased approach — prioritizing your oldest or most critical machines first — spreads out the cost while addressing the biggest risks.
Will refurbished or off-lease equipment help? It can be a reasonable option for lower-priority machines, but it should be evaluated case by case for reliability and support.
How do we know if a machine still has useful life left? Age, performance under current workloads, and whether it can run supported software are the key indicators. An IT assessment can quantify this clearly.
How Farmhouse Networking can help
Farmhouse Networking works with business owners across Oregon, Northern California, and New Mexico to plan hardware refreshes that make financial sense. We start with a straightforward assessment of your current equipment, flag machines that are approaching risk, and help you build a realistic replacement timeline and budget — not just a shopping list. We also help source and configure new equipment so you’re not left navigating a volatile market on your own.
The bottom line
The cost of waiting is no longer hypothetical. Every quarter you delay is a quarter closer to higher prices and tighter availability. If you’ve been meaning to upgrade, now is the time to plan it — not next year.
Email us at support@farmhousenetworking.com for a free hardware and lifecycle assessment. We’ll help you understand exactly where you stand and what a smart, budget-conscious upgrade plan looks like for your business.
Why waiting for an audit notice is the most expensive compliance strategy there is
Proactive compliance planning costs far less than scrambling to fix gaps after an audit notice arrives.
Most business owners don’t think about compliance until someone forces the issue – a new client contract requiring proof of security controls, an insurance renewal asking for documentation, or worse, an audit letter. By then, the real cost isn’t the audit itself. It’s everything you didn’t do in the months or years leading up to it: the gaps that piled up, the records that don’t exist, and the scramble to fix it all under a deadline. Research consistently shows that organizations that wait until they’re forced to comply end up paying roughly two-and-a-half to three times more than those who treat compliance as an ongoing practice. That gap isn’t fines alone – it’s lost productivity, disrupted operations, and the cost of fixing things the hard way instead of the easy way.
What “Waiting” Actually Costs
Lost productivity during the scramble. When an audit notice arrives, someone has to drop everything to assemble records, policies, and proof of controls that should have already existed. That’s time not spent serving customers.
Higher remediation costs. Fixing a security gap proactively might mean a software update or a policy change. Fixing it during an active audit often means emergency vendor calls, rushed system changes, and premium pricing.
Weaker negotiating position. Auditors and regulators view a track record of good-faith effort favorably. A business with no documentation looks like it never tried – and that perception drives harsher outcomes.
Business disruption. Operations can grind to a halt while staff redirect their attention to corrective action plans, investigations, or reporting requirements.
Reputational fallout. Clients, vendors, and partners notice when a business fails an audit or discloses a breach. Rebuilding trust takes far longer than building it the first time.
Action Steps to Take Now
Inventory what you actually have. List every system, vendor, and data type your business touches. You can’t protect, or document, what you haven’t identified.
Run a basic risk assessment. Identify where sensitive data lives, who has access to it, and what would happen if it were exposed or lost.
Document your policies in writing. Verbal habits don’t count as a compliance program. Write down password requirements, data handling rules, and incident response steps.
Check your vendor agreements. Make sure any vendor handling sensitive data on your behalf has appropriate contractual protections in place.
Train your staff and keep records of it. A single untrained employee can undo your entire compliance posture. Training without documentation is nearly as risky as no training at all.
Test your backups and recovery plan. A backup you’ve never tested is a backup you don’t actually have.
Set a recurring review cadence. Quarterly or biannual reviews catch small gaps before they become big ones.
Questions Business Owners Are Likely Asking
“We’ve never had a problem. Why worry about this now?” Most compliance failures aren’t discovered until something else goes wrong – a breach, a complaint, or a routine review triggered by a client or insurer. The absence of a problem so far isn’t the same as the absence of risk.
“Isn’t this what our IT vendor is already handling?” Possibly, but it’s worth confirming directly. Compliance documentation, policy writing, and risk assessments are distinct from day-to-day IT support, and gaps often hide in that space between the two.
“How much time does this realistically take?” A basic risk assessment and documentation cleanup can often be completed in a few weeks. Waiting until an audit forces the same work into days, with far less room for error.
“What’s the actual return on doing this now instead of later?” Beyond avoiding fines, proactive compliance tends to reduce insurance premiums, speed up vendor and client onboarding, and protect the business from disruption that has nothing to do with regulators – like a ransomware attack or a lost laptop.
How Farmhouse Networking Can Help
Farmhouse Networking works with business owners to close compliance gaps before they become expensive problems – not after. That means risk assessments that actually identify where your exposure lives, documentation that holds up under scrutiny, employee training programs with the paper trail to prove it, and ongoing monitoring so nothing slips through the cracks between reviews. Instead of a one-time scramble, you get a system that keeps working in the background, year-round.
The Bottom Line
Compliance isn’t a deadline – it’s a discipline. The businesses that treat it that way spend less, sleep better, and never have to explain to a client, an insurer, or a regulator why the paperwork doesn’t exist. If you’re not sure where your gaps are, that’s the best possible reason to find out now, while you still have the luxury of time.
Don’t wait for an audit notice to find out where you stand. Email support@farmhousenetworking.com and let’s talk about what a proactive compliance check would look like for your business.
Upgrading your device is exciting. Losing access to every business account is not. Here’s what every business owner needs to know before they make the switch.
Switching to a new phone without preparing your MFA can lock you out of every business account. A little preparation before the switch prevents hours of downtime.
email. The system asks for an authentication code. You open the authenticator app. The accounts are gone. Now you’re locked out.
This happens to business owners every day. Multi-factor authentication (MFA) is one of the most effective security tools available – but it’s bound to the device it was set up on. When that device changes, access can disappear instantly unless you prepare in advance.
Here’s exactly what happens, why it matters, and what to do about it.
Why MFA Breaks When You Switch Phones
Authenticator apps like Microsoft Authenticator, Google Authenticator, and Duo Mobile generate time-sensitive codes that are tied to your specific device. The codes work because the app and the service share a secret key established during setup. When you swap phones without transferring that key, the connection breaks.
The result: you cannot complete login, even with the correct password. If your old phone is already wiped or gone, and you have no backup method configured, recovery can take hours, or longer, and usually requires IT intervention.
For a business, that’s more than an inconvenience. It’s a potential compliance issue, a productivity disruption, and in some cases, a security risk if employees start using workarounds.
Action Steps Before You Switch Phones
These steps apply to you, your staff, and anyone who uses MFA to access business systems.
Inventory every account protected by MFA. Email, cloud storage, accounting software, practice management platforms, banking portals – list them all. You cannot protect what you haven’t identified.
Check your authenticator app’s backup settings. Microsoft Authenticator supports cloud backup. Google Authenticator added backup functionality in 2023. Enable it before you wipe or trade in your old device.
Register a backup MFA method. Most platforms allow you to add a secondary method – a different phone number, a hardware key, or an email-based code. Do this now, not after a problem occurs.
Save recovery codes. During initial MFA setup, most services generate one-time recovery codes. Store these in a password manager or a secure, offline location. These are your safety net if everything else fails.
Do not wipe your old phone until the new one is fully verified. Set up the authenticator app on the new device, confirm every account logs in successfully, then decommission the old device.
Notify your IT provider before the switch. If you use a managed IT service, your provider can verify admin-level access to reset MFA on critical accounts if something goes wrong during the transition.
Remove your old device from your account settings. After the switch is complete, log into your security settings for each platform and delete the old device. Leaving it registered is an unnecessary security exposure.
Q&A: What Your Employees (and Clients) Might Ask
Q: Can I just reinstall the authenticator app on my new phone? A: Installing the app is only the first step. You still need to re-link each account, either by restoring from a cloud backup or by re-scanning QR codes through each platform’s security settings. Without prior backup configuration, you’ll need your IT administrator to reset access.
Q: What if I already switched phones and I’m locked out? A: Contact your IT administrator immediately. They can reset your MFA registration at the admin level, which clears the old device and allows you to set up a new one. Do not attempt to bypass MFA – doing so may violate your organization’s security policies.
Q: Is it safe to use text message codes instead of an authenticator app? A: SMS-based codes are better than no MFA, but they’re the weakest option. They’re vulnerable to SIM-swapping attacks, where a criminal hijacks your phone number. An authenticator app is more secure and worth the minor setup effort.
Q: Do I need to do anything with my business accounts specifically? A: Yes. Business accounts managed through Microsoft 365, Google Workspace, or other platforms often have centralized MFA settings controlled by your IT administrator. Those accounts may require admin-assisted recovery if the authenticator app is lost. This is another reason to have a managed IT partner involved before the phone switch.
How Farmhouse Networking Can Help
MFA transitions are a routine part of what we manage for our clients. When one of your employees gets a new phone, we can audit their MFA registrations, verify backup methods are in place, guide them through the device transfer, and reset access at the admin level if something goes wrong.
We also help businesses build a documented MFA policy – so every employee follows a consistent, tested process when devices change, instead of figuring it out under pressure when they’re locked out.
If you don’t currently have backup MFA methods configured across your team, that’s a gap worth closing now.
Ready to Stop Worrying About MFA Lockouts?
Email us at support@farmhousenetworking.com and let’s make sure your team is set up to handle device changes without the drama. One conversation now can prevent hours of lost access later.o handle device changes without the drama. One conversation now can prevent hours of lost access later.
A new attack method bypasses MFA and uses Microsoft’s own login system against you. Every business owner using Microsoft 365 needs to read this.
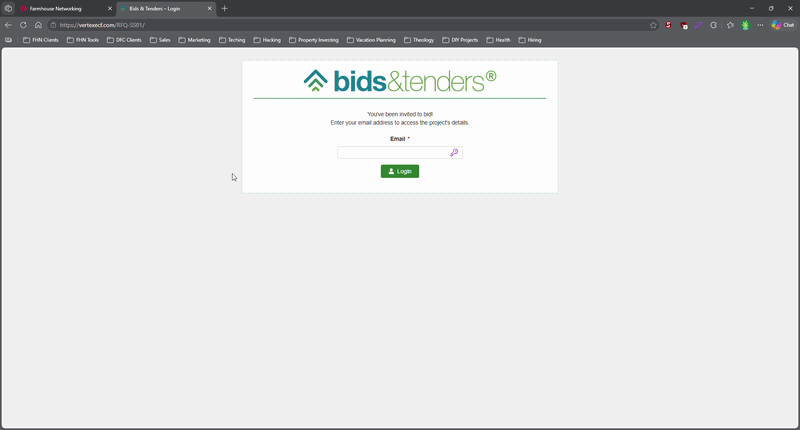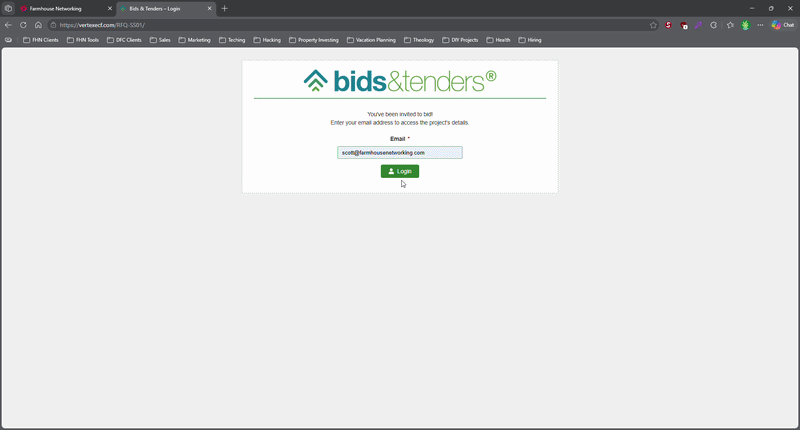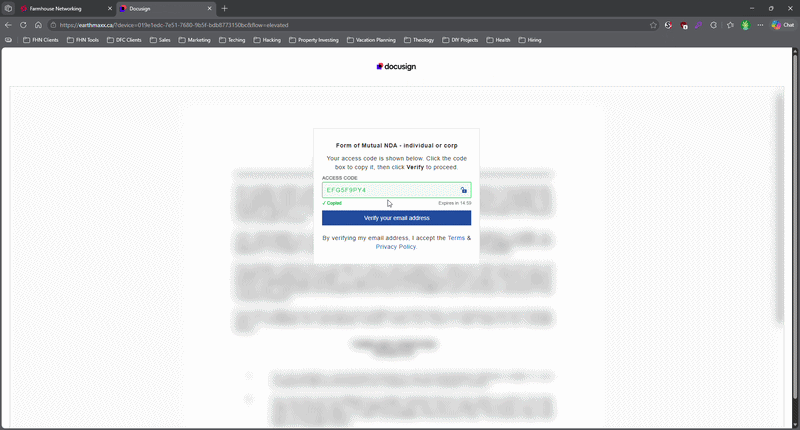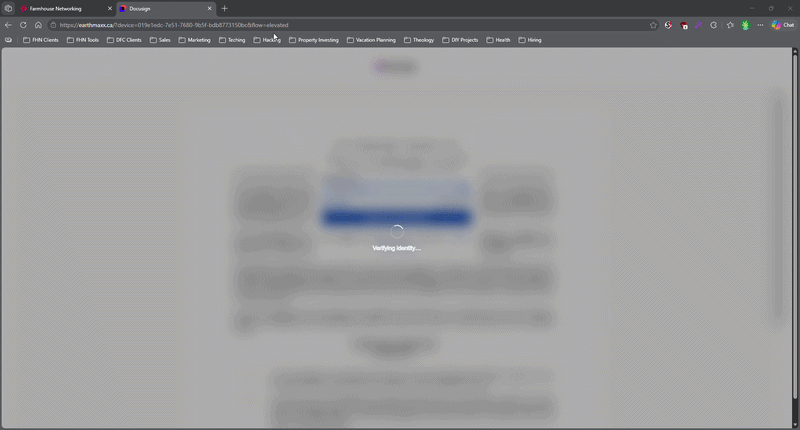
This login screen asks for an email address only, illustrating how attackers can use familiar Microsoft 365-style sign-in pages to bypass passwords.
Most small business owners believe that a strong password and multi-factor authentication make their Microsoft 365 accounts secure. That assumption is now being exploited at scale. Attackers are targeting Microsoft 365 users with device code authorization phishing – a technique that fools users into approving access tokens, bypassing multi-factor authentication protection entirely.
Campaigns using this method have surged since September 2025, representing a significant shift from limited, targeted attacks to widespread exploitation. Both organized criminal groups and nation-state actors are now using it. If your business runs on Microsoft 365, and most do, you need to act.
How the Attack Works
Microsoft has a login feature designed for devices like smart TVs and printers that can’t display a normal login screen. Instead of typing credentials on the device, a user visits a Microsoft page on their phone or computer and enters a short code. It’s a legitimate, trusted system.
Attackers exploit that trust. They initiate the device login flow themselves, then send your employee an email designed to get them to visit Microsoft’s real login page and enter the code – completing the attacker’s authentication instead of their own.
Your employee does everything right. They visit a real Microsoft website. They complete their MFA. They never hand over their password. And the attacker now has full access to your Microsoft 365 environment.
Action Steps for Your Business
Take these steps now with your IT team or provider:
Block device code flow in Microsoft Entra Conditional Access. This is the strongest mitigation available and can be deployed in report-only mode first to assess impact before full rollout. Most small businesses don’t use this feature and have no reason to leave it enabled.
Audit your Microsoft 365 OAuth app permissions. Review which third-party applications have access to your tenant and remove anything unauthorized.
Train your team on this specific attack. Standard phishing training won’t cover it. The key message is simple: if you receive a request to enter a code on a Microsoft login page that you didn’t initiate, stop and report it.
Review sign-in logs for your Microsoft 365 accounts. Unusual locations, unfamiliar devices, and off-hours logins are indicators of compromise.
Check for email forwarding rules set up without your knowledge. This is a common post-compromise action attackers use to quietly collect your outgoing email.
Review your cyber liability coverage. Confirm that account takeover scenarios are covered and understand what your response obligations are.
Q&A: What Your Clients or Partners May Ask
“How did this happen if you had MFA turned on?” This attack bypasses both traditional credential theft defenses and multi-factor authentication controls. MFA was never designed to protect against this type of authentication abuse.
“Could my information have been accessed?” If a business email account is compromised, any data in that account – client correspondence, contracts, financial information – is potentially accessible to the attacker.
“Is this being fixed by Microsoft?” Microsoft has released tools to block it, but those tools require configuration. Microsoft has been rolling out a managed Conditional Access policy aimed at blocking device code flow authentication, but it requires an administrator to enable and configure it. It doesn’t happen automatically.
“Should I be worried about my own accounts?” If you share Microsoft 365 services with a vendor or partner whose account is compromised, there’s risk of lateral movement. Security is a supply chain concern, not just an internal one.
How Farmhouse Networking Can Help
Farmhouse Networking reviews and configures Microsoft Entra Conditional Access policies to block device code phishing, audits your Microsoft 365 environment for existing unauthorized access, trains your staff on this and other current attack types, and monitors your accounts ongoing. We work with small and mid-sized businesses across Oregon, Northern California, and New Mexico – and we explain everything in plain language without the IT jargon.
Take the Next Step
Email support@farmhousenetworking.com today and ask for a Microsoft 365 security review. We’ll tell you whether this attack vector is currently open in your environment and what it takes to close it.
Continuing education isn’t just for licensed professionals — it’s the most underused competitive advantage in small business
Business owners who invest in ongoing learning stay ahead of industry changes and better serve their clients.
Ask most small business owners how they stay current in their industry, and you’ll get a variation of the same answer: they read the occasional article, attend a conference when they can, and otherwise learn by doing.
That approach works — until it doesn’t.
Industries change. Regulations shift. Client expectations evolve. New competitors arrive with tools and knowledge that didn’t exist three years ago. The small business owners who fall behind are rarely the ones who made a bad decision. They’re the ones who stopped making decisions at all, because they stopped learning what their options were.
Continuing education for business owners is not about going back to school. It’s about staying deliberately current in your industry, your craft, your compliance obligations, and the technology your business depends on. It’s about being the person in the room who actually knows what’s happening in their field — not the one nodding along.
Action Steps for Business Owners and Their IT Teams
Identify the professional associations and certifying bodies that govern your industry and confirm what continuing education or recertification requirements apply to you or your licensed staff.
Build a structured learning calendar — one that includes time for courses, industry publications, relevant conferences, and peer networking. Treat it as a business expense, because it is one.
Look for CPE, CEU, or certification programs that align directly with where your industry is heading. AI, automation, regulatory changes, and client technology expectations are reshaping most sectors right now.
When professional development introduces new tools or workflows to your business, involve your IT provider early. Technology changes made without IT planning create security gaps, compatibility problems, and support headaches.
Encourage key staff to pursue continuing education in their functional areas — operations, finance, customer service, or technical disciplines. Your team’s knowledge is a direct asset to your clients.
Document what you and your staff have learned. In industries with licensing requirements, this protects you during audits. In industries without them, it differentiates you from competitors who cannot demonstrate the same commitment.
Review your technology stack alongside your continuing education cycle. New industry knowledge often reveals where your current tools are falling short.
Connect with local business resources — chambers of commerce, SCORE, Small Business Development Centers — for low-cost or no-cost professional development that is often highly practical and locally relevant.
Questions Your Clients or Prospects Might Ask
“What makes you different from your competitors?” Demonstrated commitment to staying current — through credentials, certifications, and relevant training — is a concrete and credible differentiator in almost every market.
“Are you keeping up with changes in the industry?” Clients in regulated or fast-moving sectors ask this more than most business owners expect. The answer should be specific, not generic.
“Do you work with businesses like mine?” Industry-specific continuing education lets you answer yes with evidence. It signals that your advice is informed by real sector knowledge, not general business intuition.
“How do you stay ahead of the technology changes in your field?” This question is becoming more common as clients see technology reshaping what good service looks like. A learning culture within your business is a strong and honest answer.
How Farmhouse Networking Can Help
Professional development drives change — new tools, new workflows, new approaches to serving clients. Farmhouse Networking helps small and mid-sized businesses make sure their IT infrastructure keeps pace with what their owners and teams are learning. When a course introduces a new cloud platform, when a certification requires new software, or when industry changes shift how your business operates, we make sure the technology side is ready to support it. We handle IT so you can focus on growing.
The best investment in your business is the knowledge behind it. Email support@farmhousenetworking.com and let’s make sure your technology is as current as you are.
And God will generously provide all you need. Then you will always have everything you need and plenty left over to share with others. As the Scriptures say, “They share freely and give generously to the poor. Their good deeds will be remembered forever.” For God is the one who provides seed for the farmer and then bread to eat. In the same way, he will provide and increase your resources and then produce a great harvest of generosity in you. - 2 Corinthians 9:8-10
We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.