Farmhouse Networking calculates ransomware, server failure, and cyber insurance costs protecting Oregon SMB digital employees from downtime.
We were discussing the price customers paid for their monthly maintenance of computers and the comparison was brought up about insurance costs. As a business owner with employees, it is necessary these days to offer health insurance as part of their compensation package. If the company has vehicles that are used for business, then the government mandates that they be covered by minimum amounts of insurance. These costs are then built into the price the business owner then charges their clients for products or services.
Insurance Statistics:
According to Business.com, the average cost of health insurance for a single employee was $645 per month and $1,850 per month for a family.
According to NerdWallet.com, the average cost of car insurance was $179 per vehicle per month.
Questions:
So what about the “digital” employees of the company, aka the computers and network equipment that make business possible. How much are business owners paying to “insure” these assets? What are businesses willing to pay to make sure that their computers and network don’t have a sick day? Does the cost of insuring them include preventative care? Who does the business call in case of an accident or breakdown in the middle of the day? Does the cost of insuring include on-site service or transport to a service center?
If your company wants to keep their digital employees healthy and insure them from accidents, then contact us for assistance.
Recently had an issue with a backup software that would get stuck in START_PENDING status at every startup. This caused it to be unable to be uninstalled, repaired, or forcefully removed and re-installed. Here is how we fixed it:
1. Find out the Service Name of the service by looking for it in the Services control panel:
Farmhouse Networking force-stops stuck Windows services using taskkill, sc.exe, and Resource Monitor for Oregon SMB server reliability.
2. Open command prompt as administrator
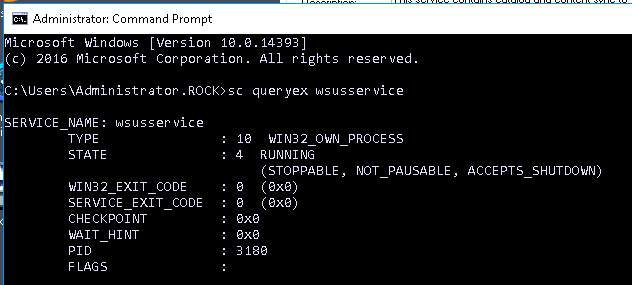
3. To get the PID type in – sc queryex [Service Name]
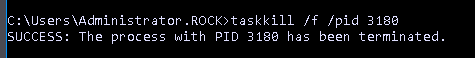
4. To kill the errant process type in – taskkill /f /pid [PID]
5. To remove the process type in – sc delete [Service Name]
One I had removed the process I restarted the server just to make sure then re-installed the software.
If your company needs help troubleshooting software issues, then contact us for assistance.
Every modern business has one thing in common – the internet.
Businesses are using computers, smart phones, tablets, etc. to connect to the internet for research, shopping, advertising, or any number of things. With a connection to the internet comes the need for routers, switches, wireless, and other network hardware to distribute internet connectivity across the company. There are malicious people on the internet that are setting traps and trying to break into companies which necessitate the use of tools like antivirus, internet filtering, spam filtering, and other protective measures. There are also people who work from their homes and need to have a way of tunneling safely into the network to use the resources there.
All of this has to be managed by someone in the company or you can contract with a managed IT service provider.
If your company needs help managing all the things connected to your internet, then contact us for assistance.
Make sure Hyper-V Host has CPUs than the combined total of CPUs for all servers being restored as these static until after the VMs are completely restored. If there is not enough CPU resources then the VMs will not boot.
Make sure Hyper-V Host has more than the combined total of RAM for all servers being restored as these settings are static until after the VMs are completely restored. If there is not enough memory then the VMs will not boot.
Create a SET NIC Team on the server (if you have multiple NICs)
Open Powershell as administrator
User the New-VMSwitch command to setup an external virtual switch to connect to for live connections
The AllowManagementOS is needed if you are using the same NIC team to access the VM host
Setup secondary Internal vSwitch to allow for testing before deploying
Setup Synology LUN targets for each VM to be restored. Make sure that they are big enough to hold all the full uncompressed size of the entire thick provisioned hard drives for the entire server.
Connect each LUN to the iSCSI Initiator on the VM Host. Make sure to bring them online, initialize them, and give them a drive letter. Synology needs this because it uses the SMB protocol to transfer the files during restore.
Make sure to allow the File and Printer Sharing app through the Windows firewall and open port 5986 to allow HTTP traffic for WinRM to allow Synology to query the Hyper-V settings.
Add the Hyper-V Host to the Active Backup for Business app.
Synology Active Backup Restore to Hyper-V
Open the Active Backup for Business app
Click on the Physical Server tab on the left
Select the server and click the Restore button
Select the point in time to restore from
Choose Restore to Microsoft Hyper-V
Choose Full Virtual Machine Restore
Change the Restore Name
Select a folder on the Hyper-V Host to place the configuration files
Select a folder on the Hyper-V Host to place each of the restore VHD files
Select a Virtual Switch on the Hyper-V Host to connect the VM to
Confirm the settings by clicking on the Done button.
After:
The VMs will boot with a single NIC and no network settings. Keep them offline and add additional NICs as needed to match the original setup. Then configure the NICs as before upon reboot. Make sure to connect to Internal Test Switch for initial steps.
Check hardware configuration of CPUs and RAM to determine if adjustments can be made. In particular, the RAM settings can be changed to startup, minimum, and maximum to allow for distribution of resources to VMs that have heavier workloads.
Boot VM to make sure it is functioning correctly. (first bootup can take upwards of 15 minutes)
Convert the VM from Gen1 to Gen2
Download Windows 10 ISO – https://www.microsoft.com/en-us/software-download/windows10
The information technology industry, also known as the IT industry, is a sizable and quickly expanding sector that includes a wide range of computing-related activities, such as software development, hardware manufacturing, networking, data analysis, cybersecurity, and digital marketing, among others.
At Farmhouse Networking, we utilize the power of IT to help our clients improve their businesses and elevate their services to the next level. Our group offers expert assistance to networks for small- to medium-sized businesses. We possess the range and depth of expertise necessary to effectively operate business-class networks thanks to years of experience.
Our team has been fervently pursuing the best technologies and tools for our clients! Our passion for delivering nothing but the best for our partners. Today, we are proud to announce that we are reaping the benefits of the fruits of our labors as we introduce our latest Clutch award. We’ve been named as one of the game-changing IT Managed Service Providers in Portland.
Clutch, for those of you who aren’t familiar with this company, they are an established platform in the heart of Washington, DC, committed to helping small, mid-market, and enterprise businesses identify and connect with the service providers they need to achieve their goals.
We would like to extend our sincere gratitude to Clutch, their staff, and everyone else who helped choose our company for this game-changer award. We are sincerely touched and appreciative of your acknowledgment.
Our company would also like to express our appreciation to clients and partners for their support. To show our gratitude and appreciation, here are some of the teams’ favorite reviews throughout the years!
Farmhouse Networking celebrated by Clutch as Portland IT managed services game-changer serving Oregon businesses with proven results.
“Farmhouse networking always has the help we need and seems to look out for our company like it was their business. Scott is never pushy and is always available to answer questions so we feel confident in our decisions.” Josh Confer, Webmaster at Chief Aircraft Inc
“Their customer service has been outstanding. Working with them on this project is perfect because they are already familiar with our location.” Mikaila Herman, Office Manager at Chinook Forest Management
As our business continues to grow our focus is on providing white labeled Tier 3 IT support services, RMM as a service, and co-managed IT services. This blog will be highlighting tips for using Powershell to get an Export List of AD Users Last Login was more than 90 Days Ago.
Research
You need to find out what the Organizational Unit (OU) path that you are trying to get the count from. The following command will list all OUs in the domain.
Get-ADOrganizationalUnit -Filter 'Name -like "*"' | Format-Table Name, DistinguishedName -A
If you want the entire organization then you will need the top level information which looks like DC=[DomainName],DC=local
Variables
$SearchOU = This is the full DistinguishedName from the above output.
The script will take several seconds to run based on the number of users in the OU being searched. The output is saved to the local c:\support directory and you can modify this script to include the FTP upload based on our previous article – https://www.farmhousenetworking.com/rmm/automation/rmm-automation-export-log-files-to-ftp/ The script can also be easily modified to change the number of days since last login.
If your company is a MSP or wants to become one and automation just seems out of reach, then contact usto run your RMM for you.
As our business continues to grow our focus is on providing white labeled Tier 3 IT support services, RMM as a service, and co-managed IT services. This blog will be highlighting tips for using Powershell to get an Active Directory User Count.
Research
You need to find out what the Organizational Unit (OU) path that you are trying to get the count from. The following command will list all OUs in the domain.
Get-ADOrganizationalUnit -Filter 'Name -like "*"' | Format-Table Name, DistinguishedName -A
If you want the entire organization then you will need the top level information which looks like DC=[DomainName],DC=local
Variables
$SearchOU = This is the full DistinguishedName from the above output.
The script will take several seconds to run based on the number of users in the OU being searched. The output is an integer number. You can do the same sort of thing for an Active Directory Group Count or Active Directory Computer Count:
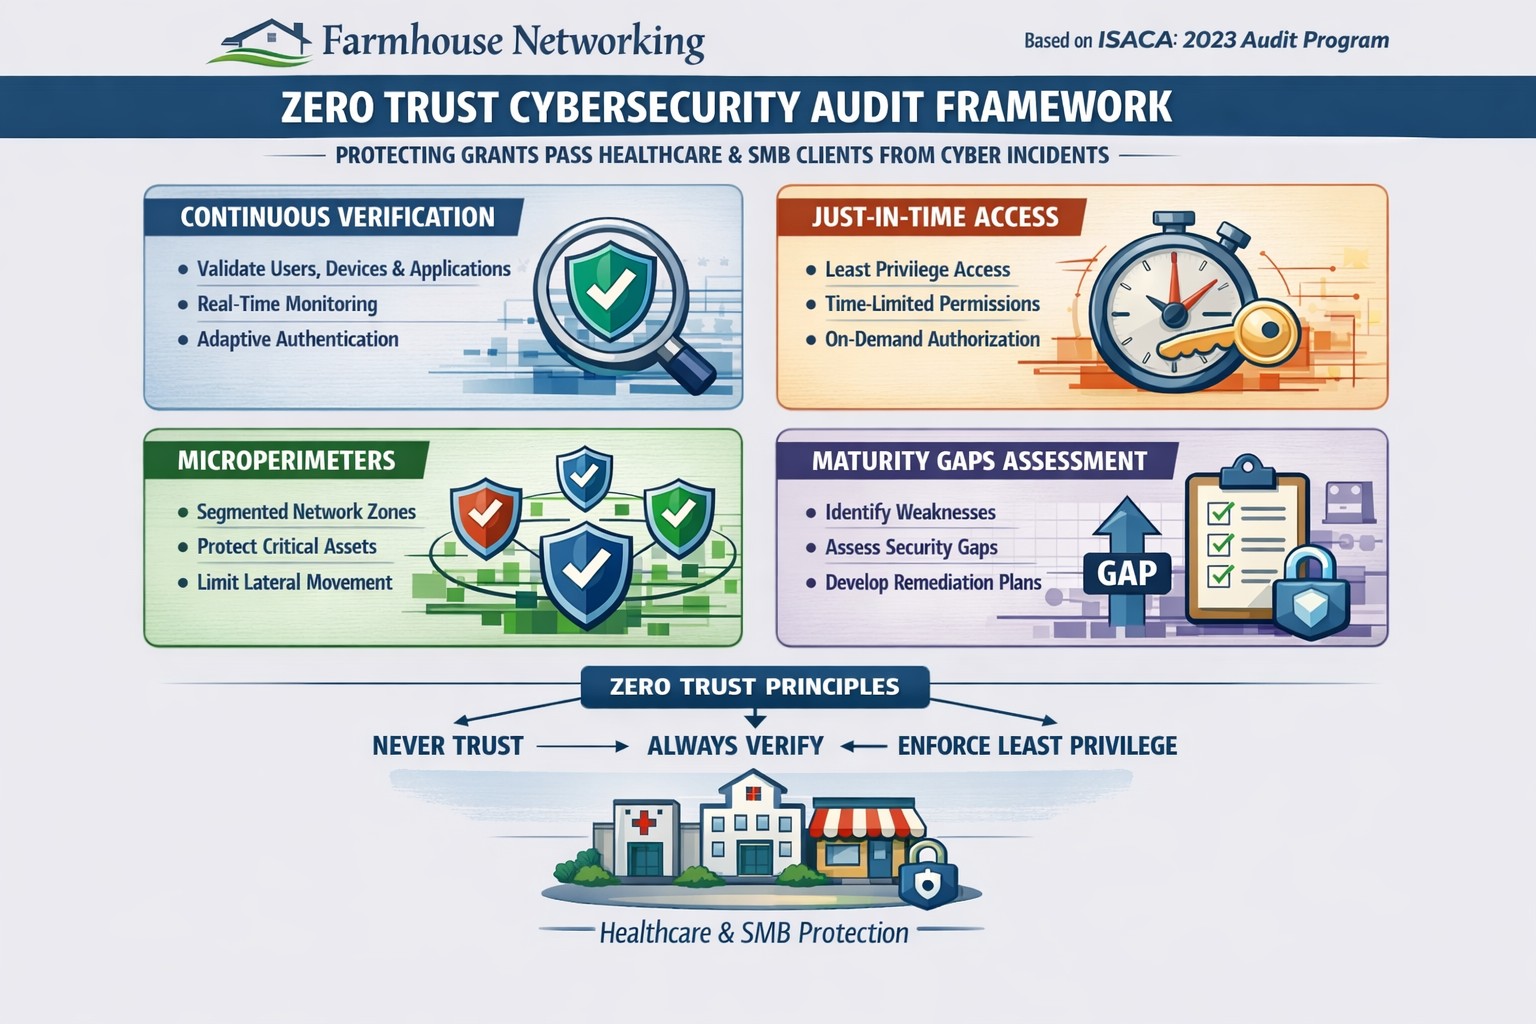
Farmhouse Networking 2023 zero trust audits verify continuous authentication and micro-segmentation for Oregon SMB cybersecurity compliance.
This is the tenth and finale in a series about the concept of Zero Trust, which means in the IT sense that you trust nothing and always verify everything surrounding and connected to your network. Today’s discussion will be on Cyber Security Audit.
Cyber Security Audit
Cyber Security Audit is a process where both internal and external systems are tested for their ability and susceptibility to being successfully attacked by hackers. This usually involves an inventory of current systems, research into known vulnerabilities, and testing of those found to see what information can be accessed. Once this process is complete a report is generated to detail both what is found and how those vulnerabilities can be addressed to protect the business’ most valuable commodity – information (intellectual property and client data). Here are some questions to ask:
Do you have an inventory of all assets in your organization? Is it up to date?
Have you tested your internal network for vulnerabilities?
Have you had a penetration test performed on your external network?
Do you know what compliance standards apply?
How do you document policies and procedures? Who oversees that?
If your company is wanting to have a free cyber security audit, then contact us for assistance.
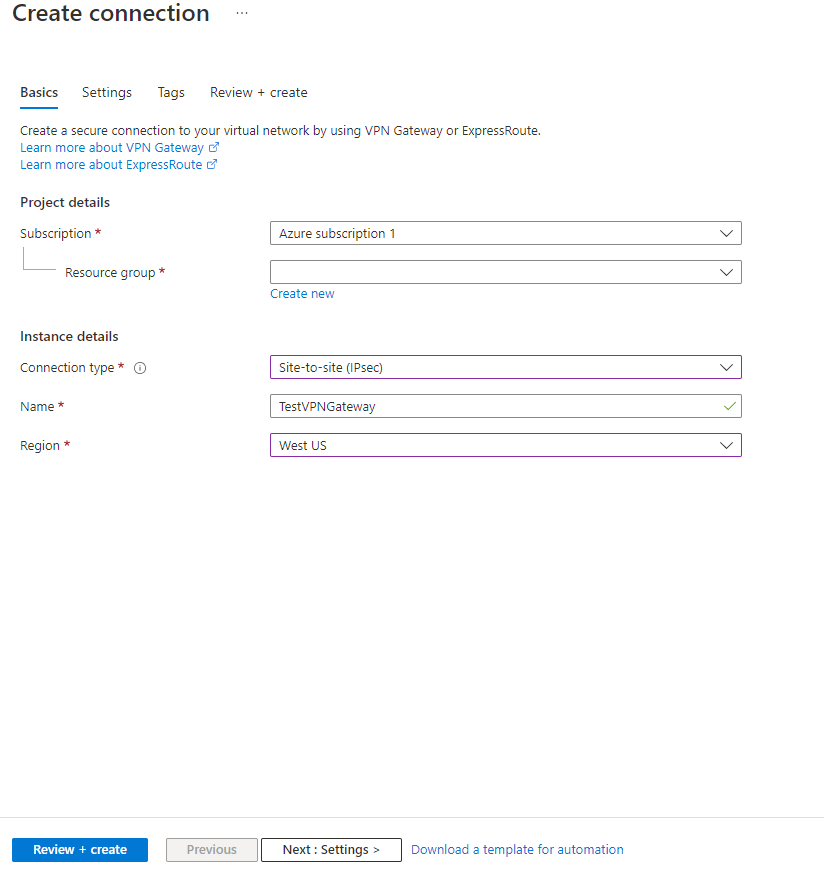
Had a local medial office want to move their current server into the cloud and because they are already an Office 365 customer, I chose to use Azure for their Virtual Machine. I helped them setup Azure to Araknis IPSec VPN to connect their headquarters to the hosted server. This tutorial will go into detail about the creation of this tunnel starting with the Microsoft Azure side first using Resource Manager. It will be using the following parameters:
VNet Name: TestNetwork
Address Space: 10.10.0.0/16
Subnets:
Primary: 10.10.10.0/24
GatewaySubnet: 10.10.0.0/24
Resource Group: TestResourceGroup
Location: West US
DNS Server: Azure Default
Gateway Name: TestVPNGateway
Public IP: TestVPNGatewayIP
VPN Type: Route-based
Connection Type: Site-to-site (IPsec)
Gateway Type: VPN
Local Network Gateway Name: TestSite
Local Subnet: 10.20.20.0/24
Connection Name: VPNtoTestSite
Configure an Azure VPN gateway
This part takes the longest, so it should be done first:
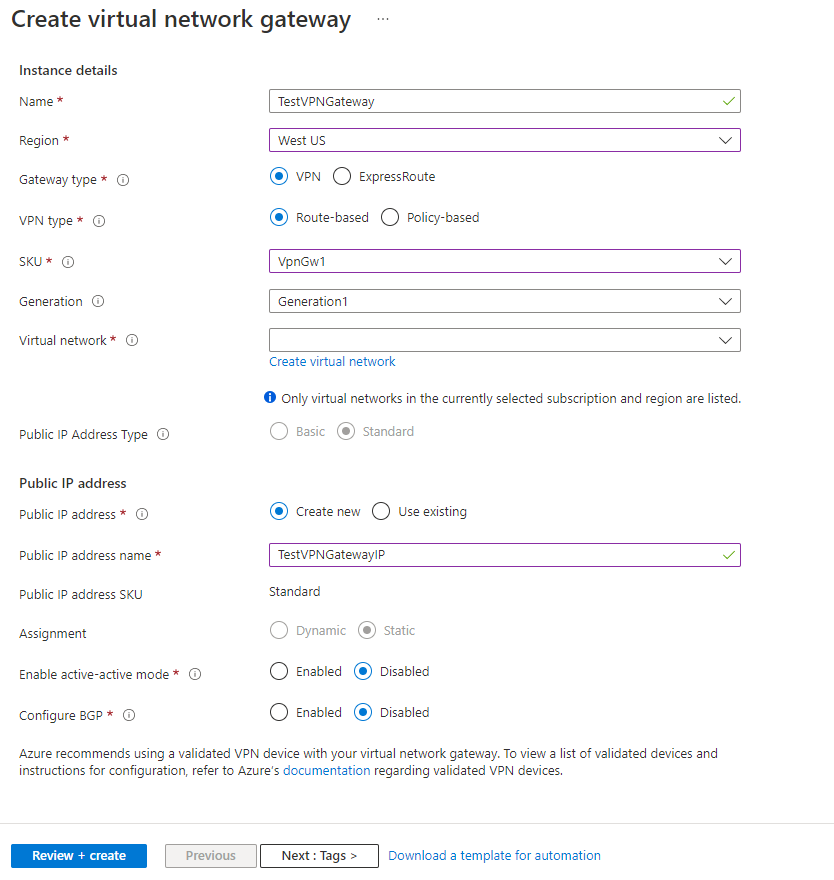
Click on the “+” icon at the top left hand side of the Resource Manager, then search for “Virtual Network Gateway” and click on the “Create” button.
Give the Virtual Network Gateway a name
Select matching Region to where Azure resources are located
Leave Gateway & VPN type the defaults
Choose a SKU <- These have changed since the article was created, so my “standard” now is WpnGw1 with Active / Active turned off (this is a good balance of performance and cost)
Choose or create a local network (not covered here, but must contain Gateway Subnet) that matches internal resources
Choose or create a Public IP Address
Leave the remaining values as their defaults and then click the “Create” button. (Please note the reminder that this takes 45 minutes to create!)
Configure an Azure Local Network Gateway
This is a reference to your on-premise network so that subnets can pass traffic:
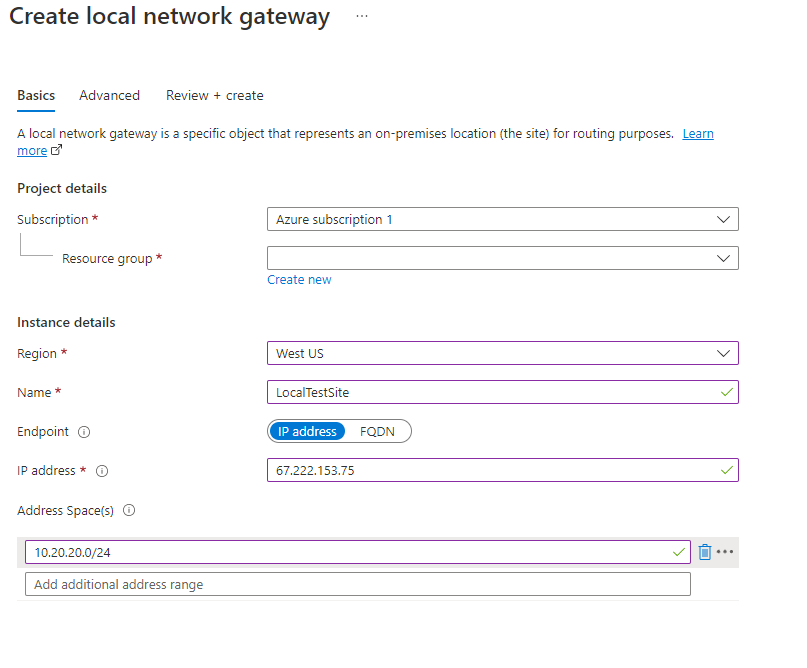
Click on the “+” icon at the top left hand side of the Resource Manager, then search for “Local Network Gateway” and click on the “Create” button.
Give the Local Network Gateway a name
Select matching Region to where Azure resources are located
Specify the external IP address of the local on-premise site
Specify the on-premise address space (subnet)
Leave the remaining values as their defaults and then click the “Create” button.
Configure an Azure VPN Connection
This will create the tunnel from Azure to the on-premise site:
Click on the “+” icon at the top left hand side of the Resource Manager, then search for “Connection” and click on the “Create” button.
Choose “Site-to-site (IPSec)” as the connection type
Give the Connection a name
Select matching Region to where Azure resources are located
Leave the remaining values as their defaults and then click the “OK” button. On the summary screen click on the “OK” button to create the connection.
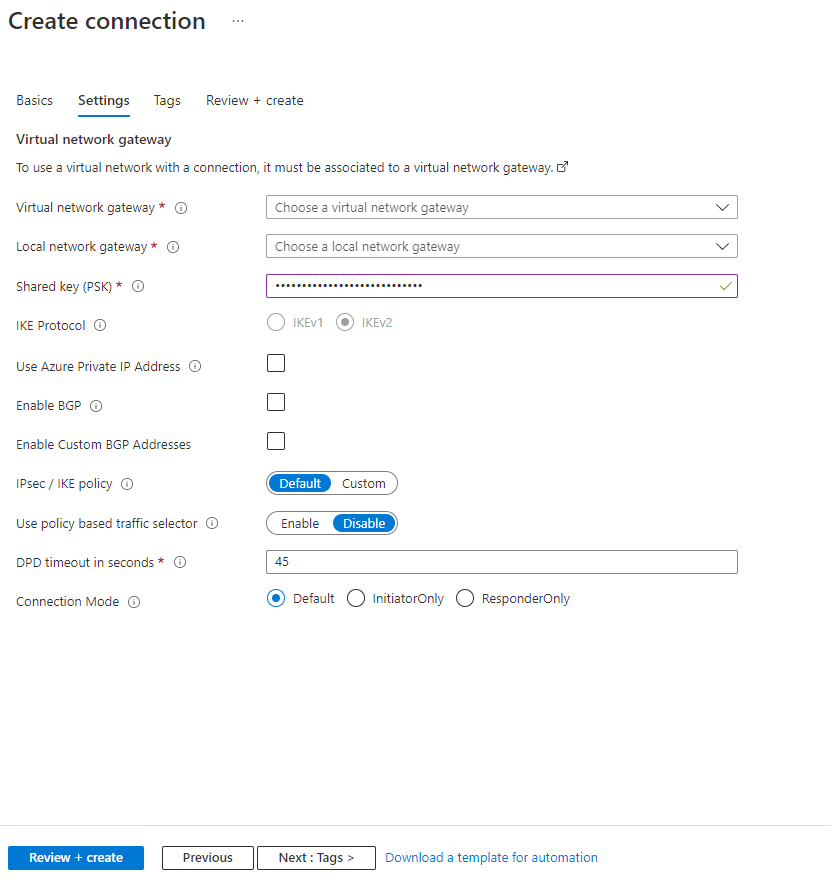
Choose the newly created Virtual Network Gateway
Choose the newly created Local Network Gateway
Specify a shared key
Leave the remaining values as their defaults and click the “Create” button.
This completes the setup of the Azure side of the VPN tunnel. Now to work on the Ubiquiti USG side.
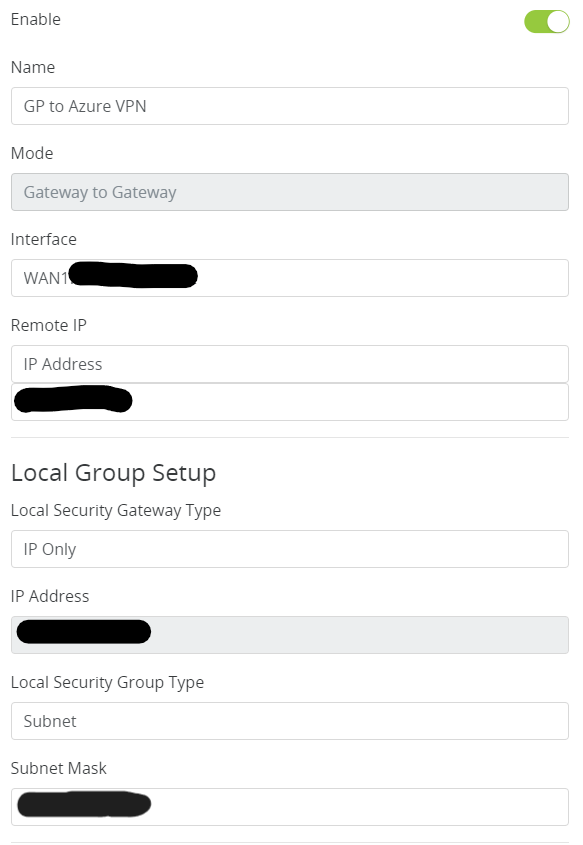
Configuring an Araknis IPSec VPN Network
Connect to Araknis router (need at least a 310 for this to work)
Click on Advanced > VPN
Scroll down to IPSec and click add new tunnel
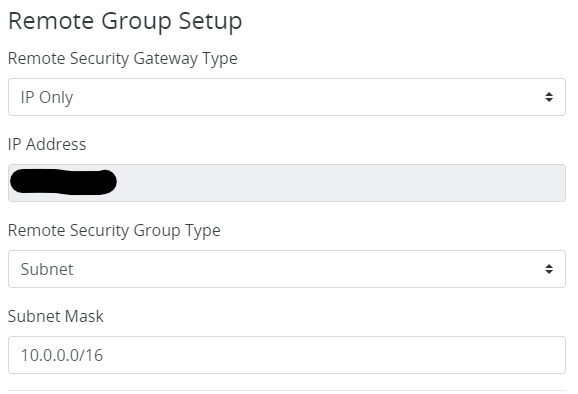
Fill in the Remote IP address of the Azure VPN Gateway
Fill in the Remote Subnet Mask
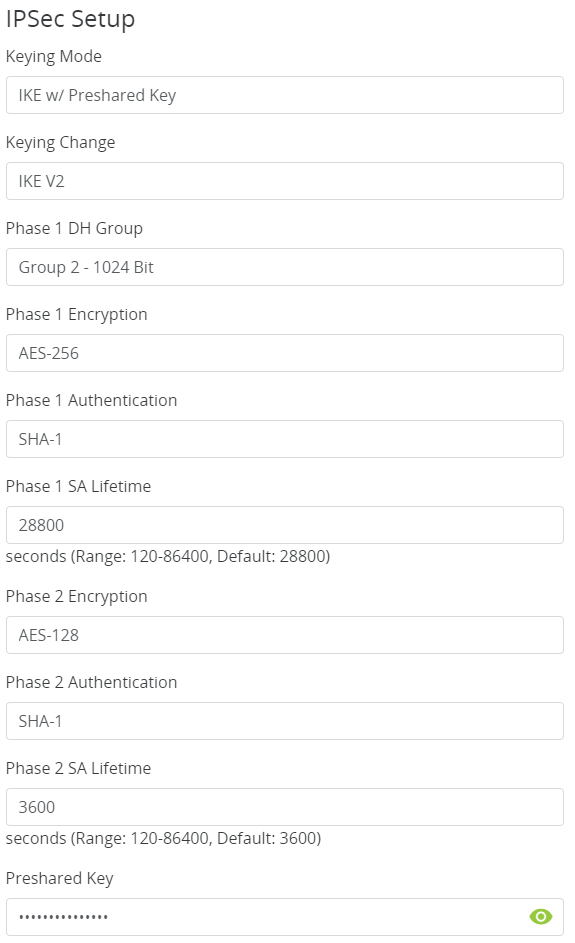
Make the following changes to IPSec Setup
That is all there is to it. If your company is currently using either Microsoft Azure or Araknis routers and would like a VPN created, then contact us for assistance.
Farmhouse Networking protects Oregon businesses from 2023 Facebook imposter scams and Instagram phishing targeting SMB owners.
In today’s social media age, we are more interconnected than ever before. While this can be great for keeping up with loved ones and shedding light on current events, it also opens a new door for scammers. Last year, annual reported losses from social media scams hit $1.1 billion. Here are the five most common types and our recommendations for protecting yourself, and your business, from them:
Phishing Scams: Scammers attempt to trick you into revealing personal information by posing as a trustworthy source in an email or message. To avoid these scams, never click on links from unknown sources and always verify the sender’s identity.
Impersonation Scams: Scammers create fake profiles and impersonate others to deceive and scam others. To avoid these scams, check profiles for authenticity by verifying their information, friends, and photos.
Giveaway Scams: Scammers promise a prize or giveaway in exchange for personal information or a payment. To avoid these scams, never give out personal information, and only participate in giveaways from reputable sources.
Investment Scams: Scammers promise high returns on investments, but it is just a trick to steal your money. To avoid these scams, do thorough research before investing, be cautious of unrealistic returns, and don’t fall for pressure tactics.
Malware Scams: Scammers use social media to spread malicious software that can harm your device or steal personal information. To avoid these scams, don’t download anything from untrusted sources and keep your device’s security software up-to-date. Our goal at (Company Name) is to keep you safe while you’re scrolling. Speaking of social media, feel free to follow us @[handle] on Facebook and @[handle] on Instagram for more security tips and product updates.
Our goal at Farmhouse Networking is to keep you safe while you’re scrolling. Speaking of social media, feel free to follow us on LinkedIn for more security tips and product updates.
Farmhouse Networking’s zero trust security model prevents lateral movement
This is the ninth in a series about the concept of Zero Trust, which means in the IT sense that you trust nothing and always verify everything surrounding and connected to your network. Today’s discussion will be on Network Security.
Network Security
Network Security is having the proper hardware and configuration of that hardware in place to protect the business network. This configuration includes segmenting network traffic to keep specific types of traffic, like guest devices, separate from traffic of business devices. It also includes keeping outsiders out of the network and detecting when they have breached security measures. Here are some questions to ask:
Do you have a business class router / firewall?
Do you have business class switches and access points that support segmentation?
Is your network configured to segment business traffic from guest traffic?
Are devices like VoIP phones and network cameras on their own network?
Is geo-location blocking turned on for non-essential countries?
Is network traffic being analyzed for suspicious activity?
Do you filter internet traffic?
Can your network detect and respond to a breach?
If your company is wanting to lock down network security, then contact us for assistance.
Farmhouse Networking virtualizes small office servers reducing hardware footprint while improving uptime and disaster recovery for Oregon SMBs.
Had a client recently who had a smaller office network (they have up to 6 concurrent users) with a server to process orders from their website using a software called StoneEdge. This software is SQL-based database with a Microsoft Access front-end. It was time to upgrade their server to new hardware and cost was definitely an issue based on their size and order volume. In this case we chose to use a Synology device to act as the virtual machine host and create a new virtual server on the host. Here are some details:
4x Seagate 4TB IronWolf Pro 7200 rpm SATA III 3.5″ Internal NAS HDD
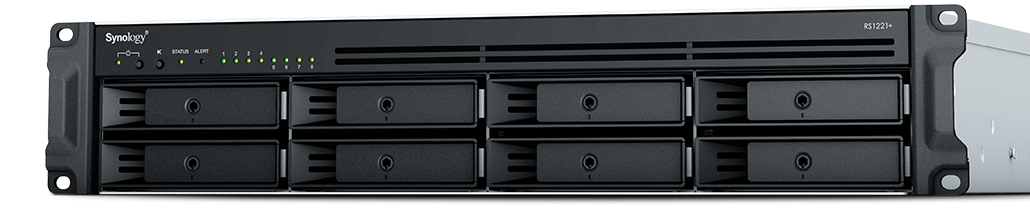
Picked the Synology based on the expandability of RAM to 32 GB, the capability to use cache drives, and storage growth over time. It also has a 4-core 2.2 Ghz Ryzen processor which was plenty based on their old servers CPU usage.
Basics of Setup
Assembled parts
Installed Synology OS
Setup HDDs in Synology SHR2 RAID
Added M.2 drives as cache
Installed the Virtual Machine Manager app
Created a VM with the max CPU available and max Memory available
Uploaded the ISO for the server OS
Installed the server OS
Setup the StoneEdge application
Migrated data
This build did not increase performance dramatically, but it did allow them to spend about half the cost of a full server to accomplish the same purpose. It also reduced costs by using the Synology for backup of the server locally and into S3 storage in the cloud for redundancy.
If your company is looking to move their servers to a virtual environment or into the cloud, then contact usto start the process
Farmhouse Networking installs Wi-Fi 6E eliminating 2.4/5 GHz congestion for Grants Pass businesses using clean 6 GHz spectrum.
Wi-Fi technology is ingrained into our everyday lives WE COLLECTIVELY STREAM more movies and TV shows, play more online games, and make more video calls than ever before, and all this activity puts a serious strain on our Wi-Fi networks. Wi-Fi 6e has various features to improve the efficiency and data of your wireless network and reduce latency. the latest Wi-Fi 6e standards offers a range of benefits, including faster and more reliable access. So, what is Wi-Fi 6e and what are some of the benefits?
Wi-Fi 6e explained
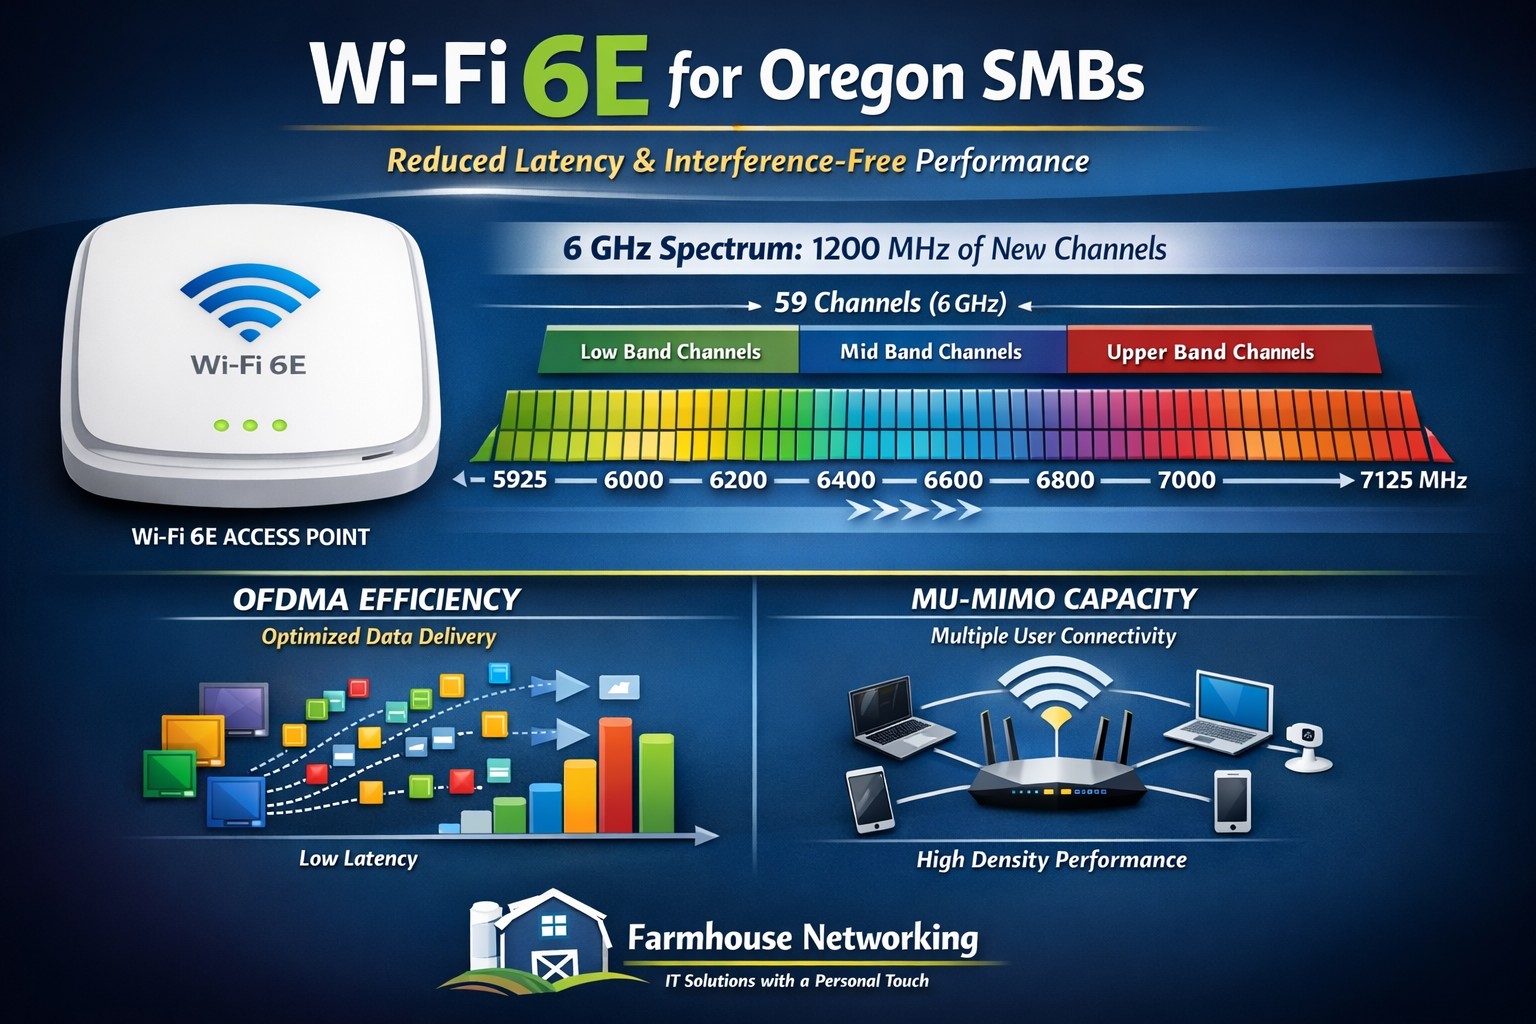
Existing technologies operate on two frequencies 2.4 GHz and 5GHz which have become more congested over time; Wi-Fi 6e adds access to a third frequency, 6GHz. now wireless devices can also use the 6GHz band. And the 6GHz band opens up the opportunity for higher transfer speeds. On top of that, currently there are about four 160 MHz-wide channels with normal Wi-Fi this 6GHz band brings with it seven 160 MHz-wide channels, More available channels mean more available spectrum for Wi-Fi service “and less overlap between networks in crowded areas like apartment complexes or offices,”. with less overlap and congestion you are able to connect more devices with the same efficiency expectation. Additionally there have been security improvements with Wi-Fi 6E that puts the burden on the router, rather than you, to secure connections between your devices. WPA3 is mandatory for all Wi-Fi 6 certified devices, which provides the latest security and authentication protocols.
Summary of Benefits
Faster, more reliable connection
Transmits data faster with less interference.
You don’t have to compete with traffic from other devices or networks.
Security improvements making it more secure and harder to hack
Accommodates more connected devices
If your company is looking to upgrade the wireless coverage in your office, whole building, or entire business complex, then contact usto evaluate your WiFi needs.
Farmhouse Networking resolves credential manager clearing after reboot by deleting Microsoft Vault folder and restarting services for Oregon RMM automation.
As our business continues to focus on providing white labeled Tier 3 IT support services, RMM as a service, and co-managed IT services this blog will be highlighting tips for using Powershell to fix Credential Manager empty after reboot. There has been several users at a bunch of clients recently that have lost access to a network share due to saved passwords and we found Credential Manager empty after reboot. It was easy enough to re-add their password to Credential Manager, but it was not sticking around. This sounds like a job for automation, so we created a script to clear the errant Credential Manger files and create a new entry for the user to connect to file shares.
Variables
$user = username to add to Credential Manager of network share connection
$pass = password to add to same
Script Snippet
### Remove file folder associated with Credential Manager
Remove-Item -Path %localappdata%\Microsoft\Vault -Recurse

### Install Credential Manager Powershell Module
Import-Module -Name CredentialManager -Force

### Convert password to Secure String and create credential
$password = ConvertTo-SecureString -string $pass -AsPlainText -Force
$Credential = new-object -typename System.Management.Automation.PSCredential -argumentlist $user, $password

# Save the credential object directly without unwrapping it:
New-StoredCredential -Credentials $Credential -Target 'Share Credentials' -Persist Enterprise -Comment "Share Credentials for $($Credential.UserName)" > $null
This script will need to be run in the context of the user who needs the credential created. Please use caution with this script as it will empty Credential Manager completely for the user context run with. Also it is advised to run a full CHKDSK /R on the root (C:\ usually) directory to make sure that nothing else is corrupt on the drive.
If your company is a MSP or wants to become one and automation just seems out of reach, then contact usto run your RMM for you.
As our business continues to focus on providing white labeled Tier 3 IT support services, RMM as a service, and co-managed IT services this blog will be highlighting tips for using Powershell to create Office 365 User and add them to groups. We have several clients with high employee turn-over which makes it necessary to often create Office 365 user. We will detail how to find all the needed data to create the proper script for each client (yes it will take a different script for each client due to different group names for each client).
Research
You need to get two pieces of information – the license type used by the organization to create users and the names of the groups to add users to
To find out the license types used use this commands:
Connect-MsolService
Get-MsolAccountSku
To find out all the groups in the organization use this commands:
Connect-ExchangeOnline
Get-UnifiedGroup | Format-Table Alias
Variables
$displayName = Full user name – usually First name & Last Name $userPrincipleName = Email address for user $adminuser = Email address for admin of Office 365 Tenant $adminpass = Password for admin of Office 365 Tenant $licenseType = Office 365 license type found in research above
There is also the need for variables for each group you will be adding users to (found in research above). For this example I will be using:
$CompanyShared = Company Shared Contacts $CompanyTimeOff = Company Time Off Calendar $BillingPayroll = Billing & Payroll Group Email
Script Snippet
###Use this command to be allowed to use DotNet assemblies
Add-Type -AssemblyName System.web

$displayName = "UserFirst UserLast"
$userPrincipleName = “User@Company.com”
$adminuser = "admin@Company.com"
$adminpass = '@dm1nP4ssw0rd'

$CompanyShared = "yes"
$CompanyTimeOff = "yes"
$BillingPayroll = "no"

###converts admin credentials to useable format for connections to Office 365
$adminpassword = ConvertTo-SecureString -string $adminpass -AsPlainText -Force
$admincred = new-object -typename System.Management.Automation.PSCredential -argumentlist $adminuser, $adminpassword

Connect-AzureAD -Credential $admincred
Connect-MsolService -Credential $admincred

$mailNickname = $userPrincipleName.Split("@")[0]

###To find User License Types use Get-MsolAccountSku
$licenseType = "companytenantID:SPB"

###Generates a random password length
$minPassLength = 8 ## characters
$maxPassLength = 15 ## characters
$passlength = Get-Random -Minimum $minPassLength -Maximum $maxPassLength

###Generates a random number of non-alpha characters in the password
$minNonAlphaChars = 1 ## characters
$maxNonAlphaChars = 5 ## characters
$nonAlphaChars = Get-Random -Minimum $minNonAlphaChars -Maximum $maxNonAlphaChars

###Creates the password, makes it useable by Azure, sets it up to not require password change, and creates account
$password = [System.Web.Security.Membership]::GeneratePassword($passlength, $nonAlphaChars)
$PasswordProfile = New-Object -TypeName Microsoft.Open.AzureAD.Model.PasswordProfile
$PasswordProfile.Password = "$password"
$PasswordProfile.ForceChangePasswordNextLogin = $false
Write-Host "Password is set to $password for $displayName"
$user = New-AzureADUSer -DisplayName $displayName -PasswordProfile $PasswordProfile -UserPrincipalName $userPrincipleName -mailNickname $mailNickname -AccountEnabled $true

###Waits 5 minutes for the user creation process in Office 365
Start-Sleep -Seconds 300

###Sets additional parameters for account that are needed like location, license type, and sets password to never expire
Get-MsolUser -UserPrincipalName $userPrincipleName | Set-MsolUser -UsageLocation US
Get-MsolUser -UserPrincipalName $userPrincipleName | Set-MsolUserLicense -AddLicenses $licenseType
Get-MsolUser –UserPrincipalName $userPrincipleName | Set-MsolUser –PasswordNeverExpires $True

###Adds new user to groups
if ($CompanyShared -eq "yes")
{ Add-MailboxPermission -Identity companyshared@premieror.com -User $userPrincipleName -AccessRights FullAccess -InheritanceType All}

if ($CompanyTimeOff -eq "yes")
{ Add-MailboxPermission -Identity companytimeoff@premieror.com -User $userPrincipleName -AccessRights FullAccess -InheritanceType All}

if ($BillingPayroll -eq "yes")
{ Add-MailboxPermission -Identity billing_payroll@premieror.com -User $userPrincipleName -AccessRights FullAccess -InheritanceType All}
This script requires that the admin account you use to setup the user have multifactor authentication turned off (I know not secure), so use a really long complex password. The script creates a random password for the new user and write it to output. The script will take several minutes to run due to the waiting for the account to finish setup before adding additional parameters and adding them to groups.
If your company is a MSP or wants to become one and automation just seems out of reach, then contact usto run your RMM for you.
As our business continues to focus on providing white labeled Tier 3 IT support services, RMM as a service, and co-managed IT services this blog will be highlighting tips for Synology resource monitoring. We have developed best practices for alerting on a Synology device for resources like CPU, Memory, and Disk Usage. When these Synology resource monitoring alerts are consistently triggered it show that the device is over utilized or if they remain triggered for long periods of time then it shows there is an issue on the device itself. We also setup weekly Storage Reports to get an accurate view of the changes and growth going on with client storage.
Setup Notifications
Make sure that Notifications are setup on the Synology first
Open Control Panel
Click on Notifications
Check enable email notifications
Choose Service Provider
Login to Gmail or use Custom SMTP server for Office 365 as the sender
Change Subject to indicate name of device
Add recipient email (Best to use one that ties into a PSA or RMM)
Click Apply
Send a Test Email
Setup Synology Resource Monitoring
Open Resource Monitor app
Click on Performance Alarm to the left
Click on Rules tab
Click Create
Create the following Rules one by one
Volume Critical
Select which volume [create multiple rules if more than one volume]
Select Disk I/O utilization
Greater than 90%
Level Critical
Volume Warning
Select which volume [create multiple rules if more than one volume]
Select Disk I/O utilization
Greater than 75%
Level Warning
System Memory Critical
Memory Usage
Greater than 90%
Level Critical
System Memory Warning
Memory Usage
Greater than 75%
Level Warning
System CPU Critical
CPU Usage
Greater than 90%
Level Critical
System CPU Warning
CPU Usage
Greater than 75%
Level Warning
Click Settings and check box to Enable usage history then click Save
Setup Storage Reports
Open Storage Analyzer
Select new location
Create new shared folder named Log Files – hide from network
Go back to Storage Analyzer and select new folder
Set volume usage data to be collected Daily at 2am
Create report task
Send to email (Best to use one that ties into a PSA)
Generate reports at Monday 4am
Keep 60 reports then click Next
Select report items
Volume Usage
Shared Folders
Potential Duplicate Files
Large Files
Least Recently Modified Files then click Next
Analyze all folders then click Next
Leave duplicate file defaults then click Next
Click Done
Close App
Once this is setup you will start getting email alerts sent to you or better yet your PSA / RMM for ticket creation and review.
If your company is a MSP or wants to become one and automation just seems out of reach, then contact us to run your RMM for you.
This is the eighth in a series about the concept of Zero Trust, which means in the IT sense that you trust nothing and always verify everything surrounding and connected to your network. Today’s discussion will be on Application Whitelisting.
Application Whitelisting
Application Whitelisting is a process of determining which software programs the company absolutely needs to do business, marking them as safe, and blocking any other program that tries to run on company computers. This methodology has the distinct advantage of blocking almost all forms of malware on computers. Pairing this with a good next-gen antivirus creates an impenetrable wall against malware threats. It also prevents users from accidentally or intentionally running something that should not be on company computers. Here are some questions to ask:
Do you know all software on your computers?
Do your users spend time on company computers listening to music?
Have any of your users ever downloaded software without asking?
Do you have a computer use policy? How is that enforced?
If your company is wanting to lock down what is running on company computers, then contact us for assistance.
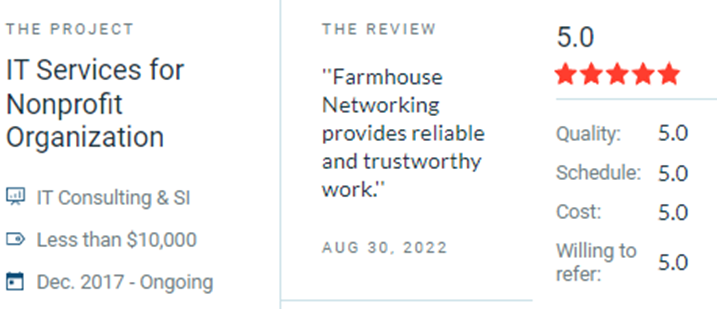
Farmhouse Networking leads as top-reviewed collaboration consultant optimizing Microsoft Teams for Oregon businesses.
At Farmhouse Networking, we provide professional support for small to medium business networks. Our mission is to bring grass-roots IT support to local and national businesses. We analyze the processes that make business happen, then help you develop long-term plans to ensure that your IT system fosters the growth your business requires to blossom.
For this reason, we proudly share a milestone for Farmhouse Networking. The Manifest has recognized us as a leading and most reviewed global productivity and collaboration company. The Manifest is a business blog and reviews platform aiming to link buyers with vendors that can help them with their ongoing or upcoming projects.
Since our establishment in 2015, we have worked with trusted hardware and software vendors to add the essential elements which provide a nourishing medium to make your business flourish. Since our founding, we have developed the breadth and depth of knowledge required to manage business-class networks properly.
Chief Aircraft Inc, an online aircraft parts retailer, engaged in an ongoing collaboration with us in 2016 for managed IT services. The project started when the client was transitioning, and we stepped in to help modernize their systems and set up a solution to back up and monitor their network properly.
“In upgrading our network and data backups Scott has managed to lower the cost to us on a long-term basis and make everything easier to access as well as more secure.” – Josh Confer, Webmaster, Chief Aircraft Inc
The whole team at Farmhouse Networking would like to use this opportunity to communicate how much we value all our clients and partners. The feedback they’ve written means so much to us and will help us cement our name in the industry. If you need a caring expert to tend to your computers and network while you do business, get in touch with us. Our organic IT support is only a phone call away
Farmhouse Networking in Grants Pass Oregon celebrates earning the UpCity Best of Oregon Award for trusted managed IT services and local business IT support.
Farmhouse Networking has been working to establish our reputation and grow our business to serve others in the surrounding areas. God has continued to be gracious to provide that growth and it is being recognized.
“Every year, UpCity’s Best of Awards honor our B2B service providers’ tremendous work within rotating focus areas. Winners are selected using a variety of online credibility ranking factors which remain consistent regardless of the year’s focus area. In 2022, we celebrate the best providers at the local level for each U.S. state and Canadian province.”
Thank you to all our clients for making this possible as we continue to serve your IT needs.
And God will generously provide all you need. Then you will always have everything you need and plenty left over to share with others. As the Scriptures say, “They share freely and give generously to the poor. Their good deeds will be remembered forever.” For God is the one who provides seed for the farmer and then bread to eat. In the same way, he will provide and increase your resources and then produce a great harvest of generosity in you. - 2 Corinthians 9:8-10
We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.