How to Get Breached, Step 4: Turn Off MFA. Those Pop-Ups Are So Annoying.
Why attackers love MFA fatigue, and how to make multi-factor authentication stronger without driving your team crazy
MFA fatigue attacks count on someone tapping Approve just to make the prompts stop. Number matching, phishing-resistant MFA, and conditional access take that option away.
Welcome back to our guide to doing security wrong. You’re reusing passwords and clicking every link in your inbox. Nice work. This week’s tip is the easiest yet: turn off multi-factor authentication. All those “Is this you signing in?” prompts slow everyone down. And if you can’t turn it off, tap Approve on every one. Your phone stops buzzing, and that’s what matters, right?
Here’s what that looks like in practice.
A Hypothetical Late-Night Buzz
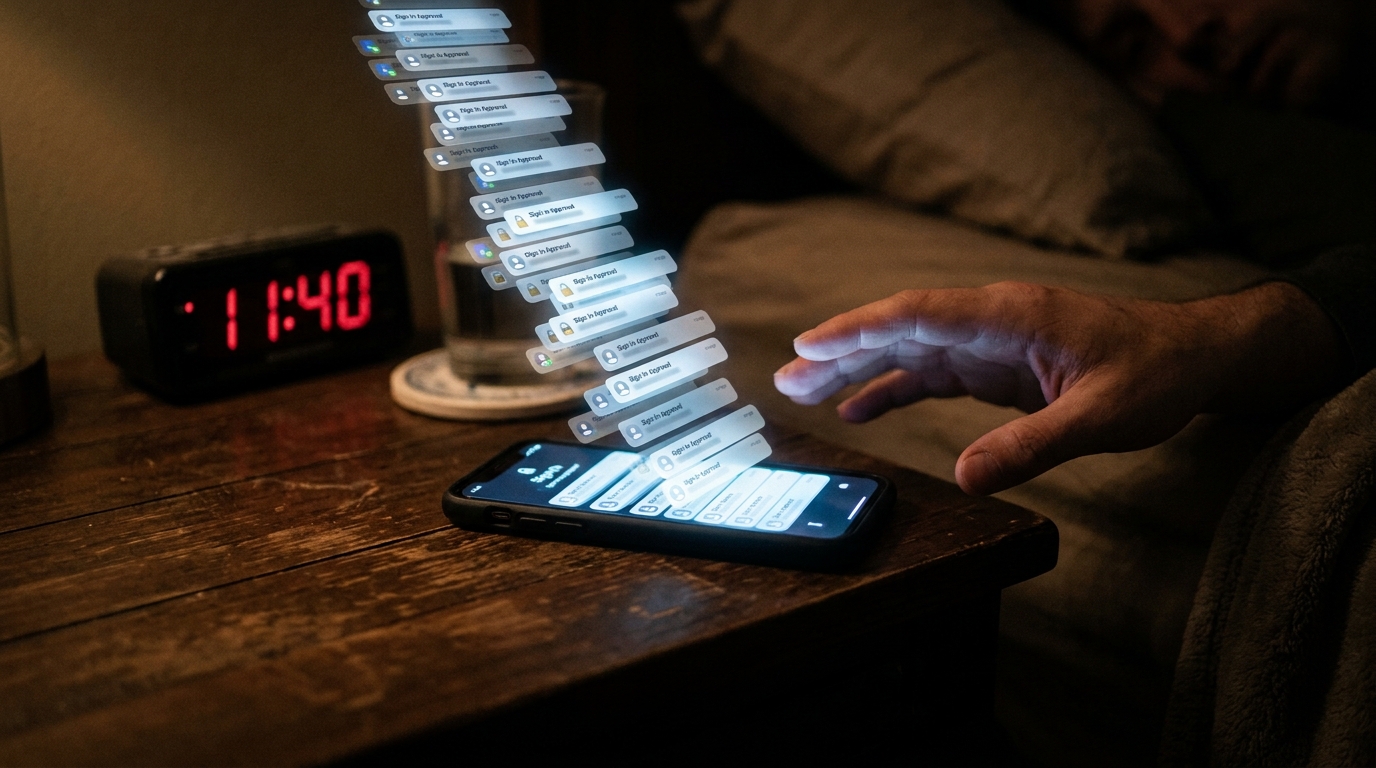
Picture the office manager at a 25-person company. At 11:40 p.m., her phone lights up with a sign-in request. She taps Deny. It comes back. And again. Around the fifteenth prompt, she approves one just to make it stop and goes back to sleep.
The person on the other end already had her password from a list of stolen credentials. By morning, they’ve read two years of email, set up a rule that quietly forwards invoices to an outside address, and sent customers “updated” payment instructions. Nobody broke any encryption. One tired person approved one prompt.
Why MFA Still Matters, and Where It Falls Short
MFA works because a stolen password alone isn’t enough to get in. That’s why attackers now focus on getting around it:
MFA fatigue (push bombing). The attacker already has the password and floods the user with approval requests, hoping one gets accepted out of frustration. Some follow up with a call or text pretending to be IT.
Phishing proxies. A fake login page passes your password and your six-digit code to the real site in real time. Codes and simple push approvals can both be captured this way.
Help desk tricks. An attacker calls in as an employee who “got a new phone” and asks for MFA to be reset.
The Cybersecurity and Infrastructure Security Agency (CISA) calls phishing-resistant MFA, such as passkeys and FIDO2 security keys, the gold standard. For push notifications, CISA recommends number matching as an interim step: the user types a number shown on the login screen into their app before access is granted.
Conditional access ties it together. Instead of treating every sign-in the same, it sets rules for who can sign in, from where, on which devices, and when to ask for stronger proof. Done well, it means fewer prompts on trusted company devices and tougher checks only when something looks off.
Action Steps for Business Owners and IT
Require MFA on every account. Email, Microsoft 365 or Google Workspace, remote access, payroll, banking, accounting, and line-of-business apps. That includes the owner and every admin. Especially the owner and every admin.
Replace simple Approve/Deny prompts. Use an authenticator app with number matching enabled, and phase out text message codes wherever possible.
Give high-risk users phishing-resistant MFA. Owners, admins, and anyone who moves money should use passkeys or FIDO2 security keys.
Turn on Conditional Access. For most small businesses on Microsoft 365, that means Business Premium. Block legacy sign-in methods that skip MFA, block countries you don’t do business in, require company-managed devices for sensitive data, and require stronger sign-in for admin roles and risky logins.
Lock down MFA resets. Verify identity before anyone’s MFA method is changed, and alert when a new device is registered.
Watch for warning signs. Repeated denied prompts, new MFA methods, logins from unexpected locations, and new mailbox forwarding rules should trigger an alert someone actually reads.
Teach one simple rule. If you didn’t start the sign-in, deny it and report it right away. Keep it no-blame, so an employee who approved something by mistake speaks up in minutes instead of hiding it.
Write it down. Document your MFA policy, any exceptions, and who approved them.
Questions Your Customers May Ask You
“If one of your employees gets phished, is my information exposed?” A stolen password alone shouldn’t get anyone in. Every account that touches customer information requires a second check, and our most sensitive accounts use phishing-resistant sign-in.
“Why does your portal make me verify with a code?” It keeps a stolen password from being enough to reach your information. The extra step takes seconds.
“How would you know if someone got into your systems?” We monitor for unusual sign-in activity, like repeated denied approvals or logins from unexpected places, and our team knows to report anything suspicious immediately.
How Farmhouse Networking Can Help
Since 2015, Farmhouse Networking has helped small and mid-sized businesses make security practical. We:
Roll out MFA with number matching, plus passkeys or security keys for owners and admins
Build Conditional Access policies in Microsoft 365 Business Premium that fit how your team works
Enable banned-password protection and dark web monitoring to catch stolen credentials early
Alert on suspicious sign-in patterns through our Wazuh SIEM monitoring
Run simulated phishing and staff training, including how to spot push bombing
Our U.S.-based team answers the phone live, so when an employee gets a strange prompt at 4:55 p.m., they reach a person, not a voicemail box.
Get a Free Breach-Readiness Review
Not sure which accounts have MFA, which still rely on text codes, or whether older sign-in methods are bypassing it altogether? Email support@farmhousenetworking.com for a free breach-readiness review. We’ll show you where the gaps are and what to fix first.
Next week: How to Get Breached, Step 5: Paste Client Data Into Any AI Tool You Find. It’s fast, it’s free, and what could go wrong?
And God will generously provide all you need. Then you will always have everything you need and plenty left over to share with others. As the Scriptures say, “They share freely and give generously to the poor. Their good deeds will be remembered forever.” For God is the one who provides seed for the farmer and then bread to eat. In the same way, he will provide and increase your resources and then produce a great harvest of generosity in you. - 2 Corinthians 9:8-10
We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.