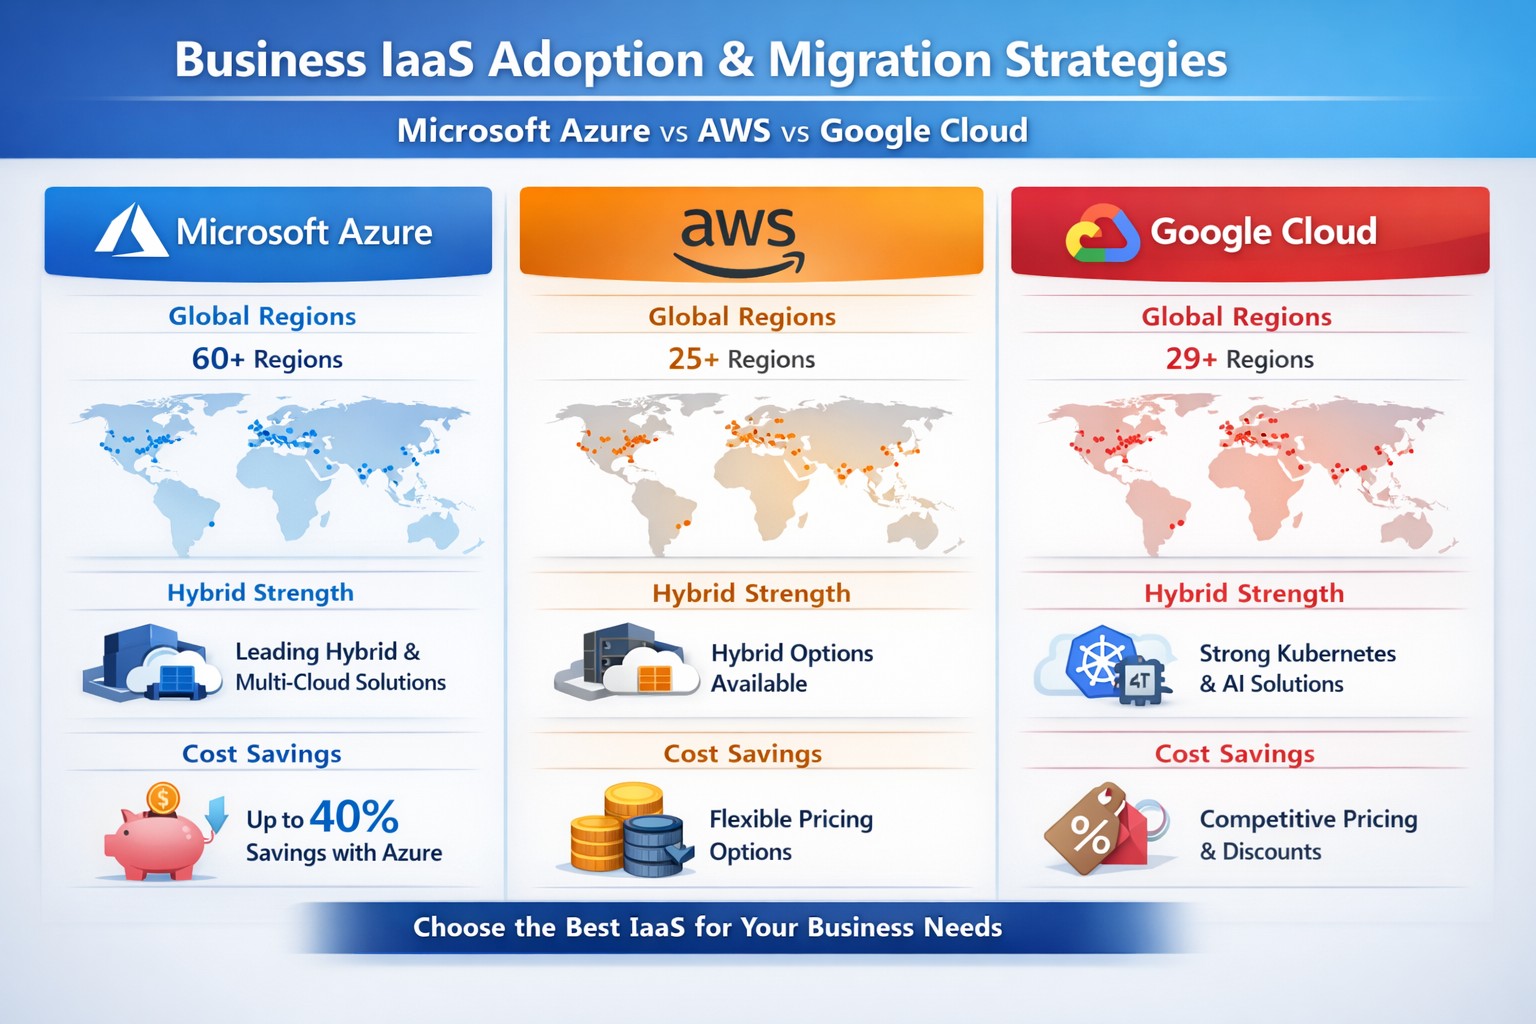
Azure IaaS leads with 60+ regions and hybrid tools, delivering superior ROI for business owners vs AWS EC2 and Google Compute.
Business owners seeking scalable, cost-effective infrastructure need proof before committing to cloud providers. Microsoft Azure IaaS delivers with superior hybrid integration, global reach exceeding 60 regions, and proven uptime SLAs up to 99.9%, outperforming AWS and Google Cloud in Microsoft-centric environments.
Azure IaaS vs. Competitors: Key Data Points
Azure leads in hybrid cloud capabilities, essential for businesses retaining on-premises systems. With Azure Arc and Azure Stack, manage multi-cloud and local resources seamlessly—unlike AWS’s less integrated hybrid tools or GCP’s limited options.
Metric
Azure IaaS
AWS EC2
Google Cloud Compute
Regions
60+
33
40+
Data Centers
300+
200+ est.
100+ est.
Hybrid Strength
Best (Azure Arc)
Moderate
Limited
Microsoft Integration
Native (Windows/SQL)
Limited
Minimal
Pricing Savings
Up to 72% reservations; Hybrid Benefit
Complex PAYG
Sustained discounts
Azure’s 20% market share trails AWS but dominates government, education, and enterprises using Microsoft tools, reducing migration friction and costs.
Practical Action Steps for Implementation
Assess Current Infrastructure: Inventory servers, apps, and data. Use Azure Migrate (free tool) to scan on-premises for compatibility—takes 1-2 days with IT team.
Pilot Migration: Provision Azure Virtual Machines in your nearest region. Start with non-critical workloads; leverage Azure Hybrid Benefit to apply existing licenses, cutting costs 40-72%.
Secure and Scale: Enable Microsoft Entra ID for IAM and Azure Sentinel for AI threat detection. Set auto-scaling policies to match demand, ensuring 99.9% SLA.
Monitor ROI: Track via Azure Cost Management. Expect 30-50% savings vs. on-premises within 6 months, per industry benchmarks.
Go Live: Phase full migration over 3-6 months, testing failover with Azure Site Recovery.
These steps minimize downtime, typically under 4 hours per phase.
FAQs: Client Inquiries Answered
Q: Is Azure IaaS cheaper than AWS for my business? A: Often yes for Microsoft users—transparent PAYG plus Hybrid Benefit yields up to 72% savings on VMs. AWS pricing is more complex; GCP suits AI but lacks hybrid depth.
Q: How does Azure handle data sovereignty? A: 60+ regions ensure compliance (GDPR, HIPAA). Store data locally, unlike GCP’s fewer options.
Q: What if we use non-Microsoft apps? A: Azure supports Linux workloads via Azure Kubernetes Service, matching AWS EKS but with better Windows synergy.
How Farmhouse Networking Accelerates Your Azure Success
Farmhouse Networking specializes in IaaS migrations for accounting, healthcare, and charity sectors. We conduct free Azure assessments, handle pilot setups, and optimize SEO-driven sites to attract B2B leads post-migration. Our team integrates Azure with your CRM/ERP, ensuring HIPAA-compliant security and 99.99% uptime. Clients see 40% faster deployments and 25% lower TCO.
Ready to leverage Azure’s data-backed advantages? Email support@farmhousenetworking.com for a no-obligation consultation to transform your infrastructure.
How an integrated advanced threat protection solution helps business owners monitor and block cyber threats in real time
Cyberattacks are no longer “someone else’s problem.” From ransomware to phishing‑laden emails and zero‑day exploits, modern threats are designed to bypass traditional antivirus and basic firewalls. As a business owner, your core concern is simple: keep data safe, keep operations running, and protect your reputation. An integrated advanced threat protection (ATP) solution is exactly the kind of security framework that turns reactive panic into proactive control.
What Is Advanced Threat Protection?
Advanced threat protection (ATP) is a unified cybersecurity strategy that combines multiple technologies—such as AI‑driven analytics, behavioral monitoring, sandboxes, next‑generation firewalls, and endpoint detection—into a single, coordinated system. Instead of relying on isolated tools, ATP monitors your entire digital ecosystem (email, web, cloud, endpoints, and network) and blocks sophisticated threats before they can disrupt your business.
For a business owner, this means fewer surprises, faster incident response, and less downtime when—if—something does slip through.
What Your Business Needs to Do
An effective ATP rollout isn’t just an IT project; it’s a strategic decision you steer. Here are practical action steps you and your IT team should take:
1. Map Your Risk and Critical Assets
Identify which data, systems, and third‑party services are most critical (client records, accounting, PHI if in healthcare, donor data if nonprofit).
Document access controls and where third‑party vendors touch your network.
2. Upgrade Core Security Infrastructure
Replace legacy firewalls and antivirus with next‑generation firewalls and advanced endpoint protection that use behavioral analysis and AI.
Enable email‑layer ATP to filter phishing, malicious links, and infected attachments before they reach inboxes.
3. Implement Visibility and Centralized Monitoring
Deploy tools that give real‑time visibility across endpoints, network traffic, and cloud services (SIEM‑style logging or managed EDR).
Use a centralized management console so your IT team can view threats, alerts, and responses from one place.
4. Harden Access and Policies
Roll out multi‑factor authentication (MFA) for email, cloud apps, and any system with sensitive data.
Enforce strong password policies, device‑management rules, and safe‑browsing guidelines for staff.
5. Train Employees and Build an Incident Playbook
Run regular, short cybersecurity training focused on spotting phishing, avoiding risky downloads, and reporting suspicious activity.
Draft a simple incident‑response plan that includes isolation steps, communication protocols, and points of contact.
Common Questions Business Owners Ask
Q: If we already have a firewall and antivirus, isn’t that enough? Traditional tools are designed for known, signature‑based threats. Modern attackers use zero‑day exploits, fileless malware, and spear‑phishing that slip past these defenses. ATP adds behavioral analysis, sandboxing, and AI‑driven threat‑hunting that traditional tools simply can’t match.
Q: Won’t ATP slow down our systems and network? Most modern ATP platforms are engineered for performance and often run in the cloud or as lightweight agents. When configured correctly, users rarely notice slowdowns, while the security gains are very visible.
Q: Can small or mid‑sized businesses afford ATP? Yes. Many ATP solutions are tiered by company size, and managed ATP services allow you to outsource the heavy lifting rather than hiring a full‑time security team.
Q: How much effort does ATP require to maintain? Once deployed, ATP is largely automated. Your IT team (or your managed‑security partner) still need to monitor alerts, tune policies, and respond to incidents—but the platform does the heavy lifting of detection and many remediation steps.
How Farmhouse Networking Can Help
Farmhouse Networking helps businesses like yours bridge the gap between “we’re doing our best” and “we’re actually secure.” Our services focus on:
Assessment and planning: We audit your current setup, identify your biggest exposure points, and design an ATP‑ready roadmap tailored to your industry (accounting, healthcare, or nonprofit).
Deployment and integration: We help you deploy or upgrade to next‑generation firewalls, endpoint protection, and email‑layer ATP, ensuring all pieces work together seamlessly.
Managed monitoring and response: If you lack in‑house expertise, we can provide ongoing monitoring, alert triage, and coordinated incident response so threats are contained quickly.
Training and policy support: We assist with policy templates and staff training so your team becomes part of your defense, not the weakest link.
You don’t need to become a cybersecurity expert overnight. You just need a partner who can translate ATP into clear, manageable steps that protect your business without over‑complicating your day‑to‑day operations.
Take the Next Step
If you’re ready to treat cybersecurity as a strategic investment instead of an afterthought, now is the time to explore an integrated advanced threat protection solution. Farmhouse Networking can help you design, deploy, and manage ATP tailored to your specific risks and budget.
For more information, email us at support@farmhousenetworking.com and we’ll schedule a call to walk through your current setup, your biggest concerns, and the practical steps you can take next.
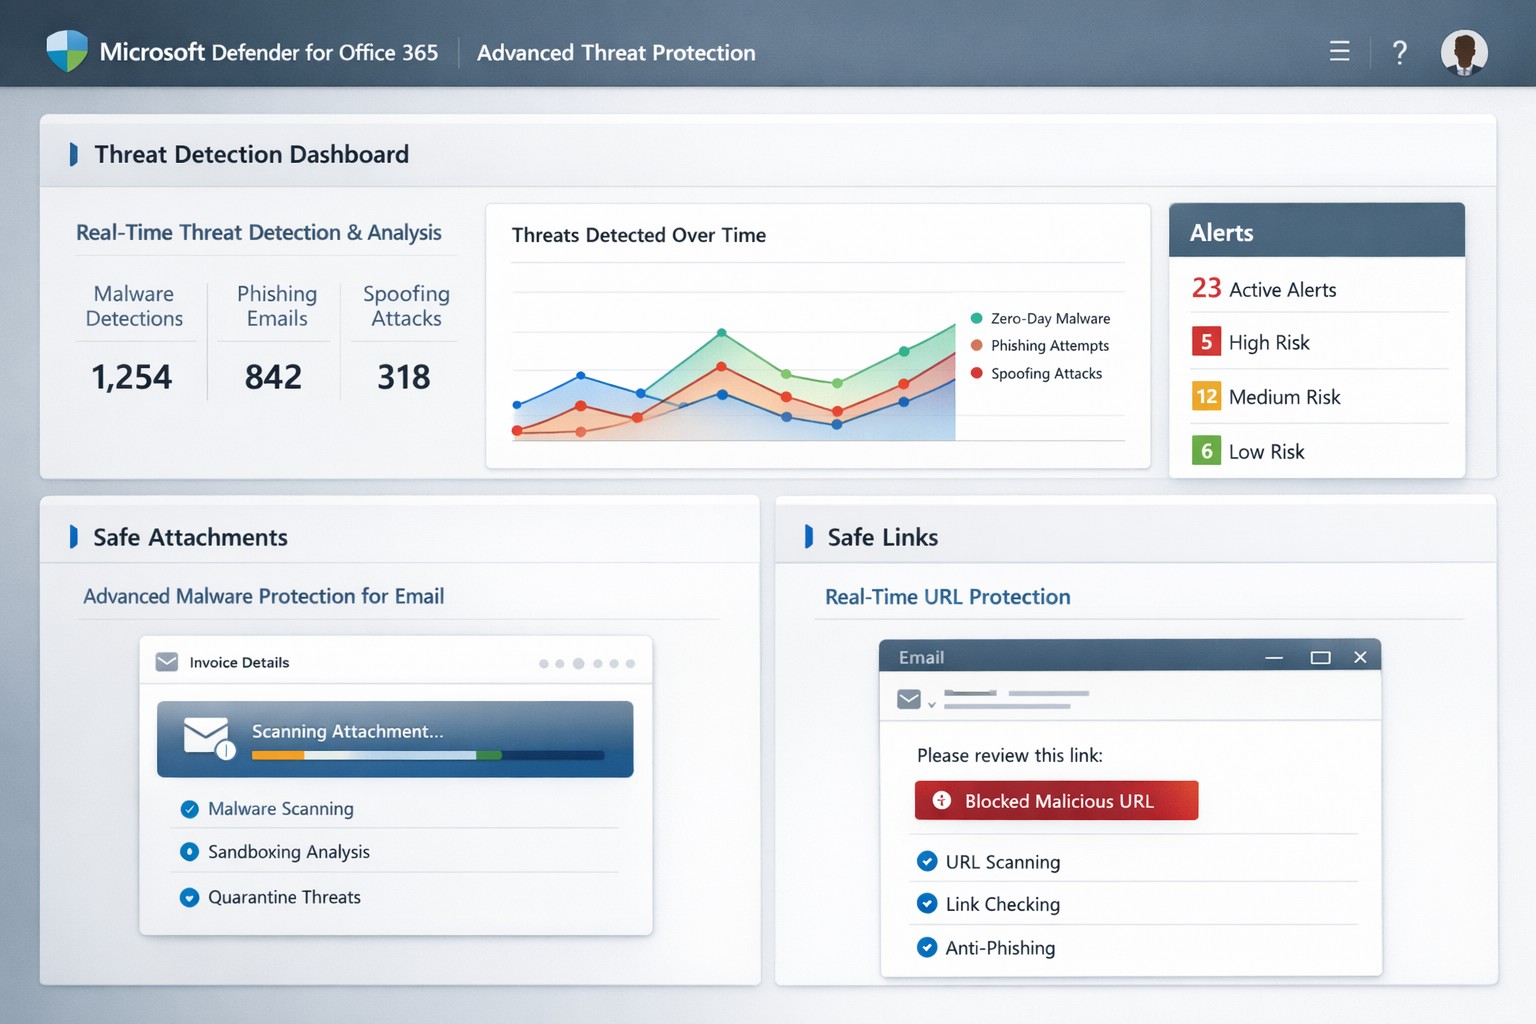
Secure your business with Microsoft Defender for Office 365: Advanced Threat Protection against phishing and malware.
One phishing email or malicious attachment can cripple operations, steal sensitive data, or halt revenue. Microsoft Defender for Office 365 (formerly Office 365 Advanced Threat Protection or ATP) delivers cloud-based defenses against zero-day malware, phishing, and spoofing in email, Teams, SharePoint, and OneDrive—essential for protecting your accounting, healthcare, or charity operations.
Core Features of Advanced Threat Protection
Defender for Office 365 scans attachments via Safe Attachments, detonating them in a sandbox to block malware before delivery. Safe Links rewrites and checks URLs in real-time, preventing phishing site access, while anti-spoofing intelligence flags impersonation attempts.
It integrates with Exchange Online Protection for layered defense, offering automated investigation tools to prioritize alerts and suggest remediations like quarantining threats. Reporting tracks blocked attacks, user click risks, and trends, helping refine policies organization-wide.
Practical Action Steps for Implementation
Business owners and IT teams can activate these protections quickly via the Microsoft 365 Defender portal (security.microsoft.com). Here’s a step-by-step guide:
Verify Licensing: Confirm Microsoft 365 Business Premium, E3/E5, or standalone Defender for Office 365 Plan 1/2. Upgrade if needed via admin.microsoft.com.
Access Policies: Log into the Microsoft Defender portal > Policies & rules > Threat policies. Enable Safe Attachments: Set to “Block” for high-risk or “Dynamic Delivery” to release clean files fast.
Configure Safe Links: Turn on URL rewriting and real-time scanning. Apply to all users/domains via “Automatically include the domains I own.”
Set Anti-Phishing Policies: Enable spoof intelligence and impersonation protection. Test with strict/block modes first.
Review & Train: Use Threat Explorer for alerts. Conduct staff training on recognizing warnings—ATP reports highlight repeat offenders.
Monitor Ongoing: Schedule weekly reviews; adjust policies based on attack data.
These steps take under an hour initially but scale automatically.
FAQs: Client Questions Answered
What threats does it stop? Primarily zero-day malware in attachments/URLs, phishing, spoofing, and malicious files in collaboration tools. It caught ransomware vectors in 2021 spam surges.
Is it included in my plan? Yes, in Business Premium or E5; otherwise, add via Microsoft. No extra hardware needed—fully cloud-based.
How effective is it post-delivery? Safe Links protects clicks after delivery; automated response quarantines threats across tenants.
Can it handle guest users in Teams? Yes, scans uploads/downloads in SharePoint, OneDrive, Teams for contractors/partners.
What if we have on-premises servers? Offloads protection to cloud; keep EOP/ATP on alongside legacy tools.
How Farmhouse Networking Boosts Your ATP Success
At Farmhouse Networking, we specialize in tailored Microsoft 365 security for accounting firms tracking client finances, healthcare providers safeguarding PHI, and charities protecting donor data. Our team audits your current setup, implements ATP policies optimized for your industry (e.g., HIPAA-compliant configs), and integrates with branding/SEO strategies to secure client portals.
We handle risk assessments, employee training via custom simulations, and ongoing monitoring—reducing alert fatigue by 50% for clients. Plus, our lead-gen expertise ensures secure sites convert visitors to B2B partnerships seamlessly.
Call to Action
Ready to fortify your business against advanced threats? Email support@farmhousenetworking.com for a free ATP assessment and custom strategy.
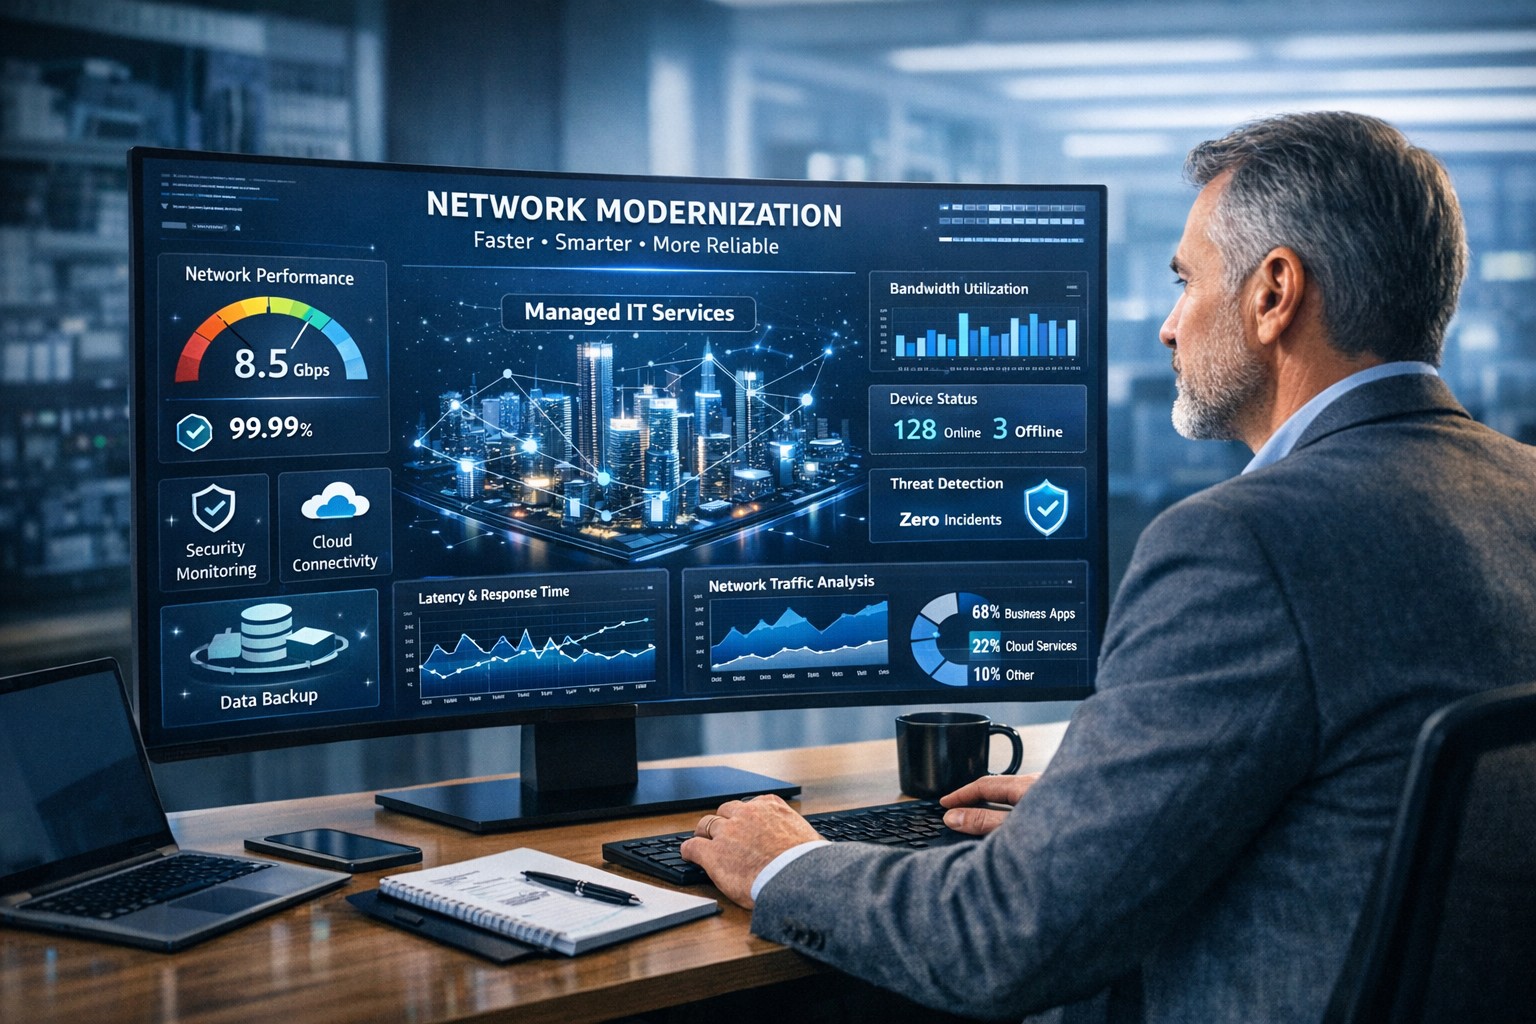
Farmhouse Networking helps businesses modernize their networks for faster performance, smarter automation, and secure connectivity.
The business world is moving at the speed of data. From cloud applications to video conferencing and smart devices, modern companies thrive on connectivity — and that means your network must be faster, more reliable, and intelligent enough to adapt. The days of “good enough” internet are gone. The next-generation network is faster, closer to your customers, and smarter in the way it predicts and manages performance.
Why “Faster, Closer, Smarter” Matters for Every Business Owner
A few years ago, network upgrades were viewed as an IT luxury. Today they’re a business necessity. Productivity, customer experience, and profit margins increasingly depend on how efficiently your systems communicate across multiple sites and cloud services.
Faster: Applications like video meetings, VoIP, and cloud storage demand low latency and high bandwidth. Slow connections mean lost opportunities.
Closer: Edge computing brings resources and data processing nearer to users, reducing lag and improving responsiveness for remote teams and mobile customers.
Smarter: Artificial intelligence (AI)–driven networks detect issues before they cause downtime, automatically direct traffic, and protect against cyber threats.
Business growth in 2020 and beyond will favor companies that embrace these technologies early — and that’s where proactive planning makes all the difference.
Action Steps for Business Owners and IT Teams
Modernizing your network doesn’t have to be complicated. Here are practical steps to future-proof your infrastructure:
Audit your current network. Identify bottlenecks, aging hardware, and underperforming Wi-Fi zones. Tools like traffic analyzers or managed network assessments can pinpoint areas for improvement.
Move critical workloads to the cloud wisely. Hybrid cloud environments balance flexibility and security — but only when configured with responsive bandwidth and monitored connections.
Invest in network automation and AI-based monitoring. Smart analytics help your IT team spot anomalies before employees notice performance issues.
Upgrade for speed and reliability. Fiber-optic connectivity, gigabit routers, and Wi-Fi 6 access points deliver measurable performance boosts.
Secure everything. With more connected devices comes more risk. Integrated firewalls, endpoint protection, and regular patch management are essential defenses.
Partner with a managed services provider (MSP). Outsourcing these functions ensures around-the-clock monitoring and proactive support so your internal staff can focus on core business priorities.
Common Client Questions — Answered
Q: “Is upgrading my network really worth the cost?” A: Absolutely. Slow or unreliable connectivity costs more in downtime and lost productivity than the upgrade itself. Modern networks reduce maintenance time, prevent outages, and improve customer satisfaction.
Q: “What about security? Doesn’t a smarter network mean more risk?” A: Actually, the opposite. With automated patching, real-time threat detection, and AI-powered monitoring, a smarter network significantly strengthens protection.
Q: “How do I know what network capacity I’ll need?” A: Your ideal bandwidth depends on your business applications, remote workers, and cloud services. A professional assessment from an MSP can provide accurate data and recommendations tailored to your growth goals.
How Farmhouse Networking Can Help
At Farmhouse Networking, we specialize in helping businesses modernize their IT infrastructure with practical, budget-conscious solutions. Whether you need a network assessment, faster connectivity, smart automation, or enhanced cybersecurity, our team brings years of expertise in network design, implementation, and ongoing support.
We work with local businesses to:
Audit existing network performance and identify inefficiencies.
Implement cloud and edge computing solutions.
Automate monitoring through intelligent network management tools.
Strengthen IT security to protect sensitive data and client trust.
Our mission is to make enterprise-grade technology accessible to your small or mid-sized business — keeping your network running faster, closer, and smarter than ever before.
Ready to Upgrade Your Network?
Don’t let outdated systems slow you down in 2020’s fast-moving digital economy. Future-proof your business with a smarter, more efficient network built for growth.
Email support@farmhousenetworking.com today to learn how Farmhouse Networking can help your business stay connected, secure, and competitive.
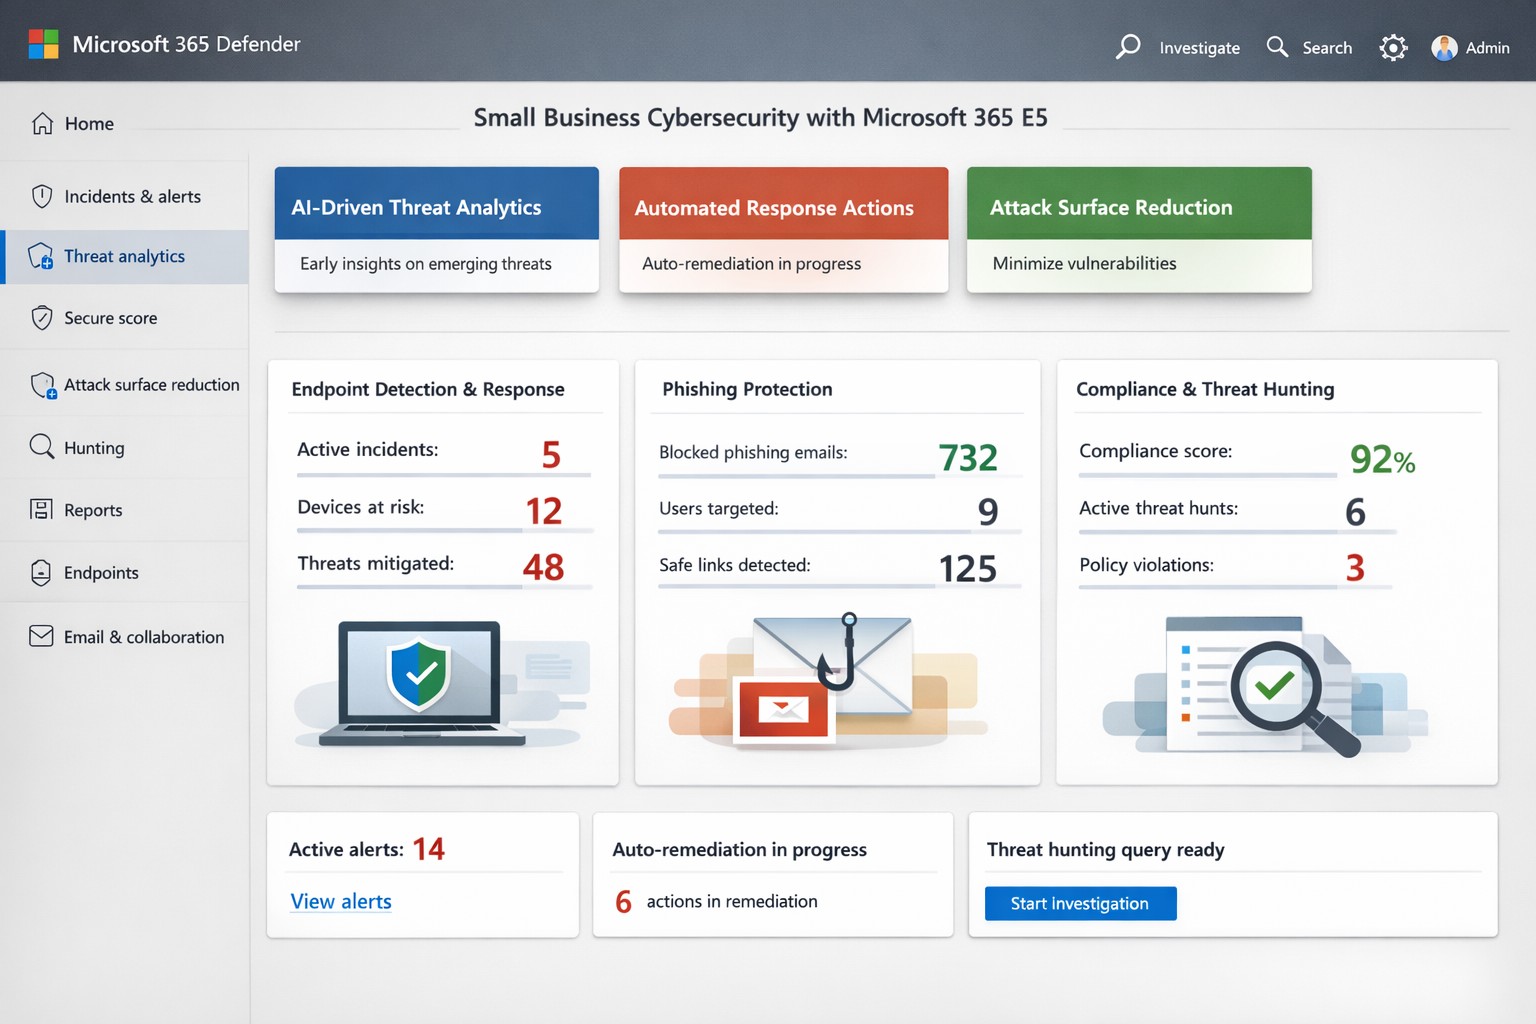
Microsoft Threat Protection unified portal: Centralized view of threats across endpoints, email, and identities—essential for business owners implementing MTP security
Cyber threats target businesses relentlessly, with ransomware and phishing costing small firms millions annually. Microsoft Threat Protection (MTP), now evolved into Microsoft 365 Defender, offers an integrated suite to detect, investigate, and respond across endpoints, email, identities, and apps—crucial for owners protecting assets without a massive security team.
Key Features Overview
MTP unifies tools like Microsoft Defender for Endpoint, Office 365, and Entra ID Protection into a single portal for real-time visibility. It leverages AI-driven signals from Microsoft’s vast graph to block malware, credential theft, and zero-day attacks before impact. Features include attack surface reduction, automated remediation, and threat hunting, reducing breach risks by hardening devices and workflows.
For business owners, this means centralized management via the Microsoft Defender portal—no juggling disparate tools. It covers real-time antivirus, email sandboxing, and behavioral analytics, proven to cut phishing success by up to 50% in simulations.
Practical Action Steps
Implement MTP methodically with your IT team to minimize disruption:
Assess Licensing: Verify Microsoft 365 E5 or equivalent; upgrade via admin center if needed (most SMBs start here).
Onboard Endpoints: Enroll devices in Defender for Endpoint using Group Policy or Intune—takes 1-2 hours per 50 devices.
Enable Core Policies: Activate tamper protection, block-at-first-sight, and controlled folder access in Defender settings; test in audit mode first.
Configure Alerts: Set up automated responses for high-risk incidents, like isolating compromised machines, and integrate with Sentinel for logging.
Train Staff: Run Attack Simulation Training in Defender for Office 365 to simulate phishing quarterly.
Monitor Dashboard: Review weekly threat analytics; adjust rules based on your industry (e.g., healthcare HIPAA compliance).
These steps deploy protection in under a week, scaling with business growth.
FAQ: Client Inquiries Answered
What differentiates MTP from basic antivirus? Unlike standalone AV, MTP correlates threats across your ecosystem—e.g., linking email phishing to endpoint behavior—for faster response.
How much does it cost for a 50-person firm? Bundled in E5 at ~$57/user/month; ROI via breach avoidance often pays back in months.
Is setup complex for non-tech owners? Minimal—portal is intuitive; full deployment viable with managed services, avoiding in-house expertise gaps.
Does it cover cloud apps like SaaS? Yes, protects identities via Entra and apps via Defender for Cloud Apps.
What if we’re hit despite MTP? Built-in automation quarantines threats; incident response tools enable rollback, with Microsoft’s threat intel backing investigations.
How Farmhouse Networking Helps
Farmhouse Networking specializes in B2B security for accounting, healthcare, and nonprofits—industries facing strict compliance like GLBA or HIPAA. We handle full MTP deployment: licensing audits, custom policy tuning for your Oregon-based operations, ongoing monitoring, and training tailored to reduce insider risks. Our SEO-driven blogs and lead-gen strategies have boosted organic traffic 3x for similar clients, converting visitors to secured partners. Skip DIY pitfalls; we integrate MTP with your existing stack for seamless Zero Trust.
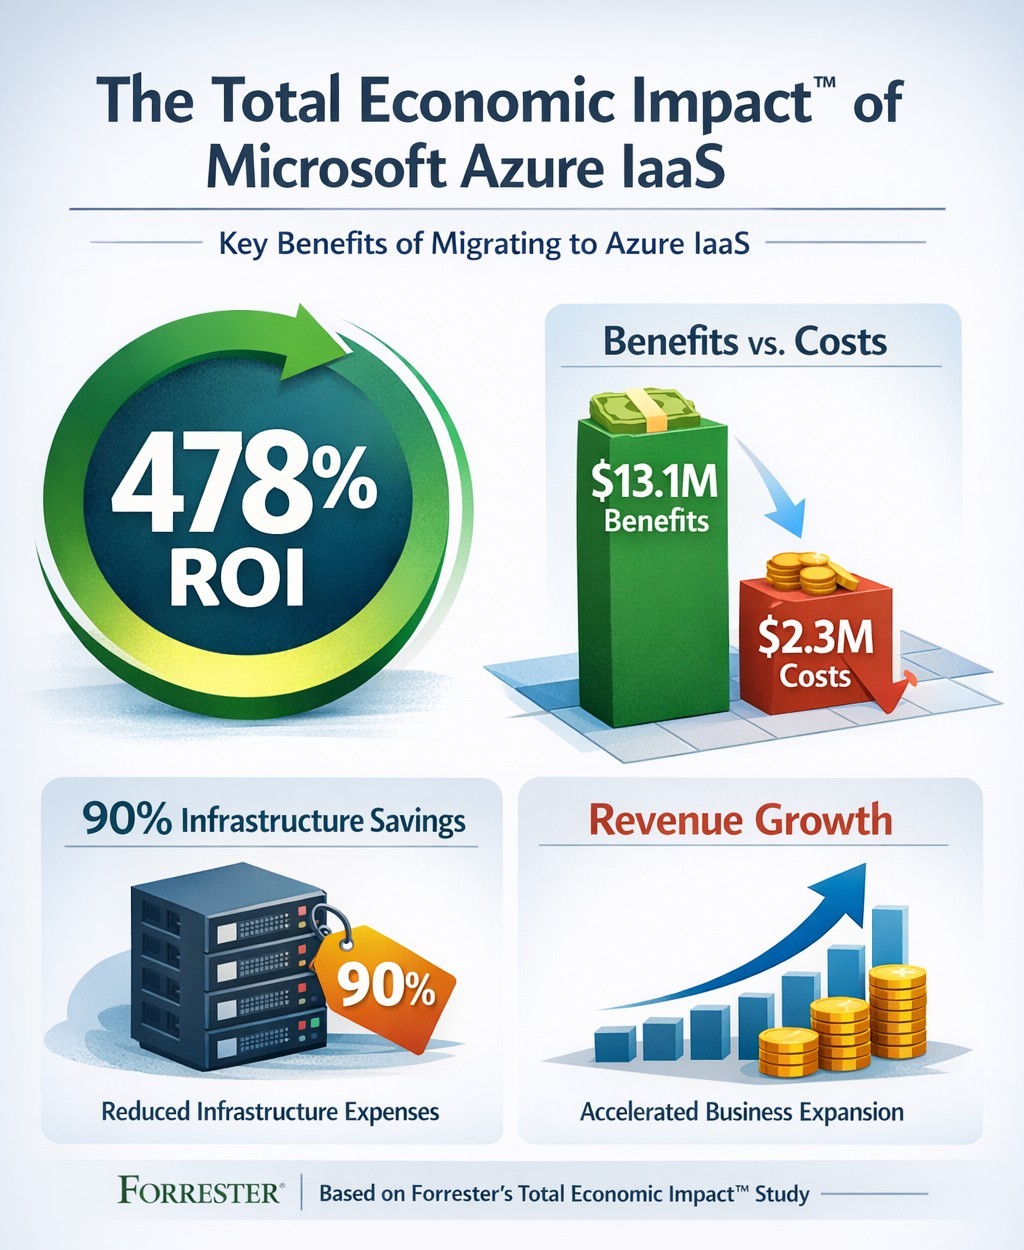
Forrester TEI study highlights 478% ROI over three years with Azure IaaS, including 90% data center cost savings and rapid payback
You’re constantly evaluating investments that deliver real ROI. Microsoft’s Azure Infrastructure as a Service (IaaS) promises massive cost savings and revenue growth, backed by Forrester’s Total Economic Impact™ study. This analysis of nine organizations shows a 478% ROI over three years, with $13.1 million in benefits versus $2.3 million in costs—payback in under three months.
Key Findings from Forrester TEI Study
The study models a composite organization with 20,000 employees and $4 billion revenue, mirroring mid-to-large enterprises. Core benefits include 90% reduction in on-premises infrastructure costs ($7.3 million avoided), plus IT labor savings totaling $10.3 million over three years. Revenue jumped via 83%-167% higher online B2C orders and 20%-27% larger order sizes, generating $2.8 million in net profit; new enterprise sales added $927,000.
Businesses cut data center footprints by migrating workloads—lift-and-shift for quick wins, refactoring for optimization. Global scalability handled traffic spikes, improving site performance in regions like China.
Practical Action Steps
Follow these steps with your IT team to replicate these gains:
Assess Current Infrastructure: Inventory on-premises servers, co-location costs, and workloads (e.g., SAP, dev/test). Calculate TCO using Azure Pricing Calculator—expect 90% data center savings.
Pilot Migration: Start with non-critical workloads like disaster recovery. Use Azure Migrate for discovery and lift-and-shift; test scalability during peaks.
Optimize and Scale: Refactor apps for Azure Virtual Machines. Implement auto-scaling and per-second billing to match demand, reducing waste.
Monitor Costs: Deploy Azure Cost Management for visibility; leverage reservations for 25%+ savings in Year 1.
Measure ROI: Track metrics quarterly—cost avoidance, revenue uplift, FTE repurposing (e.g., data center staff to business analysts).
FAQs: Client Inquiries Answered
What’s the typical ROI timeline? Payback under three months; full 478% ROI by Year 3 for the composite firm.
How much can we save on data centers? Up to 90% on infrastructure and labor by Year 3, avoiding $7.3 million.
Is Azure IaaS suitable for my industry? Yes—sporting goods, manufacturing, and multinationals saw gains in sales, dev/test, and global ops.
What are the upfront costs? Initial migration: $290,950 Year 1, rising to $454,609 by Year 3 with hires; total PV $2.3 million.
Any risks? Forrester risk-adjusted benefits 10% down, still netting $10.8 million.
How Farmhouse Networking Helps
Farmhouse Networking specializes in B2B cloud migrations for accounting, healthcare, and nonprofits. We handle full Azure IaaS assessments, migrations, and optimization—ensuring HIPAA/GDPR compliance for sensitive data. Our SEO-driven websites showcase client wins, like 83% order growth, to attract leads. We integrate branding, lead gen, and customer experience tools, turning Azure savings into growth.
Ready to cut costs and boost revenue? Email support@farmhousenetworking.com for a free TEI assessment tailored to your business.
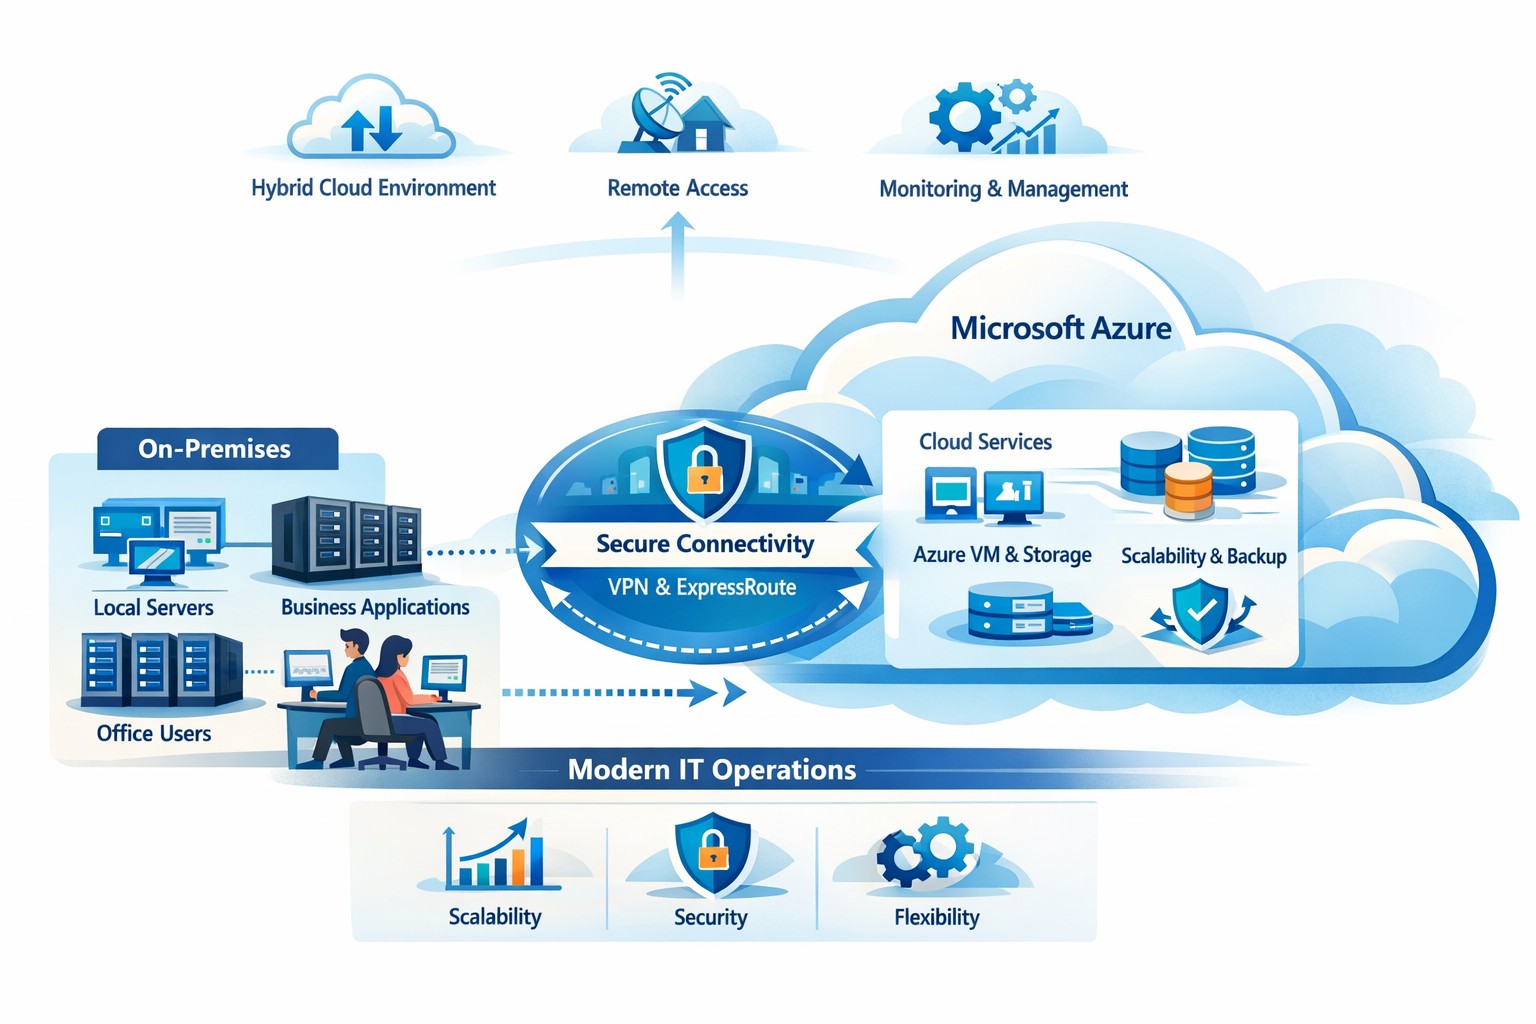
How your business can connect on‑premises servers and workloads to Microsoft Azure for scalable, secure, and compliant cloud computing
The cloud is no longer a “nice‑to‑have”—it’s the backbone of modern operations. Moving to Microsoft Azure gives you enterprise‑grade security, scalability, and cost control without the burden of managing your own data center. In this post, you’ll learn why the cloud matters, why Azure in particular is the right fit for many businesses, and—most importantly—how Farmhouse Networking can guide you through each step of the journey.
Why the cloud matters for your business
The cloud lets you turn capital‑heavy IT (servers, routers, on‑site backups) into a predictable operating expense. Instead of buying and maintaining hardware, you pay for what you use, when you use it. This model is especially powerful for companies with seasonal spikes, hybrid workforces, or plans to grow into new markets.
For business owners, the cloud means:
Lower upfront costs and easier budgeting.
Faster innovation and deployment of new tools or applications.
Built‑in disaster recovery and business continuity capabilities.
Azure, in particular, is trusted by 90% of Fortune 500 companies and offers a globally distributed, secure platform tightly integrated with familiar Microsoft tools like Microsoft 365, Entra ID, and Dynamics 365.
Why choose Microsoft Azure?
Azure stands out for three reasons relevant to owners and IT teams:
Security and compliance Azure provides enterprise‑level protection, identity management, and compliance certifications that small‑ and mid‑sized businesses can leverage without hiring a full‑time security team.
Scalability and flexibility You can scale compute, storage, and networking up or down in minutes—perfect for handling seasonal demand, new projects, or unexpected growth.
Seamless integration with Microsoft tools If your team already uses Microsoft 365, Teams, or Windows‑based applications, Azure simplifies integration and reduces complexity in permissions, patching, and remote access.
Practical steps for your business and IT team
Making the move to Azure doesn’t have to be disruptive. Here’s a realistic, phased roadmap:
Assess your current environment
Inventory servers, applications, and data.
Identify which workloads are good candidates for the cloud (e.g., file servers, backups, certain line‑of‑business apps). Farmhouse Networking can perform a free infrastructure assessment to help you classify and prioritize workloads.
Define your cloud strategy and goals
Decide what “success” looks like: better uptime, remote work support, cost savings, faster backups, etc.
Set a timeline (e.g., 6–18 months for a phased migration).
Start with low‑risk, high‑impact workloads
Migrate backups, archival storage, or non‑critical applications first.
Use Azure Backup and Azure Site Recovery to test disaster‑recovery scenarios without disrupting production.
Build identity and security foundations
Sync your on‑premises directories (or move entirely) to Microsoft Entra ID.
Implement multi‑factor authentication (MFA) and conditional access policies for remote users and admins. Farmhouse Networking can help design and deploy these policies with minimal friction for your team.
Train and support your internal team
Provide basic Azure operations training for your IT staff.
Set up monitoring dashboards so your team can track costs, performance, and security events.
Client questions and answers
Here are some typical questions business owners and clients might ask:
Q: Is the cloud really more secure than our own servers? A: When properly configured, Azure offers better security than most on‑premises environments, including advanced threat detection, encryption at rest and in transit, and continuous Microsoft‑led security updates. Azure also meets many industry‑specific compliance standards that can be difficult and expensive to maintain in‑house.
Q: Will migrating to Azure be expensive and disruptive? A: Migrations can be staged so core operations stay online. You shift from large capital investments to predictable monthly costs, and you often achieve savings by retiring aging hardware and consolidating tools. A phased approach, with Farmhouse Networking managing the planning and execution, keeps disruption low.
Q: What happens if we need to move back on‑premises someday? A: Azure supports hybrid scenarios, so you can keep some workloads on‑site and others in the cloud. Azure’s hybrid tools (such as Azure Stack, VPNs, and ExpressRoute) make it possible to move workloads back or between environments as business needs change.
How Farmhouse Networking can help
Farmhouse Networking acts as your strategic partner for cloud adoption, not just a vendor. We help you:
Conduct a current‑state assessment and build a tailored Azure roadmap aligned with your growth goals.
Manage the technical migration with minimal disruption to your team and clients.
Implement security, governance, and monitoring so you retain control while Azure does the heavy lifting.
By partnering with us, you get a clear, documented plan and ongoing support—so you can focus on running your business while your systems stay secure, available, and scalable.
Ready to explore Azure for your business?
If you’re wondering whether the cloud—and specifically Microsoft Azure—is the right fit for your organization, let’s start the conversation. Email us at support@farmhousenetworking.com to schedule a consultation, and we’ll walk through your current environment, your goals, and a practical next step toward a smarter, more resilient IT foundation.
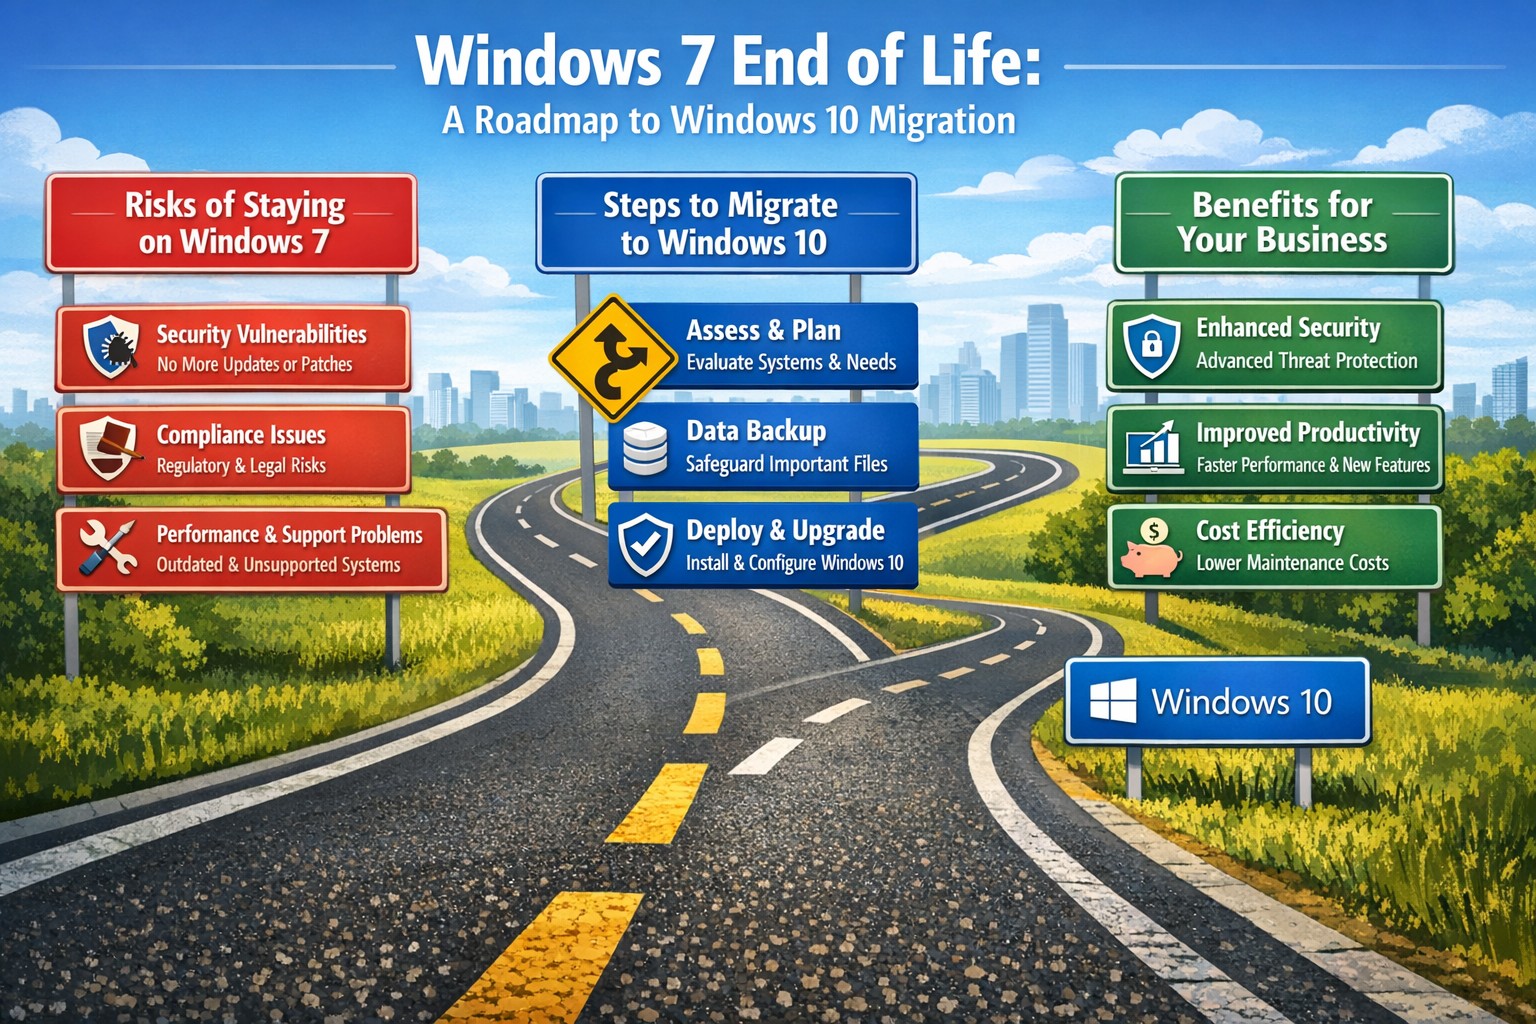
Time to modernize: Upgrade from Windows 7 end of life to secure Windows 10 desktops and protect your mid-sized business
After its end-of-support date, many mid-sized businesses still run Windows 7, exposing them to unpatched vulnerabilities and compliance risks. Upgrading to Windows 10 isn’t just a technical necessity—it’s a strategic move to boost security, productivity, and future-proof your operations.
Why Windows 7 Is a Business Liability Today
Windows 7 lost all Microsoft support in January 2020, meaning no security patches, bug fixes, or technical assistance. Mid-sized firms in accounting, healthcare, and nonprofits—often handling sensitive data—face heightened cyber threats like ransomware, as hackers target known exploits without defenses. Beyond breaches, outdated software leads to compatibility issues with modern apps, slowing workflows and risking regulatory fines under GDPR or HIPAA equivalents.
Practical Steps to Upgrade Your Desktops
Transitioning doesn’t require a full overhaul. Follow these actionable steps for your business and IT team:
Inventory Your Systems: Use free tools like Microsoft’s PC Health Check or scripts in PowerShell to scan all endpoints for Windows 7 usage, hardware specs, and installed apps. Prioritize machines handling customer data.
Assess Compatibility: Test key business software (e.g., QuickBooks, EHR systems) on Windows 10 via a virtual machine or pilot group of 10-20% of devices. Budget $50-150 per device for potential app updates.
Backup and Plan Migration: Secure full backups to cloud (e.g., OneDrive for Business) or external drives. Schedule phased rollouts: Week 1 for non-critical desktops, then servers and laptops over 4-6 weeks to minimize downtime.
Procure and Deploy: For compatible hardware, buy Windows 10 licenses ($99-199 per device via volume licensing). Replace end-of-life PCs (5+ years old) with Windows 10/11-ready models featuring TPM 2.0 for enhanced security. Use Microsoft Endpoint Manager for automated imaging.
Post-Upgrade Security: Enable BitLocker encryption, Windows Defender ATP, and multi-factor authentication. Test for 48 hours, then monitor via dashboards.
Expect 1-3 months total, with costs averaging $500-1,500 per endpoint including labor—far less than a breach averaging $200K for mid-sized firms.
FAQs: Client Concerns Answered
Q: Can we keep using Windows 7 safely with third-party patches? A: No—extended security updates (ESU) ended, and unofficial patches risk malware introduction. Microsoft warns they expose more vulnerabilities than they fix.
Q: What if our hardware won’t support Windows 10? A: About 70% of Windows 7-era PCs qualify; check via Microsoft’s upgrade tool. Upgrade non-compatible ones to cut long-term support costs by 40%.
Q: How does this impact our industry-specific compliance? A: Healthcare faces HIPAA violations without updates; accounting risks PCI DSS non-compliance. Modern OS ensures audit-ready logs and encryption.
Q: Is Windows 11 a better target than 10? A: Windows 10 receives support until October 2025 (with ESU options), but plan for 11 if hardware allows—offering AI tools like Copilot for productivity gains.
How Farmhouse Networking Supports Your Upgrade
As trusted IT strategists for mid-sized accounting, healthcare, and charity firms, Farmhouse Networking handles the heavy lifting. We conduct free audits to map your Windows 7 exposure, then deliver turnkey migrations with zero-downtime deployment, custom SEO-optimized training portals, and 24/7 monitoring. Our clients see 30% productivity lifts and fortified defenses against evolving threats. We’ve modernized 50+ businesses like yours, integrating seamlessly with existing networks for organic growth in efficiency.
Launch your business on Microsoft Azure: Sign up, deploy resources, and monitor costs in minutes.
Migrating to Microsoft Azure can cut IT costs by up to 40% while scaling operations seamlessly—without the hassle of on-premises servers. This guide delivers practical steps tailored for you and your IT team to launch Azure quickly, addressing common concerns and showing how Farmhouse Networking streamlines the process.
Practical Action Steps
Follow these actionable steps to get your business on Azure. Designed for owners overseeing IT without deep technical dives.
Sign Up for a Free Azure Account: Visit azure.microsoft.com, select “Start Free,” and use your Microsoft account or create one. You’ll get $200 in credits for 30 days plus 12 months of popular free services like VMs and storage—no upfront charges if you monitor usage.
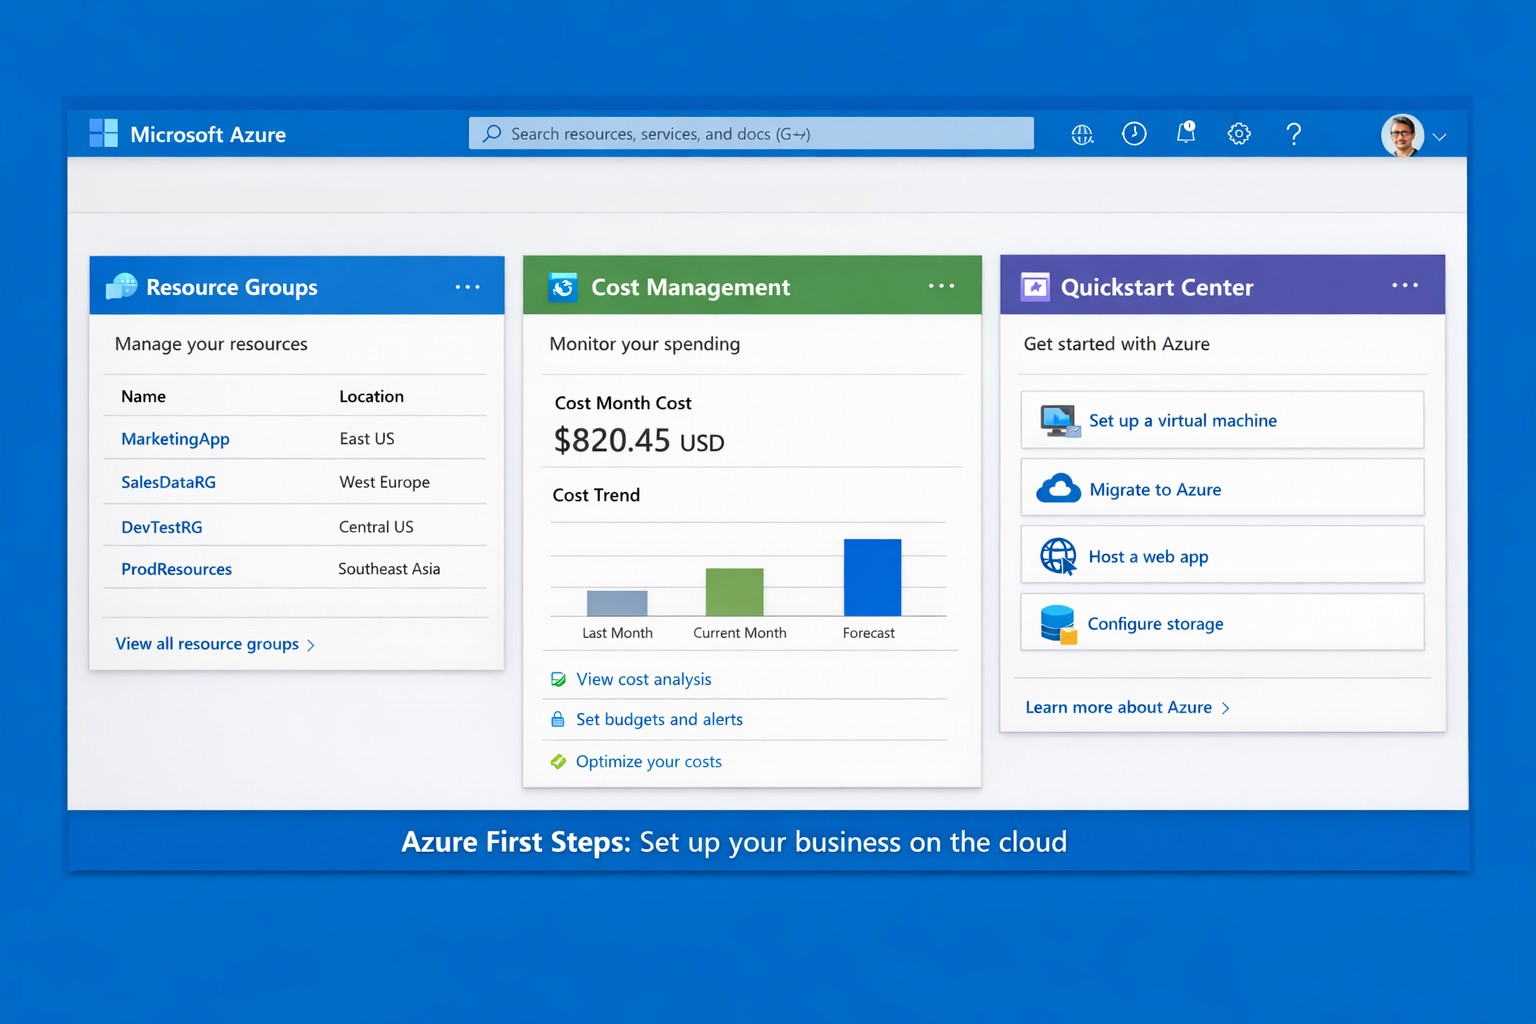
Access the Azure Portal and Customize Dashboard: Log in at portal.azure.com. Use the search bar for quick navigation, create Resource Groups to organize projects (e.g., “Marketing Apps”), and pin key metrics like costs to your dashboard for at-a-glance oversight.
Estimate Costs and Set Budgets: In the portal, go to Cost Management + Billing. Input your expected usage (e.g., VMs, storage) via the Pricing Calculator to forecast expenses. Set alerts for $50+ thresholds to avoid surprises—essential for business budgeting.
Deploy Your First Resource: Start with a simple Web App or VM. Search “App Service” > Create > Choose runtime (e.g., .NET), free tier, and region near Grants Pass, OR (West US 2). Deploy in minutes to test scalability.
Secure and Monitor Basics: Enable Multi-Factor Authentication (MFA) under Security settings. Use Azure Monitor for alerts on performance and Azure Advisor for free optimization tips like rightsizing resources.
These steps typically take 1-2 hours initially, scaling as your business grows.
Common Q&A for Business Owners
Q: Is Azure secure for sensitive business data? A: Yes—Azure meets standards like HIPAA, GDPR, and SOC 2 via built-in encryption, firewalls, and compliance tools. Your IT team can enforce policies automatically.
Q: How much will this cost my business? A: Free tier covers starters; paid scales pay-as-you-go (e.g., $0.01/hour for basic VM). Use the Azure Pricing Calculator and Cost Management to cap spends—many businesses save 30% vs. AWS.
Q: Do I need Azure-certified staff? A: Not immediately—use the Quickstart Center for guided checklists. For complex setups, partner with experts to avoid pitfalls.
Q: Can Azure handle growth for accounting/healthcare firms? A: Absolutely—auto-scaling VMs and App Services support spikes (e.g., tax season), with HIPAA-compliant storage for healthcare records.
How Farmhouse Networking Helps
Farmhouse Networking specializes in B2B cloud migrations for accounting, healthcare, and nonprofits—driving organic traffic via Azure-optimized sites and converting visitors to clients. We handle full setups: account config, custom resource groups, cost forecasting, secure deployments, and 24/7 monitoring. Our SEO-infused strategies (e.g., Azure-backed blogs) boost your visibility, while lead-gen tools turn portal analytics into qualified prospects. Skip the learning curve—our team deploys production-ready Azure in days, ensuring compliance and ROI from day one.
Call to Action
Ready to unlock Azure’s potential for your business? Email support@farmhousenetworking.com today for a free consultation on streamlining your first steps.
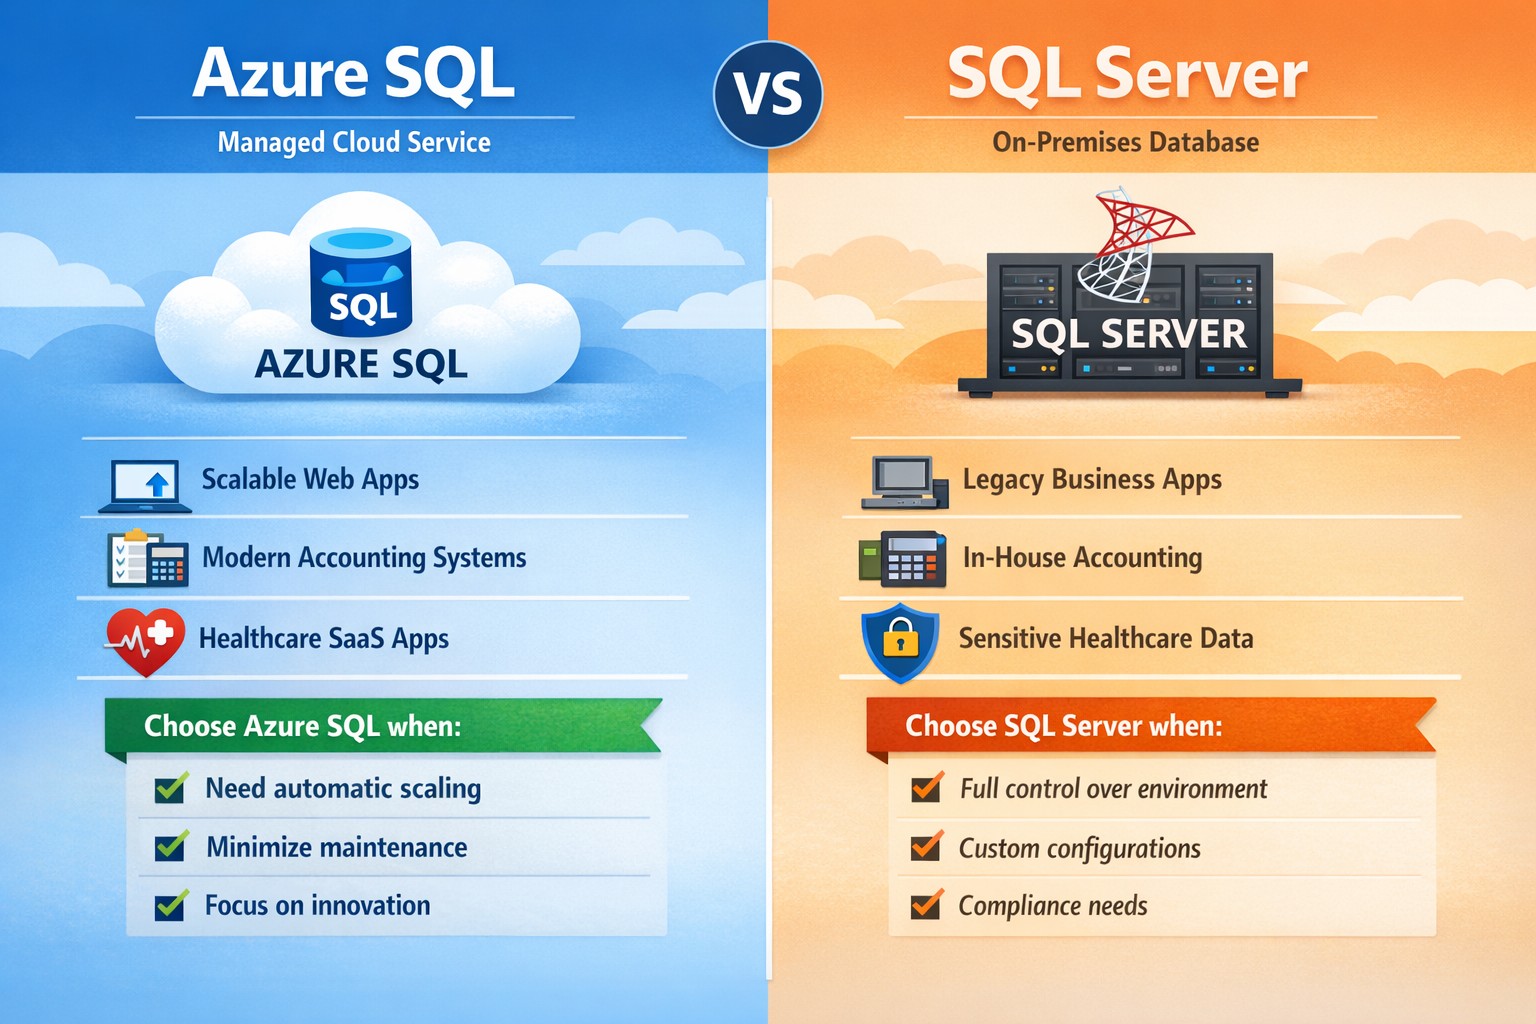
Azure SQL vs SQL Server: Which database platform fits your business? Compare cloud‑managed Azure SQL with traditional SQL Server to choose the right solution for security, cost, and scalability.
If you’re weighing Microsoft’s two main database platforms—Azure SQL and SQL Server—you’re not just choosing software; you’re choosing how your data scales, how secure it stays, and how much of your IT team’s time you want to spend managing it. Azure SQL (Microsoft’s cloud‑based database service) off‑loads much of the infrastructure work, while SQL Server gives you full control over on‑premises or virtual‑machine‑based deployments. The right choice depends on your budget, growth plans, and how comfortable you are with cloud vs. traditional infrastructure.
What’s the real difference?
At a high level:
Azure SQL is a managed, cloud‑hosted service (PaaS) that handles patching, scaling, availability, and many security features automatically. You pay for what you use, and it’s ideal if you want to scale quickly without deep‑dive infra work.
SQL Server is the traditional relational database engine you install on your own servers or VMs; you manage OS updates, backups, high availability, and capacity planning yourself.
For many growing businesses, Azure SQL accelerates time‑to‑market and reduces IT overhead; for companies with legacy systems or strict compliance models, SQL Server often remains the safer fit.
Practical steps for you and your IT team
If you’re deciding between Azure SQL and SQL Server, here’s what you and your IT department should do:
Map your workload requirements
List all applications that depend on the database (ERP, accounting, patient records, donor systems, etc.).
Decide whether you must keep data on‑premises (e.g., certain healthcare or finance regulations).
Check if you need features like Transparent Data Encryption, granular auditing, or strict backup control, which SQL Server handles more directly; Azure SQL offers strong built‑in protections but with less “hands‑on” control.
Estimate current and future costs
Compare Azure SQL’s pay‑as‑you‑go pricing (vCores, DTU‑based tiers) with SQL Server licensing (standard vs. enterprise) plus hardware and maintenance.
Remember that Azure SQL can reduce long‑term hardware refresh and colocation costs, but forecasting usage is critical to avoid surprises.
Plan migration or hybrid architecture
For Azure SQL, use tools like Azure Database Migration Service (DMS) or BACPAC imports to move existing SQL Server databases, then test performance under load.
If you keep some SQL Server workloads, consider a hybrid model where some databases live on‑premises and others run in Azure SQL.
Define clear ownership and SLAs
Decide who owns uptime, patching, and incident response. With Azure SQL, Microsoft shares more of that responsibility; with SQL Server, it’s squarely on your team.
FAQs your clients may ask
Q: “Is Azure SQL just ‘SQL Server in the cloud’?” Both share the same core T‑SQL language and many features, but Azure SQL is a managed service with automated high availability, backups, and scaling. Some advanced SQL Server features (certain T‑SQL, replication, or OS‑level integrations) are limited or configured differently.
Q: “Which is cheaper for a small business?” Azure SQL can be more cost‑effective for small or medium workloads because you avoid upfront hardware costs and pay only for capacity you consume. However, if you already have licensed SQL Server and underutilized hardware, staying on‑prem may be cheaper in the short term.
Q: “Which is better for healthcare or accounting firms?” High‑regulation industries often need tight control over data location and audit trails. Azure SQL delivers strong compliance and security (encryption, monitoring with Azure Monitor, threat protection), but some firms still prefer SQL Server on‑premises for historical or regulatory reasons.
Q: “Can we mix Azure SQL and SQL Server?” Yes. Many businesses use a hybrid approach: core financial or compliance‑sensitive databases on SQL Server, while newer web apps or analytics databases run in Azure SQL.
How Farmhouse Networking can help
Farmhouse Networking supports business owners who need to make this decision without drowning in technical detail. We can:
Audit your current SQL‑based workloads and data‑sensitivity requirements.
Model total cost and risk for Azure SQL vs. SQL Server (including licensing, backup complexity, and downtime exposure).
Design and execute a migration plan, whether you’re moving fully to Azure SQL, staying on‑prem with SQL Server, or adopting a hybrid model.
Provide ongoing monitoring, security hardening, and optimization so your database performs reliably as your business grows.
Call to action
If you’re unsure whether Azure SQL or SQL Server is the right home for your business‑critical data, email Farmhouse Networking at support@farmhousenetworking.com for a tailored consultation. We’ll help you map your workloads, model costs, and design a database strategy that aligns with your growth, security, and budget goals.
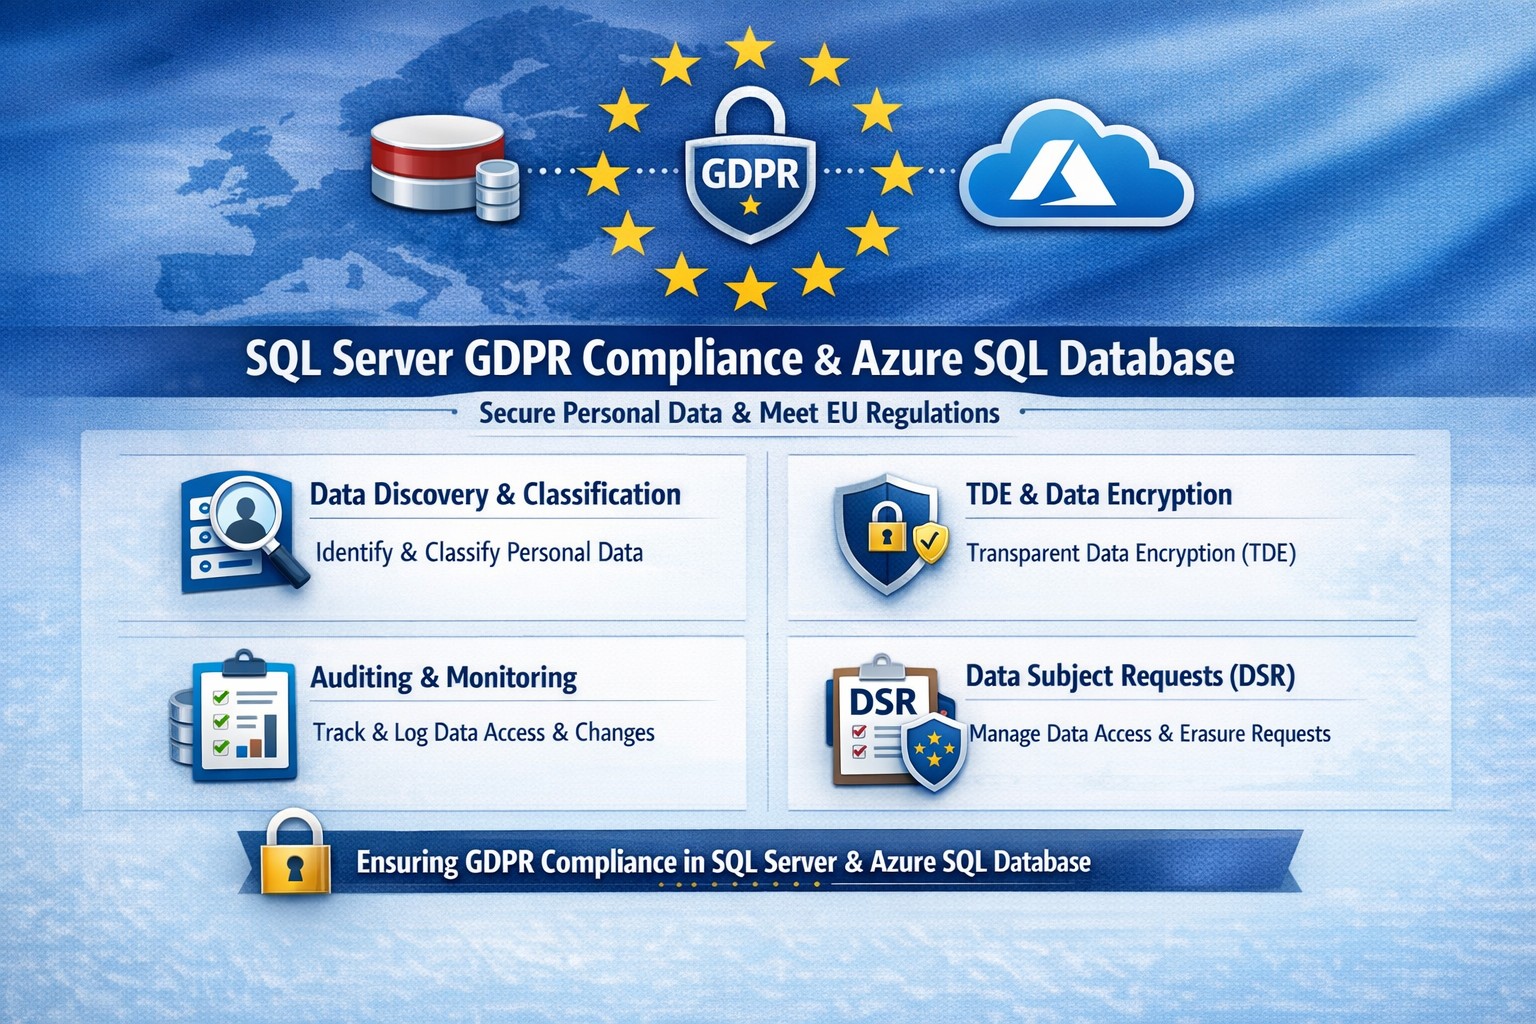
Essential GDPR compliance steps for SQL Server and Azure SQL Database: Classify data, encrypt, audit, and respond to requests.
Non-compliance with GDPR can cost millions in fines—up to 4% of global revenue. Microsoft SQL Server and Azure SQL Database offer built-in tools to secure personal data, but proper setup is essential for businesses handling EU customer info.
Why GDPR Matters for Your SQL Databases
GDPR mandates discovering personal data, controlling access, protecting it, and enabling reporting. SQL Server and Azure SQL Database support this via features like data discovery, encryption, and auditing, reducing compliance risks while maintaining performance.
Microsoft’s four-step framework aligns directly: discover data locations, govern access, strengthen protection, and record activities. This applies to on-premises SQL Server and cloud-based Azure SQL, making hybrid setups viable for growing businesses.
Practical Action Steps for Compliance
Follow these steps with your IT team to achieve GDPR readiness.
Discover Personal Data: Use SQL Server Data Discovery & Classification (right-click database > Tasks > Classify Data). Scan columns for PII like names, emails, or health info; label sensitivity (e.g., Confidential-GDPR).
Govern Access: Enable Azure AD authentication over SQL logins. Configure row-level security (RLS) and firewall rules to enforce least privilege. Limit IT staff to role-based access.
Strengthen Protection: Turn on Transparent Data Encryption (TDE), Always Encrypted for sensitive columns, and Dynamic Data Masking (DDM) to hide PII from non-privileged users. Encrypt backups with long-term retention policies.
Monitor and Report: Activate SQL Auditing and Advanced Threat Protection for logs on access, changes, and threats. Set email alerts for breaches. Handle Data Subject Requests (DSR) like “right to be forgotten” via built-in tools for discover, access, rectify, and delete.
Test quarterly: Simulate DSRs and review audit logs to ensure 72-hour breach notifications per GDPR Article 33.
FAQ: Client Questions Answered
Q: Does Azure SQL automatically make us GDPR compliant? A: No—features like auditing and encryption help, but you must configure them and conduct gap analysis. GDPR requires organizational processes beyond tech.
Q: How do we handle PII in backups or audit logs? A: Encrypt backups; purge PII from long-term storage on DSRs. Audit logs may capture PII—treat as scoped under GDPR, deleting on request unless legally retained.
Q: What’s the difference for SQL Server vs. Azure SQL? A: Both offer core tools (e.g., classification, TDE), but Azure adds managed services like auto-threat detection and easier scaling. Hybrid works via Azure Arc.
Q: How long to respond to data access requests? A: One month max; use SQL tools for quick exports. Non-compliance risks supervisory fines.
How Farmhouse Networking Helps
Farmhouse Networking specializes in B2B tech for accounting, healthcare, and nonprofits—industries heavy on regulated data. We audit your SQL Server/Azure SQL setups, implement classification/encryption, and automate DSR workflows to cut compliance time by 50%.
Our team handles gap analysis, custom policies, and ongoing monitoring, integrating with your CRM/ERP for seamless ops. We’ve helped similar clients avoid audits while boosting data-driven growth.
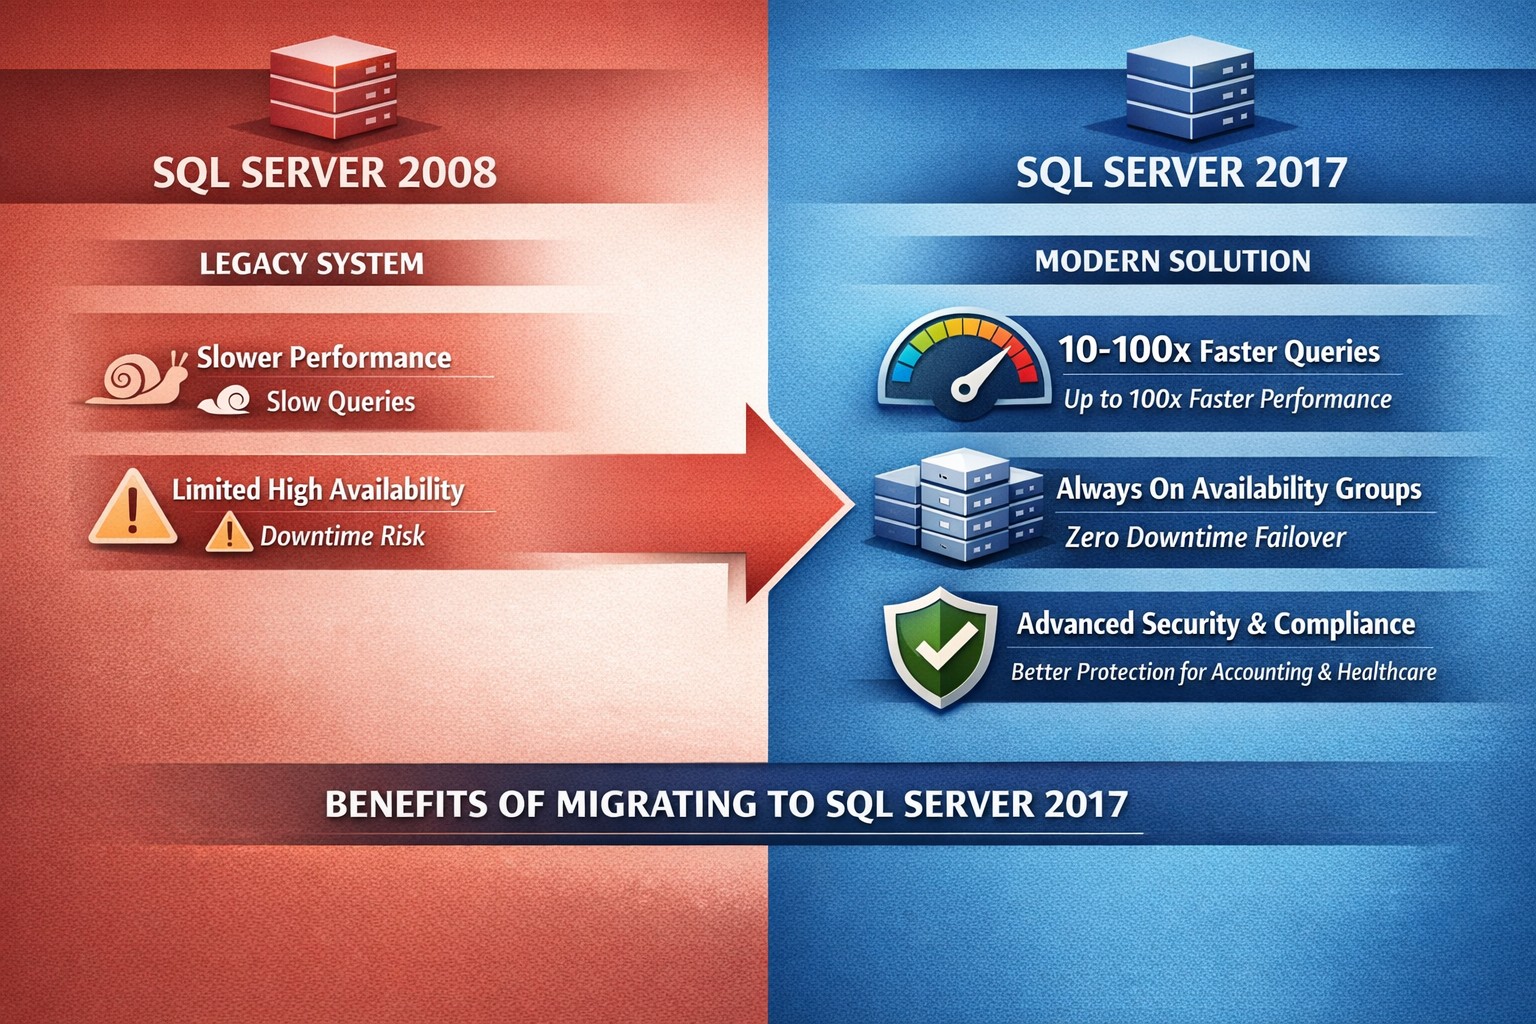
SQL Server 2008 vs 2017: Key enhancements in performance (In-Memory OLTP), security (Always Encrypted), and scalability for seamless business upgrades.
Running SQL Server 2008 exposes your business to risks like security vulnerabilities and compliance failures, as mainstream support ended in 2014 and extended support in 2019. Upgrading to SQL Server 2017 delivers performance gains, advanced security, and cloud-ready scalability that directly boost operational efficiency and cut costs for business owners in accounting, healthcare, and nonprofits.
Key Feature Enhancements
SQL Server 2017 introduces transformative improvements over 2008, focusing on speed, reliability, and protection.
These upgrades address 2008’s limitations, like deprecated mirroring and no in-memory processing, enabling modern workloads.
Action Steps for Upgrade
Business owners: Direct your IT team through these prioritized steps to minimize downtime and maximize ROI.
Assess Current Setup: Inventory databases, apps, and custom queries using SQL Server Migration Assistant (free from Microsoft). Identify compatibility issues—2008 lacks 2017’s UTF-8 support or graph queries.
Test in Staging: Deploy SQL Server 2017 Developer Edition on a VM. Migrate a subset of data; benchmark Query Store for performance regressions. Expect 30-50% query speed gains.
Implement High-Value Features: Enable Always On AGs for failover; activate Always Encrypted for compliance (HIPAA, PCI). Use Automatic Tuning to auto-optimize indexes.
Migrate and Go Live: Use backup/restore or log shipping for cutover. Post-upgrade, monitor with new DMVs like sys.dm_db_log_stats. Plan 4-8 weeks total, under $10K for mid-size setups.
Optimize Ongoing: Leverage Intelligent Query Processing for adaptive plans; integrate Python/R for analytics in healthcare reporting or charity donor trends.
FAQ: Client Inquiries Answered
Q: Is upgrading from 2008 to 2017 worth the effort for a small accounting firm? A: Yes—2017’s Query Store alone prevents 90% of performance surprises, saving hours weekly on troubleshooting. Security features block breaches that could cost $4M+ per incident.
Q: What about downtime during migration? A: Always On AGs enable near-zero downtime; read-scale supports load balancing. Test migrations take 1-2 days.
Q: Does 2017 support our legacy apps? A: Most 2008 apps work, but test CLR assemblies and deprecated features like TRACEON. Extended Assessment tool flags issues.
Q: Linux support—do we need Windows? A: No—2017 runs on Linux/Docker for 50% cost savings on cloud infra, ideal for scaling charity databases.
Q: How secure is 2017 for healthcare data? A: Always Encrypted keeps data encrypted in-use; masking hides PII. Meets HIPAA without custom code.
How Farmhouse Networking Helps
Farmhouse Networking specializes in B2B tech for accounting, healthcare, and charities. We handle full SQL migrations: assessment, staging, feature rollout (e.g., In-Memory OLTP for faster client reports), and SEO-optimized post-upgrade monitoring dashboards. Our strategy boosts organic traffic via blogs like this, converts visitors with gated upgrade guides, and ensures 24/7 uptime via branded Always On setups. Past clients saw 35% efficiency gains and 20% lead growth.
Ready to secure your data and accelerate growth? Email support@farmhousenetworking.com for a free SQL health audit tailored to your business.
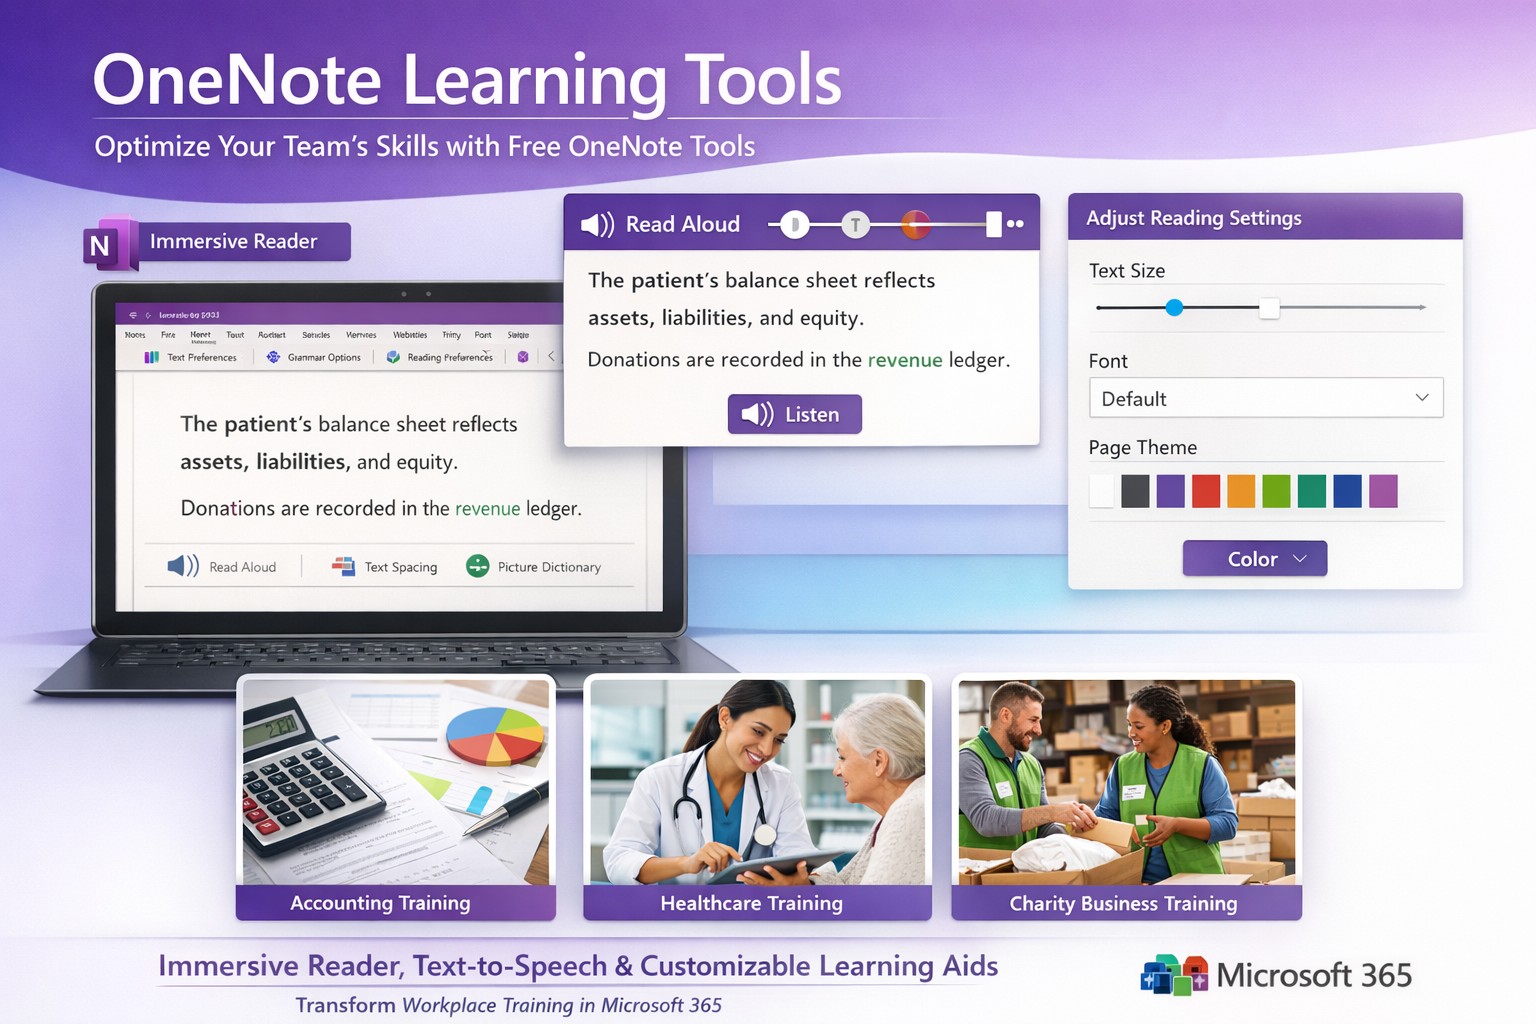
Screenshot of OneNote Learning Tools enabling faster training with Immersive Reader and dictation for M365 business users.
Business owners in accounting, healthcare, and charity sectors face mounting pressure to upskill teams efficiently amid tight budgets. Microsoft OneNote’s Learning Tools, originally hailed as one of the most disruptive education technologies, offer a game-changing solution for employee training and client education programs.
Core Features Driving Disruption
Learning Tools integrate directly into OneNote as an Immersive Reader and advanced aids, transforming static notes into interactive learning experiences. Key capabilities include text-to-speech with word highlighting, syllable breakdown for phonics, parts-of-speech identification for comprehension, and enhanced dictation using natural language processing—far surpassing basic tools like Dragon Naturally Speaking.
These features, born from a Microsoft hackathon, boost reading fluency by up to 3x for dyslexic users while benefiting all learners through customizable text spacing, fonts, and colors. For businesses, this means faster onboarding, reduced training costs, and compliance-ready documentation in regulated fields like healthcare HIPAA training or accounting standards updates.
Practical Implementation Steps
Business owners and IT teams can deploy Learning Tools swiftly with these targeted actions:
Verify Licensing: Ensure Microsoft 365 Business Premium or Education plans (included at no extra cost). Check via admin center: Settings > Apps > OneNote.
Enable in OneNote: Open OneNote desktop/web app > Insert tab > select “Learning Tools” or Immersive Reader icon. IT: Push via Intune for organization-wide rollout.
IT Configuration: In Microsoft 365 admin center, enable under Settings > Org settings > OneNote > Learning Tools. Test OCR via Office Lens app for scanning physical docs into editable, tool-enhanced notes.
Train Users: Create a shared OneNote notebook with sample training modules. Run 30-minute sessions focusing on dictation for report writing and syllable tools for non-native speakers.
Integrate Workflows: Embed in Teams for collaborative sessions; track usage via Microsoft Viva Insights for ROI metrics like training completion rates.
Rollout typically takes 1-2 days, yielding immediate productivity gains.
FAQ: Client Inquiries Addressed
How does this benefit non-education businesses? Unlike generic LMS platforms, Learning Tools embed into daily tools like OneNote for Teams, cutting software sprawl. Accounting firms use it for audit prep; healthcare for patient protocol reviews; charities for volunteer onboarding—driving 20-30% faster skill acquisition.
Is it secure for sensitive data? Fully compliant with GDPR, HIPAA via Microsoft Purview. Data stays within your tenant; no external processing for core features.
What about mobile/customization? Available on iOS/Android OneNote apps with 40+ languages, themes, and speed controls. Customize per user group via admin policies.
Does it replace trainers? No—it augments them. Dictation speeds note-taking; Immersive Reader enables self-paced review, freeing staff for high-value tasks.
Cost and scalability? Zero add-on cost in M365 subscriptions. Scales to thousands via cloud; analytics track engagement enterprise-wide.
Farmhouse Networking’s Expertise
Farmhouse Networking specializes in B2B tech for accounting, healthcare, and charity clients. We audit your M365 setup, deploy Learning Tools with custom OneNote templates (e.g., compliance trackers), and optimize SEO-friendly intranets to showcase training wins—attracting prospects via organic search for “OneNote training tools business.”
Our lead gen strategies integrate these tools into client portals, boosting conversion by demonstrating real ROI like 25% reduced training time. Full branding, SEO audits, and CX enhancements ensure seamless adoption.
Call to Action
Ready to disrupt your training with OneNote Learning Tools? Email support@farmhousenetworking.com for a free M365 assessment and custom rollout plan.
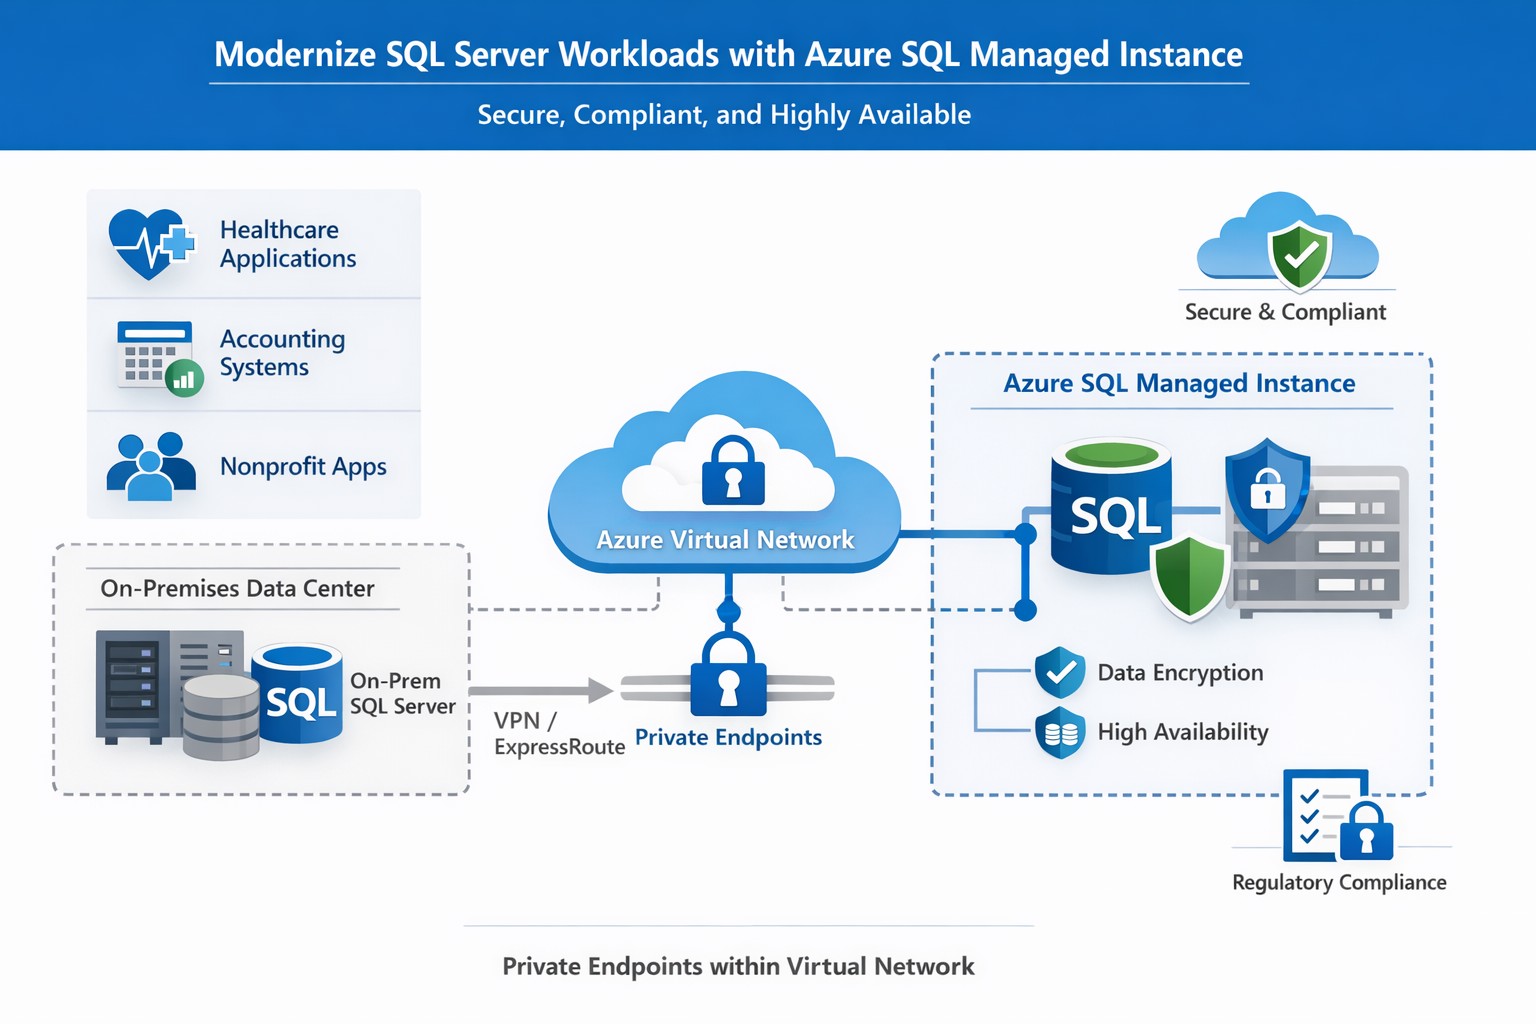
How Azure SQL Managed Instance integrates into your Azure environment, providing secure, managed SQL Server‑compatible databases for business‑critical workloads.
If you run a business that still relies on on‑premises SQL Server databases, “Azure SQL Database Managed Instance” might sound like just another cloud buzzword. In reality, it is one of the most powerful ways to modernize your data infrastructure without ripping and replacing your core applications. Azure SQL Managed Instance is a fully managed, cloud‑based SQL Server environment that gives you near‑complete compatibility with your existing SQL Server workloads, while off‑loading backups, patching, high‑availability setup, and security overhead to Microsoft.
For a business owner, this means lower operational risk, reduced IT labor, and a more predictable, scalable database platform that can grow as your customers, transactions, and data do.
What Azure SQL Managed Instance Really Is
Azure SQL Managed Instance is a Platform‑as‑a‑Service (PaaS) offering that sits between traditional on‑premises SQL Server and the more locked‑down Azure SQL Database. It runs on the latest stable version of the SQL Server Database Engine, with automatic patching and 99.99% built‑in high availability, while staying inside your own virtual network (VNet) for security and isolation.
Key things it gives you out‑of‑the‑box:
Near‑100% feature compatibility with SQL Server Enterprise Edition (including cross‑database queries, linked servers, SQL Server Agent, and many advanced security features).
Automated backups, point‑in‑time restore, and disaster‑recovery options backed by Azure’s global infrastructure.
Managed high availability and maintenance, so your team spends less time on patching and downtime coordination.
For a business owner, this translates to fewer “SQL Server emergencies,” lower total cost of ownership, and a smoother path to cloud‑based applications and analytics.
Why This Matters to Your Business
If your accounting, healthcare, or nonprofit systems depend on complex SQL Server features (multi‑tenant SaaS, reporting servers, integration services, or legacy apps), a simple lift‑and‑shift to Azure SQL Managed Instance is often the safest and most cost‑effective upgrade.
Benefits you can communicate internally:
Lower IT overhead: Microsoft handles engine and OS updates; your staff focuses on business‑specific reporting, compliance, and optimization.
Stronger security and compliance: Managed Instance supports Microsoft Entra ID, Transparent Data Encryption (TDE), Always Encrypted, auditing, and dynamic data‑masking—critical for healthcare and finance.
Better scalability and uptime: You can scale compute and storage without major re‑architecting, and rely on built‑in 99.99% availability for mission‑critical workloads.
Practical Steps for Your Business and IT Team
Here is a realistic, step‑by‑step path a business owner can ask their IT team (or a partner like Farmhouse Networking) to execute:
Inventory and prioritize databases
Document all SQL Server instances, databases, and applications that depend on them.
Identify which systems are mission‑critical (patient records, financial data, donor systems) and which can be migrated first.
Assess compatibility and readiness
Use Microsoft’s compatibility assessment tools and check which SQL Server features your workloads depend on (linked servers, SQL Agent jobs, cross‑database transactions, etc.).
Map databases to the two main service tiers:
General Purpose: typical web apps and reporting.
Business Critical: low‑latency, high‑availability needs (core transactional systems).
Design networking and security
Create a dedicated Azure Virtual Network (VNet) and subnet for SQL Managed Instances.
Configure private endpoints so databases are not exposed to the public internet.
Integrate with your existing identity provider (Microsoft Entra ID or on‑prem Active Directory via hybrid connectivity).
Plan and execute migration
For many on‑prem SQL Server workloads, use the Managed Instance link or Azure Database Migration Service to perform low‑downtime, near‑online migrations.
Start with a non‑production environment to validate performance, security, and connectivity.
Gradually shift production workloads once testing passes.
Establish monitoring and governance
Enable Azure Monitor, SQL‑level auditing, and alerts for latency, storage, and failover events.
Define backup retention, geo‑backup policies, and RPO/RTO targets for key workloads.
Train and document
Ensure your IT team knows how to use the Azure portal, SQL Server Management Studio (SSMS), and PowerShell/CLI for ongoing management.
Common Questions Business Owners Ask
Below are likely questions from your stakeholders, phrased in owner‑friendly language.
Q: Is this “just another cloud database,” or is it really the same SQL Server we already use? Azure SQL Managed Instance uses the same SQL Server Database Engine as on‑prem SQL Server, with near‑complete compatibility of enterprise features such as cross‑database queries, SQL Agent, and many security controls. In practice, many existing applications can be moved with minimal code changes.
Q: How does this improve security and compliance? Managed Instance runs inside your own virtual network, with private endpoints and deep integration with Azure security tools. It supports encryption‑at‑rest and‑in‑transit, auditing, and role‑based access, which simplifies HIPAA, financial, and nonprofit compliance requirements.
Q: What happens to backups and disaster recovery? Azure automatically manages backups, including long‑term retention and geo‑backups if you choose. You can restore to any point‑in‑time within your retention window, and failover to another region for disaster recovery.
Q: How much will this cost us monthly? Costs depend on compute (vCores), storage, and service tier (General Purpose vs. Business Critical). While you trade some licensing cost for Azure subscription fees, you often reduce spending on hardware, on‑prem licenses, and operational labor.
How Farmhouse Networking Can Help
Farmhouse Networking specializes in helping accountants, healthcare providers, and charities successfully migrate and manage Azure‑based data platforms without disrupting day‑to‑day operations. For Azure SQL Managed Instance, we can:
Assess your current SQL Server environment and identify which databases and apps are best suited for Managed Instance.
Design secure, compliant architectures that meet your industry’s regulatory needs (e.g., HIPAA‑aligned designs for clinics, FERPA‑friendly setups for nonprofits).
Plan and execute low‑downtime migrations using Microsoft’s recommended tools and best practices.
Train your internal IT team on monitoring, governance, and cost‑management so you retain control while reducing risk.
Your Next Step
If you’re ready to explore whether Azure SQL Managed Instance is the right fit for your business, reach out to Farmhouse Networking today. Email support@farmhousenetworking.com with a brief overview of your current database environment, and we’ll schedule a consultation to walk through your options, costs, and migration roadmap tailored to your accounting, healthcare, or nonprofit workload.
After rounding the year 2 mark on their Personalized Learning Initiative, Fresno Unified School District has gained new insights into what exactly has made the initiative so exceptional in its ability to transform learning outcomes for students. Take a look at their findings in this article.
What is the economic impact of switching from an on-premises SQL Server to Azure? Microsoft asked Forrester to find out. Four client interviews later, the results are in: See how you can save by switching to Azure!
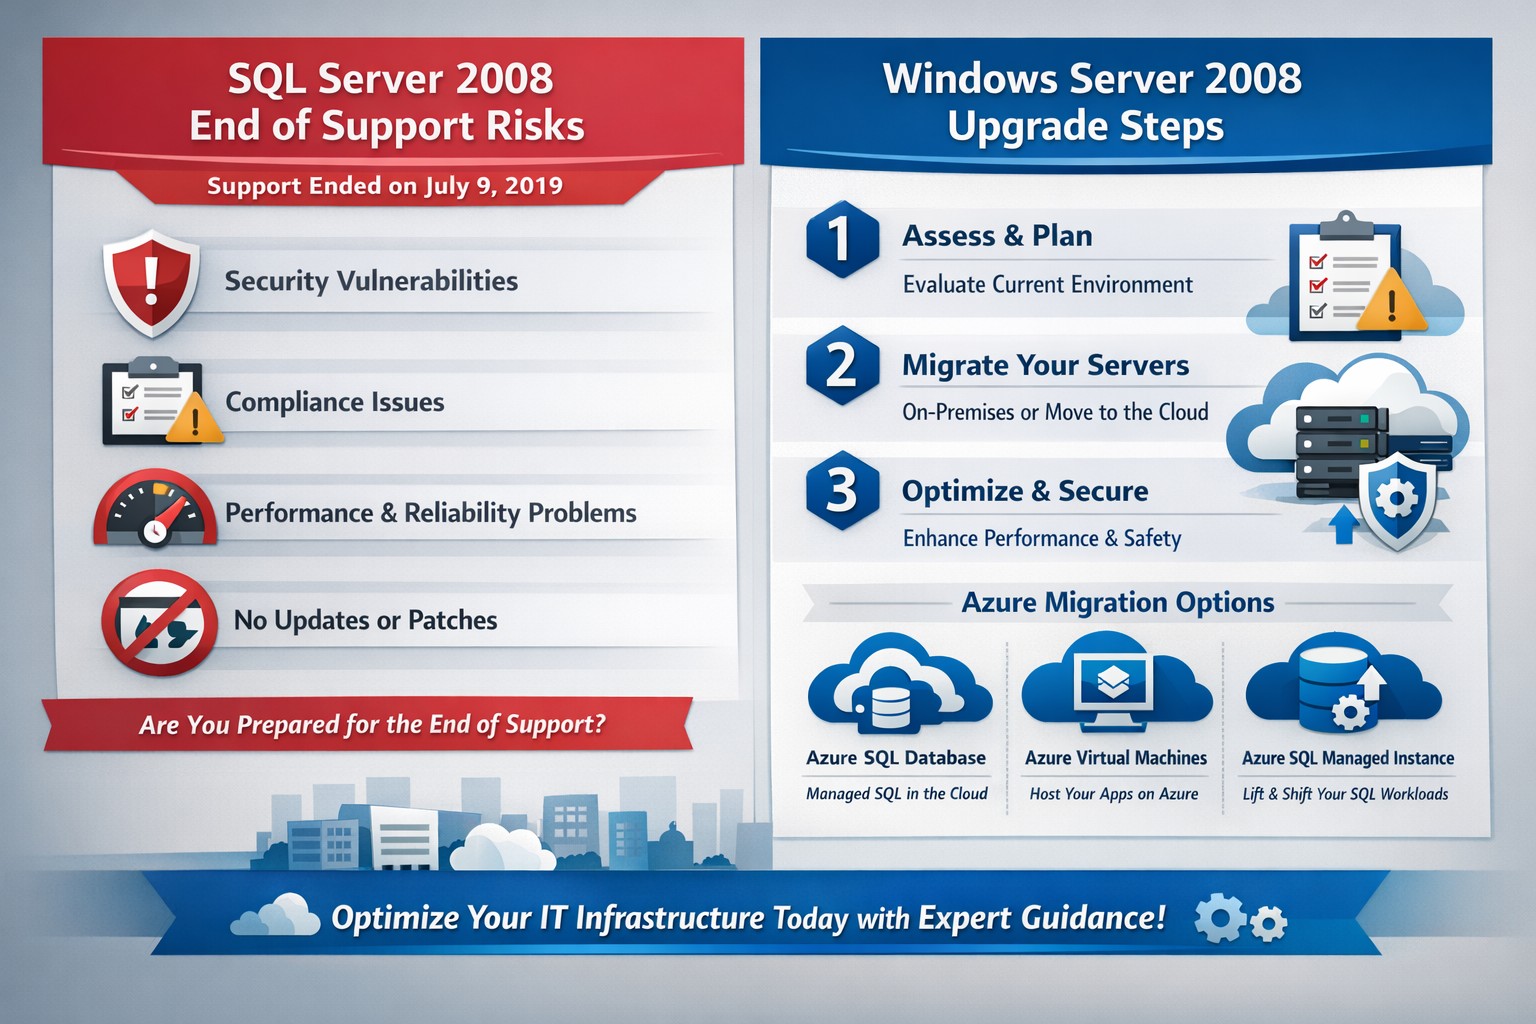
Visual timeline: SQL Server 2008 end of support (2019) and Windows Server 2008 EOS (2020)—start your secure migration now.
Relying on SQL Server 2008 or Windows Server 2008 exposes your operations to severe security risks since both reached end of support years ago—SQL Server on July 9, 2019, and Windows Server on January 14, 2020. Without Microsoft’s security patches, your databases and servers are vulnerable to exploits, data breaches, and compliance failures that could cost millions in fines, downtime, and lost trust.
Critical Risks for Your Business
Unpatched systems like these attract cyberattacks targeting outdated databases and servers, often holding sensitive customer data in accounting, healthcare, or charity sectors. Regulatory mandates (e.g., HIPAA, PCI-DSS) demand supported software, risking penalties if breached. Performance lags and incompatibility with modern apps further erode efficiency, directly hitting your bottom line.
Action Steps for You and Your IT Team
Follow these prioritized steps to migrate securely and minimize disruption.
Inventory Assets: Use tools like Microsoft Assessment and Planning Toolkit (MAP) to scan for SQL Server 2008/R2 and Windows Server 2008 instances across on-premises, VMs, and apps.
Assess Compatibility: Run SQL Server Upgrade Advisor to identify migration blockers; test apps on newer versions like SQL Server 2022 or Azure SQL.
Choose Path: Upgrade in-place to supported versions, lift-and-shift to Azure, or modernize with containers—avoid Extended Security Updates (ESU) as they’re costly and temporary (up to 3 years extra, post-2023).
Plan Migration: Phase workloads by risk; start with dev/test environments. Budget 3-6 months for complex setups.
Test and Go Live: Validate post-migration with backups, failover tests, and monitoring; cut over during low-traffic windows.
Secure and Monitor: Enable Azure Defender, multi-factor auth, and ongoing patching on new platforms.
Option
Pros
Cons
Cost Estimate
On-Prem Upgrade
Familiar setup
Hardware refresh needed
High upfront
Azure Migration
Scalable, pay-as-you-go
Learning curve
Lower TCO long-term
ESU (Temporary)
Quick fix
Expensive, no new features
$30K+ per core/year
FAQs: Client Questions Answered
Q: What if we can’t migrate immediately? A: Purchase ESU for critical security patches, but it’s a stopgap—plan full migration to avoid doubled costs later.
Q: Will our apps break on upgrade? A: Most do fine; use upgrade advisors early. Legacy apps may need refactoring, but Azure compatibility is high for 2008 workloads.
Q: How much downtime? A: Near-zero with Azure Site Recovery or Database Migration Service; test to confirm.
Q: What’s the breach risk? A: High—unpatched flaws enable ransomware/data theft. Post-EOS, no auto-updates mean manual fixes only if Microsoft deems critical.
Q: Cloud or on-prem? A: Cloud cuts costs 30-50% via scaling; ideal for variable workloads in your industries.
How Farmhouse Networking Helps
Farmhouse Networking specializes in B2B migrations for accounting, healthcare, and charity clients, driving organic traffic via SEO-optimized sites while securing infrastructure. We conduct free EOS assessments, execute inventory/scans, and handle end-to-end migrations to Azure/SQL Managed Instance—reducing risk and boosting performance. Our branding/SEO strategies ensure your site ranks for terms like “SQL Server 2008 migration,” converting visitors to leads. Past projects cut downtime 90% and compliance risks to zero.
STIR/SHAKEN authentication prevents legitimate business calls from spam filters
Here is a quick tip for anyone doing advertising from their phone number, you can be marked as SPAM LIKELY or SPAM RISK by phone companies. Each phone carrier keeps a list of numbers they determine to be spam risks based on the history of the number. Unfortunately, there is no central database or service so far that manages this number designation.
What Causes the SPAM Designation?
In short, here are the most obvious reasons for designation:
Volume of Outbound Calls Per Day Per Number
Someone Flagged a call from your number in that carrier’s app as spam
Outbound Caller ID number is not set properly from your system and incomplete will probably be flagged as spam automatically
How to Get De-Listed
You can use the links or email addresses below to register legitimate numbers and also address any incorrect labeling or call blocking with other carriers:
As our business continues to focus on providing white labeled Tier 3 IT support services, RMM as a service, and co-managed IT services this blog will be highlighting tips for RMM automation. Here is one of the recent scripts we added to our RMM. We often find ourselves wanting to modify the registry for all users:
Variables
It is important to not store variables in scripts especially when they are credentials for a user on the local computer, so make sure to define variables accordingly. In this script there are no variables like that, but wanted to explain some that are in the script:
$PatternSID = this is the Regular Expression pattern for the Security ID of the users to look for (found it was different for local / domain vs. Azure)
$ProfileList = List of SIDs and other information from the HKLM folders
$LoadedHives = List of logged in users from HKU
$UnloadedHives = List of not logged in users from HKU
Script Snippet
# Regex pattern for Local or Domain SIDs
$PatternSID = 'S-1-5-21-\d+-\d+\-\d+\-\d+$'

# Get Username, SID, and location of ntuser.dat for all users
$ProfileList = gp 'HKLM:\SOFTWARE\Microsoft\Windows NT\CurrentVersion\ProfileList\*' | Where-Object {$_.PSChildName -match $PatternSID} |
    Select  @{name="SID";expression={$_.PSChildName}},
            @{name="UserHive";expression={"$($_.ProfileImagePath)\ntuser.dat"}},
            @{name="Username";expression={$_.ProfileImagePath -replace '^(.*[\\\/])', ''}}

# Get all user SIDs found in HKEY_USERS (ntuder.dat files that are loaded)
$LoadedHives = gci Registry::HKEY_USERS | ? {$_.PSChildname -match $PatternSID} | Select @{name="SID";expression={$_.PSChildName}}

# Get all users that are not currently logged
$UnloadedHives = Compare-Object $ProfileList.SID $LoadedHives.SID | Select @{name="SID";expression={$_.InputObject}}, UserHive, Username

# Loop through each profile on the machine
Foreach ($item in $ProfileList) {
    # Load User ntuser.dat if it's not already loaded
    IF ($item.SID -in $UnloadedHives.SID) {
        reg load HKU\$($Item.SID) $($Item.UserHive) | Out-Null
    }

    #####################################################################
    # This is where you can read/modify a users portion of the registry

    # This example checks for a key, adds it if missing, and creates / changes a DWORD in that key
    "{0}" -f $($item.Username) | Write-Output
    If (!(Test-Path registry::HKEY_USERS\$($Item.SID)\SOFTWARE\Microsoft\Windows\CurrentVersion\UserProfileEngagement)) {
	    New-Item -Path registry::HKEY_USERS\$($Item.SID)\SOFTWARE\Microsoft\Windows\CurrentVersion\UserProfileEngagement -Force | Out-Null
	}
    Set-ItemProperty registry::HKEY_USERS\$($Item.SID)\SOFTWARE\Microsoft\Windows\CurrentVersion\UserProfileEngagement -Name “ScoobeSystemSettingEnabled” -Value “0” -Type DWord

    #####################################################################

    # Unload ntuser.dat
    IF ($item.SID -in $UnloadedHives.SID) {
        ### Garbage collection and closing of ntuser.dat ###
        [gc]::Collect()
        reg unload HKU\$($Item.SID) | Out-Null
    }
}
# Regex pattern for AzureAD SIDs
$PatternSID = 'S-1-12-1-\d+-\d+\-\d+\-\d+$'

# Get Username, SID, and location of ntuser.dat for all users
$ProfileList = gp 'HKLM:\SOFTWARE\Microsoft\Windows NT\CurrentVersion\ProfileList\*' | Where-Object {$_.PSChildName -match $PatternSID} |
    Select  @{name="SID";expression={$_.PSChildName}},
            @{name="UserHive";expression={"$($_.ProfileImagePath)\ntuser.dat"}},
            @{name="Username";expression={$_.ProfileImagePath -replace '^(.*[\\\/])', ''}}

# Get all user SIDs found in HKEY_USERS (ntuder.dat files that are loaded)
$LoadedHives = gci Registry::HKEY_USERS | ? {$_.PSChildname -match $PatternSID} | Select @{name="SID";expression={$_.PSChildName}}

# Get all users that are not currently logged
$UnloadedHives = Compare-Object $ProfileList.SID $LoadedHives.SID | Select @{name="SID";expression={$_.InputObject}}, UserHive, Username

# Loop through each profile on the machine
Foreach ($item in $ProfileList) {
    # Load User ntuser.dat if it's not already loaded
    IF ($item.SID -in $UnloadedHives.SID) {
        reg load HKU\$($Item.SID) $($Item.UserHive) | Out-Null
    }

    #####################################################################
    # This is where you can read/modify a users portion of the registry

    # This example checks for a key, adds it if missing, and creates / changes a DWORD in that key
    "{0}" -f $($item.Username) | Write-Output
    If (!(Test-Path registry::HKEY_USERS\$($Item.SID)\SOFTWARE\Microsoft\Windows\CurrentVersion\UserProfileEngagement)) {
	    New-Item -Path registry::HKEY_USERS\$($Item.SID)\SOFTWARE\Microsoft\Windows\CurrentVersion\UserProfileEngagement -Force | Out-Null
	}
    Set-ItemProperty registry::HKEY_USERS\$($Item.SID)\SOFTWARE\Microsoft\Windows\CurrentVersion\UserProfileEngagement -Name “ScoobeSystemSettingEnabled” -Value “0” -Type DWord

    #####################################################################

    # Unload ntuser.dat
    IF ($item.SID -in $UnloadedHives.SID) {
        ### Garbage collection and closing of ntuser.dat ###
        [gc]::Collect()
        reg unload HKU\$($Item.SID) | Out-Null
    }
}
Checking whether each item already exists helps the RMM to get the proper exit code and not show the script as failed when run.
If your company is a MSP or wants to become one and automation just seems out of reach, then contact us to run your RMM for you.
Nobody wants to be hacked, breached, compromised, or whatever else they are calling it now. Here is a quick list of things to think about to keep your company safe:
Compromise Prevention
Keep track of your inventory, both software and hardware.
Make sure to properly dispose of these things (recycle or responsible destruction)
Scan your network for vulnerabilities
Patch or remediate everything you find
Manage your antivirus & keep it up-to-date
Keep your passwords complex & safely stored
Remove all users / accounts when no longer in use
Look at best practices to harden your computers / network to attacks
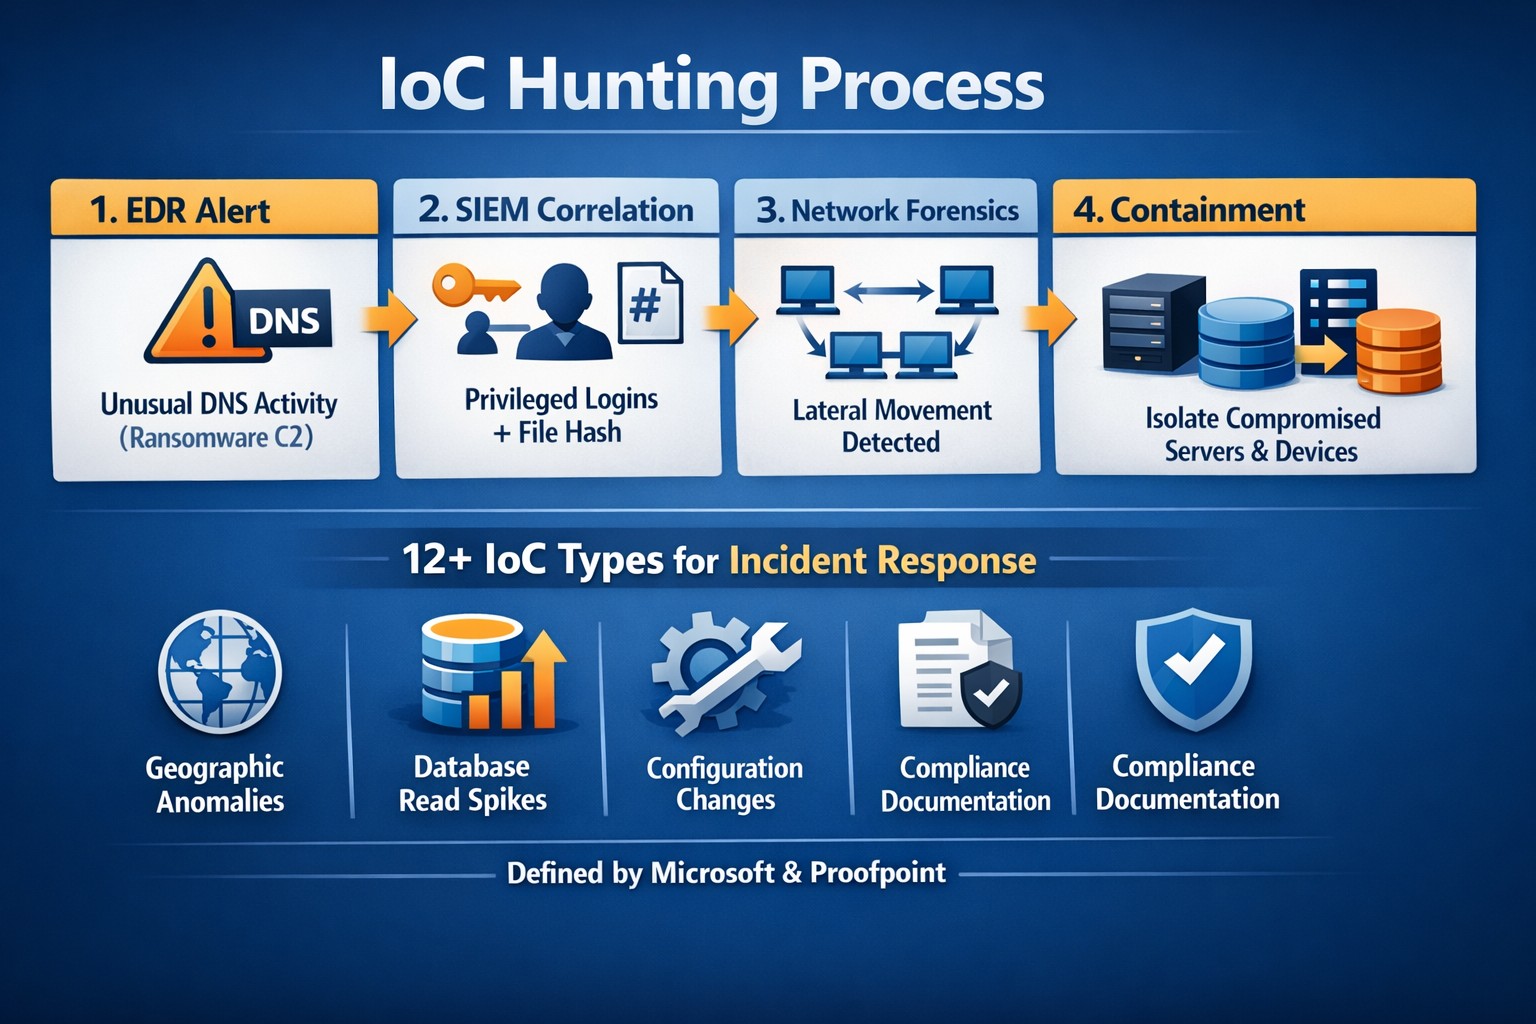
Monitor your network for strange activity (indicators of compromise)
If your company is concerned about security, then contact us to take care of it for you.
And God will generously provide all you need. Then you will always have everything you need and plenty left over to share with others. As the Scriptures say, “They share freely and give generously to the poor. Their good deeds will be remembered forever.” For God is the one who provides seed for the farmer and then bread to eat. In the same way, he will provide and increase your resources and then produce a great harvest of generosity in you. - 2 Corinthians 9:8-10
We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.