Had a local medial office want to move their current server into the cloud and because they are already an Office 365 customer, I chose to use Azure for their Virtual Machine. I helped them setup Azure to Araknis IPSec VPN to connect their headquarters to the hosted server. This tutorial will go into detail about the creation of this tunnel starting with the Microsoft Azure side first using Resource Manager. It will be using the following parameters:
VNet Name: TestNetwork
Address Space: 10.10.0.0/16
Subnets:
Primary: 10.10.10.0/24
GatewaySubnet: 10.10.0.0/24
Resource Group: TestResourceGroup
Location: West US
DNS Server: Azure Default
Gateway Name: TestVPNGateway
Public IP: TestVPNGatewayIP
VPN Type: Route-based
Connection Type: Site-to-site (IPsec)
Gateway Type: VPN
Local Network Gateway Name: TestSite
Local Subnet: 10.20.20.0/24
Connection Name: VPNtoTestSite
Configure an Azure VPN gateway
This part takes the longest, so it should be done first:
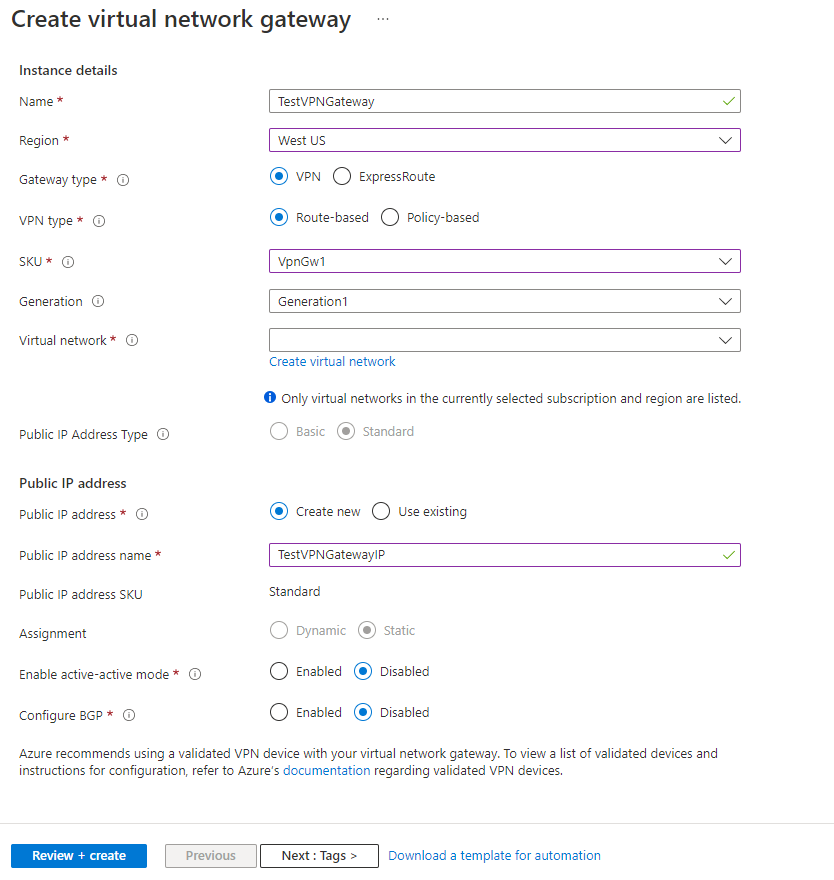
Click on the “+” icon at the top left hand side of the Resource Manager, then search for “Virtual Network Gateway” and click on the “Create” button.
Give the Virtual Network Gateway a name
Select matching Region to where Azure resources are located
Leave Gateway & VPN type the defaults
Choose a SKU <- These have changed since the article was created, so my “standard” now is WpnGw1 with Active / Active turned off (this is a good balance of performance and cost)
Choose or create a local network (not covered here, but must contain Gateway Subnet) that matches internal resources
Choose or create a Public IP Address
Leave the remaining values as their defaults and then click the “Create” button. (Please note the reminder that this takes 45 minutes to create!)
Configure an Azure Local Network Gateway
This is a reference to your on-premise network so that subnets can pass traffic:
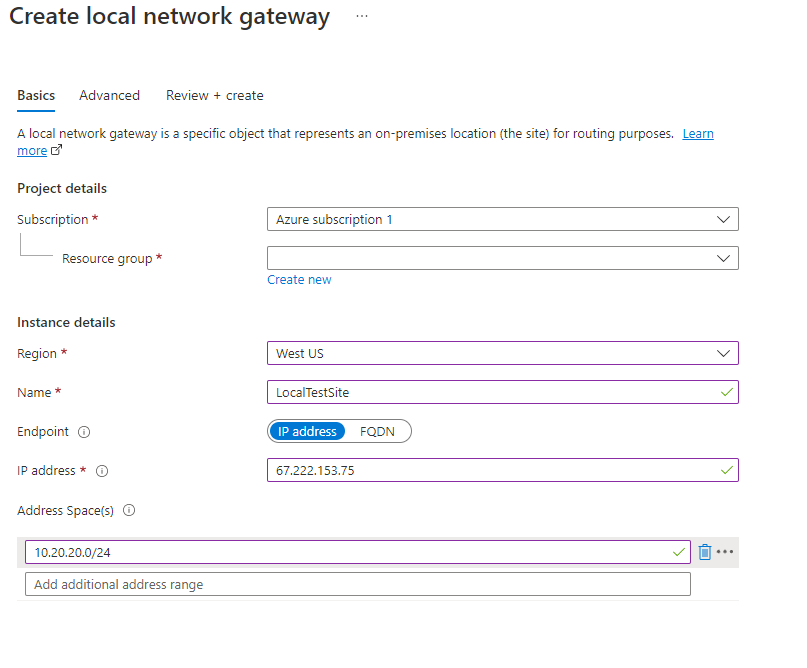
Click on the “+” icon at the top left hand side of the Resource Manager, then search for “Local Network Gateway” and click on the “Create” button.
Give the Local Network Gateway a name
Select matching Region to where Azure resources are located
Specify the external IP address of the local on-premise site
Specify the on-premise address space (subnet)
Leave the remaining values as their defaults and then click the “Create” button.
Configure an Azure VPN Connection
This will create the tunnel from Azure to the on-premise site:
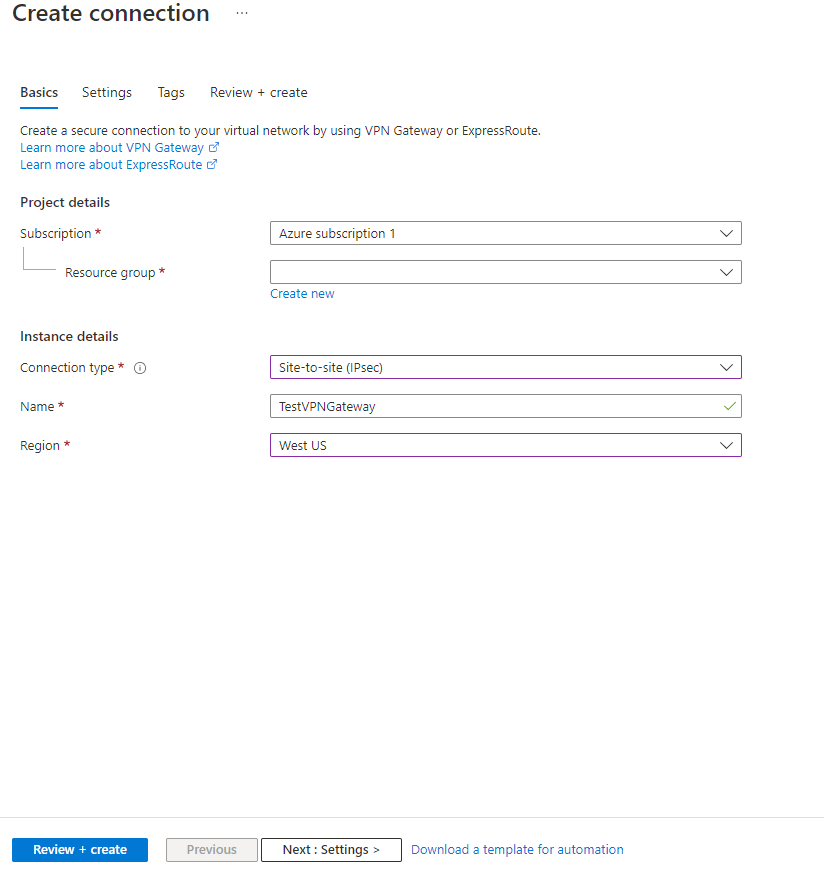
Click on the “+” icon at the top left hand side of the Resource Manager, then search for “Connection” and click on the “Create” button.
Choose “Site-to-site (IPSec)” as the connection type
Give the Connection a name
Select matching Region to where Azure resources are located
Leave the remaining values as their defaults and then click the “OK” button. On the summary screen click on the “OK” button to create the connection.
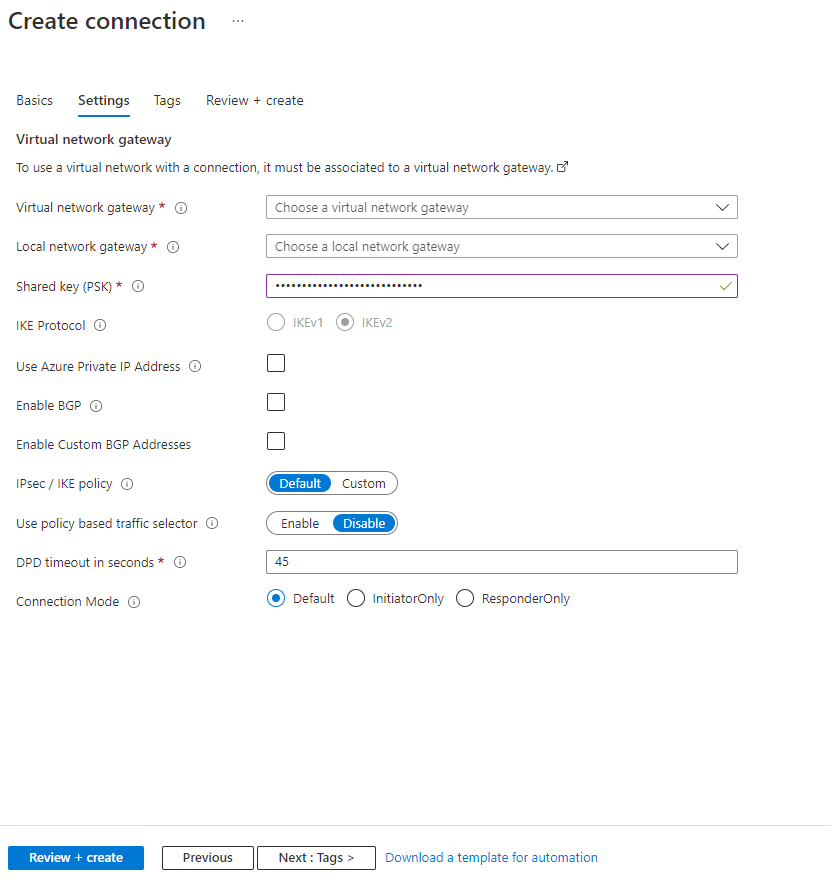
Choose the newly created Virtual Network Gateway
Choose the newly created Local Network Gateway
Specify a shared key
Leave the remaining values as their defaults and click the “Create” button.
This completes the setup of the Azure side of the VPN tunnel. Now to work on the Ubiquiti USG side.
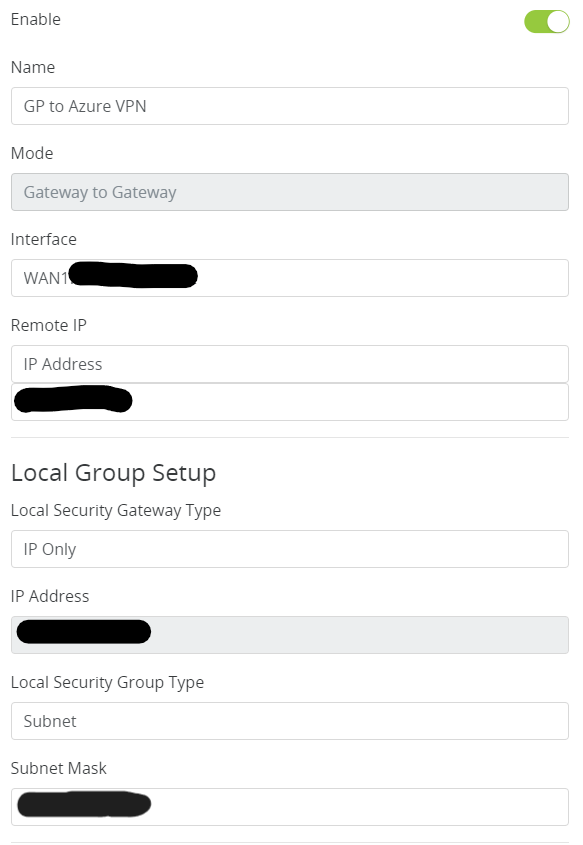
Configuring an Araknis IPSec VPN Network
Connect to Araknis router (need at least a 310 for this to work)
Click on Advanced > VPN
Scroll down to IPSec and click add new tunnel
Fill in the Remote IP address of the Azure VPN Gateway
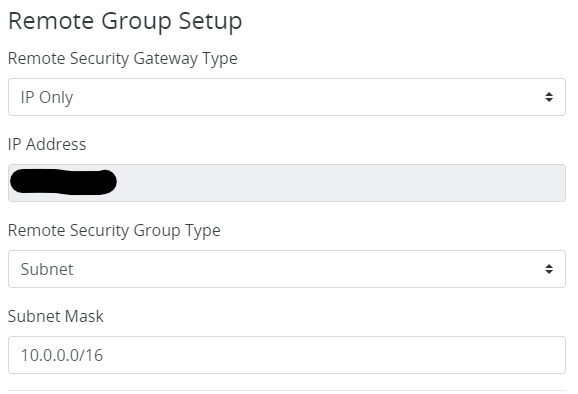
Fill in the Remote Subnet Mask
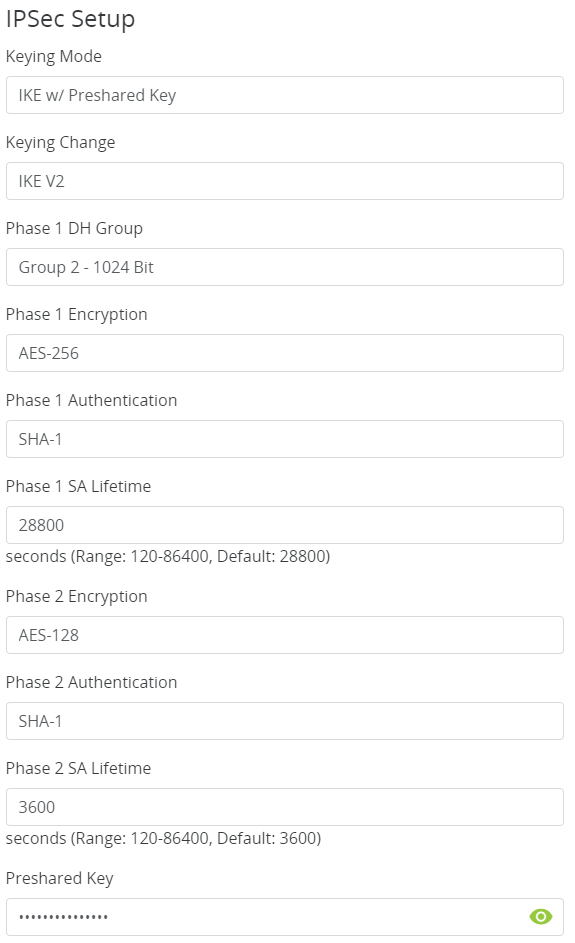
Make the following changes to IPSec Setup
That is all there is to it. If your company is currently using either Microsoft Azure or Araknis routers and would like a VPN created, then contact us for assistance.
Farmhouse Networking’s zero trust security model prevents lateral movement
This is the ninth in a series about the concept of Zero Trust, which means in the IT sense that you trust nothing and always verify everything surrounding and connected to your network. Today’s discussion will be on Network Security.
Network Security
Network Security is having the proper hardware and configuration of that hardware in place to protect the business network. This configuration includes segmenting network traffic to keep specific types of traffic, like guest devices, separate from traffic of business devices. It also includes keeping outsiders out of the network and detecting when they have breached security measures. Here are some questions to ask:
Do you have a business class router / firewall?
Do you have business class switches and access points that support segmentation?
Is your network configured to segment business traffic from guest traffic?
Are devices like VoIP phones and network cameras on their own network?
Is geo-location blocking turned on for non-essential countries?
Is network traffic being analyzed for suspicious activity?
Do you filter internet traffic?
Can your network detect and respond to a breach?
If your company is wanting to lock down network security, then contact us for assistance.
Farmhouse Networking virtualizes small office servers reducing hardware footprint while improving uptime and disaster recovery for Oregon SMBs.
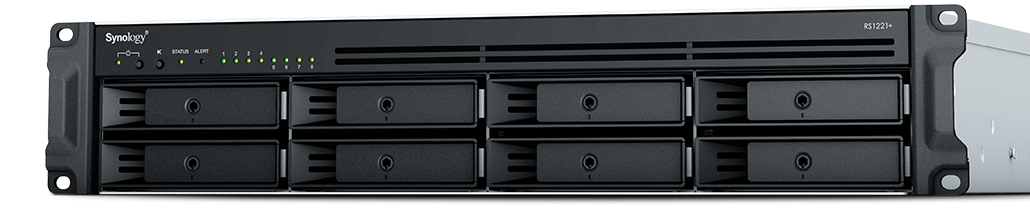
Had a client recently who had a smaller office network (they have up to 6 concurrent users) with a server to process orders from their website using a software called StoneEdge. This software is SQL-based database with a Microsoft Access front-end. It was time to upgrade their server to new hardware and cost was definitely an issue based on their size and order volume. In this case we chose to use a Synology device to act as the virtual machine host and create a new virtual server on the host. Here are some details:
4x Seagate 4TB IronWolf Pro 7200 rpm SATA III 3.5″ Internal NAS HDD
Picked the Synology based on the expandability of RAM to 32 GB, the capability to use cache drives, and storage growth over time. It also has a 4-core 2.2 Ghz Ryzen processor which was plenty based on their old servers CPU usage.
Basics of Setup
Assembled parts
Installed Synology OS
Setup HDDs in Synology SHR2 RAID
Added M.2 drives as cache
Installed the Virtual Machine Manager app
Created a VM with the max CPU available and max Memory available
Uploaded the ISO for the server OS
Installed the server OS
Setup the StoneEdge application
Migrated data
This build did not increase performance dramatically, but it did allow them to spend about half the cost of a full server to accomplish the same purpose. It also reduced costs by using the Synology for backup of the server locally and into S3 storage in the cloud for redundancy.
If your company is looking to move their servers to a virtual environment or into the cloud, then contact usto start the process
Farmhouse Networking resolves credential manager clearing after reboot by deleting Microsoft Vault folder and restarting services for Oregon RMM automation.
As our business continues to focus on providing white labeled Tier 3 IT support services, RMM as a service, and co-managed IT services this blog will be highlighting tips for using Powershell to fix Credential Manager empty after reboot. There has been several users at a bunch of clients recently that have lost access to a network share due to saved passwords and we found Credential Manager empty after reboot. It was easy enough to re-add their password to Credential Manager, but it was not sticking around. This sounds like a job for automation, so we created a script to clear the errant Credential Manger files and create a new entry for the user to connect to file shares.
Variables
$user = username to add to Credential Manager of network share connection
$pass = password to add to same
Script Snippet
### Remove file folder associated with Credential Manager
Remove-Item -Path %localappdata%\Microsoft\Vault -Recurse

### Install Credential Manager Powershell Module
Import-Module -Name CredentialManager -Force

### Convert password to Secure String and create credential
$password = ConvertTo-SecureString -string $pass -AsPlainText -Force
$Credential = new-object -typename System.Management.Automation.PSCredential -argumentlist $user, $password

# Save the credential object directly without unwrapping it:
New-StoredCredential -Credentials $Credential -Target 'Share Credentials' -Persist Enterprise -Comment "Share Credentials for $($Credential.UserName)" > $null
This script will need to be run in the context of the user who needs the credential created. Please use caution with this script as it will empty Credential Manager completely for the user context run with. Also it is advised to run a full CHKDSK /R on the root (C:\ usually) directory to make sure that nothing else is corrupt on the drive.
If your company is a MSP or wants to become one and automation just seems out of reach, then contact usto run your RMM for you.
As our business continues to focus on providing white labeled Tier 3 IT support services, RMM as a service, and co-managed IT services this blog will be highlighting tips for using Powershell to create Office 365 User and add them to groups. We have several clients with high employee turn-over which makes it necessary to often create Office 365 user. We will detail how to find all the needed data to create the proper script for each client (yes it will take a different script for each client due to different group names for each client).
Research
You need to get two pieces of information – the license type used by the organization to create users and the names of the groups to add users to
To find out the license types used use this commands:
Connect-MsolService
Get-MsolAccountSku
To find out all the groups in the organization use this commands:
Connect-ExchangeOnline
Get-UnifiedGroup | Format-Table Alias
Variables
$displayName = Full user name – usually First name & Last Name $userPrincipleName = Email address for user $adminuser = Email address for admin of Office 365 Tenant $adminpass = Password for admin of Office 365 Tenant $licenseType = Office 365 license type found in research above
There is also the need for variables for each group you will be adding users to (found in research above). For this example I will be using:
$CompanyShared = Company Shared Contacts $CompanyTimeOff = Company Time Off Calendar $BillingPayroll = Billing & Payroll Group Email
Script Snippet
###Use this command to be allowed to use DotNet assemblies
Add-Type -AssemblyName System.web

$displayName = "UserFirst UserLast"
$userPrincipleName = “User@Company.com”
$adminuser = "admin@Company.com"
$adminpass = '@dm1nP4ssw0rd'

$CompanyShared = "yes"
$CompanyTimeOff = "yes"
$BillingPayroll = "no"

###converts admin credentials to useable format for connections to Office 365
$adminpassword = ConvertTo-SecureString -string $adminpass -AsPlainText -Force
$admincred = new-object -typename System.Management.Automation.PSCredential -argumentlist $adminuser, $adminpassword

Connect-AzureAD -Credential $admincred
Connect-MsolService -Credential $admincred

$mailNickname = $userPrincipleName.Split("@")[0]

###To find User License Types use Get-MsolAccountSku
$licenseType = "companytenantID:SPB"

###Generates a random password length
$minPassLength = 8 ## characters
$maxPassLength = 15 ## characters
$passlength = Get-Random -Minimum $minPassLength -Maximum $maxPassLength

###Generates a random number of non-alpha characters in the password
$minNonAlphaChars = 1 ## characters
$maxNonAlphaChars = 5 ## characters
$nonAlphaChars = Get-Random -Minimum $minNonAlphaChars -Maximum $maxNonAlphaChars

###Creates the password, makes it useable by Azure, sets it up to not require password change, and creates account
$password = [System.Web.Security.Membership]::GeneratePassword($passlength, $nonAlphaChars)
$PasswordProfile = New-Object -TypeName Microsoft.Open.AzureAD.Model.PasswordProfile
$PasswordProfile.Password = "$password"
$PasswordProfile.ForceChangePasswordNextLogin = $false
Write-Host "Password is set to $password for $displayName"
$user = New-AzureADUSer -DisplayName $displayName -PasswordProfile $PasswordProfile -UserPrincipalName $userPrincipleName -mailNickname $mailNickname -AccountEnabled $true

###Waits 5 minutes for the user creation process in Office 365
Start-Sleep -Seconds 300

###Sets additional parameters for account that are needed like location, license type, and sets password to never expire
Get-MsolUser -UserPrincipalName $userPrincipleName | Set-MsolUser -UsageLocation US
Get-MsolUser -UserPrincipalName $userPrincipleName | Set-MsolUserLicense -AddLicenses $licenseType
Get-MsolUser –UserPrincipalName $userPrincipleName | Set-MsolUser –PasswordNeverExpires $True

###Adds new user to groups
if ($CompanyShared -eq "yes")
{ Add-MailboxPermission -Identity companyshared@premieror.com -User $userPrincipleName -AccessRights FullAccess -InheritanceType All}

if ($CompanyTimeOff -eq "yes")
{ Add-MailboxPermission -Identity companytimeoff@premieror.com -User $userPrincipleName -AccessRights FullAccess -InheritanceType All}

if ($BillingPayroll -eq "yes")
{ Add-MailboxPermission -Identity billing_payroll@premieror.com -User $userPrincipleName -AccessRights FullAccess -InheritanceType All}
This script requires that the admin account you use to setup the user have multifactor authentication turned off (I know not secure), so use a really long complex password. The script creates a random password for the new user and write it to output. The script will take several minutes to run due to the waiting for the account to finish setup before adding additional parameters and adding them to groups.
If your company is a MSP or wants to become one and automation just seems out of reach, then contact usto run your RMM for you.
As our business continues to focus on providing white labeled Tier 3 IT support services, RMM as a service, and co-managed IT services this blog will be highlighting tips for Synology resource monitoring. We have developed best practices for alerting on a Synology device for resources like CPU, Memory, and Disk Usage. When these Synology resource monitoring alerts are consistently triggered it show that the device is over utilized or if they remain triggered for long periods of time then it shows there is an issue on the device itself. We also setup weekly Storage Reports to get an accurate view of the changes and growth going on with client storage.
Setup Notifications
Make sure that Notifications are setup on the Synology first
Open Control Panel
Click on Notifications
Check enable email notifications
Choose Service Provider
Login to Gmail or use Custom SMTP server for Office 365 as the sender
Change Subject to indicate name of device
Add recipient email (Best to use one that ties into a PSA or RMM)
Click Apply
Send a Test Email
Setup Synology Resource Monitoring
Open Resource Monitor app
Click on Performance Alarm to the left
Click on Rules tab
Click Create
Create the following Rules one by one
Volume Critical
Select which volume [create multiple rules if more than one volume]
Select Disk I/O utilization
Greater than 90%
Level Critical
Volume Warning
Select which volume [create multiple rules if more than one volume]
Select Disk I/O utilization
Greater than 75%
Level Warning
System Memory Critical
Memory Usage
Greater than 90%
Level Critical
System Memory Warning
Memory Usage
Greater than 75%
Level Warning
System CPU Critical
CPU Usage
Greater than 90%
Level Critical
System CPU Warning
CPU Usage
Greater than 75%
Level Warning
Click Settings and check box to Enable usage history then click Save
Setup Storage Reports
Open Storage Analyzer
Select new location
Create new shared folder named Log Files – hide from network
Go back to Storage Analyzer and select new folder
Set volume usage data to be collected Daily at 2am
Create report task
Send to email (Best to use one that ties into a PSA)
Generate reports at Monday 4am
Keep 60 reports then click Next
Select report items
Volume Usage
Shared Folders
Potential Duplicate Files
Large Files
Least Recently Modified Files then click Next
Analyze all folders then click Next
Leave duplicate file defaults then click Next
Click Done
Close App
Once this is setup you will start getting email alerts sent to you or better yet your PSA / RMM for ticket creation and review.
If your company is a MSP or wants to become one and automation just seems out of reach, then contact us to run your RMM for you.
This is the eighth in a series about the concept of Zero Trust, which means in the IT sense that you trust nothing and always verify everything surrounding and connected to your network. Today’s discussion will be on Application Whitelisting.
Application Whitelisting
Application Whitelisting is a process of determining which software programs the company absolutely needs to do business, marking them as safe, and blocking any other program that tries to run on company computers. This methodology has the distinct advantage of blocking almost all forms of malware on computers. Pairing this with a good next-gen antivirus creates an impenetrable wall against malware threats. It also prevents users from accidentally or intentionally running something that should not be on company computers. Here are some questions to ask:
Do you know all software on your computers?
Do your users spend time on company computers listening to music?
Have any of your users ever downloaded software without asking?
Do you have a computer use policy? How is that enforced?
If your company is wanting to lock down what is running on company computers, then contact us for assistance.
This is the seventh in a series about the concept of Zero Trust, which means in the IT sense that you trust nothing and always verify everything surrounding and connected to your network. Today’s discussion will be on software patching.
Software Patching
Software patching is a neccesity because no person who writes code is perfect and hackers are actively looking for these mistakes. The hackers find the mistakes and then develop ways of using these to exploit the software, computer, or whatever else they can gain access to. The only way to combat both the mistakes and the exploits is to discover them before the hackers do and patch the hole in the software. This patch can however lead to unforseen consequences to the software, so a plan for testing and deployment of patches is needed to avoid unexpected downtime to businesses.Here are some questions to ask:
Do you know all of the hardware and software on your network?
Do you check for hardware, operating system, and other software regularly?
How do you check for updates, patches, or upgrades to software?
How do you install these patches? Is it automated?
Are these patches tested before installation?
What happens if a patch causes problems?
Do you have a log of all installed updates?
Are any systems or software on your network no longer supported for updates?
If your company is going to use full disk encryption or has compliance requirements that you need consulting for, then contact us for assistance.
As our business continues to focus on providing white labeled Tier 3 IT support services, RMM as a service, and co-managed IT services this blog will be highlighting tips for RMM automation. Here is a script that we came up with to handle a particular client that dumps tons of PDFs into a folder unsorted and wants individual folders created for each unique file name. We have tailored this script to be used not only at that client but for any folder on any Microsoft Windows computer that needs to be sorted in this manner. This script could easily be modified to sort other types of files.
Variables
Here are the variables we are using for this script:
$SourceFolder = This is the target folder to be sorted
Script Snippet
# Defines the folder that sorted data will go into
$TargetFolder = $SourceFolder + " Sorted"

#Defines how to match files with similar names, in this case we put files with the same name then a dash or underscore and other numbers or letters to be placed in the same folder
$MatchRegEx = "[-_]"


#Grabs only the PDF files in the folder being sorted (modify for other extension types or remove filter to sort all files)
Get-ChildItem -Path $SourceFolder -Filter *.pdf |
    ForEach-Object {
        #Creates folder name for child folders in sorted data
        $FileNameFolder = $_.Name -split $MatchRegEx
        $ChildPath = Join-Path -Path $FileNameFolder[0].Replace('.pdf','') -ChildPath $_.Name

        [System.IO.FileInfo]$Destination = Join-Path -Path $TargetFolder -ChildPath $ChildPath

        #Checks if folder exists and if not creates child folder
        if( -not ( Test-Path -Path $Destination.Directory.FullName -erroraction silentlycontinue) ){
            New-Item -ItemType Directory -Path $Destination.Directory.FullName
            }

        #Copies file into child folder
        Copy-Item -Path $_.FullName -Destination $Destination.FullName
        }
This script is non-destructive meaning that the files are copied and not moved. This script gives screen output of each new child folder created.
If your company is a MSP or wants to become one and automation just seems out of reach, then contact us to run your RMM for you.
This is the sixth in a series about the concept of Zero Trust, which means in the IT sense that you trust nothing and always verify everything surrounding and connected to your network. Today’s discussion will be on endpoint security.
Endpoint Security
Endpoint security is a fancy term used to describe how the computers on the network are protected. This used to be done by antivirus but due to the complexity of the attacks hackers are using to compromise networks these days, the definition has expanded greatly. This now includes things like Enhanced Detection & Response software, Security Operations Centers, DNS Filtering, employee train and more. Here are some questions that you should be asking yourself:
Are your endpoints protected by antivirus or enhanced detection & response?
Is website traffic being monitored? Restricted?
Are your employees being trained in cyber security?
Are computer logs being monitored for malicious activity?
Would unusual or suspicious activity on a computer be noticed? Alerted on?
Do you have security permissions set on all file shares?
Do you have least privileged access configured on those shares?
Do you keep track of what software is installed on all workstations?
Do you block access to unauthorized software?
Are files encrypted on servers and workstations?
Are your mobile devices managed? Can you wipe them remotely?
Are USB ports blocking removeable storage devices?
Are endpoints set to automatically log-out?
If your company is going to use full disk encryption or has compliance requirements that you need consulting for, then contact us for assistance.
Farmhouse Networking secures Oregon business backups with zero trust immutability preventing ransomware encryption and deletion.
This is the third in a series about the concept of Zero Trust, which means in the IT sense that you trust nothing and always verify everything surrounding and connected to your network. Today’s discussion will be on the backup of important data.
Backup
Backup is a way of creating multiple copies of your important data and the systems that house them. This has become a necessity thanks to acts of God (unforeseen physical disasters), acts of employees (accidental or purposeful destruction of data), and acts of malicious hackers (ransomware or malware). Here are some questions that you should be asking yourself:
What data or systems are being backed up?
How often are these backups being performed?
Are your backups protected from natural disasters (offsite and redundant)?
How long are backups being stored?
Once expired are they securely removed?
What is the process for recovering files, emails, workstations, servers, applications, databases?
Have you tested your recovery process lately?
Do you know how long it will take to recover?
How will business continue until systems are restored?
How will you merge new information into recovered data once restored?
How often do you test your recovery process?
Is the recovery test process automated?
Take time to think about these questions and decide where changes can be made to better protect your IT investments, or contact us to do the thinking for you.
Farmhouse Networking secures vendor access with zero trust verification for Grants Pass businesses, protecting against supply chain threats.
This is the second in a series about the concept of Zero Trust, which means in the IT sense that you trust nothing and always verify everything surrounding and connected to your network. Today’s discussion will be on the vendors you purchase network equipment from.
Trusted Vendors
Trusted vendors are those who supply workstations, servers, routers, switches, power protection, software, and anything else connected to your network. Here are some questions that you should be asking yourself:
Do you know who makes your network equipment, servers, computers, and software?
Do you know the way to contact their support and have current account access information?
Do you have current warranties / support contracts on hardware and software?
Is the hardware able to perform at the level needed?
Are you purchasing software from those who meets industry standards?
If a subscription, how much are you paying and are you on the correct plan for your needs?
When is the last time you upgraded your software and hardware?
Have you budgeted for the next upgrade?
Take time to think about these questions and decide where changes can be made to better protect your IT investments, or contact us to do the thinking for you.
Farmhouse Networking deploys zero trust physical security for Grants Pass businesses, verifying every facility access request continuously.
This is the first in a series about the concept of Zero Trust, which means in the IT sense that you trust nothing and always verify everything surrounding and connected to your network. Today’s discussion will be on the physical security surrounding your network.
Physical Security
Physical security can include the locks on the doors, where things are placed, and how they are protected from the unpredictability of the environment. Here are some questions that you should be asking yourself:
Do you know where your network equipment is located?
Is the server / network in a separate area from where work is done?
Is this separate area behind a locked door?
Is the equipment in a locked rack or cabinet?
Is there a separate air conditioning zone for this area (servers like it cold)?
Is there a separate alarm zone for this equipment?
Who has the codes?
Is there a security camera watching this area (we don’t install these)?
How long is the recording for?
Who has access to the recordings?
Are computers located in areas where customers can physically touch them?
Are unused USB ports on the computer turned off or locked?
Are all systems protected by battery backup devices?
Are all systems off the floor in case of a flood?
Take time to think about these questions and decide where changes can be made to better protect your IT investments, or contact us to do the thinking for you.
We caught wind of two separate actions the US has taken against Cyber Threats from Russia over the weekend:
Kaspersky
The first is news that the US Federal Communications Commission has added Russian cybersecurity company Kaspersky Lab to its list of entities that pose an “unacceptable risk to US national security,” according to a report from Bloomberg. This company has been banned from use by government agencies since 2017 when a bill was signed due to the companies ties to the Kremlin.
Russian Hackers
The second article was a press release from the FBI stating that:
“The Department of Justice unsealed two indictments today charging four defendants, all Russian nationals who worked for the Russian government, with attempting, supporting and conducting computer intrusions that together, in two separate conspiracies, targeted the global energy sector between 2012 and 2018. In total, these hacking campaigns targeted thousands of computers, at hundreds of companies and organizations, in approximately 135 countries.”
This hacking activity should be another wake-up call to American businesses to harden their defenses and remain vigilant against cyber security threats. These people are nationally sponsored criminals and we must protect ourselves.
If your company is currently using Kaspersky or any other Russian based vendors, then it is time to carefully consider whether to continue being connected with them and contact us for assistance migrating to a trusted source.
83% of employees continue accessing old employer’s accounts
Farmhouse Networking Grants Pass implements robust employee offboarding to revoke access and secure networks for Oregon businesses.
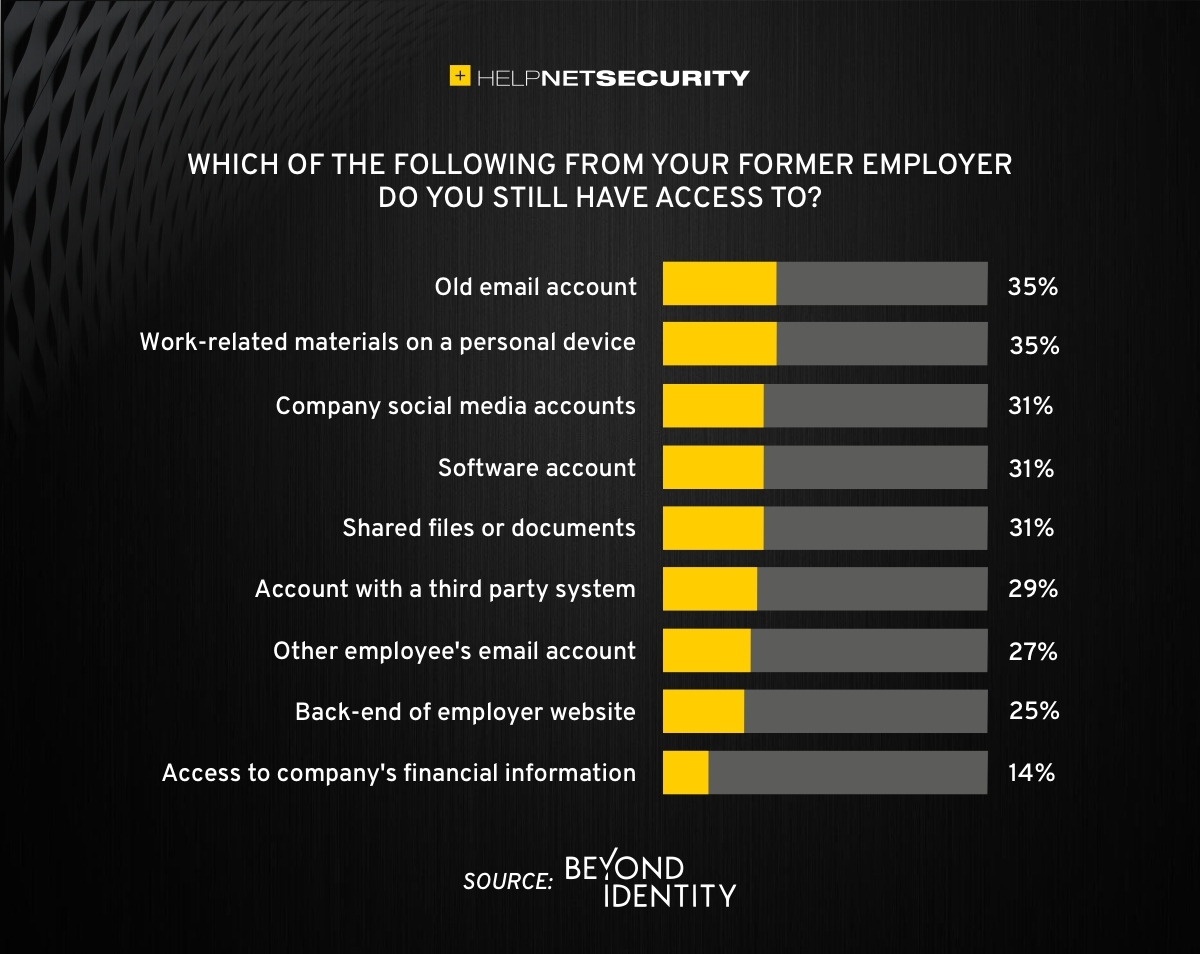
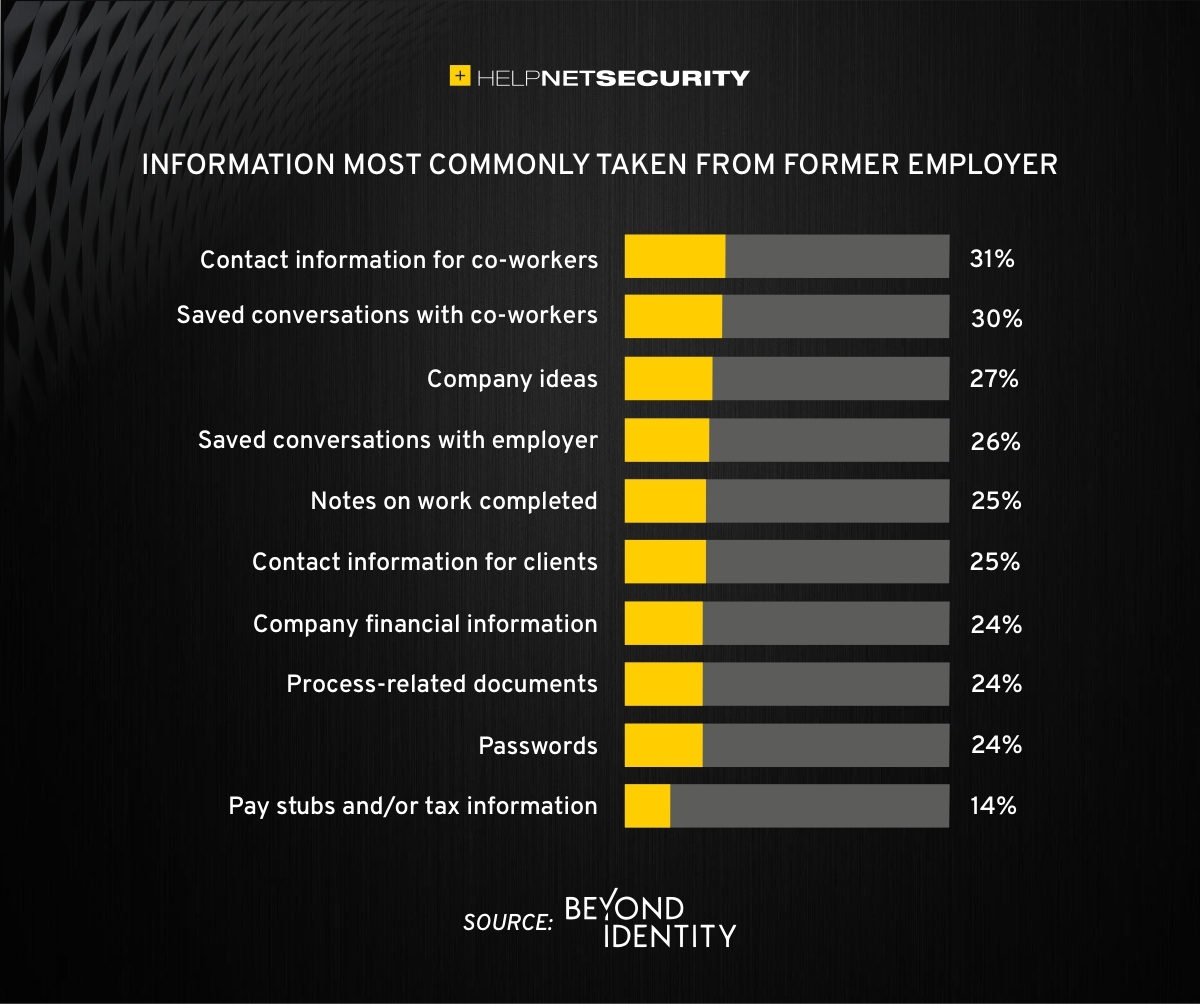
A study was performed by Beyond Identity throughout the US, UK, and Ireland which found that 83% of employees admitted to maintaining continued access to accounts from a previous employer. Also a shocking 56% admitted to using this access to harm their former employer.
The study also states that a professional and details offboarding process can prevent unauthorized access by former employees by eliminating their passwords and other insecure authentication methods. Strangely enough this also creates a sense of goodwill in the company that helps to lessen the motivation for employees to attempt this kind of malicious access. This kind of process is vital considering the current employment market and high turn over rates at almost all companies.
If your company does not have a detailed and documented offboarding process, thencontact usfor assistance.
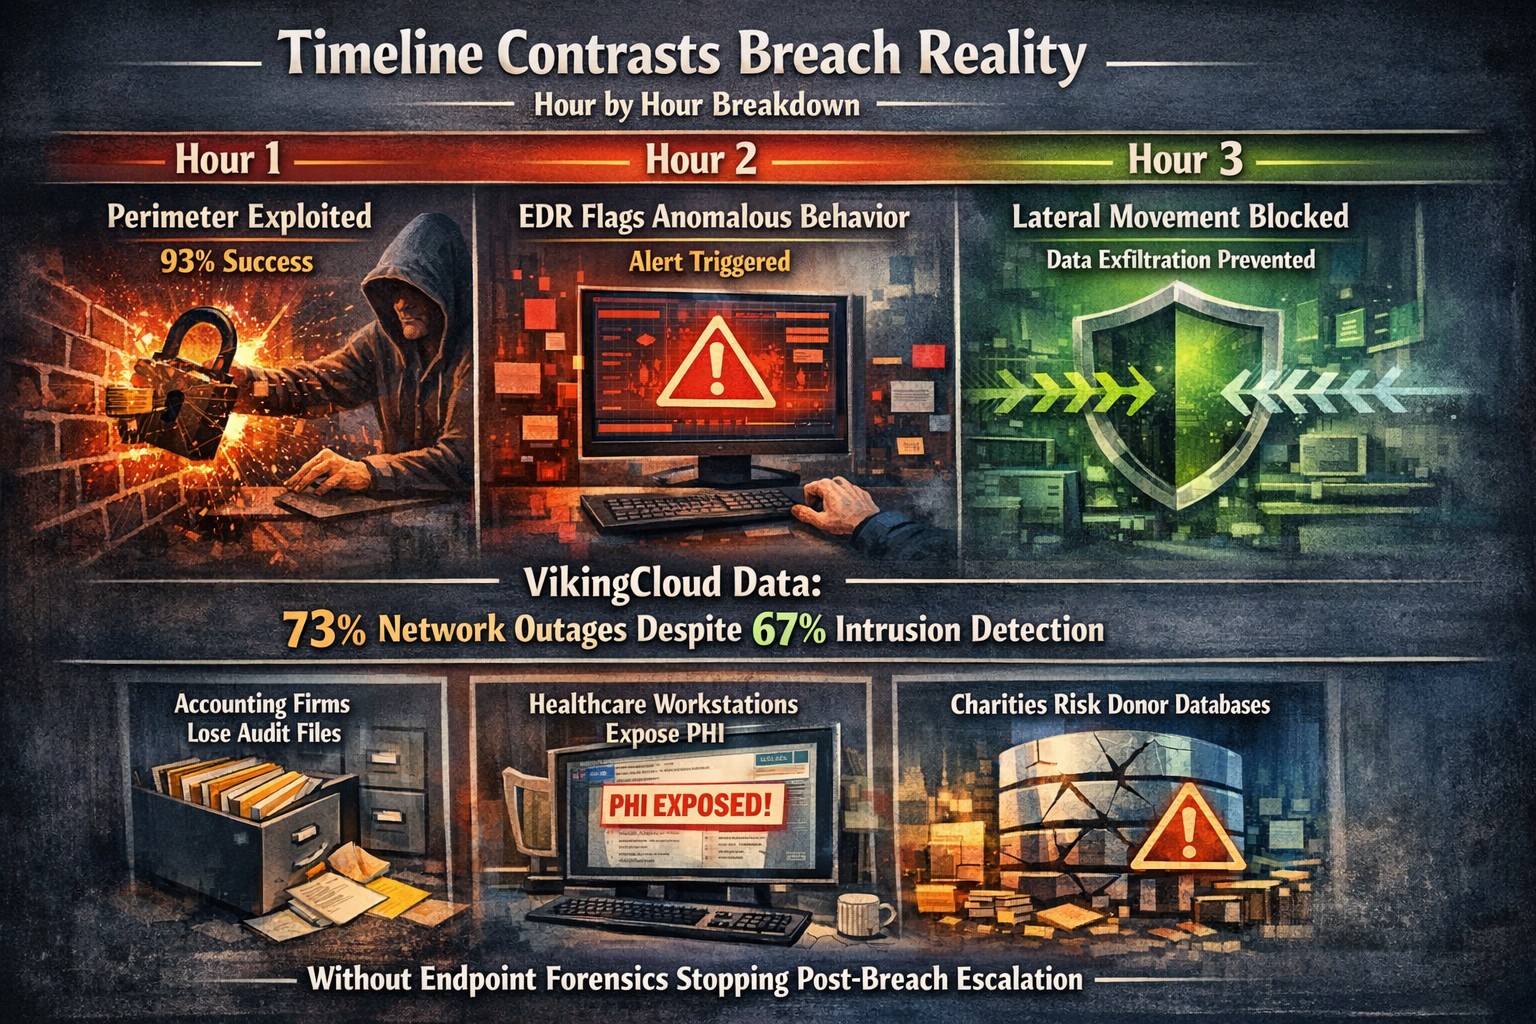
Security researchers performed penetration testing on the networks of 45 various mid-sized companies and found that in real life scenarios 93% of those networks were able to be compromised to the point of business disruption. Here are the details:
The Target
The 45 companies were polled to determine what would be an unacceptable business interruption. They decided that the following met that criteria:
Disruption of production processes
Disruption of service delivery processes
Compromise of the digital identity of top management
Theft of funds
Theft of sensitive information
Fraud against users
These became the target for the penetration testers.
The Process
In order for the penetration tester to achieve their target, they followed the following process:
Breach the network perimeter – This was done by the use of compromised passwords found on the Dark Web and know vulnerabilities on devices that were directly connected to the internet
Obtain maximum privileges – In 100% of the networks, once an attacker was inside the network
Gaining access to key systems – With maximum privileges, the testers are able to gain access to other areas of the network including databases, executives computers, and production servers
Develop attacks on target systems – Once key systems are compromised the testers then figured out how to create the unacceptable business interruption. Although they could have created these interruptions, they only gathered proof that they could to present the data to the companies.
How to Defend
There are a couple main ways to defend against these kinds of attacks:
Security Controls / Segmentation – Creating least privileged access to key systems and segmenting the network will keep hackers from traversing the network once inside
Enhanced Network Monitoring – Modern cyber security tools watch activity and traffic on the network to find indicators of compromise. They pool this information into an attack history that can be used to remediate and further protect.
Your company is not as safe as you think, so contact us for free initial cybersecurity evaluation and risk report. .
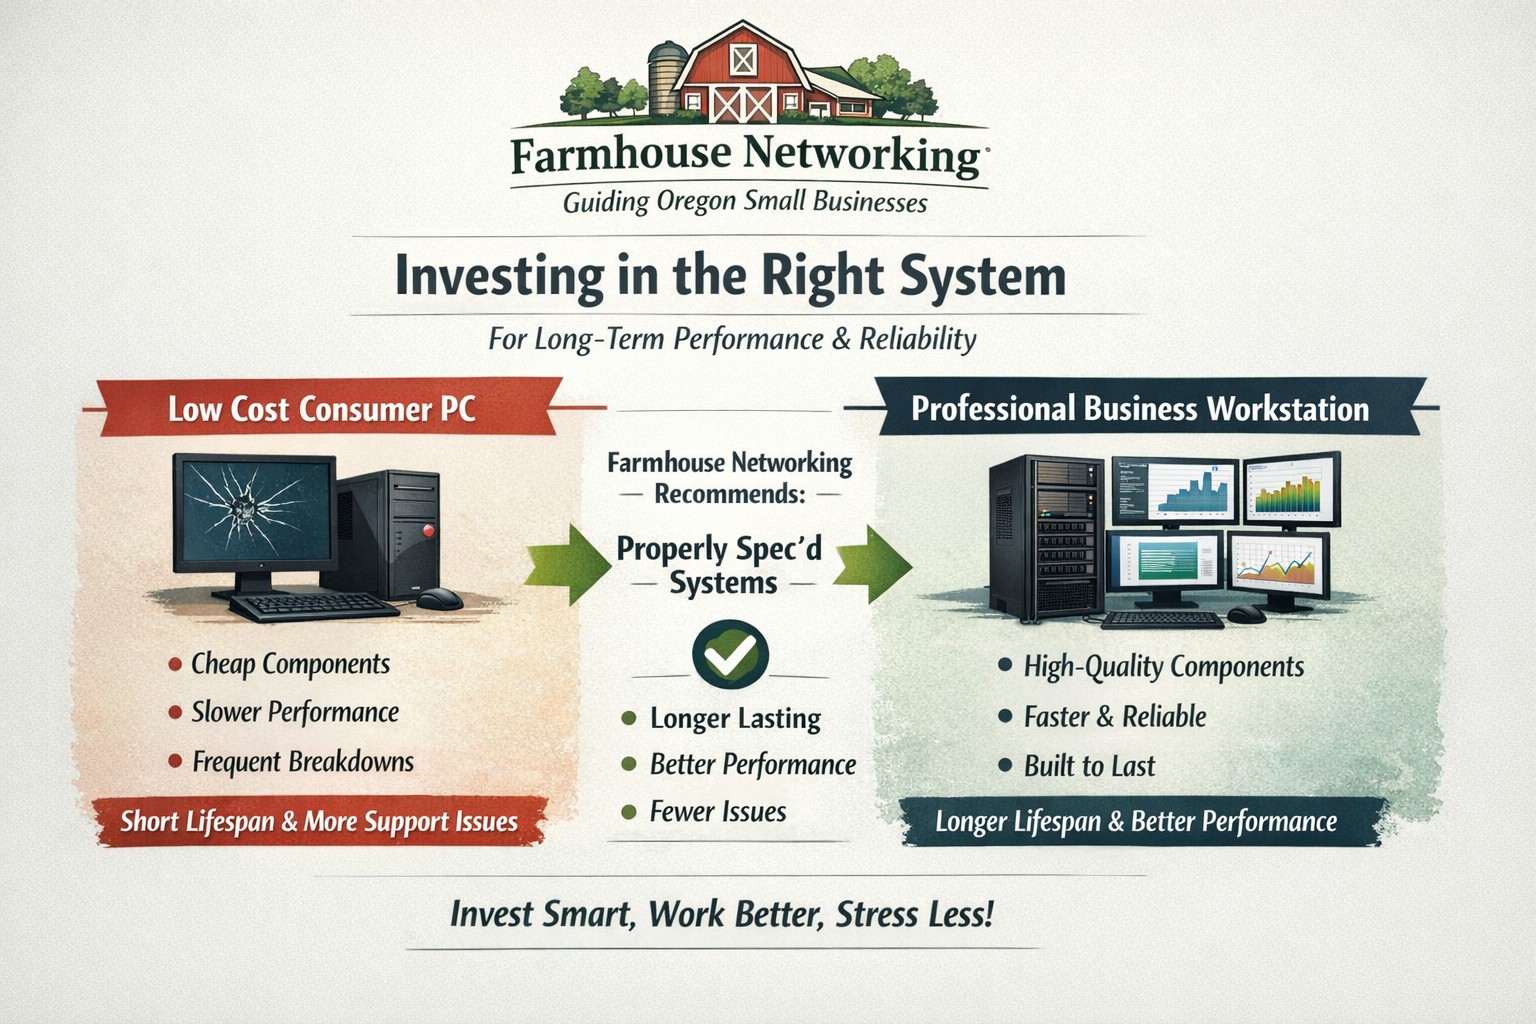
Farmhouse Networking helps small businesses choose new computers where price reflects long term reliability, performance, and lower total cost of ownership.
Based on some recent experiences and plenty of past experiences, we thought it would be good to help customers make good choices when shopping for new computers. The easiest and best way is to trust us to do the research and know your company’s computing needs enough to provide you with the best computer for the best price. However there are some that like the thrill of the hunt and want to find the best “deal” themselves. They try to save money via sales that we honestly cannot compete with on price. This newsletter is meant to help guide them to the best options for solid performance and longevity in their investment.
Shopping Guide
Big Box Stores (Staples, Walmart, Costco, Best Buy, etc.): Seeing the local adds, these retailers are often at the top of the list for many people when shopping for a computer. They offer the convenience of being able to physically touch the computer being purchased and not having to wait for the computer to be shipped from some other part of the country. The downside is that these retailers are selling a commodity product for the smallest cost possible to maximize their profits. This means they are willing to have computers made from the least expensive parts and lowest build quality. They also find ways of scrimping on important features and masking this deficiency with flashy claims on features or partnerships with celebrity endorsements. Don’t be fooled these are disposable computers that will not stand up to the demands of a business environment.
Online Discount Sellers (eBay, Amazon, Google. Overstock, etc.): Bargain hunters are getting savvier with online tools and searches for the products they want. This type of “retailer” works much like the big box store, but you have to trust the pictures you see online and wait for the product to arrive from across the country or globe. These online stores are often just marketplaces where smaller retailers post their products to gain greater visibility then they could on their own. They are also notorious for selling what appear to be quality computers that have been “refurbished” in-house. These refurbished computers are usually years old and are a Frankenstein monster of spare used parts from their shop. Much like buying a car from a used car lot, you get all the troubles of someone else’s computer with all the reliability of a computer that is past its prime held together with old parts.
What to look for in a new computer
Business Class: This is important because manufactures who have this distinction on their products take the time to make a quality computer with mid-range parts. These computers will have all the needed features and typically last much longer then the disposable computers from other stores. If you go directly to the manufacturers website, they will typically have a section labeled Business that you can look through the models they have given this distinction.
Processors: This is the capacity of the computer to crunch through data. There are two main companies that make these chips, Intel and AMD. Intel is what I recommend for the majority of business users (except for those who only do light office work). They currently are using a system of Generations and i-series distinctions. The Generations help determine the age of the processor with the latest being 12th-generation processors, so if you are looking at a computer with a 9th-generation processor it is likely 3 years old out of the box. The i-series consists of i3, i5, i7, and i9 which is a measure of the raw computing power that the processor contains. Our recommendation for businesses are i5 for general office work and i7 if you are a power user who does many things at once.
Memory: This is the short-term memory capacity of the computer, so the more you have the more you can accomplish at once. These chips also have designations of DDR technology and PC-speed rating. The DDR technology has slowly changed over time and they are now shipping DDR5 chips for top of the line gaming computers, but for typical office computers the DDR4 technology will be the best performance per dollar. As for the PC-speed rating, it will somewhat match the DDR number with the latest in the PC5-38400 range, but again the PC4 with the highest number possible next to it will be sufficient. General office work can be accomplished with 8GB of RAM, but 16GB is becoming the new norm. Those who want more performance will need to go to 32GB or higher.
Hard Drive: This is the long-term memory storage of the computer. There have been massive improvements in technology on these in the past few years and performance has jumped substantially. This is one of the ways that big box stores save money the most, they sell an old fashioned hard drive in a new computer and performance suffers greatly. The newest technology is called NVMe and any new computer should contain this kind of hard drive to see the best performance. If cost is prohibitive, then at least get the previous technology of an SSD installed in the computer.
Everything Else: The rest is mostly personal taste. If you want wireless, then get one with wireless in it with the latest being WiFi6 and some include Bluetooth connections too. If you want a large screen, touchscreen, fingerprint scanner, lightweight, certain specific ports for your devices, or whatever other features – these will be the finishing touches that help shape your final choice.
If your company is going to looking to buys new computer, then contact us to save yourself the time and money of getting a computer or worse the wrong computer.
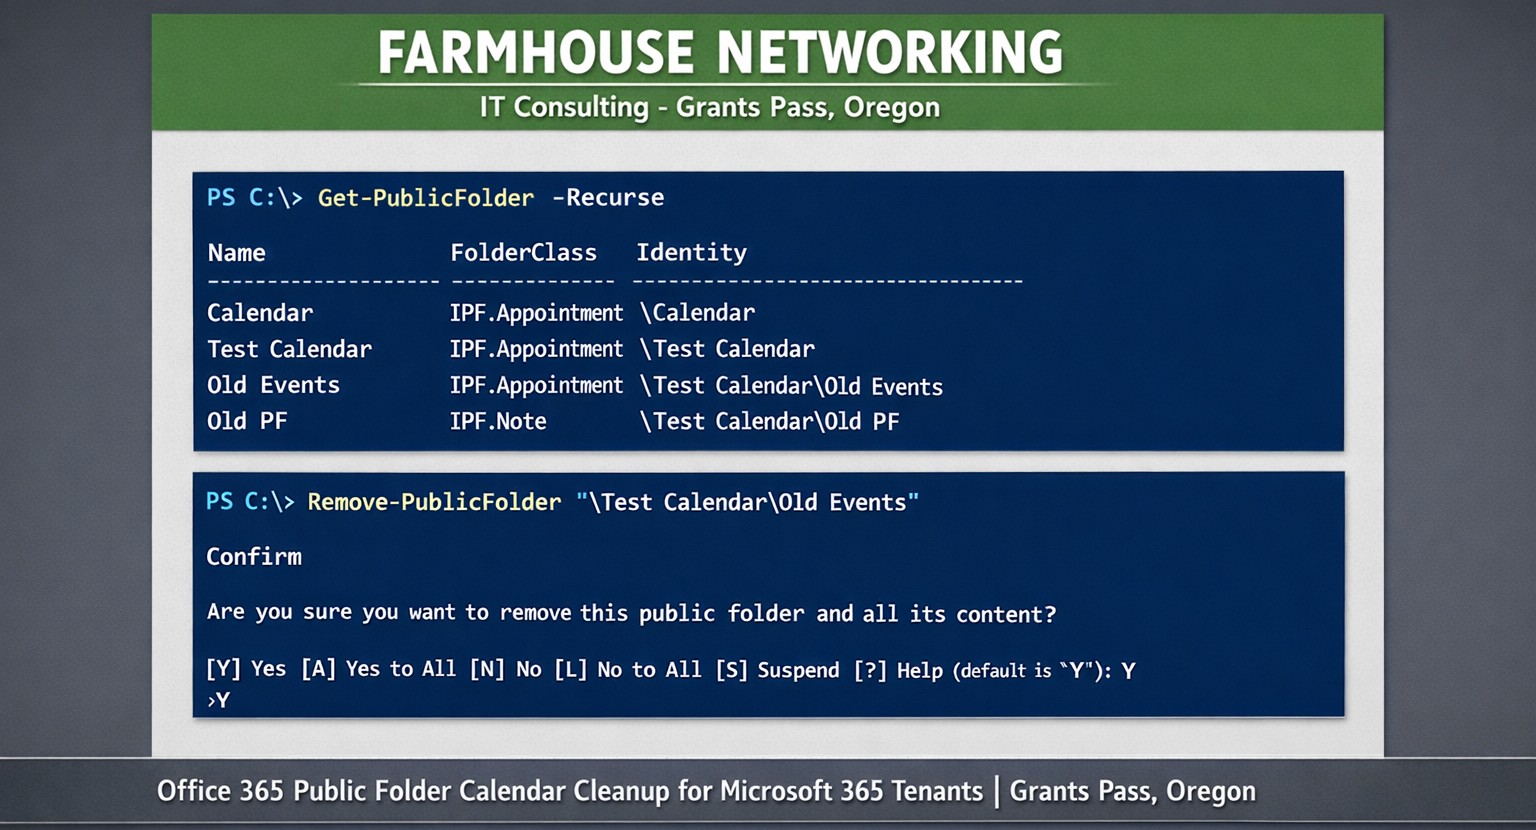
Farmhouse Networking uses PowerShell get-publicfolder -Recurse to locate and remove unwanted Office 365 public folder calendars for Grants Pass clients.
Here is a quick bit of Powershell that helped me to track down a “shared calendar” in a Co-Managed IT / Tier3 client’s Office 365 tenant. After looking in Shared Mailboxes and Resources for the calendar with no luck, we tried to get into the Exchange Management Console (EMC). The loading circle of death went on for an eternity, so switched to good old Powershell. Found the commands as follows after connecting to Exchange Online in Powershell:
If your company is looking for local management of your Office 365 tenant or need advanced support for your IT team, then contact us to find out how much you can save with us.
Farmhouse Networking helps businesses modernize their networks for faster performance, smarter automation, and secure connectivity.
The business world is moving at the speed of data. From cloud applications to video conferencing and smart devices, modern companies thrive on connectivity — and that means your network must be faster, more reliable, and intelligent enough to adapt. The days of “good enough” internet are gone. The next-generation network is faster, closer to your customers, and smarter in the way it predicts and manages performance.
Why “Faster, Closer, Smarter” Matters for Every Business Owner
A few years ago, network upgrades were viewed as an IT luxury. Today they’re a business necessity. Productivity, customer experience, and profit margins increasingly depend on how efficiently your systems communicate across multiple sites and cloud services.
Faster: Applications like video meetings, VoIP, and cloud storage demand low latency and high bandwidth. Slow connections mean lost opportunities.
Closer: Edge computing brings resources and data processing nearer to users, reducing lag and improving responsiveness for remote teams and mobile customers.
Smarter: Artificial intelligence (AI)–driven networks detect issues before they cause downtime, automatically direct traffic, and protect against cyber threats.
Business growth in 2020 and beyond will favor companies that embrace these technologies early — and that’s where proactive planning makes all the difference.
Action Steps for Business Owners and IT Teams
Modernizing your network doesn’t have to be complicated. Here are practical steps to future-proof your infrastructure:
Audit your current network. Identify bottlenecks, aging hardware, and underperforming Wi-Fi zones. Tools like traffic analyzers or managed network assessments can pinpoint areas for improvement.
Move critical workloads to the cloud wisely. Hybrid cloud environments balance flexibility and security — but only when configured with responsive bandwidth and monitored connections.
Invest in network automation and AI-based monitoring. Smart analytics help your IT team spot anomalies before employees notice performance issues.
Upgrade for speed and reliability. Fiber-optic connectivity, gigabit routers, and Wi-Fi 6 access points deliver measurable performance boosts.
Secure everything. With more connected devices comes more risk. Integrated firewalls, endpoint protection, and regular patch management are essential defenses.
Partner with a managed services provider (MSP). Outsourcing these functions ensures around-the-clock monitoring and proactive support so your internal staff can focus on core business priorities.
Common Client Questions — Answered
Q: “Is upgrading my network really worth the cost?” A: Absolutely. Slow or unreliable connectivity costs more in downtime and lost productivity than the upgrade itself. Modern networks reduce maintenance time, prevent outages, and improve customer satisfaction.
Q: “What about security? Doesn’t a smarter network mean more risk?” A: Actually, the opposite. With automated patching, real-time threat detection, and AI-powered monitoring, a smarter network significantly strengthens protection.
Q: “How do I know what network capacity I’ll need?” A: Your ideal bandwidth depends on your business applications, remote workers, and cloud services. A professional assessment from an MSP can provide accurate data and recommendations tailored to your growth goals.
How Farmhouse Networking Can Help
At Farmhouse Networking, we specialize in helping businesses modernize their IT infrastructure with practical, budget-conscious solutions. Whether you need a network assessment, faster connectivity, smart automation, or enhanced cybersecurity, our team brings years of expertise in network design, implementation, and ongoing support.
We work with local businesses to:
Audit existing network performance and identify inefficiencies.
Implement cloud and edge computing solutions.
Automate monitoring through intelligent network management tools.
Strengthen IT security to protect sensitive data and client trust.
Our mission is to make enterprise-grade technology accessible to your small or mid-sized business — keeping your network running faster, closer, and smarter than ever before.
Ready to Upgrade Your Network?
Don’t let outdated systems slow you down in 2020’s fast-moving digital economy. Future-proof your business with a smarter, more efficient network built for growth.
Email support@farmhousenetworking.com today to learn how Farmhouse Networking can help your business stay connected, secure, and competitive.
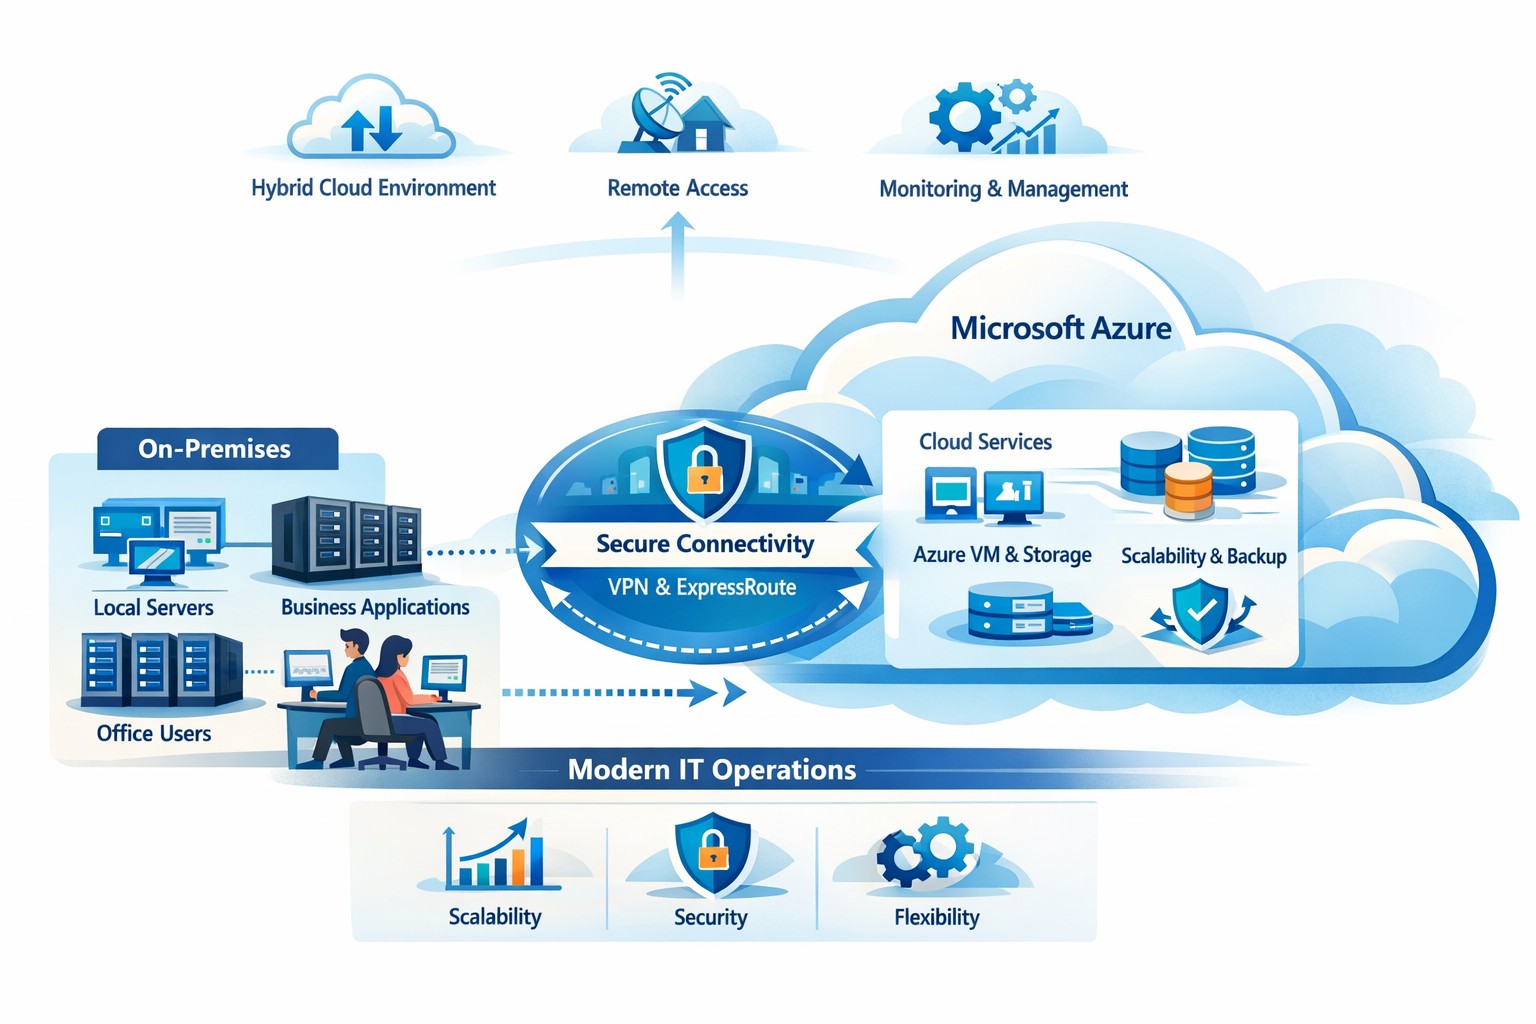
How your business can connect on‑premises servers and workloads to Microsoft Azure for scalable, secure, and compliant cloud computing
The cloud is no longer a “nice‑to‑have”—it’s the backbone of modern operations. Moving to Microsoft Azure gives you enterprise‑grade security, scalability, and cost control without the burden of managing your own data center. In this post, you’ll learn why the cloud matters, why Azure in particular is the right fit for many businesses, and—most importantly—how Farmhouse Networking can guide you through each step of the journey.
Why the cloud matters for your business
The cloud lets you turn capital‑heavy IT (servers, routers, on‑site backups) into a predictable operating expense. Instead of buying and maintaining hardware, you pay for what you use, when you use it. This model is especially powerful for companies with seasonal spikes, hybrid workforces, or plans to grow into new markets.
For business owners, the cloud means:
Lower upfront costs and easier budgeting.
Faster innovation and deployment of new tools or applications.
Built‑in disaster recovery and business continuity capabilities.
Azure, in particular, is trusted by 90% of Fortune 500 companies and offers a globally distributed, secure platform tightly integrated with familiar Microsoft tools like Microsoft 365, Entra ID, and Dynamics 365.
Why choose Microsoft Azure?
Azure stands out for three reasons relevant to owners and IT teams:
Security and compliance Azure provides enterprise‑level protection, identity management, and compliance certifications that small‑ and mid‑sized businesses can leverage without hiring a full‑time security team.
Scalability and flexibility You can scale compute, storage, and networking up or down in minutes—perfect for handling seasonal demand, new projects, or unexpected growth.
Seamless integration with Microsoft tools If your team already uses Microsoft 365, Teams, or Windows‑based applications, Azure simplifies integration and reduces complexity in permissions, patching, and remote access.
Practical steps for your business and IT team
Making the move to Azure doesn’t have to be disruptive. Here’s a realistic, phased roadmap:
Assess your current environment
Inventory servers, applications, and data.
Identify which workloads are good candidates for the cloud (e.g., file servers, backups, certain line‑of‑business apps). Farmhouse Networking can perform a free infrastructure assessment to help you classify and prioritize workloads.
Define your cloud strategy and goals
Decide what “success” looks like: better uptime, remote work support, cost savings, faster backups, etc.
Set a timeline (e.g., 6–18 months for a phased migration).
Start with low‑risk, high‑impact workloads
Migrate backups, archival storage, or non‑critical applications first.
Use Azure Backup and Azure Site Recovery to test disaster‑recovery scenarios without disrupting production.
Build identity and security foundations
Sync your on‑premises directories (or move entirely) to Microsoft Entra ID.
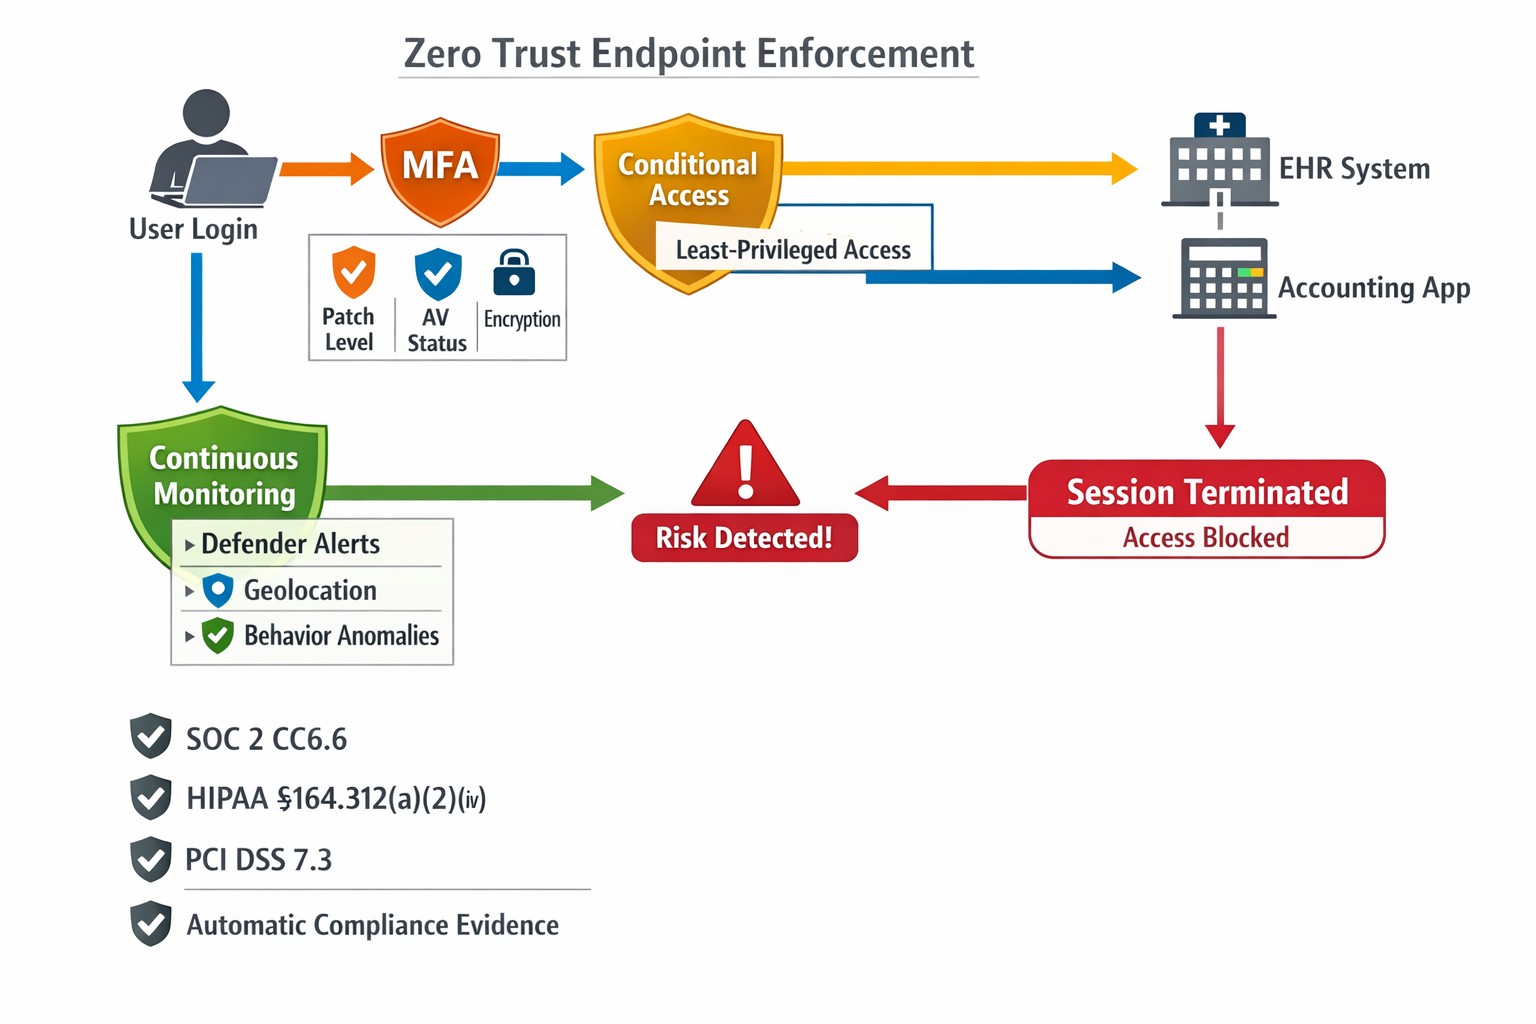
Implement multi‑factor authentication (MFA) and conditional access policies for remote users and admins. Farmhouse Networking can help design and deploy these policies with minimal friction for your team.
Train and support your internal team
Provide basic Azure operations training for your IT staff.
Set up monitoring dashboards so your team can track costs, performance, and security events.
Client questions and answers
Here are some typical questions business owners and clients might ask:
Q: Is the cloud really more secure than our own servers? A: When properly configured, Azure offers better security than most on‑premises environments, including advanced threat detection, encryption at rest and in transit, and continuous Microsoft‑led security updates. Azure also meets many industry‑specific compliance standards that can be difficult and expensive to maintain in‑house.
Q: Will migrating to Azure be expensive and disruptive? A: Migrations can be staged so core operations stay online. You shift from large capital investments to predictable monthly costs, and you often achieve savings by retiring aging hardware and consolidating tools. A phased approach, with Farmhouse Networking managing the planning and execution, keeps disruption low.
Q: What happens if we need to move back on‑premises someday? A: Azure supports hybrid scenarios, so you can keep some workloads on‑site and others in the cloud. Azure’s hybrid tools (such as Azure Stack, VPNs, and ExpressRoute) make it possible to move workloads back or between environments as business needs change.
How Farmhouse Networking can help
Farmhouse Networking acts as your strategic partner for cloud adoption, not just a vendor. We help you:
Conduct a current‑state assessment and build a tailored Azure roadmap aligned with your growth goals.
Manage the technical migration with minimal disruption to your team and clients.
Implement security, governance, and monitoring so you retain control while Azure does the heavy lifting.
By partnering with us, you get a clear, documented plan and ongoing support—so you can focus on running your business while your systems stay secure, available, and scalable.
Ready to explore Azure for your business?
If you’re wondering whether the cloud—and specifically Microsoft Azure—is the right fit for your organization, let’s start the conversation. Email us at support@farmhousenetworking.com to schedule a consultation, and we’ll walk through your current environment, your goals, and a practical next step toward a smarter, more resilient IT foundation.
And God will generously provide all you need. Then you will always have everything you need and plenty left over to share with others. As the Scriptures say, “They share freely and give generously to the poor. Their good deeds will be remembered forever.” For God is the one who provides seed for the farmer and then bread to eat. In the same way, he will provide and increase your resources and then produce a great harvest of generosity in you. - 2 Corinthians 9:8-10
We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.