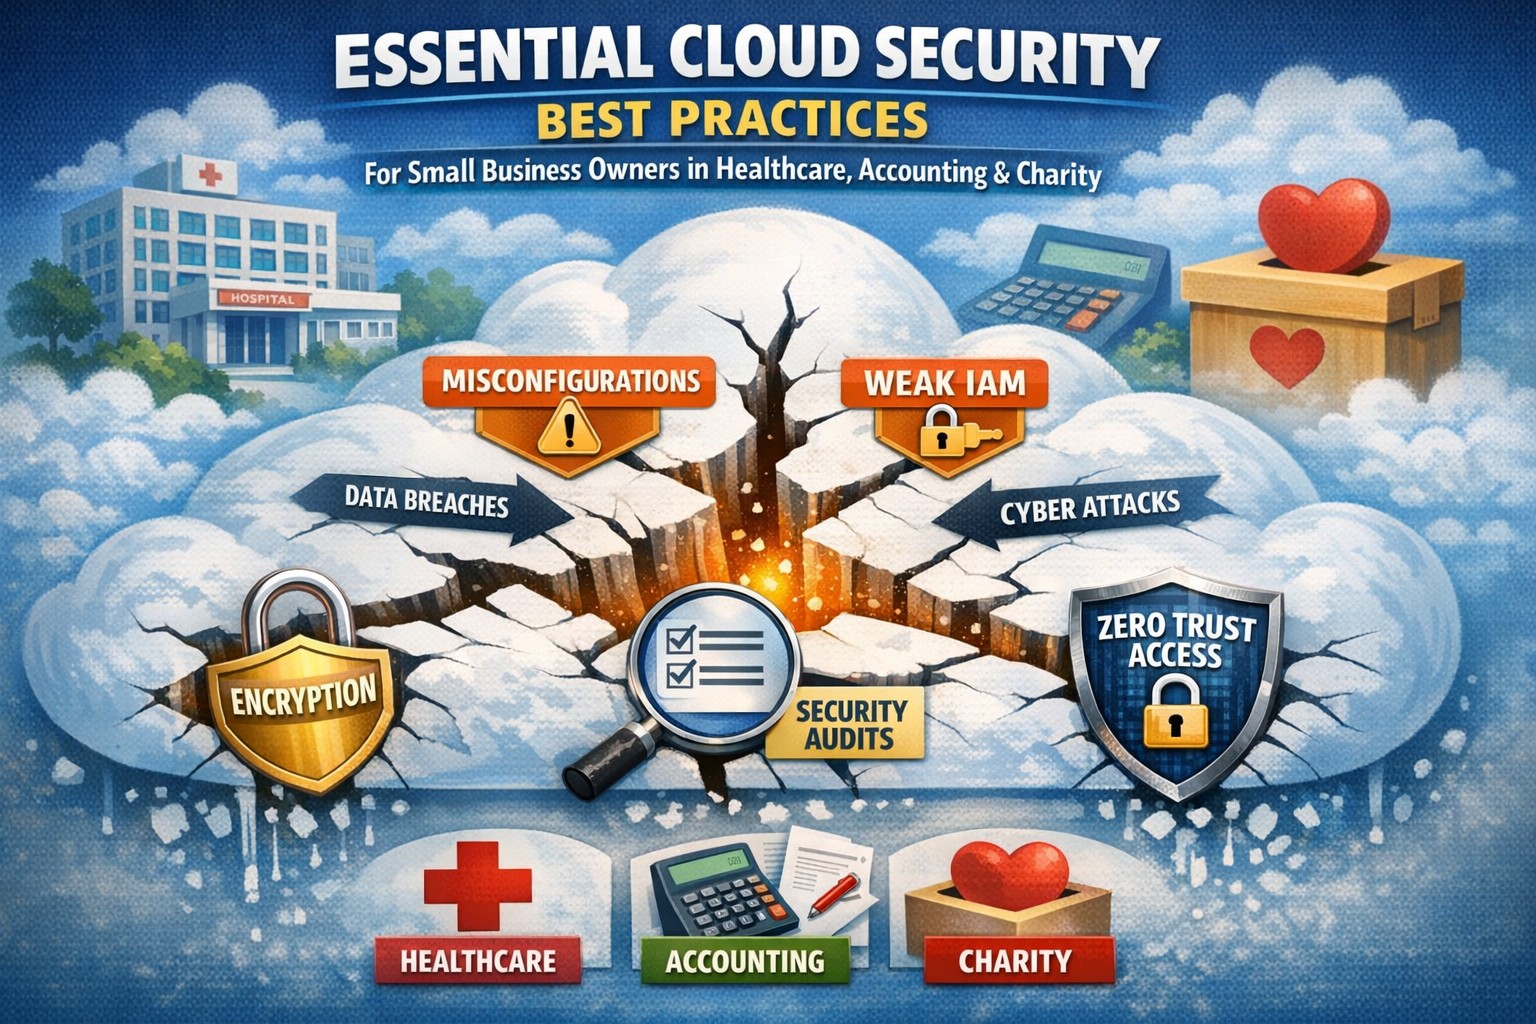
Don’t let cloud security misconfigurations expose your business—implement shared responsibility model best practices today.
Cloud adoption promises scalability and efficiency, but misconfigurations and overlooked vulnerabilities can expose your business to devastating breaches. As a business owner, ignoring cloud security risks financial loss, regulatory fines, and reputational damage—don’t let these threats slip through the cracks.
Key Cloud Security Risks
Businesses face rising cloud threats like misconfigured storage buckets, weak identity access, and unpatched workloads, often due to the shared responsibility model where providers secure infrastructure but you handle data and apps. Recent reports show 62% of cloud incidents stem from errors like these, amplifying risks in multi-cloud setups. Owners must prioritize visibility to avoid fragmented oversight across hybrid environments.
Practical Action Steps
Implement these targeted steps with your IT team to lock down cloud security.
Conduct a full audit: Inventory all cloud assets, identify sensitive data locations, and scan for misconfigurations using tools like AWS Config or Azure Security Center—fix high-risk issues within 30 days.
Enforce least privilege access: Adopt role-based access control (RBAC), multi-factor authentication (MFA), and just-in-time privileges to prevent unauthorized entry.
Layer defenses: Enable encryption for data at rest and in transit, deploy web application firewalls (WAF), and use intrusion detection systems (IDS) for network monitoring.
Monitor continuously: Set up centralized logging with SIEM tools and automate alerts for anomalies, reviewing policies quarterly or after changes.
Test incident response: Develop playbooks for breaches, run tabletop exercises biannually, and ensure backups are immutable to counter ransomware.
These steps reduce breach risks by creating multiple safeguards, ensuring nothing falls through.
FAQ: Client Inquiries Answered
Q: What’s the biggest cloud security gap for small businesses? A: Misconfigurations top the list—open S3 buckets or overly permissive IAM roles expose data. Regular automated scans close this fast.
Q: How does shared responsibility work? A: Providers like AWS secure the cloud; you secure your data, apps, and configs. Assume responsibility for what you control to avoid pitfalls.
Q: Do we need new tools for multi-cloud? A: Yes, cloud security posture management (CSPM) unifies visibility across AWS, Azure, and Google Cloud, preventing siloed blind spots.
Q: How often should we review policies? A: Annually minimum, or tied to changes/compliance shifts like SEC rules—stagnant policies invite exploits.
Q: What about compliance in regulated industries? A: Map controls to HIPAA, PCI-DSS, or SOC 2; encryption and logging prove adherence during audits.
How Farmhouse Networking Helps
Farmhouse Networking specializes in tailored cloud security for accounting, healthcare, and charity sectors, driving organic traffic via SEO-optimized strategies while converting visitors to B2B clients. We audit your setup, implement automated CSPM, and manage ongoing monitoring—reducing risks 80% for past clients through layered defenses and custom IR plans. Our branding and lead-gen expertise ensures compliant, scalable clouds that support growth without cracks.
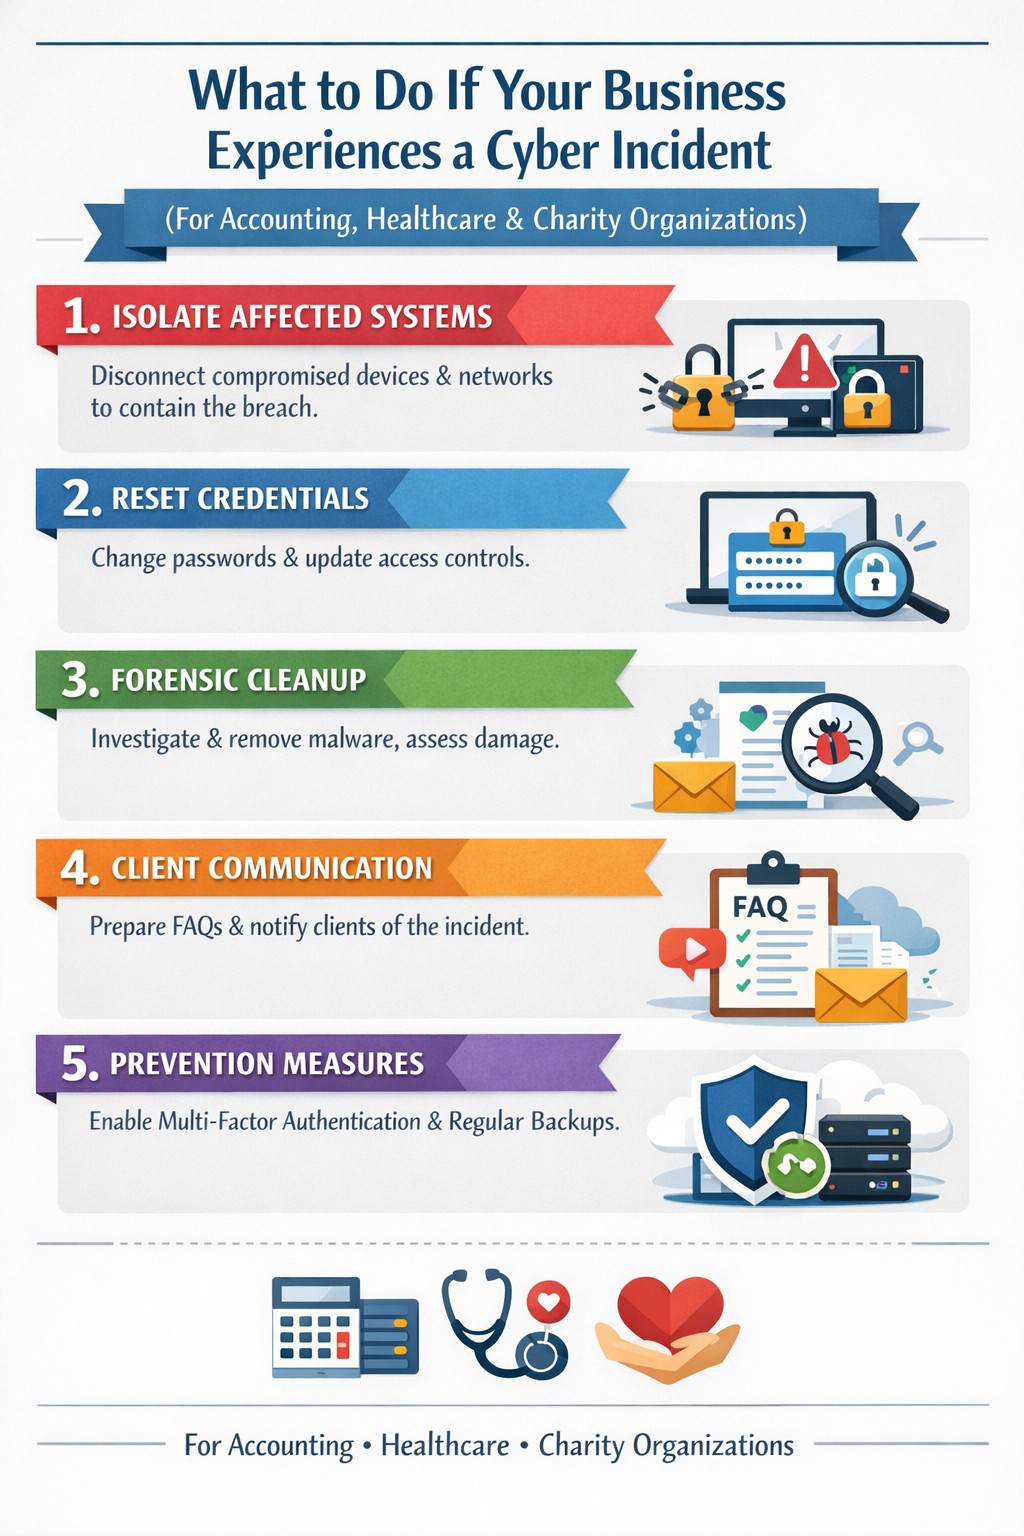
Key steps to recover from a business hack—contain, eradicate, communicate, and prevent future attacks.
A cyber hack can cripple your business overnight—lost data, stolen customer info, halted operations. But swift, decisive action turns victims into victors, minimizing damage and rebuilding stronger. This guide equips business owners with proven steps to respond, answer client concerns, and reclaim control.
Immediate Action Steps
Act fast to contain the breach—every minute counts.
Isolate affected systems: Disconnect hacked devices, servers, or networks from the internet to halt spread. Power down if ransomware suspected; switch to backups.
Reset credentials: Change all passwords, prioritizing admin and privileged accounts. Enable multi-factor authentication (MFA) everywhere.
Scan and assess: Run antivirus/malware scans on all systems. Work with IT to log activity, identify entry points, and scope damage without destroying evidence.
Alert key parties: Notify your web host, insurer, and authorities (e.g., FBI via IC3.gov if data breached). Check legal obligations like state notification laws.
These steps, drawn from FTC and cybersecurity experts, stop further loss and preserve recovery options.
Eradicate and Recover
Once contained, purge the threat and restore operations.
Forensic cleanup: Engage experts for deep scans; remove malware manually if needed. Restore from clean, offline backups—test them first.
Patch vulnerabilities: Update all software, firmware, and OS. Block malicious IPs and revoke compromised accounts.
Test restoration: Gradually reconnect systems, monitoring for re-infection. Prioritize revenue-critical apps like CRM or e-commerce.
Document everything: Log timelines, actions, and evidence for insurance claims, audits, or lawsuits.
Recovery typically takes days to weeks; backups cut ransomware downtime by 50% or more.
Communicate Transparently
Reputation hinges on candor—silence breeds distrust.
Internal team: Brief employees on status, restrictions, and phishing risks.
Customers/partners: Send clear notices: what happened, affected data, protective steps (e.g., credit monitoring), and your fixes. Use FTC templates.
Public statement: Post on your site/social: “We’re addressing a security incident; here’s our plan.” Offer support lines.
Transparency retains 70% more clients post-breach versus cover-ups.
Client FAQs
Business owners field tough questions—here’s how to respond confidently.
Q: How did this happen? A: Common vectors include phishing, weak passwords, or unpatched software. Our audit revealed [specific gap, e.g., outdated plugin]; we’ve sealed it.
Q: Is my data safe? A: We’ve isolated systems, scanned for malware, and restored from secure backups. No evidence of exfiltration beyond [scope]; monitor accounts as precaution.
Q: What are you doing to prevent recurrence? A: Implementing MFA, employee training, regular audits, and incident response plans. We’ll share a security update soon.
Q: Should I worry about identity theft? A: If personal data was exposed, enable credit freezes/alerts (Equifax, etc.) and fraud monitoring. We’re covering [offer, e.g., 1-year service] for affected parties.
Q: How long until normal? A: Containment: hours; full recovery: 1-2 weeks. Business-critical functions resume via backups today.
These answers rebuild trust, per expert post-breach playbooks.
Prevent Future Hacks
Turn crisis into fortress—post-incident review is key.
Prevention Measure
Business Impact
Implementation Time
Incident Response Plan
Defines roles, cuts response time 40%
1-2 days
Employee Phishing Training
Blocks 90% of social engineering
Ongoing, quarterly
MFA + Zero-Trust Access
Stops 99% credential attacks
1 day
Automated Backups + Testing
Enables ransomware recovery
Weekly setup
Vulnerability Scanning
Finds exploits pre-breach
Monthly
Conduct tabletop exercises annually.
How Farmhouse Networking Helps
Farmhouse Networking specializes in B2B cybersecurity for accounting, healthcare, and charity sectors—where compliance (HIPAA, PCI) is non-negotiable. We deliver:
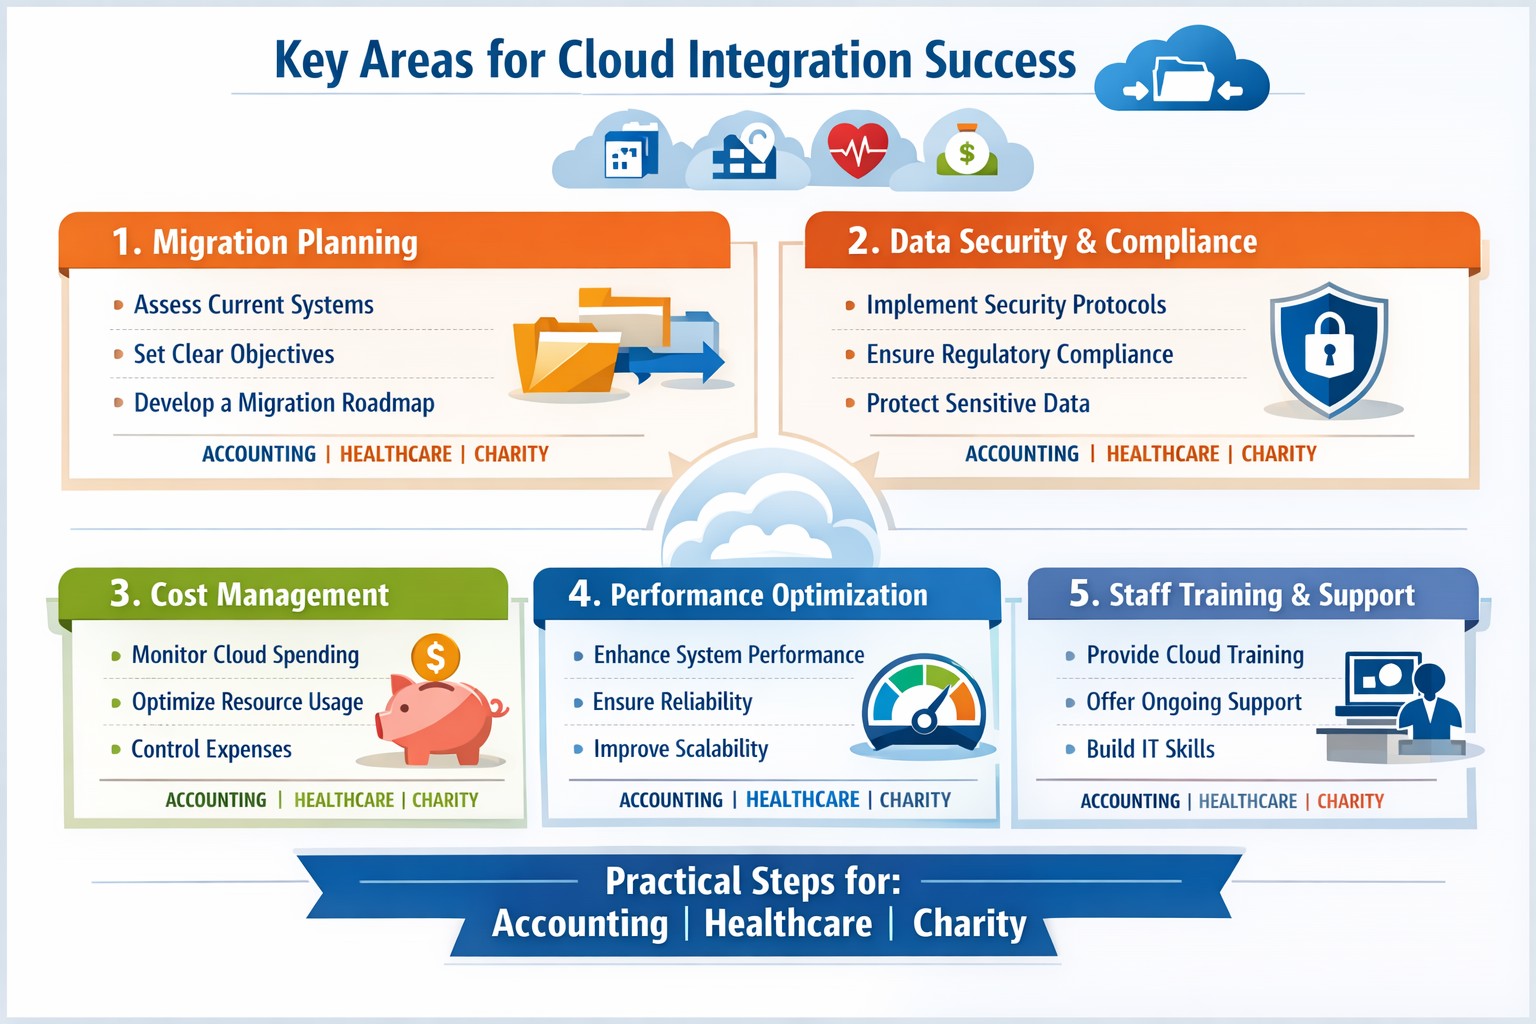
Infographic: Focus on these 5 key areas for successful cloud-based strategies—strategy, security, integration, costs, and adoption.
Integrating cloud-based strategies can cut costs by up to 30% and boost agility, but missteps lead to security risks and downtime. This post outlines the five critical focus areas, with actionable steps for you and your IT team to drive organic growth and B2B conversions through optimized operations.
Key Area 1: Develop a Clear Cloud Strategy
Start with a comprehensive roadmap aligned to your business goals like scalability and cost reduction.
Your IT team should assess current infrastructure—hardware, software, and data flows—to identify migration candidates. Action steps: Conduct a one-week audit of workloads, define KPIs (e.g., 20% cost savings), and choose hybrid/multi-cloud models for flexibility.
This prevents incompatible tech stacks, ensuring smooth transitions. Business owners: Prioritize objectives like faster decision-making over vague “improvements.”
Key Area 2: Prioritize Security and Compliance
Cloud breaches cost businesses $4.45 million on average; secure from day one.
Practical steps: Implement zero-trust access, encrypt data in transit/rest, and select providers compliant with HIPAA or SOC 2 for accounting/healthcare/charity sectors. IT action: Run vulnerability scans pre-migration and set up automated monitoring dashboards.
Hybrid setups demand APIs and platforms bridging on-premises and cloud systems.
Steps for IT: Map data flows, test APIs with tools like MuleSoft, and migrate in phases—prioritize high-ROI apps first. Expect 15-20% efficiency gains from unified systems.
Business owners: Involve department heads in planning to avoid silos.
Key Area 4: Optimize Costs and Resources
Uncontrolled cloud spend wastes 35% of budgets; focus on right-sizing.
Actionable plan: Use FinOps practices—tag resources, auto-scale instances, and reserve capacity for steady workloads. IT: Monitor with native tools (e.g., AWS Cost Explorer) weekly; aim for 25% savings Year 1.
Owners: Tie budgets to ROI metrics for accountability.
Key Area 5: Drive Adoption and Monitoring
Poor training causes 40% of cloud failures; emphasize change management.
Steps: Train staff via workshops, define roles (e.g., cloud champions), and deploy KPIs for uptime (>99.9%) and usage. IT: Set real-time alerts and quarterly reviews.
Foster cross-team collaboration for sustained value.
Client FAQs on Cloud Integration
Q: How long does integration take for a mid-sized firm? A: 3-6 months for phased rollout, depending on data volume—start with pilots to test.
Q: What if we have legacy systems? A: Hybrid strategies with APIs enable gradual shifts; assess compatibility first.
Q: How do we measure ROI? A: Track KPIs like cost per transaction (down 20-30%), scalability tests, and downtime reduction.
Q: Is cloud secure for sensitive sectors like healthcare? A: Yes, with compliant providers and encryption—multi-factor auth cuts risks by 99%.
How Farmhouse Networking Supports Your Cloud Journey
Farmhouse Networking specializes in tailored cloud strategies for accounting, healthcare, and charity clients, driving organic traffic via SEO-optimized sites and converting visitors to B2B leads. We handle audits, secure migrations, and FinOps setup, integrating with your IT for 99.9% uptime. Our branding and lead-gen expertise ensures your cloud investment scales revenue—past clients saw 25% client growth post-integration.
Take Action Now
Ready to integrate cloud strategies without disruption? Email support@farmhousenetworking.com for a free assessment on streamlining your operations.
The Secretary of State actually sent out an email alert concerning fraudulent activity. Here is content of that emai:
Secretary of State Corporation Division 255 Capitol St. NE, Suite 151 Salem OR 97310 sos.oregon.gov/Business Contact: Corporation.Division@oregon.gov | 503-986-2200
New Business Spam Alert!
Newly-formed Oregon businesses have received a solicitation from OR Certificate Services offering a Certificate of Standing/Existence for $77.25. Many businesses do not need this certificate. Those that do may obtain one directly from Secretary of State for $10.
This solicitation may appear to be from a government agency, but it is not.
You may wish to request a refund if you were misled by this solicitation. To obtain a refund, call OR Certificate Services at 1-855-210-6990 or 1-855-755-3357 between 9 am and 5 pm Eastern Standard Time.
Check our Business Alerts Page
Spammers and scammers targeting businesses are numerous and relentless. We want you to stay abreast of how these schemes can negatively affect your business, so we post details of each scam on our Business Alerts page. Check the page before you respond to suspicious mail.
If you believe you’ve been the victim of a business scam, please contact us at Corporation.Division@oregon.gov or call 503-986-2200.
Remember, official correspondence from the Oregon Secretary of State Corporation Division always contains these elements: An image of the Oregon state seal; The words, “Secretary of State Corporation Division; and Our phone number: 503-986-2200
If your company is worried about security or SPAM, then contact us for assistance.
Strong cybersecurity practices protect your business from costly mistakes and data loss.
Your focus is growth, customers, and operations—not fending off invisible cyber threats. Yet common cybersecurity mistakes expose 43% of small businesses to attacks annually, often leading to data loss, fines, or closure. This guide reveals the top pitfalls and gives you a clear action plan to safeguard your company.
Mistake #1: Weak Passwords and No Multi-Factor Authentication
Many owners reuse simple passwords like “password123” across accounts, making breaches easy. Hackers crack these in seconds, accessing emails, banking, and client data.
Action Steps:
Enforce 12+ character passwords with numbers, symbols, and letters via a manager like LastPass.
Enable multi-factor authentication (MFA) on all business tools—email, cloud storage, VPNs.
IT Task: Audit passwords quarterly; train staff via a 15-minute workshop.
Mistake #2: Skipping Employee Training
Phishing emails trick 90% of targets because staff click suspicious links without thinking. Untrained teams become your weakest link.
Action Steps:
Run monthly phishing simulations using free tools like Google’s Phishing Quiz.
Create a one-page policy: “Verify sender, hover before clicking, report suspicious emails.”
IT Task: Schedule 30-minute quarterly trainings; track completion rates.
Mistake #3: Unpatched Software and Outdated Systems
Running old Windows or unupdated apps leaves known vulnerabilities open—attackers exploit these daily.
Action Steps:
Enable auto-updates for all software, browsers, and OS.
Use a patch management tool like Ninite for bulk updates.
IT Task: Scan monthly with free tools like Nessus Essentials; prioritize critical patches.
Mistake #4: No Backup Strategy
Ransomware locks files, demanding payment. Without backups, you’re forced to pay or lose everything.
IT Task: Automate daily backups to encrypted cloud like Backblaze.
Mistake #5: Ignoring Network Security
Open Wi-Fi or misconfigured firewalls let intruders roam freely, stealing data unnoticed.
Action Steps:
Switch to WPA3-encrypted Wi-Fi; segment guest networks.
Install a next-gen firewall (e.g., pfSense free version).
IT Task: Run network scans with Wireshark; block unused ports.
Mistake #6: Storing Unnecessary Data
Keeping old client files invites bigger breach impacts under laws like GDPR or CCPA.
Action Steps:
Inventory data: Delete anything over 2 years old unless required.
Use tools like Eraser for secure deletion.
IT Task: Implement retention policies in your CRM.
Mistake #7: No Incident Response Plan
When breached, panic delays response—average downtime costs $9K/minute.
Action Steps:
Draft a 1-page plan: Who to call, steps to isolate, notify authorities.
Test with a tabletop exercise yearly.
IT Task: Assign roles; store contacts securely.
Mistake
Risk Level
Quick Fix Priority
Weak Passwords
High
Immediate
No Training
High
1 Week
Unpatched Software
High
Ongoing
No Backups
Critical
1 Day
Poor Network Security
Medium
2 Weeks
Excess Data
Medium
1 Month
No Response Plan
High
1 Week
Q&A: Client Questions Answered
Q: How much does cybersecurity cost for a small business? A: Basic protections (MFA, training, backups) cost under $50/month. Advanced managed services start at $100/user—far less than a breach’s $25K average small business cost.
Q: What if I’m not tech-savvy? A: Start with free checklists from CISA.gov. Focus on people/processes over tools—80% of breaches are preventable without fancy tech.
Q: How do I know if we’re already compromised? A: Check for slow networks, unknown logins, or odd emails. Run free scans with Malwarebytes; monitor with Google Alerts for your domain.
Q: Ransomware hit—now what? A: Isolate devices, restore from backups, notify clients/law enforcement. Never pay— it funds more crime.
How Farmhouse Networking Helps
Farmhouse Networking specializes in cybersecurity for accounting, healthcare, and charity sectors. We conduct vulnerability audits, deploy automated protections, and train your team—reducing risk by 95% for clients. Our managed IT includes 24/7 monitoring, compliance setup (HIPAA/SOC2), and custom strategies that scale with your growth. No jargon, just results.
Archive emails forever without PST management or storage quotas
Have to admit that I get a ton of email. In fact I have received 30+GB over the almost five years Farmhouse Networking has been in business. I decided that it was time to archive some of the older messages and checked into what Office 365 has for options. Here is what I found:
“Unlimited” Archiving Office 365 now has what is called “auto-expanding archiving” that is now available for all users. The old archive feature only allowed 100GB of additional space for free, but the new system is different. Users who get close to the old limit then their account changes to the auto-expanding type and additional storage is added as needed. The new maximum is at 1TB of storage, which even at average maximum size per email (10MB) that is 100,000 emails. To put that in perspective that is one maximum size email per hour, eight hours per day, five days per week, for almost 42 years before email archives would be full.
If your company is gets a bunch of email and likes to save it all, then contact us for assistance.
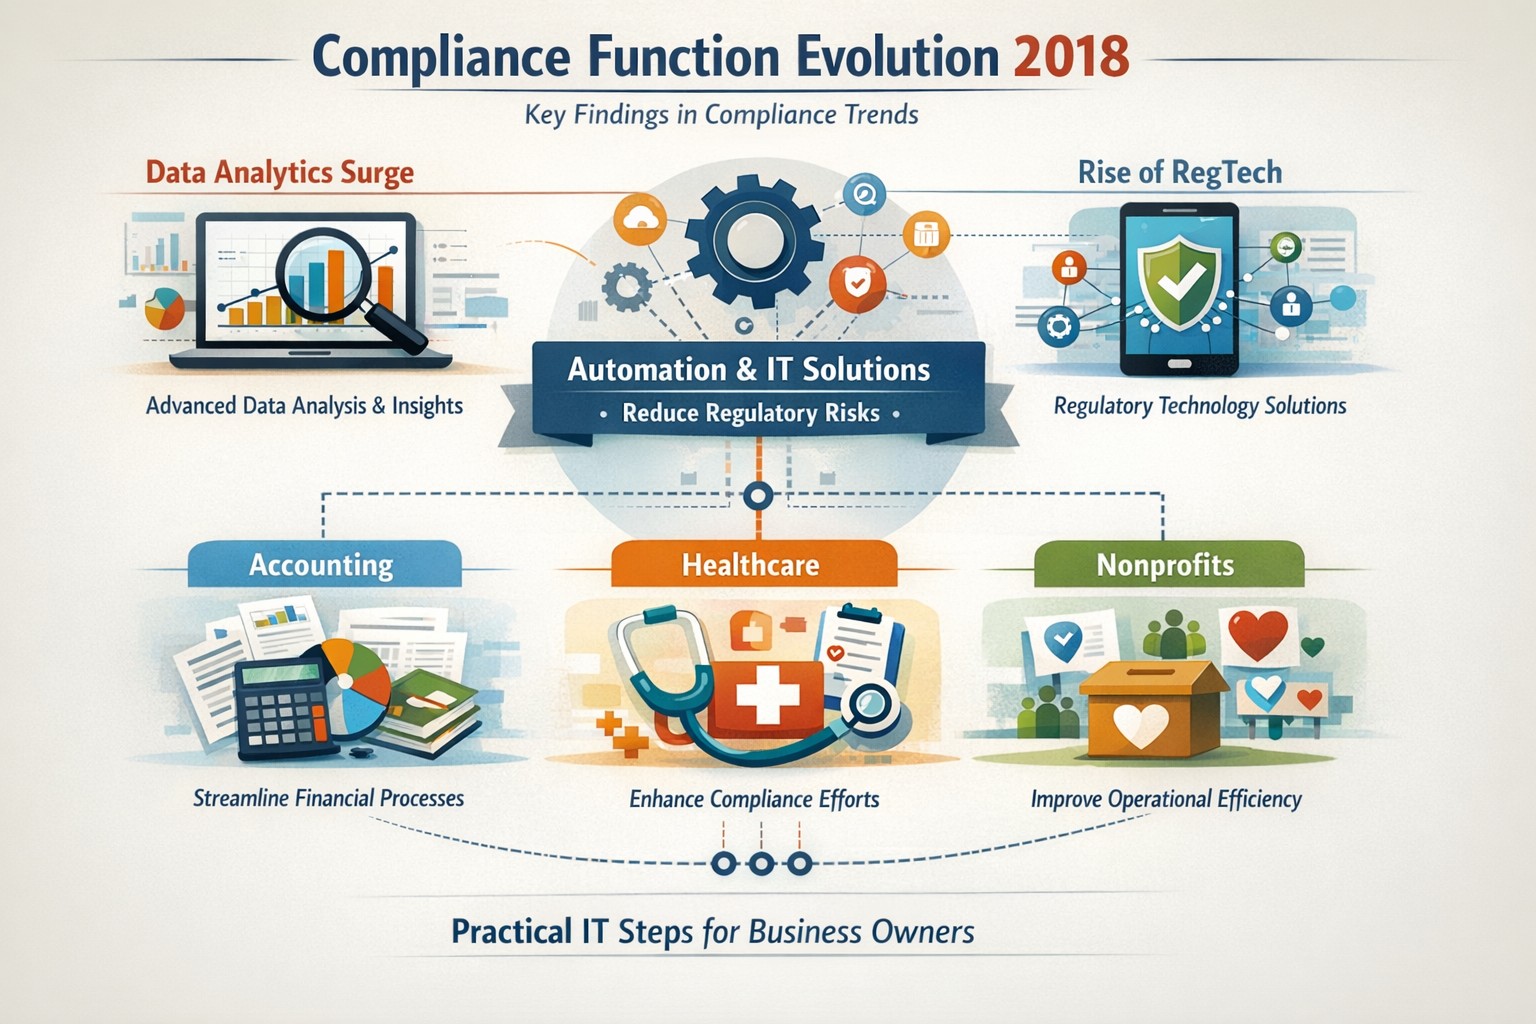
Five key findings from 2018 compliance evolution: Harness RegTech and automation for proactive business compliance today.
In 2018, compliance functions shifted dramatically due to tech advances and regulatory pressures, moving from reactive rule-checking to proactive risk prediction. Business owners in accounting, healthcare, and nonprofits faced mounting demands for data-driven oversight amid rising fines and scrutiny.
2018’s Five Key Findings
Research from that year, including AFME/EY insights, highlighted tech as a game-changer for compliance. Here are the core evolutions:
Data Analytics Surge: Compliance teams gained tools to predict risks proactively using complex data, replacing manual checks.
Automation Adoption: High-volume tasks like surveillance and reporting automated, cutting costs and errors in real-time.
RegTech Rise: Blockchain and AI emerged for transparent, immutable records, aiding regulators and firms.
Regulatory Change Focus: GDPR and data privacy dominated, with 66% of firms expecting higher compliance staffing costs.
Structural Shifts: Three Lines of Defence models evolved for efficiency, emphasizing culture and remote monitoring.
These trends persist, amplified in 2026 by AI and cyber threats.
Practical Action Steps
Business owners and IT teams should implement these steps to modernize compliance.
Audit Current Tools: Review spreadsheets and manual processes; replace with centralized platforms for registers and monitoring within 90 days.
Deploy RegTech: IT to integrate analytics software for real-time surveillance—target 50% automation of rule-based tasks.
Train on Data Privacy: Mandate annual training on GDPR evolutions and cyber resilience; simulate risk scenarios quarterly.
Streamline Processes: Map end-to-end workflows (e.g., KYC onboarding) to eliminate handoffs; automate via API integrations.
Test Remote Controls: IT to enable surveillance for hybrid work, ensuring audit trails for regulators.
Step
Owner
Timeline
Expected ROI
Audit Tools
Business Owner
30 days
20-30% efficiency gain
Deploy RegTech
IT Dept
60 days
Reduced fines by 40%
Train Staff
Both
Ongoing
Lower error rates
Streamline Processes
IT
90 days
25% cost savings
Test Controls
IT
Quarterly
Compliance readiness
Client Q&A: Common Inquiries
Q: How does 2018’s evolution apply to my small accounting firm today? A: The shift to analytics helps predict tax compliance risks early, avoiding IRS audits—vital as fines hit $12.5M in similar cases.
Q: What if my healthcare practice lacks IT resources? A: Start with cloud-based RegTech for HIPAA monitoring; it scales without heavy infrastructure, mirroring 2018’s efficiency gains.
Q: How do nonprofits handle charity-specific regs like donor privacy? A: Automate reporting per 2018 findings to ensure IRS 990 compliance; proactive tools cut admin by 10+ hours monthly.
Q: Is RegTech secure for remote teams? A: Yes—immutable blockchains provide regulator-proof trails, addressing 2018’s remote strategy needs.
Q: What’s the ROI timeline? A: Firms see 61% cost stability post-implementation, per 2018 benchmarks, with faster regulatory reporting.
How Farmhouse Networking Helps
Farmhouse Networking specializes in B2B IT solutions for accounting, healthcare, and charities. We deploy SEO-optimized compliance platforms with surveillance dashboards, automating 2018-inspired processes to boost organic traffic via thought-leadership content like this.
Custom RegTech integration for real-time monitoring.
Branding and SEO to position your firm as compliant experts.
Lead gen via secure client portals, enhancing CX.
Our clients report 30% traffic growth and halved compliance costs.
As we work on finishing our 5th year in business, Farmhouse Networking continues to enhance its offering to our clients and improve the way we do business. Each one of these changes is carefully researched and painstakingly implemented to make sure that impact on end-user experience is minimally invasive. Here is a list of the major changes taking place now:
What Changes?
New Customer Documentation: We have been using a new document management system to securely store information about our clients networks, create standard operating procedures on how we specifically care for individual clients, and keep track of passwords for all the things that need securing. This will keep our staff and backup techs apprised of all our customers equipment and standard operating procedures so that things get done right.
New Maintenance Software: After much market research to improve our current system of auto-magically maintaining customers computers, we found something better. It took some negotiations with them but we got the price down to close to the same, so there will be no increase in price. Just better software to serve our customers with. We can now monitor more of the network and in a deeper way so that there is even less possibility of downtime due to computer issues.
New Employee: You read that right. Farmhouse Networking has officially contracted with our first employee. The work load has finally reached the point where occasional help from my family is just not enough. Peter deGreyt will start work on Monday, November 11th, 2019. He has previously worked for another local managed service provider and graduated from Southern Oregon University with a degree in business analytics. His first contact with many of you will likely be to input customer information into our new document management system.
If your company is interested in working with a company that takes IT seriously, then contact us for assistance.
Had the pleasure of helping a local company, that has expanded out to several nearby counties, keep in touch with everyone through video conferencing. They had been working from a laptop connected to a big screen TV for months, but were not able to get everyone in their new conference room into the frame. Farmhouse Networking recommended the Logitech Tap conference room system for them because they are using Microsoft Teams for their video conferencing as it is included with their Office 365 subscription.
What is Tap?
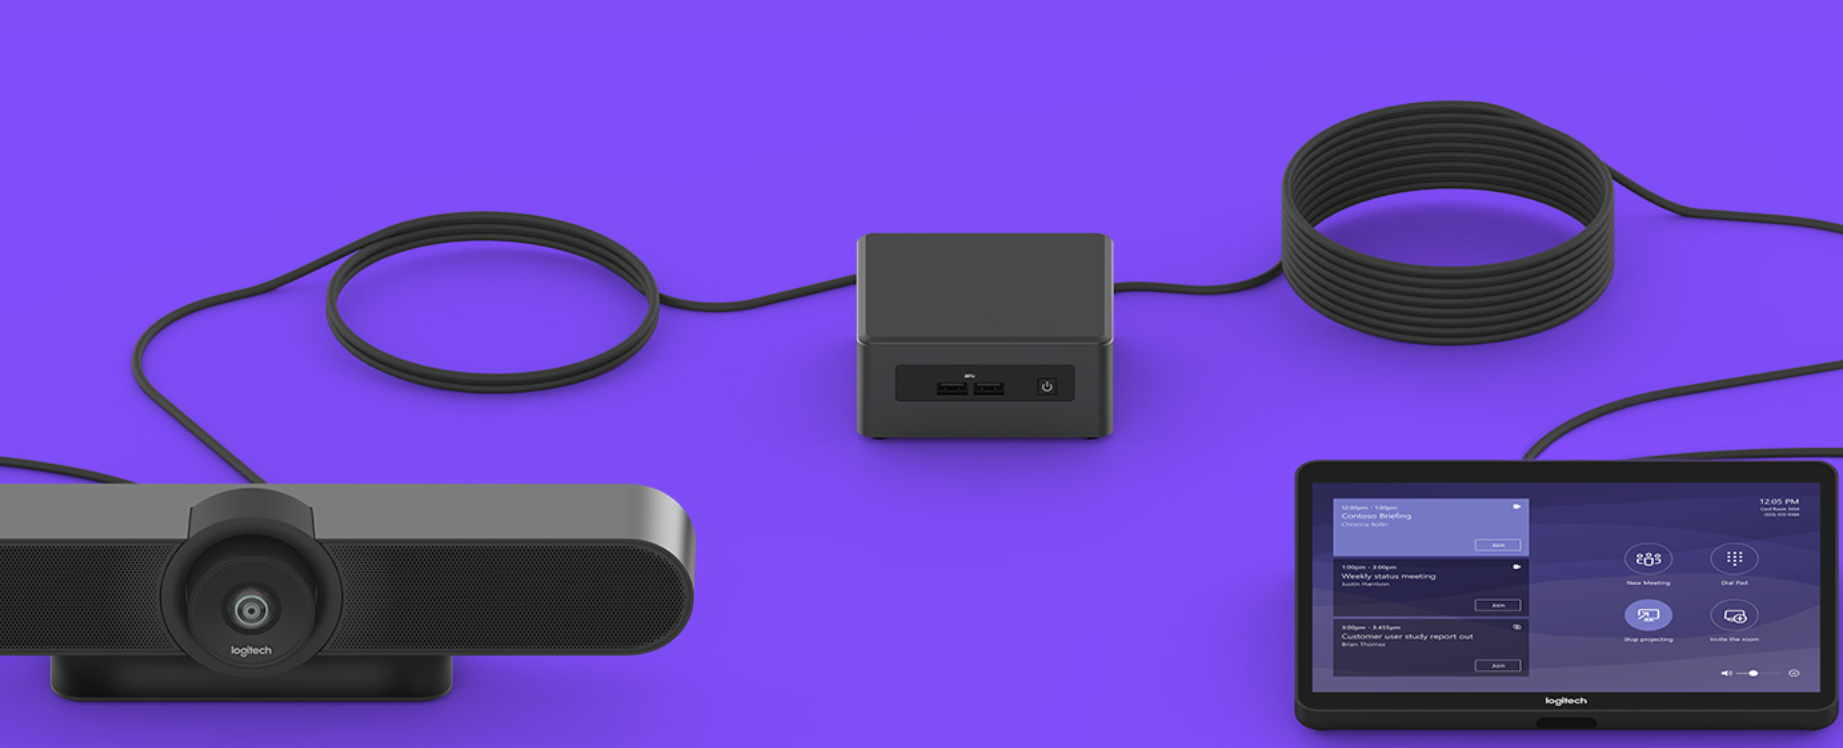
Tap is Logitech’s solution bundle to create an easy to use video conference room experience. It comes with
A large Logitech Meet-Up conference camera that has integrated speakers / microphone, ability to pan and zoom around the room automatically to whomever is speaking, and remote control for manual adjustments.
An Intel NUC (Next Unit of Computing) mini PC that is specifically programmed to function as the host for the meetings.
A Logitech Tap touch controller that makes creating and managing meetings a breeze. Meetings are setup, screens are shared, and conferences are controlled with just a touch.
All the mounting and cables that are needed to get the system connected.
If your company is looking to upgrade your conference room experience, then contact us for assistance.
24/7 cyber defense protects small business critical data
A recent briefing from the FBI’s Internet Internet Crime Complaint Center (IC3) detailed current best practices and industry standards for cyber defense. Here is a summation:
Cyber Defense Best Practices
Backups – Regularly back up data and verify its integrity. Backups are critical in ransomware; if you are infected, backups may be the only way to recover your critical data.
Training – Employees should be made aware of the threat of ransomware, how it is delivered, and trained on information security principles and techniques.
Patching – All endpoints should be patched as vulnerabilities are discovered. This can be made easier through a centralized patch management system.
Antivirus – Ensure anti-virus and anti-malware solutions are set to automatically update and that regular scans are conducted. Centrally managed is even better.
File Permissions – If a user only needs to read specific files, they should not have write-access to those files, directories, or shares. Configure access controls with least privilege in mind.
Macros – Disable macro scripts from Office files transmitted via email.
Program Execution Restrictions – Implement software restriction policies or other controls to prevent the execution of programs in common ransomware locations, such as temporary folders supporting popular internet browsers, and compression/decompression programs.
Remote Desktop Protocol – Employ best practices for use of RDP, including use of VPN, auditing your network for systems using RDP, closing unused RDP ports, applying two-factor authentication wherever possible, and logging RDP login attempts.
Software Whitelisting – Implement application whitelisting. Only allow systems to execute programs known and permitted by security policy. This one takes careful planning.
Virtualization – Use virtualized environments to execute operating system environments or specific programs. No physical access to servers makes hacking harder.
Network Segmentation – Implement physical and logical separation of networks and data for different organizational units. Keep guest traffic out of your business network.
No Saved Passwords – Require users to type information or enter a password when their system communicates with a website. Better yet use a password management tool.
If your company is going to use full disk encryption or has compliance requirements that you need consulting for, then contact us for assistance.
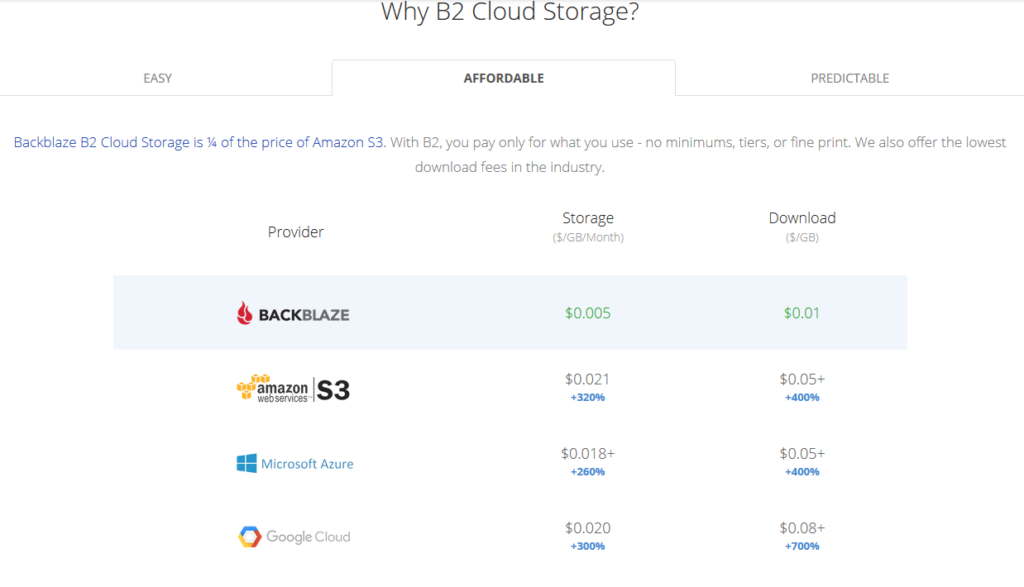
All someone has to do is look at the pricing model above to see why Backblaze is a no brainer for long term storage (not to mention the first 10GB of storage is free. With its recent inclusion as a destination for web server’s WHM backup, Farmhouse Networking has been recommending our hosting provider customers to make the switch from AWS Glacier. Here is the steps to make the switch:
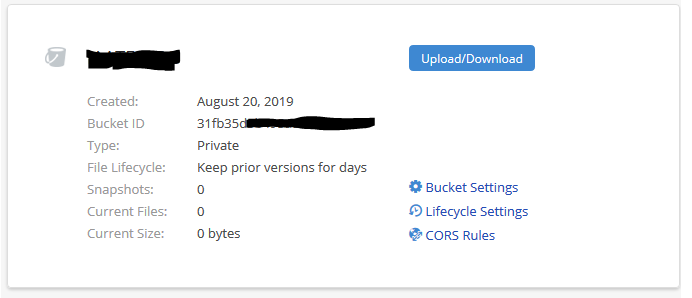
Setup Backblaze Buckets
Login to Backblaze account
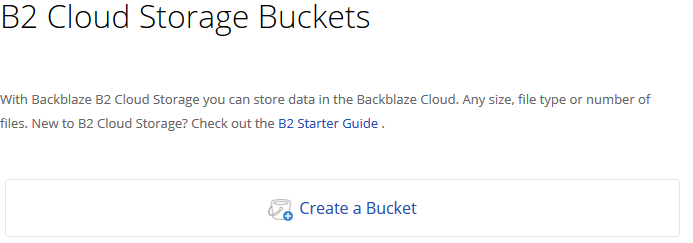
Click on the Create Bucket button in the B2 Cloud Storage Buckets section
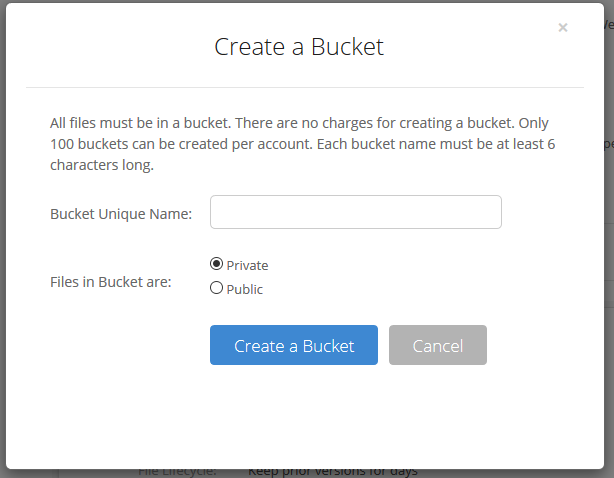
3. Give the Bucket a name and keep the bucket private for the backups. Click on the Create a Bucket button.
4. Copy down your Backblaze Bucket name and Backblaze Bucket ID
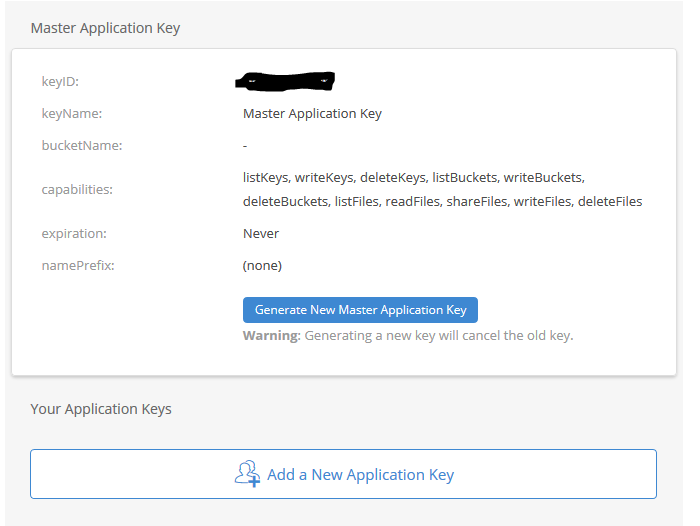
Setup Backblaze Application Key
Click on the App Keys section
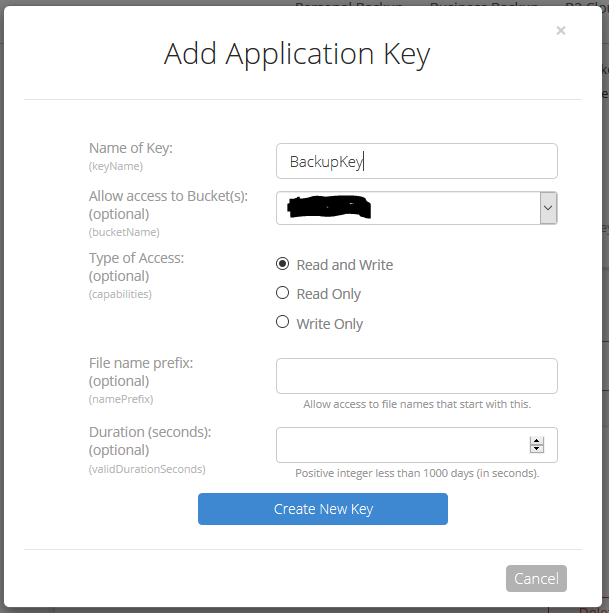
Click on Add a New Application Key
3. Give the Backblaze Application Key a name, chose the newly created bucket from the list and make sure to leave the Type of Access as “Read and Write”. Click the Create Key button.
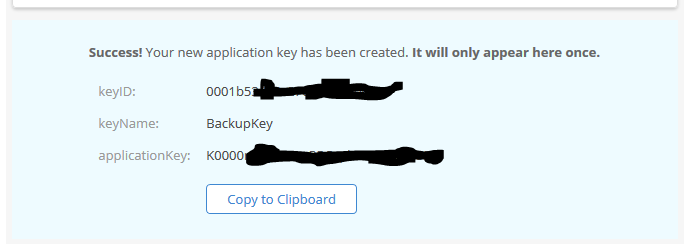
4. Make sure to copy down the Backblaze Application keyID and Backblaze Application applicationKey. This will be the only time they are both shown. If you lose the Backblaze Application applicationKey then you will have to delete the current one and create a new one.
Setup WHM Backup to Backblaze
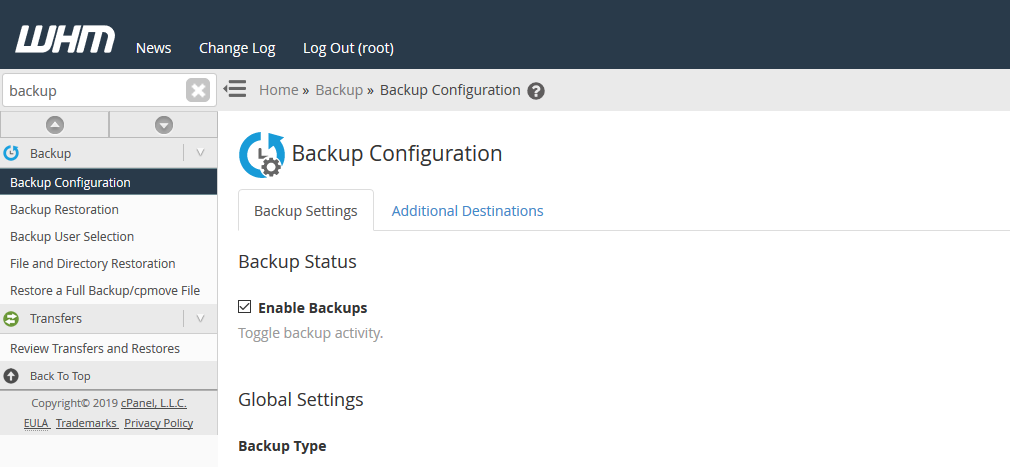
Connect to WHM as root user and choose Backup Configuration from the menu. The specific WHM backup settings are not discussed here, but feel free to contact us for advise on how to do so.
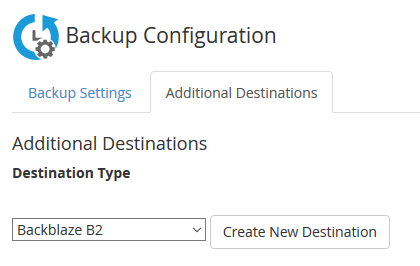
2. Click on Additional Destinations. Chose Backblaze B2 from the Destination Type and click on the Create New Destination button.
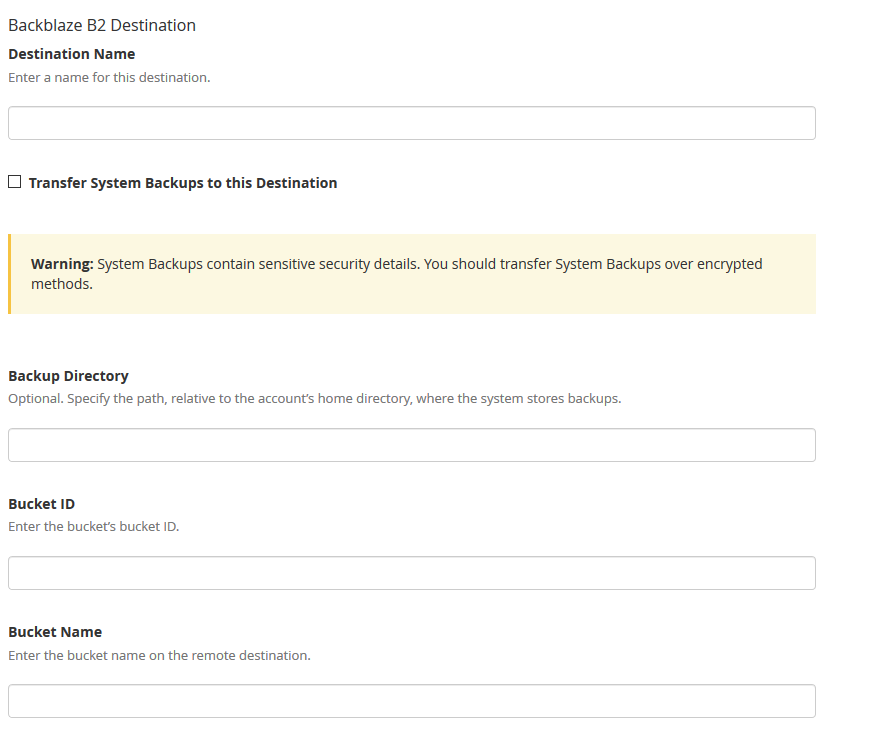
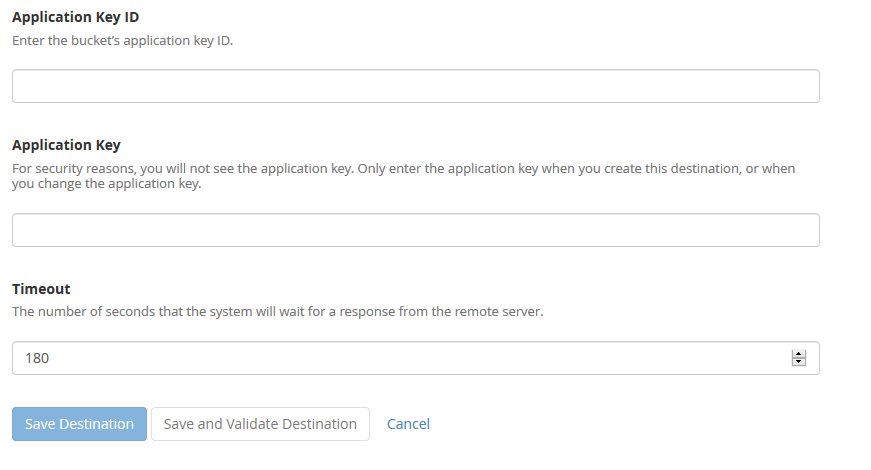
3. Enter in a backup name. Click on the “System Backups” if that is desired. Leave the Backup Directory blank. Enter in the Backblaze Bucket ID and Backblaze Bucket Name copied down earlier. Enter in the Backblaze Application Key ID and Backblaze Application Key. Click on the Save and Validate Destination button.
Make sure to disable your old AWS Glacier backup destination. All backups on Glacier should be set to auto delete according to a lifecycle, but if not then wait 120 days from creation to remove them to avoid any penalties. Speaking of lifecycles, it is a good idea to change the lifecycle settings on the Backblaze bucket to auto delete after a determined number of days since they do charge for total storage utilized.
If your company is would like to discuss the layers of security you have in place, then contact us for assistance.
A single ransomware infection can freeze a church’s donations, records, and operations
Got a call a couple weeks ago from a local church:
“we came in and open the computer and we have ransomware on there. We can’t even get to any of our stuff. It’s telling us to email somebody and so that they can free up the computer.”
How does this happen?
Generally these things happen because people click on things they shouldn’t. Whether in an attachment in email from someone they don’t recognize, a link in social media that sounds too good to pass up, or an advertisement for something they can’t live without. Once the user gives permission for something to open or run on their computer the game is over and the hacker wins.
What to do when it happen?
Stop using the computer.
Leave the computer alone! Do not carry out any further commands, including commands to Save data.
Do not close any of the computer’s windows or programs. Leave the computer alone.
Leave everything plugged in and do not turn off the computer or peripheral devices.
If possible, physically disconnect the computer from networks to which it is attached.
Call us immediately. Write down any unusual behavior of the computer (screen messages, unexpected disk access, unusual responses to commands) and the time when they were first noticed.
Write down any changes in hardware, software, or usage that preceded the malfunction.
Do not attempt to remove a suspected virus! Let the professionals do the dirty work.
How to prevent this from happening?
Layers of protection is the simple answer. A good antivirus installed to stop the bad programs from running, DNS filtering to keep users off of bad sites / advertisements, a good backup of all data to recover when this does happen, and most important of all EDUCATION – teaching users what safe internet usage looks like and having policies in effect to train them can mitigate 60-70% of infections.
If your company is would like to discuss the layers of security you have in place, then contact us for assistance.
$37+/hour wasted on IT issues = $9,000+ annually per employee
“Office workers across the UK are wasting 14 days per person each year — or 1.8 billion hours a year in total — because the technology they’re given isn’t good enough.” – BetaNews
Outdated Tech = Wasted Time
Slowness: When a computer is slow, so is the worker operating it. As a computer ages, like anything else, the parts inside wear down. Regular maintenance and replacement are the solution to increasing employee productivity.
Crashing: As computer crashes happen data is damaged or lost. This means work has to be re-done. Crashing can be a sign of software issues or hardware issues that require proper diagnosis. Once fixed employees can get back to business without interruptions.
Incompatibility: Out-dated software or hardware can cause what used to work perfectly to stop all together. Regular updates of all software and replacement of aging hardware is always the best policy. Helping employees stay on track with standard operating procedures makes work flow possible.
Security: Hackers are constantly working to find new ways of breaching security measures. Without current security solutions (firewall / DNS filtering / antivirus / SPAM filtering / password management ) and up-to-date systems, your network is a sitting duck. Network downtime due to a breach can be a business killer.
If your company is using out-of-date technology, then contact us for assistance.
Modernization = immediate 30% IT cost reduction with compliance
Legacy infrastructure can limit scalability, increase downtime, and require expensive patchwork fixes. Modern solutions — whether in the cloud or hybrid configurations — give small businesses flexibility, automation, and predictable operating costs.
According to Gartner, companies that modernize their IT environments reduce infrastructure costs by up to 30% and improve operational efficiency by 25% or more. For small business owners, these savings can directly impact profitability and competitiveness.
Action Steps to Modernize and Optimize IT
To start seeing results, take a structured approach to IT modernization:
Assess Your Current Infrastructure Conduct a full audit of your hardware, software, and network assets. Identify outdated servers, unsupported software, and bottlenecks that affect performance or security.
Move to Scalable Cloud Solutions Transition from on-premises systems to cloud-based environments like Microsoft Azure or Google Workspace. Cloud solutions reduce capital expenditures, improve accessibility, and support remote teams.
Virtualize Where Possible Replace physical servers with virtual machines. Virtualization consolidates workloads, reduces energy usage, and simplifies disaster recovery planning.
Implement Automation and AI Tools Automate repetitive IT maintenance tasks such as updates, monitoring, and backups. Modern IT management software decreases manual intervention and minimizes human error.
Enhance Cybersecurity Frameworks As you modernize, integrate advanced security tools — firewalls, endpoint detection, and multi-factor authentication — to prevent modern cyber threats.
Adopt Predictable Cost Models Consider a managed IT service provider (MSP) that delivers infrastructure and support under a fixed monthly fee. This approach eliminates unpredictable repair costs and frees capital for innovation.
Common Questions from Business Owners
Q: How do I know if my infrastructure is outdated? A: Signs include frequent downtime, slow systems, incompatible applications, or rising maintenance costs. If your servers are older than five years or your support software is no longer updated, it’s time for a change.
Q: What’s the ROI of IT modernization? A: Beyond cost savings, modernization improves workforce productivity, customer satisfaction, and business agility. Many SMBs see full ROI within 12–24 months through improved uptime and reduced service calls.
Q: Is the cloud secure for small businesses? A: Yes, if configured properly. Major cloud providers maintain rigorous security standards and compliance certifications. Working with an IT partner ensures proper access controls and data backup procedures.
Q: How disruptive is the modernization process? A: With professional planning, disruption can be minimized. Migration often occurs after-hours or in stages to ensure operations continue smoothly.
How Farmhouse Networking Can Help
At Farmhouse Networking, we specialize in helping small and mid-sized businesses modernize their IT infrastructure for measurable cost savings. Our services include:
Comprehensive infrastructure assessments to identify inefficiencies.
Cloud migration and virtualization support tailored to your industry needs.
Cybersecurity modernization to protect against evolving threats.
Managed IT services with predictable monthly pricing and rapid support response times.
We handle the transformation process end to end — from planning and deployment to monitoring and optimization — so you can focus on running your business rather than managing technology.
Email us at support@farmhousenetworking.com to learn how Farmhouse Networking can help you modernize your IT infrastructure and optimize your company’s technology spend.
Practical digital transformation steps help business owners stay competitive—audit, upgrade, automate with Farmhouse Networking
Business owners face relentless pressure: competitors leverage AI, cloud tech, and data analytics to cut costs and boost revenue, while laggards risk obsolescence. Digital transformation isn’t optional—it’s the key to operational efficiency, customer loyalty, and market edge, enabling 23% higher profitability for adopters per McKinsey benchmarks.
Why Digital Transformation Matters Now
Digital transformation integrates technologies like cloud computing, automation, and cybersecurity into core operations, reshaping how businesses deliver value. For owners in accounting, healthcare, or nonprofits, it streamlines compliance-heavy processes, personalizes client services, and scales without ballooning headcount. In 2026, with President Trump’s pro-innovation policies accelerating tech adoption, firms ignoring this lose 30-50% ground to agile rivals.
Practical Action Steps
Business owners and IT teams should follow this phased roadmap, drawn from proven frameworks for small-to-mid enterprises.
Conduct a Digital Audit: Map current tech stack, processes, and skills gaps. Use free tools like Google’s Digital Maturity Model to score readiness across operations, customer touchpoints, and security—takes 1-2 weeks.
Set SMART Goals: Define measurable targets, e.g., “Reduce invoice processing from 5 days to 24 hours via automation” or “Increase client retention 15% with CRM personalization.” Align with revenue growth or cost savings.
Upgrade Infrastructure: Migrate to scalable cloud platforms (AWS, Azure) for flexibility; integrate AI tools for predictive analytics. Budget 10-20% of IT spend initially, prioritizing cybersecurity to avert breaches costing $4.5M on average.
Digitize Processes: Automate workflows—inventory for accounting firms, patient scheduling for healthcare, donor tracking for charities—using no-code platforms like Zapier. Train staff via 2-4 hour sessions.
Measure and Iterate: Track KPIs quarterly (e.g., ROI, uptime) with dashboards. Pilot quick wins first, scaling successes over 12-18 months.
Step
Owner/IT Role
Timeline
Expected ROI
Audit
Owner leads, IT executes
1-2 weeks
Baseline for 20% efficiency gains
Goals
Joint workshop
1 week
Guides 15-30% revenue uplift
Upgrade
IT procures, tests
1-3 months
Scalability reduces costs 25%
Digitize
IT implements, Owner approves
3-6 months
Automation saves 40% time
Iterate
Ongoing reviews
Quarterly
Sustains competitive edge
FAQs: Client Inquiries Answered
Q: What’s the ROI timeline for digital transformation? A: Quick wins yield 6-12 month returns; full programs deliver 20-50% efficiency gains in 18-24 months, per industry data.
Q: How do we avoid disruption during rollout? A: Phase implementations, starting with non-critical processes. Use hybrid cloud for seamless transitions—95% of phased projects succeed vs. 30% big-bang approaches.
Q: Is it affordable for small firms in accounting/healthcare/charities? A: Yes—cloud tools start at $50/user/month. Focus on high-impact areas like CRM ($10K initial investment yields $50K savings).
Q: How to upskill staff without big budgets? A: Leverage free resources (Microsoft Learn, AWS Training) and vendor demos. Partner with MSPs for hands-on support.
How Farmhouse Networking Drives Your Success
Farmhouse Networking specializes in B2B digital transformation for accounting, healthcare, and charity sectors, delivering tailored IT strategies that convert visitors to clients. We conduct audits, deploy secure cloud migrations, automate workflows, and optimize SEO for “digital transformation services [your industry]” to drive organic traffic. Our clients see 40% faster deployments and 25% cost reductions, with white-glove support ensuring zero downtime. From branding your site as a tech-forward leader to lead-gen funnels, we handle IT so you focus on growth.
Local VoIP expertise eliminates traditional phone system costs
When it comes to phone service there is not much difference between providers. They all bring dial tone to your business and route calls to their destination. They all provide the same set of features that users have come to know and use.
What Makes Farmhouse Networking Different
No Introductory Rates: Most local providers will offer an attractive introductory rate to get your business. The only bad part is after one years time you are automatically changed to the regular price which is often $10-$20 more per line.
No Installation Costs: As we are a growing provider of phone services, anyone signing up for phone service with us this year will have no installation costs.
No Bogus Taxes or Fees: We have looked at phone bills from the major local providers and each of them has some bogus tax or fee added to the phone bill. (The only valid ones are Telecommunications Relay Service, Telephone Assistance Program, the Telecommunications Devices Access Program, E911 (VoIP), FCC Regulatory Fee (VoIP), FUSF (VoIP), and P.U.C. Fee – in case you were wondering)
Phone Costs: Unlike computers, there is no reason why you need to buy brand new phones. There are vendor programs that sell re-conditioned phones at much lower costs and they work just as good as the new ones. There is also leasing options available to help ease the pain of purchasing phones too.
Our Prices: We are not out to gouge our clients or nickel / dime them to death as you have already read. The only question now is how much do we charge? For the standard user, the cost of a phone line is only $29.95 per month. The cost of a standard fax line is only $22.50 per month.
Extra Features: We have several features that most of the other providers just don’t. A customer portal that clients can use to chat with fellow employees, check voicemails, track expenses, and make other account changes. A mobile app that can be used to turn your smart phone into an extension of your desk phone and more. Also failover to another phone number – if the power or internet is out you can have your calls routed to any other phone.
If your company uses phones for business, then contact us to see the true difference.
This article came from the need of another local tech company to forward an Exacqvision Web Portal to something other than port 80, as it was already in use. I could not find a detail article on how to accomplish Sophos DNAT while changing the port number:
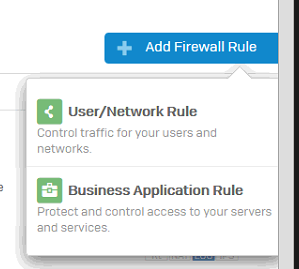
How to configure Sophos DNAT for an internal server
Navigate to Firewall then click +Add Firewall Rule and select Business Application Policy.
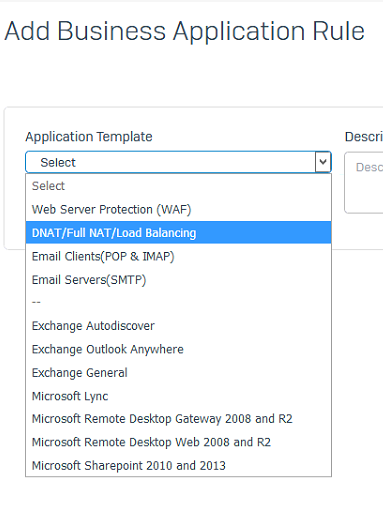
Select Application Template and choose DNAT/Full NAT/Load Balancing.
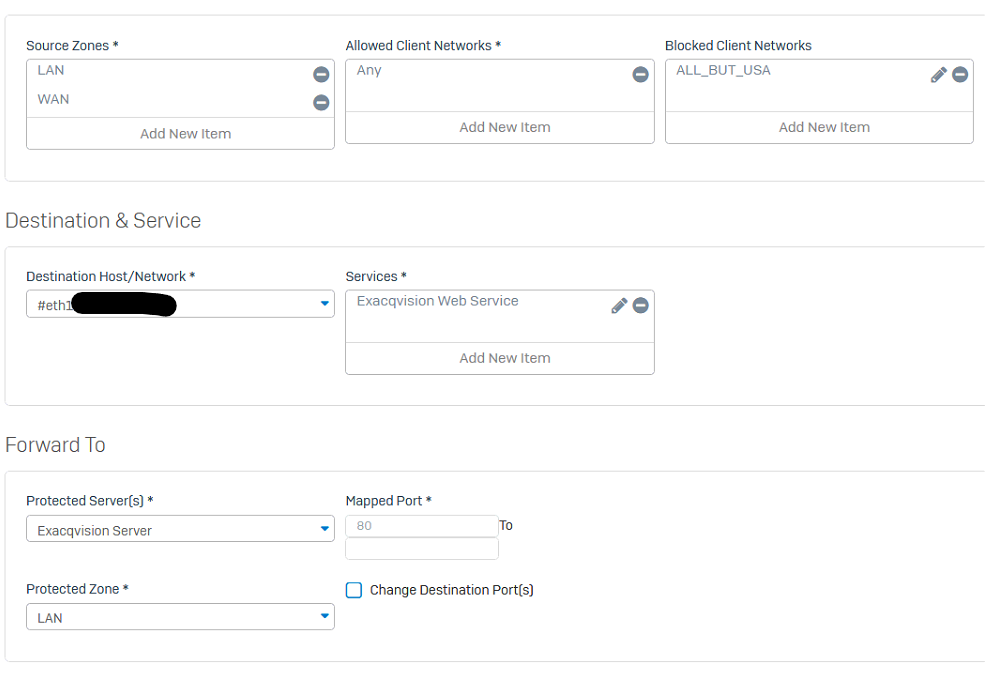
Fill out the settings as shown below:
Rule Name
Source Zones: WAN (and LAN if needed)
Allowed Client Networks: Any
Destination Host/Network: WAN Interface (#eth0-? whichever one you use)
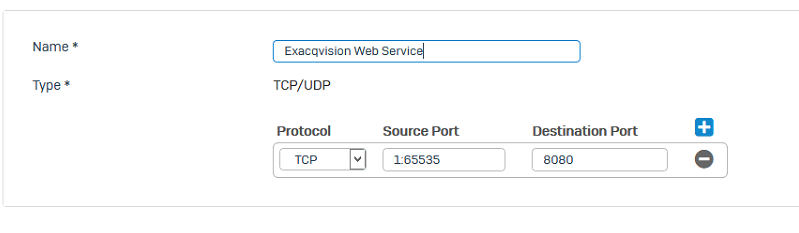
Services: Either select the service you already created or create a new one for the external port to be used as below
Protected Servers: Select an existing or create a host entry for the internal server.
Protected Zone: Select the Zone in which the host resides (LAN or DMZ).
Change Destination Port(s): Check this then change the port to the internal port.
Click Save to save the configuration.
If your company is using a Sophos router and is unsure of how to configure it, then contact us for assistance in making the best use of your router.
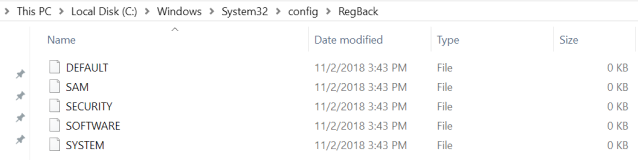
In a new Windows 10 Support article, dated June 28th, Microsoft comes clean that they will no longer be backing up the registry file with its built in backup feature. “This change is by design, and is intended to help reduce the overall disk footprint size of Windows.” They instead recommend that System Restore be enabled and used to recover in case of registry corruption (which by the way uses disk space too).
Ending Registry Backup
The Windows Registry is a hierarchical database that stores low-level settings for Windows 10 and installed applications that rely on it. The kernel, device drivers, services, Security Accounts Manager, and user interface configuration are all in the registry. If the registry is lost then system settings, drivers, user interface tweaks, and many programs will all need to be fixed or re-installed from scratch.
If your company is using the built in Windows Backup feature, then contact us for assistance moving to a system that provides complete backup of your systems.
Farmhouse Networking has had a long standing policy that we do not keep a record of client passwords (except when needed for device administration). That is about to change, but before we talk about our new password policy let’s talk password storage:
Common Password Storage
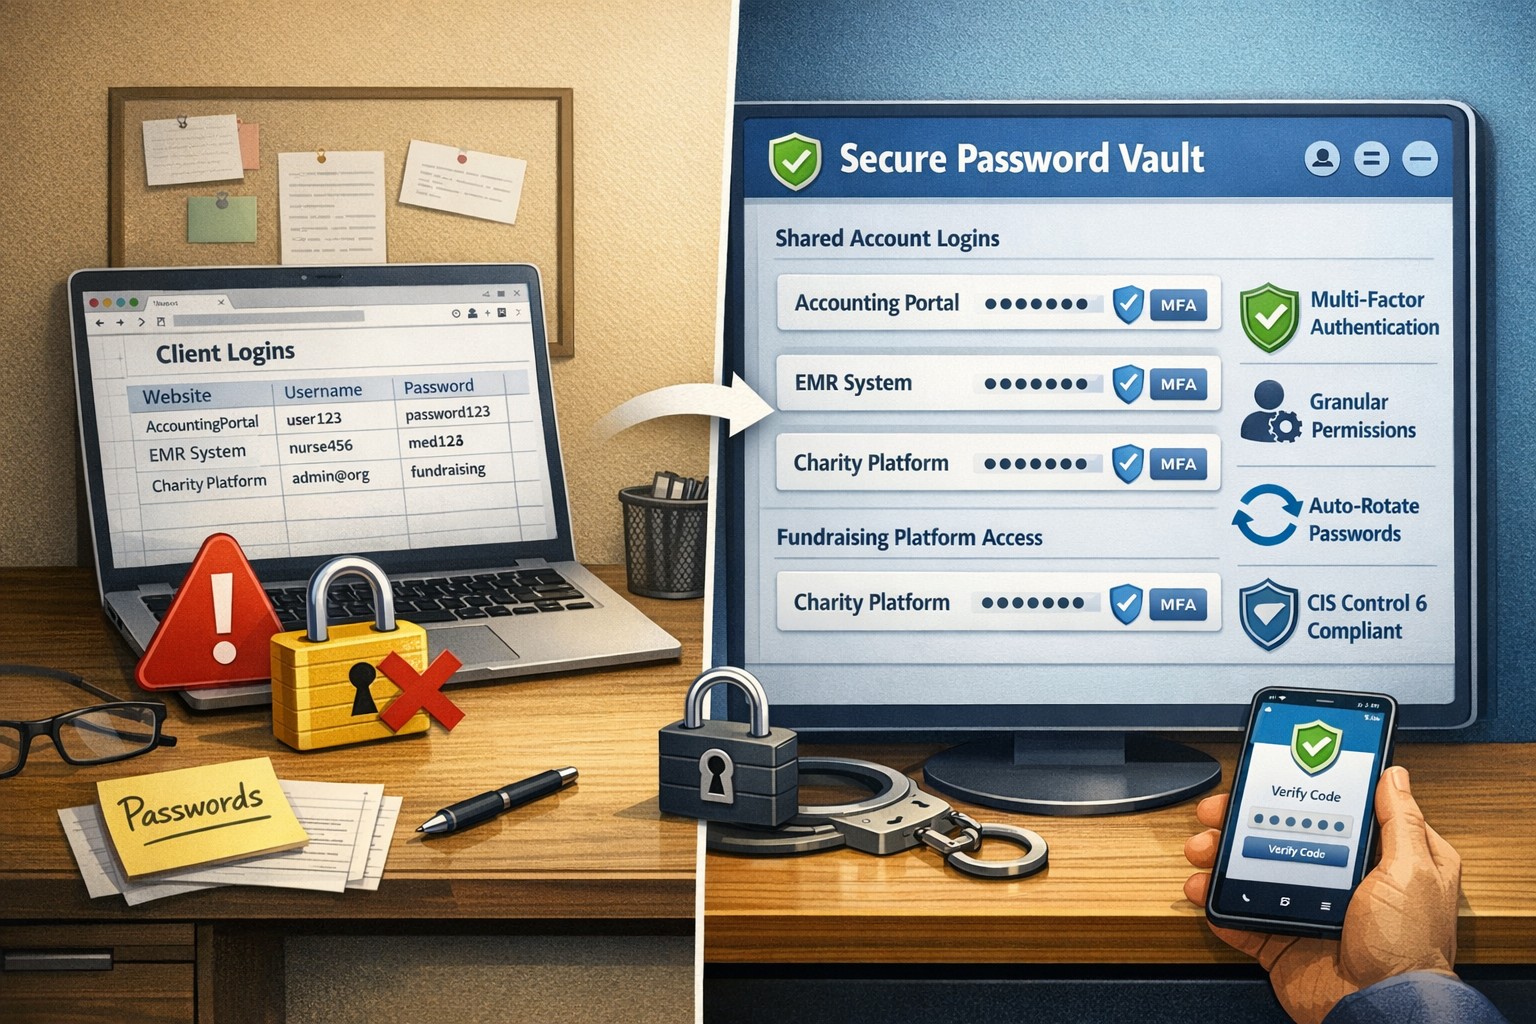
Here are some popular places where many businesses store their passwords that make them very vulnerable to being stolen.
Passwords written on paper (that are not under lock and key):
On your desk under your keyboard (or taped underneath)
Under your stapler or desk decorations
On sticky notes stuck to your monitor or desk
On a scrap of paper on your desk or in a drawer
In a notebook or address book
In a old-fashioned Rolodex file
Paper printouts or photocopies of your passwords
Anyone with access to your office could easily find and steal passwords stored like this.
Passwords stored in your computer (without using encryption):
Remembered in your web browser
A document called “Passwords” that you’ve created anywhere on your computer, perhaps using Microsoft Word or Excel
A document with any other name on your computer (including the password as the name)
Email drafts that you’ve created (but not sent) containing password information
Anyone with access to your computer could easily find and steal passwords stored like this, including both a person with physical access to it as well as a virus or hacker gaining access via the internet, or scamming you into granting them access, even once.
Passwords stored in your smartphone or tablet (without using encryption):
Electronic “Notes” containing password information
Other documents or emails similar to the ones listed in computer storage above
Anyone with access to your device could easily find and steal passwords stored like this.
Passwords sent via regular (insecure) email:
Emails that you have sent to yourself containing password information
Emails that you have sent to anyone else containing password information
Any information that you send using regular (unencrypted) email puts that information at risk of being stolen. Email is neither private nor secure. Sending an email is like mailing a postcard, and hackers and thieves can easily read the contents. You should never send passwords (or any other confidential or sensitive data) via regular email.
Secure Password Storage
Now for the discussion of Farmhouse Networking’s new password policy. We are partnering with a company to provide a storage of passwords and other client documentation with military grade encryption. This partnership also allows us to address the dangers that common password storage present by offering our clients this same encrypted password storage service. Here are some of the benefits of this service:
Unlimited users
Unlimited passwords
Each user has a personal password vault
Shared company password vault
Security groups to manage access
Auditing & reporting (Compliance)
Secure password sharing
1-Click Login Tool (for all major browsers)
Mobile Device Access
Only $15 per month (Compared to Lastpass Business at $4 per user per month)
If your company is using common password storage of any kind do yourself a security favor and contact us to upgrade to secure password storage.
And God will generously provide all you need. Then you will always have everything you need and plenty left over to share with others. As the Scriptures say, “They share freely and give generously to the poor. Their good deeds will be remembered forever.” For God is the one who provides seed for the farmer and then bread to eat. In the same way, he will provide and increase your resources and then produce a great harvest of generosity in you. - 2 Corinthians 9:8-10
We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.